 esrrhs/pingtunnel
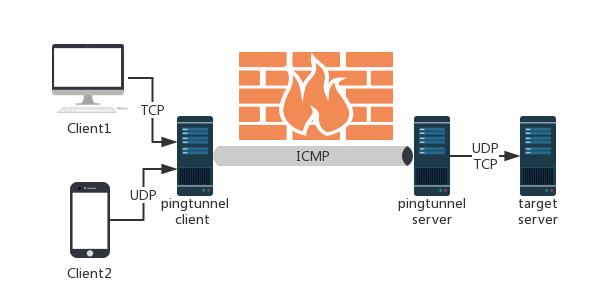
Pingtunnel is a tool that send TCP/UDP traffic over ICMP





Pingtunnel is a network tool that tunnels TCP/UDP/SOCKS5 traffic over ICMP Echo (Ping) packets to bypass strict network firewalls or throttled TCP/UDP traffic.
⚠️ Note: This tool is strictly intended for study and research purposes. Do not use it for any illegal purpose.
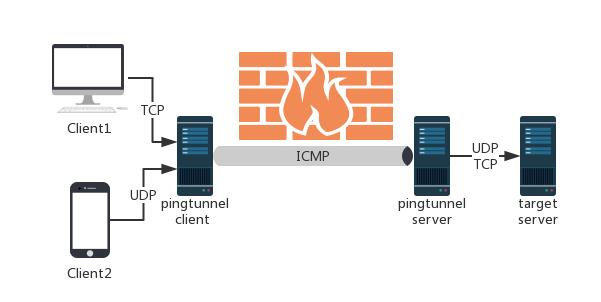
-password) drives mutual authentication and end-to-end AEAD encryption (default chacha20-poly1305, optional aes256/aes128).-forward): the server can relay incoming traffic through an upstream SOCKS5/HTTP proxy.pingtunnel config.json or pingtunnel -c config.json;config.json in the current directory is loaded automatically by default;bb) suppresses bufferbloat and packet-loss-induced stalls.Sample files ship with the repository. Just fill in your server IP and a strong password:
config-server.json){
"type": "server",
"password": "YOUR_STRONG_PASSWORD_HERE",
"encrypt": "chacha20",
"icmp_listen": "0.0.0.0"
}
Start the server (requires root / administrator privileges):
sudo ./pingtunnel config-server.json
# or: sudo ./pingtunnel -c config-server.json
config-client-socks5.json){
"type": "client",
"listen": "127.0.0.1:1080",
"server": "YOUR_SERVER_IP",
"socks5": true,
"password": "YOUR_STRONG_PASSWORD_HERE",
"encrypt": "chacha20"
}
Start the client:
./pingtunnel config-client-socks5.json
# or: ./pingtunnel -c config-client-socks5.json
Then set your browser or system proxy to SOCKS5 127.0.0.1:1080.
Run on a machine with a public IP:
sudo ./pingtunnel -type server -password YOUR_STRONG_PASSWORD_HERE
(Optional) Disable the Linux kernel's default ICMP echo replies to avoid interference:
echo 1 > /proc/sys/net/ipv4/icmp_echo_ignore_all
./pingtunnel -type client -l 127.0.0.1:1080 -s YOUR_SERVER_IP -socks5 -password YOUR_STRONG_PASSWORD_HERE
./pingtunnel -type client -l :2222 -s YOUR_SERVER_IP -t 192.168.1.100:22 -password YOUR_STRONG_PASSWORD_HERE
./pingtunnel -type client -l :5353 -s YOUR_SERVER_IP -t 8.8.8.8:53 -udp -password YOUR_STRONG_PASSWORD_HERE
docker run --name pingtunnel-server -d \
  --restart=always \
  --privileged \
  --network host \
  esrrhs/pingtunnel ./pingtunnel -type server -password YOUR_STRONG_PASSWORD_HERE
docker run --name pingtunnel-server -d \
  --restart=always \
  --privileged \
  --network host \
  -v /etc/pingtunnel/server.json:/app/server.json:ro \
  esrrhs/pingtunnel ./pingtunnel /app/server.json
For more advanced options and topologies (server-side secondary proxy, port forwarding, SOCKS5 authentication, flow control and congestion tuning), see: 👉 USAGE.md - Pingtunnel Usage and Configuration Guide
