 controlplaneio/kubesec
Analyse des risques de sécurité pour les ressources Kubernetes
[![Testing Workflow][testing_workflow_badge]][testing_workflow_badge] [![Security Analysis Workflow][security_workflow_badge]][security_workflow_badge] [![Release Workflow][release_workflow_badge]][release_workflow_badge]
[![Go Report Card][goreportcard_badge]][goreportcard] [![PkgGoDev][go_dev_badge]][go_dev]
Pour plus d'exemples, visitez Kubesec.io, qui utilise l'API hébergée de ControlPlane à l'adresse v2.kubesec.io/scan.
Créez un fichier de ressource Kubernetes (par exemple, kubesec-test.yaml) à analyser. Pour un test rapide, vous pouvez enregistrer le manifeste Pod suivant :
$ cat <<EOF > kubesec-test.yaml
apiVersion: v1
kind: Pod
metadata:
  name: kubesec-demo
spec:
  containers:
  - name: kubesec-demo
    image: gcr.io/google-samples/node-hello:1.0
    securityContext:
      readOnlyRootFilesystem: true
EOF
Exécutez une analyse sur votre fichier de manifeste :
# Using the local binary
kubesec scan kubesec-test.yaml

# Or using Docker
docker run -i kubesec/kubesec:v2 scan /dev/stdin < kubesec-test.yaml

# Using the local binary with a human-readable table output format
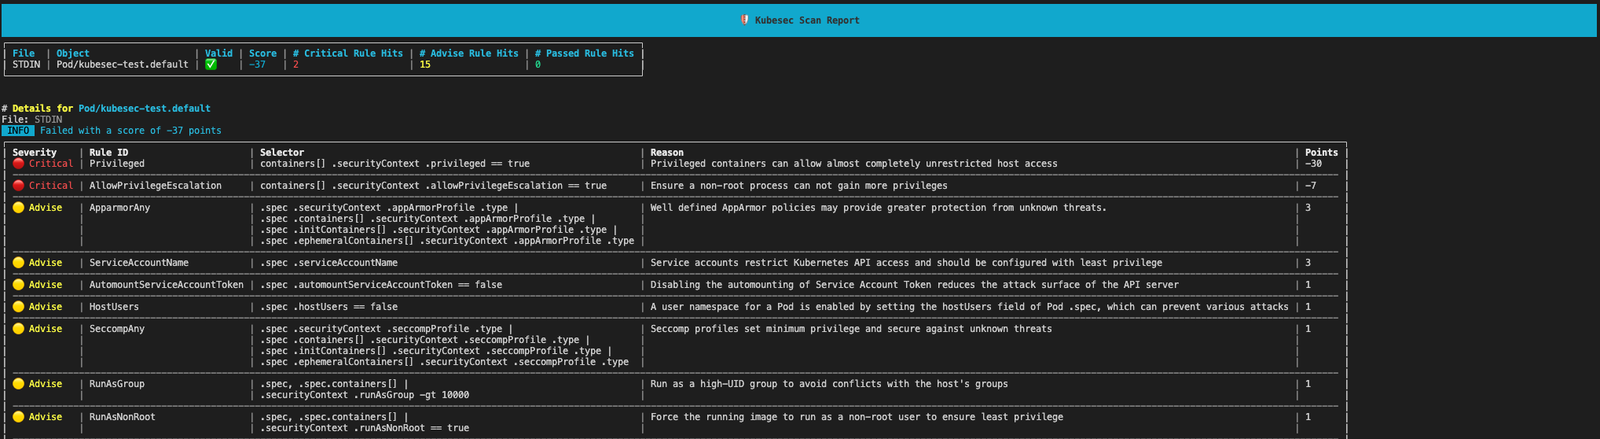
kubesec scan kubesec-test.yaml --format table
[!TIP] Pour afficher les résultats dans un tableau lisible plutôt qu'au format JSON par défaut, utilisez l'option
--format table.
kubesec affichera un score de sécurité et une analyse détaillée de votre ressource.
Kubesec est disponible sous forme de :
docker.io/kubesec/kubesec:v2Ou installez le dernier commit depuis GitHub avec :
$ go install github.com/controlplaneio/kubesec/v2@latest
$ GO111MODULE="on" go get github.com/controlplaneio/kubesec/v2
Analysez des ressources Kubernetes à partir de fichiers locaux ou de l'entrée standard.
Kubesec peut analyser plusieurs documents YAML dans un seul fichier d'entrée, ou analyser des documents provenant de plusieurs fichiers à la fois, à condition qu'ils soient correctement formatés comme plusieurs documents séparés par ---.
# Scan a specific local YAML file
kubesec scan ./deployment.yaml

# Scan from standard input (JSON or YAML)
cat file.json | kubesec scan -

# Scan a rendered Helm chart
helm template -f values.yaml ./chart | kubesec scan /dev/stdin

# Scan multiple YAML documents separated by '---'
{ cat test/asset/multi.yml; echo "---"; cat test/asset/critical.yml; } | kubesec scan -
Vous pouvez exécuter les mêmes commandes d'analyse en utilisant l'image Docker officielle :
# Scan a file via Docker using standard input
docker run -i kubesec/kubesec:v2 scan /dev/stdin < kubesec-test.yaml
Kubesec prend en charge trois formats de sortie différents, spécifiés par l'option --format / -f : json (par défaut), table et template, et peut analyser plusieurs documents YAML dans un seul fichier d'entrée.
# JSON array output (default behaviour)
kubesec scan ./deployment.yaml --format json

# Human-readable table output
kubesec scan ./deployment.yaml --format table

# Use a custom template for the output
kubesec scan ./deployment.yaml --format template --template report-template.tmpl
# One rule
kubesec scan --rules CapSysAdmin kubesec-test.yaml

# Multiple rules
kubesec scan --rules RunAsNonRoot,SeccompAny,ApparmorAny kubesec-test.yaml
[
  {
    "object": "Pod/security-context-demo.default",
    "valid": true,
    "message": "Failed with a score of -30 points",
    "score": -30,
    "scoring": {
      "critical": [
        {
          "selector": "containers[] .securityContext .capabilities .add == SYS_ADMIN",
          "reason": "CAP_SYS_ADMIN is the most privileged capability and should always be avoided",
          "points": -30
        }
      ],
      "advise": [
        {
          "selector": "containers[] .securityContext .runAsNonRoot == true",
          "reason": "Force the running image to run as a non-root user to ensure least privilege",
          "points": 1
        },
        {
          // ...
        }
      ]
    }
  }
]
# Print all scanning rules with their associated point scores
kubesec print-rules

# Print all scanning rules with their associated point scores as a table
kubesec print-rules --format table
[
  {
    "id": "AllowPrivilegeEscalation",
    "selector": "containers[] .securityContext .allowPrivilegeEscalation == true",
    "reason": "Ensure a non-root process can not gain more privileges",
    "kinds": [
      "Pod",
      "Deployment",
      "StatefulSet",
      "DaemonSet"
    ],
    "points": -7,
    "advise": 0
  },
...
]
Kubesec utilise kubeconform (merci @yannh) pour valider les manifestes à analyser. Cela implique que la spécification de différents emplacements de schémas suit les règles décrites dans le README de kubeconform.
# Usees the latest schema from upstream
# Schema will be fetched from: https://raw.githubusercontent.com/yannh/kubernetes-json-schema/master/master-standalone-strict/pod-v1.json
kubesec scan ./pod.yaml

# Use a specific schema version from upstream (format x.y.z with no v prefix)
# Schema will be fetched from: https://raw.githubusercontent.com/yannh/kubernetes-json-schema/master/v1.25.3-standalone-strict/pod-v1.json
kubesec scan ./pod.yaml --kubernetes-version 1.25.3


