

Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Catégories

Criminalistique Numérique

Outils pour l'acquisition, la préservation et l'analyse des preuves numériques à des fins légales ou d'enquête.

Recommandé par Kitploit

Meilleurs outils

10 sélectionnés
autopsy preview#1

autopsy

GitHubsleuthkit/autopsy
3.3kil y a 6 mois
sleuthkit preview#2

sleuthkit

GitHubsleuthkit/sleuthkit
3.2kil y a 6 jours
volatility3 preview#3

volatility3

GitHubvolatilityfoundation/volatility3
4.3kil y a 1 mois
plaso preview#4

plaso

GitHublog2timeline/plaso
2.2kil y a 3 jours
bulk_extractor preview#5

bulk_extractor

GitHubsimsong/bulk_extractor
1.4kil y a 1 mois
velociraptor preview#6

velociraptor

GitHubvelocidex/velociraptor
4.2kil y a 14h 10m
timesketch preview#7

timesketch

GitHubgoogle/timesketch
3.5kil y a 8 jours
mvt preview#8

mvt

GitHubmvt-project/mvt
16.1kil y a 2 jours
androidqf preview#9

androidqf

GitHubmvt-project/androidqf
230il y a 13 jours
avml preview#10

avml

GitHubmicrosoft/avml
1.1kil y a 7 jours
Plus récentsPertinencePlus populairesMis à jour récemment
1453 résultats
antipwny preview

antipwny

GitHubrvazarkar/antipwny

Un IDS basé sur l'hôte écrit en C# ciblant Metasploit

defensive-toolsmemory-forensicspersistence-mechanisms+3
45il y a 13 ans
whapa preview

whapa

GitHubb16f00t/whapa

Kit d'outils forensiques graphique pour analyser, décrypter et extraire les données WhatsApp des appareils Android et iOS, y compris les sauvegardes…

android-securityencryption-decryption-toolsios-security+5
1.5kil y a 3 mois
sdrtrunk preview

sdrtrunk

GitHubdsheirer/sdrtrunk

A cross-platform java application for decoding, monitoring, recording and streaming trunked mobile and related radio protocols using Software Defined…
wireless-securitydigital-forensics
2.2kil y a 12h 12m
gpg_reaper preview

gpg_reaper

GitHubkacperszurek/gpg_reaper

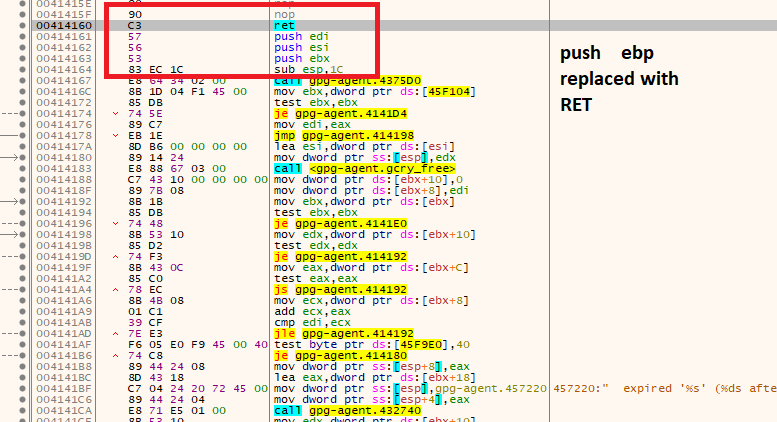
GPG Reaper - Obtenir/Voler/Restaurer des clés privées GPG depuis le cache/mémoire de gpg-agent

memory-forensicsexploitationpost-exploitation+1
96il y a 8 ans
ReClass.NET preview

ReClass.NET

GitHubreclassnet/reclass.net

Plus qu'un port de ReClass vers la plateforme .NET.
dynamic-analysis-sandboxingmemory-forensicscode-analysis+4
2.2kil y a 3 ans
dumpzilla preview

dumpzilla

GitHubbusindre/dumpzilla

Extraire toutes les informations forensiques intéressantes des navigateurs Firefox, Iceweasel et Seamonkey
osintforensicsinformation-gathering+1
148il y a 11 mois
MozCache preview

MozCache

GitHubbusindre/mozcache

Script shell simple pour effectuer une analyse forensique du cache des navigateurs Mozilla (Firefox, Iceweasel et Seamonkey).

forensicsdigital-forensics
1il y a 8 ans
Linux-Kodachi preview

Linux-Kodachi

GitHubwmal/linux-kodachi

Système d'exploitation renforcé basé sur Debian axé sur la confidentialité avec une pile d'anonymat pré-intégrée (Tor, VPN, DNSCrypt), des outils…

osintvulnerability-scannersforensics+9
489il y a 26 jours
grr preview

grr

GitHubgoogle/grr

Cadre de forensique en direct à distance et de réponse aux incidents avec un agent Python pour collecter des données forensiques depuis les…

disk-forensicsmemory-forensicsnetwork-forensics+4
5.1kil y a 1 mois
Apktool preview

Apktool

GitHubibotpeaches/apktool

Un outil de rétro-ingénierie pour les fichiers APK Android

android-securitymobile-app-pentestingreverse-engineering+4
25.3kil y a 6 jours
linux_screenshot_xwindows preview

linux_screenshot_xwindows

GitHubeurecom-s3/linux_screenshot_xwindows

Plugin Volatility pour extraire X captures d'écran d'un dump mémoire

memory-forensicsforensicsinformation-gathering+1
37il y a 8 ans
rastrea2r preview

rastrea2r

GitHubrastrea2r/rastrea2r

Collecter & chasser les IOCs avec entrain et style

ioc-managementreconnaissancememory-forensics+6
238il y a 1 mois
guasap-whatsapp-foresincs-tool preview

guasap-whatsapp-foresincs-tool

GitHubquantika14/guasap-whatsapp-foresincs-tool

Outil forensique WhatsApp

forensicsmobile-forensicsdata-recovery+1
176il y a 4 mois
memoro preview

memoro

GitHubepfl-vlsc/memoro

Memoro: Un profileur de tas détaillé

dynamic-analysis-sandboxingmemory-forensicsdebuggers+1
184il y a 5 ans
sRDI preview

sRDI

GitHubmonoxgas/srdi

Implémentation en shellcode de l'injection de DLL réflective. Convertit les DLL en shellcode indépendant de la position.
memory-forensicspayload-generationexploitation+7
2.5kil y a 4 ans
SafeText preview

SafeText

GitHubdavidjacobson/safetext

Script pour supprimer les homoglyphes et les caractères de largeur nulle afin de permettre la distribution sécurisée de documents provenant de…

data-exfiltrationforensicsdigital-forensics+1
136il y a 7 ans
sshkey-grab preview

sshkey-grab

GitHubnetspi/sshkey-grab

Récupérer les clés SSH de ssh-agent

memory-forensicsexploitationpost-exploitation
223il y a 11 ans
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

Cet outil permet de récupérer d'anciennes informations de session RDP (mstsc) sous forme de fichiers PNG corrompus. Ces fichiers PNG permettent à un…


reconnaissancememory-forensicsforensics+4
218il y a 8 ans
Précédent1…636465…81Suivant







