
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Catégories

Sécurité des Bases de Données

Outils d'évaluation de bases de données, test d'injection SQL, audit, chiffrement et surveillance d'activité.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
sqlmap preview#1

sqlmap

GitHubsqlmapproject/sqlmap
38.2kil y a 1 jour
openvas-scanner preview#2

openvas-scanner

GitHubgreenbone/openvas-scanner
4.8kil y a 1 jour
nuclei preview#3

nuclei

GitHubprojectdiscovery/nuclei
30.4kil y a 1 jour
metasploit-framework preview#4

metasploit-framework

GitHubrapid7/metasploit-framework
38.8kil y a 0 jours
nmap preview#5

nmap

GitHubnmap/nmap
13.3kil y a 2 jours
zaproxy preview#6

zaproxy

GitHubzaproxy/zaproxy
15.6kil y a 1 jour
wapiti preview#7

wapiti

GitHubwapiti-scanner/wapiti
1.9kil y a 27 jours
semgrep preview#8

semgrep

GitHubsemgrep/semgrep
16.2kil y a 2 jours
trivy preview#9

trivy

GitHubaquasecurity/trivy
37.4kil y a 1 jour
wazuh preview#10

wazuh

GitHubwazuh/wazuh
16.5kil y a 3 jours
Plus récentsPertinencePlus populairesMis à jour récemment
650 résultats
CVE-2024-55976 preview

CVE-2024-55976

GitHubrandomrobbiebf/cve-2024-55976

Critical Site Intel <= 1.0 - Injection SQL non authentifiée
vulnerability-analysisexploitationweb-application-exploitation+3
1il y a 1 an
CVE-2024-51818 preview

CVE-2024-51818

GitHubrandomrobbiebf/cve-2024-51818

Fancy Product Designer <= 6.4.3 - Injection SQL non authentifiée
vulnerability-analysisexploitationweb-application-exploitation+3
1il y a 1 an
CVE-2025-64513 preview

CVE-2025-64513

GitHubshinyseam/cve-2025-64513

PoC pour CVE-2025-64513 — Vulnérabilité de contournement d'authentification du proxy Milvus. Scanner par lots pour vérifier l'accès non autorisé et…
vulnerability-analysisexploitationinformation-gathering+3
1il y a 11 mois
CVE-2024-0399 preview

CVE-2024-0399

GitHubxbz0n/cve-2024-0399

Preuve de concept d'exploitation pour CVE-2024-0399, une injection SQL temporelle post-authentification dans WooCommerce Customers Manager 29.4,…
vulnerability-analysisexploitationweb-application-exploitation+3
1il y a 2 ans
CVE-2025-67644-LangGraph-3.0.1-SQLite-Checkpoint-SQL-Injection preview

CVE-2025-67644-LangGraph-3.0.1-SQLite-Checkpoint-SQL-Injection

GitHubmbanyamer/cve-2025-67644-langgraph-3.0.1-sqlite-checkpoint-sql-injection

Exploit de preuve de concept pour CVE-2025-67644, une vulnérabilité d'injection SQL dans LangGraph SQLite Checkpoint. Démontre une injection SQL…
vulnerability-analysisexploitationweb-application-exploitation+4
1il y a 8 mois
CVE-2025-66947 preview

CVE-2025-66947

GitHubkabir0104k/cve-2025-66947

Preuve de concept pour une injection SQL aveugle basée sur le temps dans un panneau d'administration PHP. Démontre l'exploitation via un paramètre…
vulnerability-analysisweb-application-exploitationpenetration-testing+2
1il y a 10 mois
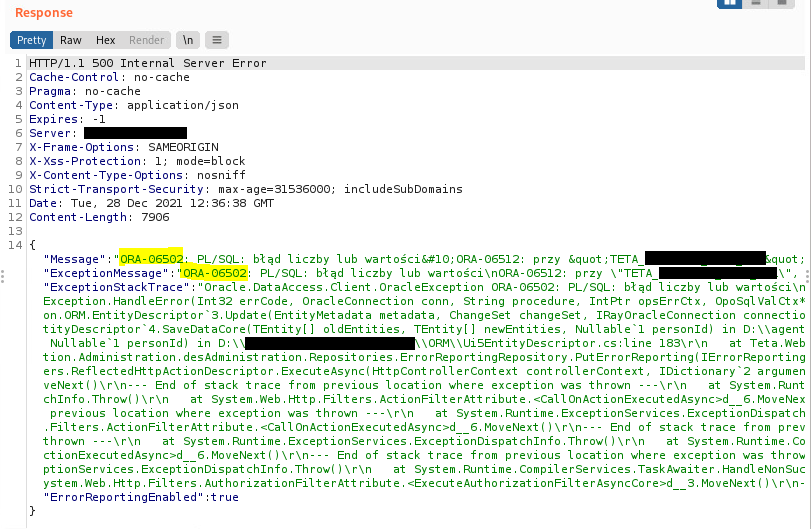
CVE-2022-27434 preview

CVE-2022-27434

GitHublongwayhomie/cve-2022-27434

Il a été découvert que UNIT4 TETA Mobile Edition 29HF13 contient une vulnérabilité d'injection SQL via le paramètre ProfileName dans la page…
vulnerability-analysisweb-application-exploitationinformation-gathering+2
1il y a 4 ans
mysql_dos preview

mysql_dos

GitHubjptr218/mysql_dos

Un outil pour faire planter les serveurs MySQL avec CVE-2017-3599
vulnerability-analysisexploitationpenetration-testing+1
1il y a 5 ans
-CVE-2012-2661-ActiveRecord-SQL-injection- preview

-CVE-2012-2661-ActiveRecord-SQL-injection-

GitHubr4x0r1337/-cve-2012-2661-activerecord-sql-injection-

Exploit de preuve de concept pour CVE-2012-2661, une vulnérabilité d'injection SQL dans Ruby on Rails ActiveRecord. Inclut un article en malais…
vulnerability-analysisexploitationweb-security+2
1il y a 3 ans
CVE-2022-23305_POC preview

CVE-2022-23305_POC

GitHubtkomlodi/cve-2022-23305_poc

CVE-2022-23305 POC d'injection SQL JDBCAppender Log4J
vulnerability-analysisexploitationweb-application-exploitation+3
1il y a 3 ans
CVE-2020-15052 preview

CVE-2020-15052

GitHubpratikshad19/cve-2020-15052

Artica Proxy Community Edition avant la version 4.30.000000 permet une injection SQL.
vulnerability-analysisexploitationweb-application-exploitation+2
1il y a 6 ans
Mongobleed-Detector-CVE-2025-14847 preview

Mongobleed-Detector-CVE-2025-14847

GitHubkeraattin/mongobleed-detector-cve-2025-14847

Mongobleed Detector CVE-2025-14847
vulnerability-scannersexploitationinformation-gathering+3
1il y a 9 mois
Oracle-mysql-CVE-2012-2122 preview

Oracle-mysql-CVE-2012-2122

GitHubcyberharsh/oracle-mysql-cve-2012-2122

Environnement d'exploit basé sur Docker pour la vulnérabilité de contournement d'authentification MySQL/MariaDB CVE-2012-2122. Démontre le défaut de…
vulnerability-analysisexploitationpenetration-testing+3
1il y a 6 ans
CTF_Django_CVE-2022-34265 preview

CTF_Django_CVE-2022-34265

GitHublnwza0x0a/ctf_django_cve-2022-34265

Défi CTF basé sur Docker démontrant une injection SQL dans les fonctions de base de données Trunc() et Extract() de Django (CVE-2022-34265) avec des…
vulnerability-analysisweb-application-exploitationctf+3
1il y a 4 ans
CVE-2024-48245 preview

CVE-2024-48245

GitHubshadowbyte1/cve-2024-48245

Vulnérabilité d'injection SQL dans Vehicle Management System 1.0 - 1.3
privilege-escalationvulnerability-analysisexploitation+3
1il y a 1 an
CVE-2025-1094 preview

CVE-2025-1094

GitHubaninfosec/cve-2025-1094

Il s'agit d'un défaut d'assainissement des entrées causé par une incompatibilité d'encodage, permettant à une entrée conçue de contourner les…
vulnerability-analysisexploitationweb-application-exploitation+5
1il y a 1 an
CVE-2020-7471-Django preview

CVE-2020-7471-Django

GitHubhuzaifakhan771/cve-2020-7471-django

PoC pour la vulnérabilité d'injection SQL dans PostgreSQL avec Django, trouvée dans Django 1.11 avant 1.11.28, 2.2 avant 2.2.10, et 3.0 avant 3.0.3.
vulnerability-analysiscode-analysisexploitation+3
1il y a 5 ans
cve-2025-14847 preview

cve-2025-14847

GitHubkuyrathdaro/cve-2025-14847

MongoBleed : outil de découverte de fuites de mémoire pour CVE-2025-14847

memory-forensicsvulnerability-analysisexploitation+3
il y a 10 mois
Précédent1…252627…37Suivant
Sécurité des Bases de Données — Page 26 | Kitploit








