
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Commandement et Contrôle — Page 14 | Kitploit
Catégories

Commandement et Contrôle

Frameworks C2, redirecteurs, écouteurs et outils d'infrastructure de commandement.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
sliver preview#1

sliver

GitHubbishopfox/sliver
11.7kil y a 5 jours
Mythic preview#2

Mythic

GitHubits-a-feature/mythic
4.7kil y a 19 jours
Empire preview#4

Empire

GitHubbc-security/empire
5.2kil y a 1 mois
merlin preview#6

merlin

GitHubne0nd0g/merlin
5.6kil y a 15 jours
AdaptixC2 preview#8

AdaptixC2

GitHubadaptix-framework/adaptixc2
3.5kil y a 1 mois
emp3r0r preview#9

emp3r0r

GitHubjm33-m0/emp3r0r
1.7kil y a 1 jour
metasploit-framework preview#12

metasploit-framework

GitHubrapid7/metasploit-framework
38.8kil y a 9h 8m
kubesploit preview#13

kubesploit

GitHubcyberark/kubesploit
1.2kil y a 1 an
NetExec preview#14

NetExec

GitHubpennyw0rth/netexec
5.8kil y a 1 jour
impacket preview#15

impacket

GitHubfortra/impacket
16.0kil y a 1 jour
Plus récentsPertinencePlus populairesMis à jour récemment
2535 résultats
doublepulsar-c2-traffic-decryptor preview

doublepulsar-c2-traffic-decryptor

GitHubwithsecurelabs/doublepulsar-c2-traffic-decryptor

Un script python2 pour le traitement d'un fichier PCAP afin de déchiffrer le trafic C2 envoyé à l'implant DOUBLEPULSAR
packet-sniffing-analysisencryption-decryption-toolsexploitation+3
225il y a 9 ans
thorse preview

thorse

GitHubpushpenderindia/thorse

THorse est un générateur de RAT (Remote Administrator Trojan) pour les systèmes Windows/Linux écrit en Python 3.
password-crackingexploit-frameworkspayload-generation+6
614il y a 3 ans
Malleable-C2-Randomizer preview

Malleable-C2-Randomizer

GitHubbluscreenofjeff/malleable-c2-randomizer

Un script pour randomiser les profils C2 malléables de Cobalt Strike et réduire les risques de déclencher les contrôles de détection basés sur les…
exploit-frameworkspayload-generationids-ips-evasion+3
454il y a 8 ans
gmailc2 preview

gmailc2

GitHubmachine1337/gmailc2

Un serveur C2 totalement indétectable qui communique via Google SMTP pour contourner les protections antivirus et les restrictions de trafic réseau.
payload-generationpersistence-mechanismsshellcode+4
486il y a 1 an
GoAT preview

GoAT

GitHubpetercunha/goat

🐐 GoAT (Golang Advanced Trojan) est un trojan qui utilise Twitter comme serveur C&C

privilege-escalationosint-social-engineeringpersistence-mechanisms+7
261il y a 9 ans
shells preview

shells

GitHub4ndr34z/shells

Script pour générer des revshells
payload-generationexploitationreverse-engineering+9
487il y a 2 ans
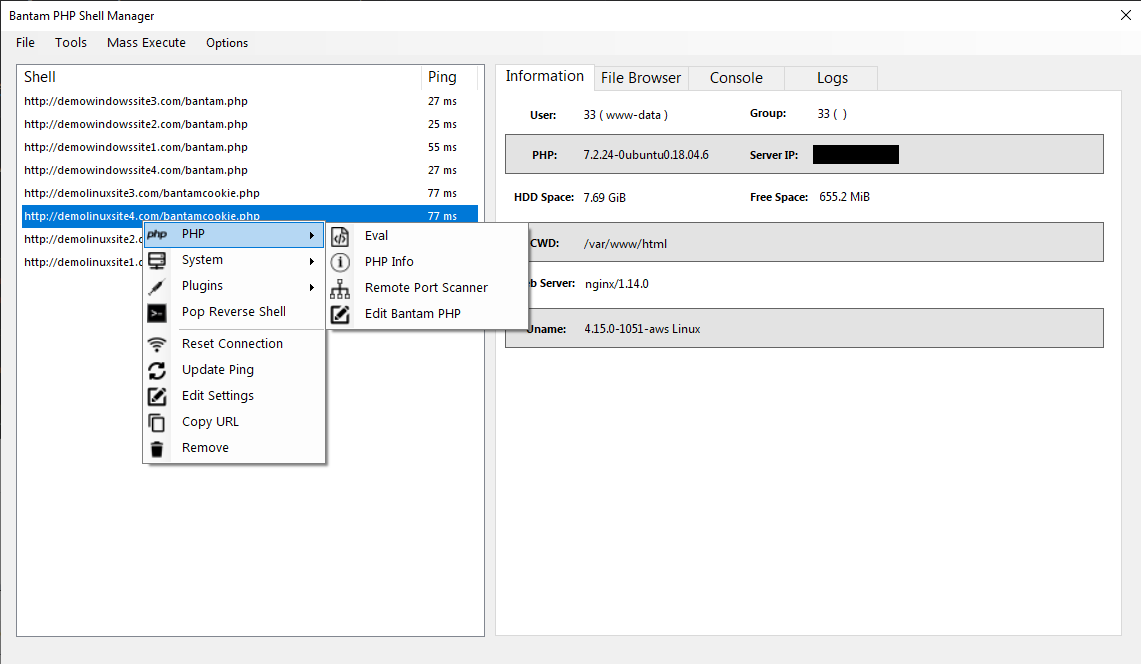
bantam preview

bantam

GitHubgellin/bantam

Un outil de gestion et de génération de backdoor PHP/C2 offrant un streaming de payload chiffré de bout en bout conçu pour contourner les systèmes…
encryption-decryption-toolspayload-generationids-ips-evasion+5
282il y a 4 ans
njRAT preview

njRAT

GitHubmwsrc/njrat

Extraction du code source de njRAT
privilege-escalationpayload-generationpersistence-mechanisms+9
310il y a 9 ans
botnet-hackpack preview

botnet-hackpack

GitHubtreehacks/botnet-hackpack

Construire un botnet de commande et contrôle de base en C

persistence-mechanismsmalware-analysiscommand-and-control+3
403il y a 7 ans
nah preview

nah

GitHubmanuelschipper/nah

un garde-fou qui bloque les actions catastrophiques des agents
privilege-escalationcontainer-securitydynamic-analysis-sandboxing+8
464il y a 10 jours
quasibot preview

quasibot

GitHubsmaash/quasibot

gestionnaire de webshell complexe, botnet quasi-http.
reconnaissancepassword-attacksexploitation+6
284il y a 11 ans
GRAT2 preview

GRAT2

GitHubr3nhat/grat2

Nous avons développé le projet GRAT2 de Commande et Contrôle (C2) à des fins d'apprentissage.
privilege-escalationpost-exploitationcommand-and-control+3
411il y a 5 ans
TelegramRAT preview

TelegramRAT

GitHubmachine1337/telegramrat

RAT multiplateforme basé sur Telegram qui communique via Telegram pour contourner les restrictions réseau.
information-gatheringpost-exploitationcommand-and-control+3
446il y a 1 an
GhostTunnel preview

GhostTunnel

GitHubpegasuslab/ghosttunnel

Outil de transmission furtive de porte dérobée utilisant les trames de requête de sonde et de balise 802.11 pour des attaques sur réseaux isolés.…
post-exploitationwireless-securitycommand-and-control+1
335il y a 7 ans
DNSStager preview

DNSStager

GitHubmhaskar/dnsstager

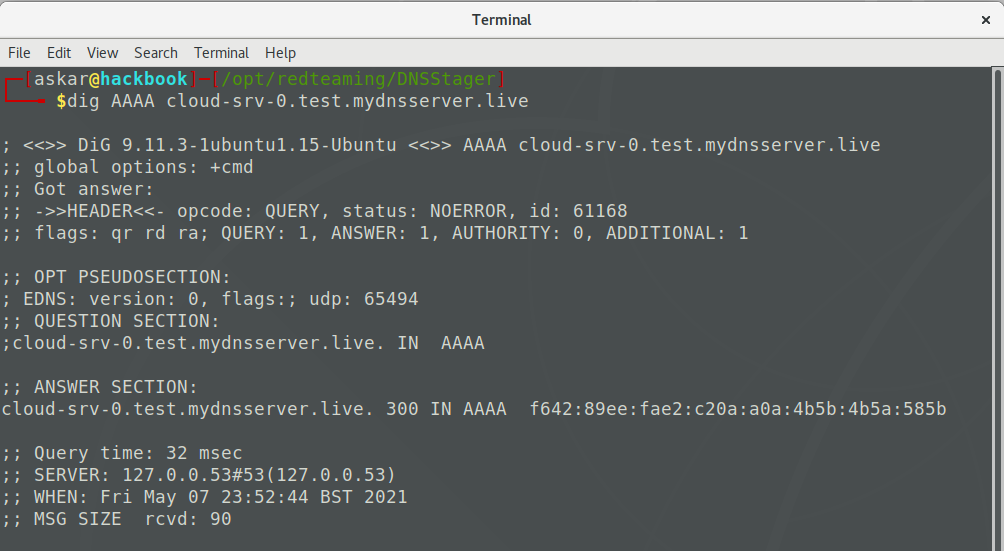
Cacher votre payload dans le DNS
payload-generationexploitationcommand-and-control+3
622il y a 3 ans
spawn preview

spawn

GitHubboku7/spawn

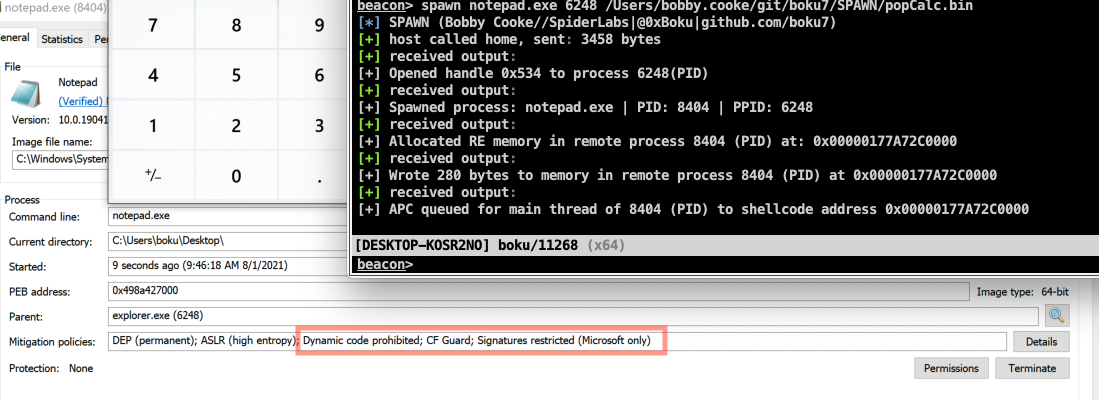
Cobalt Strike BOF qui génère un processus sacrificiel, l'injecte avec du shellcode et exécute la charge utile. Conçu pour contourner les hooks…
privilege-escalationexploitationshellcode+5
467il y a 3 ans
egressbuster preview

egressbuster

GitHubtrustedsec/egressbuster

Egressbuster est une méthode pour vérifier le filtrage de sortie et identifier si les ports sont autorisés. S'ils le sont, vous pouvez…
network-securitypenetration-testingcommand-and-control
374il y a 5 ans
SSHPry2.0 preview

SSHPry2.0

GitHubnopernik/sshpry2.0

SSHPry v2 - Espionner et contrôler le TTY des clients connectés SSH

phishing-toolspost-exploitationcommand-and-control+2
401il y a 9 ans
Précédent1…131415…100Suivant








