 onsec-fr/cve-2020-0688-scanner
Herramienta rápida para verificar CVE-2020-0688 en múltiples hosts con un método no intrusivo.

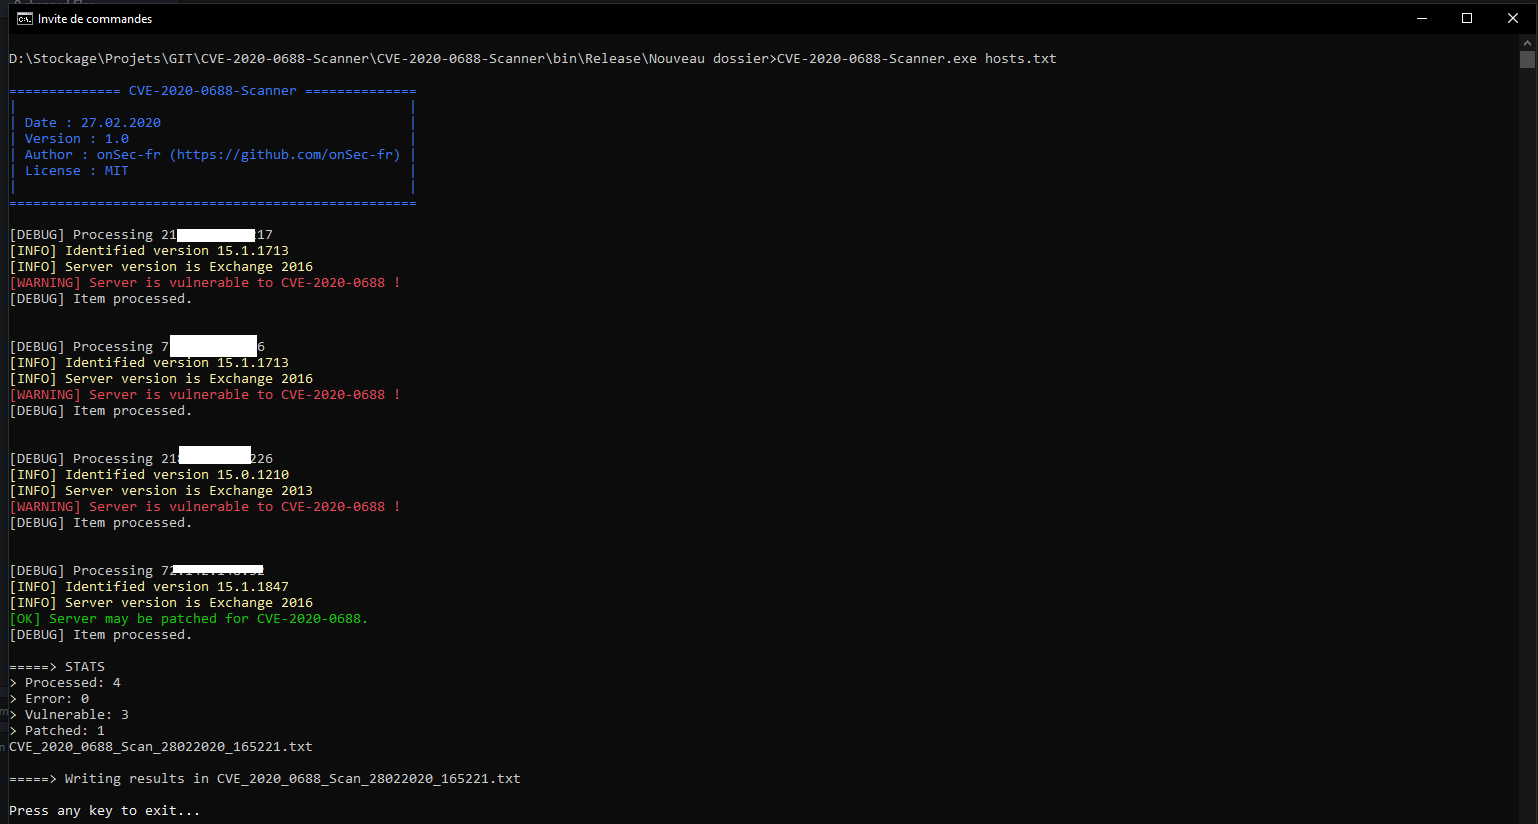
Quick C# tool for checking CVE-2020-0688 on multiple hosts with a non-intrusive method.

git clone https://github.com/onSec-fr/CVE-2020-0688-Scanner.git
./CVE-2020-0688-Scanner.exe [path_to_input_file]
Note : the input file can contain ip addresses, hostnames and FQDN.
This tool has been developed to test your own system or for authorized security testing. Make sure you check with your local laws before running this tool.
Since Exchange 2013, only the first 3 parts of the version number can be retrieved in this way. This means that sometimes the server may be vulnerable if it has not the very last cumulative update. In this case the server is flagged as "maybe patched".
Descubre las herramientas más usadas por nuestra comunidad.
Sin datos de popularidad aún.
