
Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

··Feeds·Contacto·Privacidad·© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
Next.js_exploit_CVE-2024-34351 — Demostración educativa de una vulnerabilidad de Server-Side Request Forgery (SSRF) en Next.js (CVE-2024-34351), con ejemplos paso a paso de explotación y mitigación. | Kitploit
Herramientas/GitHubGitHub/avergnaud/next.js_exploit_cve-2024-34351
Análisis de VulnerabilidadesExplotación de Aplicaciones WebSeguridad WebAprendizaje y EducaciónLabs y Práctica
GitHubavergnaud/next.js_exploit_cve-2024-34351

Next.js_exploit_CVE-2024-34351

Demostración educativa de una vulnerabilidad de Server-Side Request Forgery (SSRF) en Next.js (CVE-2024-34351), con ejemplos paso a paso de explotación y mitigación.

Ver Repositorio
111hace 2 añosAún no revisado

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →
Compartir

csr-rsc-ssg-isr-ssr-ssrf

Este repositorio puede servir como soporte para presentar uno o varios meetup(s). El recorrido es el siguiente...

  • "CSR" Client Side Rendering: React como librería SPA estándar
  • "RSC" React Server Components: ejecución de componentes React únicamente del lado del servidor
  • "SSG" Static Site Generation: ejecución de componentes React durante el build
  • "ISR" Incremental Static Regeneration: regeneración de componentes a la demanda
  • "SSR" Server Side Rendering: pre-renderizado del lado del servidor y luego ejecución (hidratación) del lado del cliente
  • "SSRF" Server Side Request Forgery: una vulnerabilidad de seguridad corregida recientemente en Next.JS

Este trabajo se basa principalmente en dos fuentes:

  • https://demystifying-rsc.vercel.app/
  • https://www.assetnote.io/resources/research/digging-for-ssrf-in-nextjs-apps

mind map

CSR Client Side Rendering

1-csr-load-data vanilla react SPA loading data

mind map CSR

[!IMPORTANT] CSR (Client-Side Rendering): React code is delivered to the browser, which generates content that is inserted into the DOM.
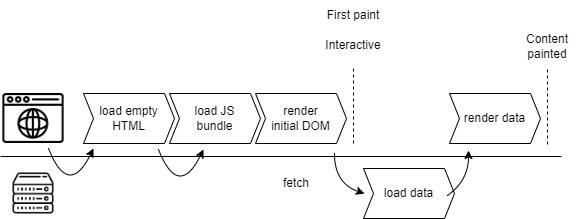
client side rendering loading data

demostración

cd 1-csr-load-data
npm start

CSR load data gif

2-csr-router vanilla react SPA routing

[!IMPORTANT] After the page has been loaded for the first time, navigating to other pages on the same website uses JavaScript to re-render parts of the page without requiring a full page refresh.

demostración

cd 2-csr-router
npm start

client side rendering routing

RSC React Server Components

3-rsc-load-data React Server Components (Next.js impl) loading data

mind map CSR

[!IMPORTANT] React components which are written to run only on the server, rather than in the browser.
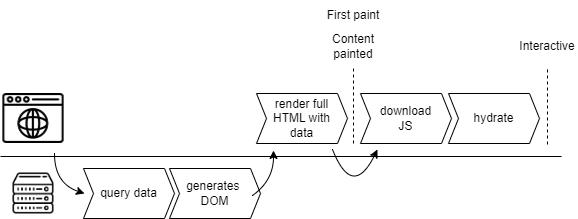
React Server Components loading data

demostración

cd 3-rsc-load-data
npm run build
npm run start
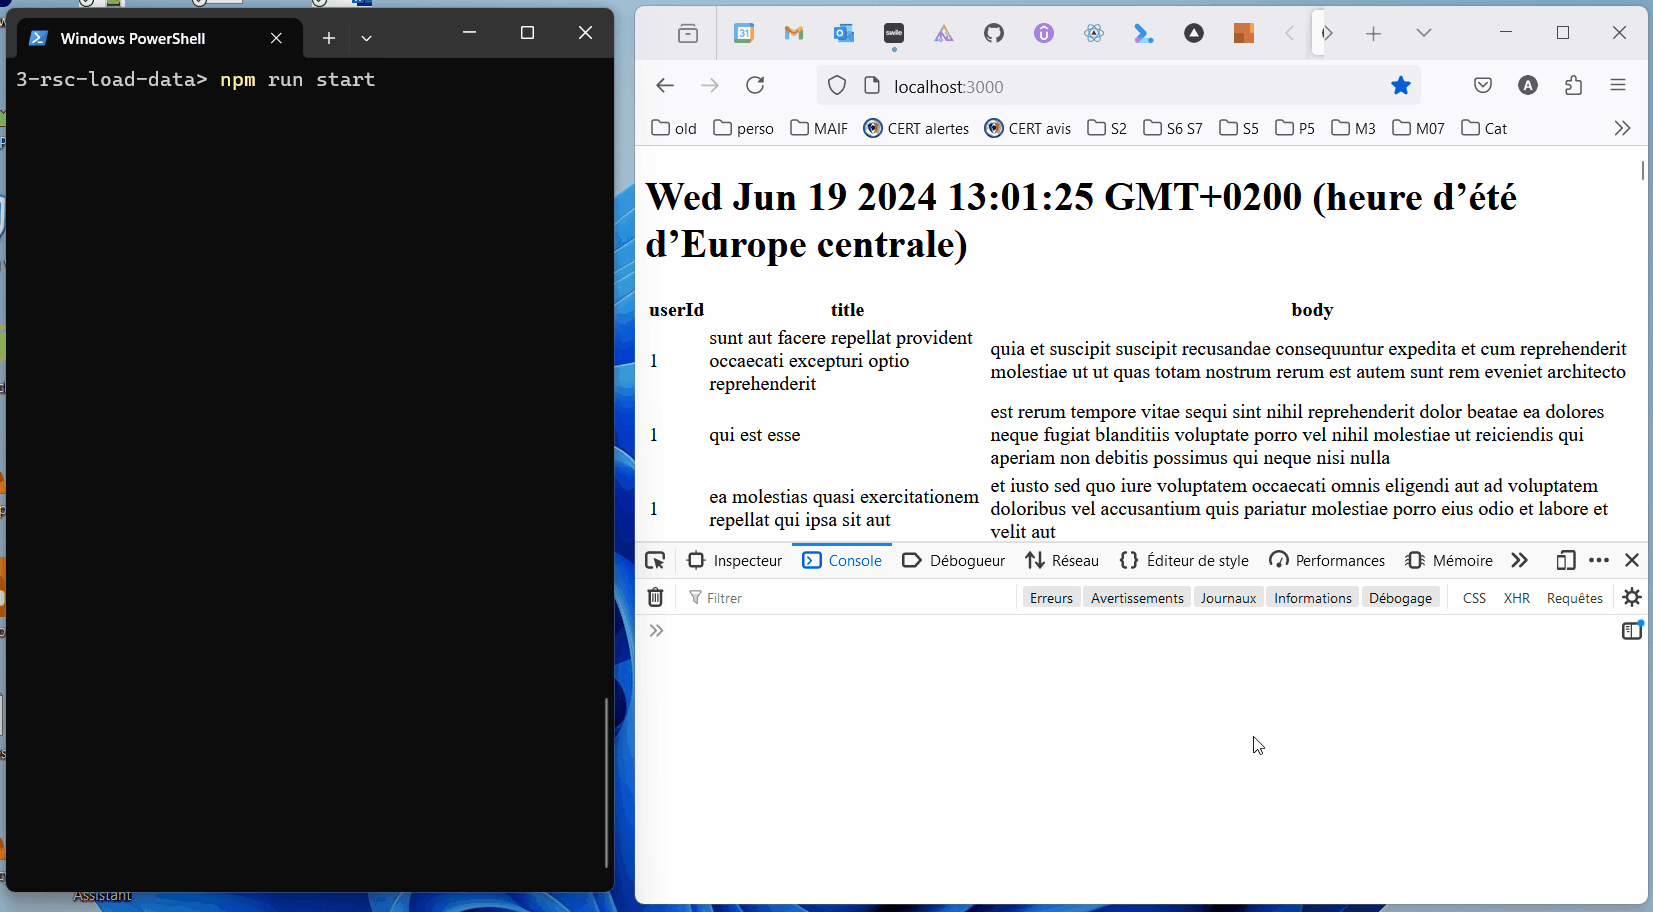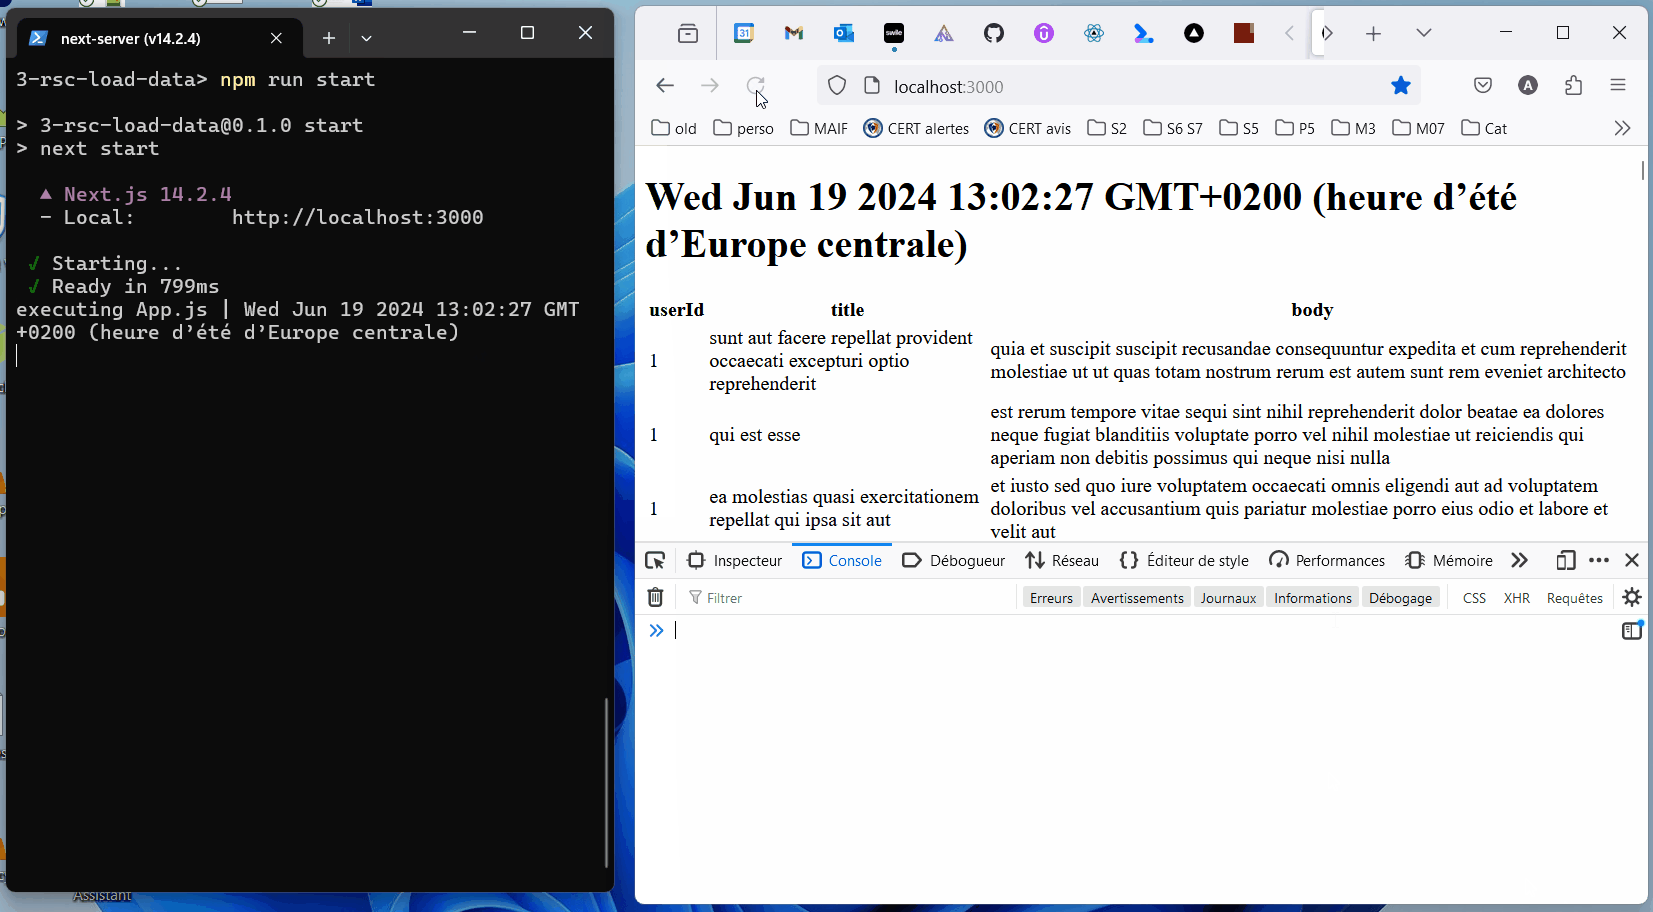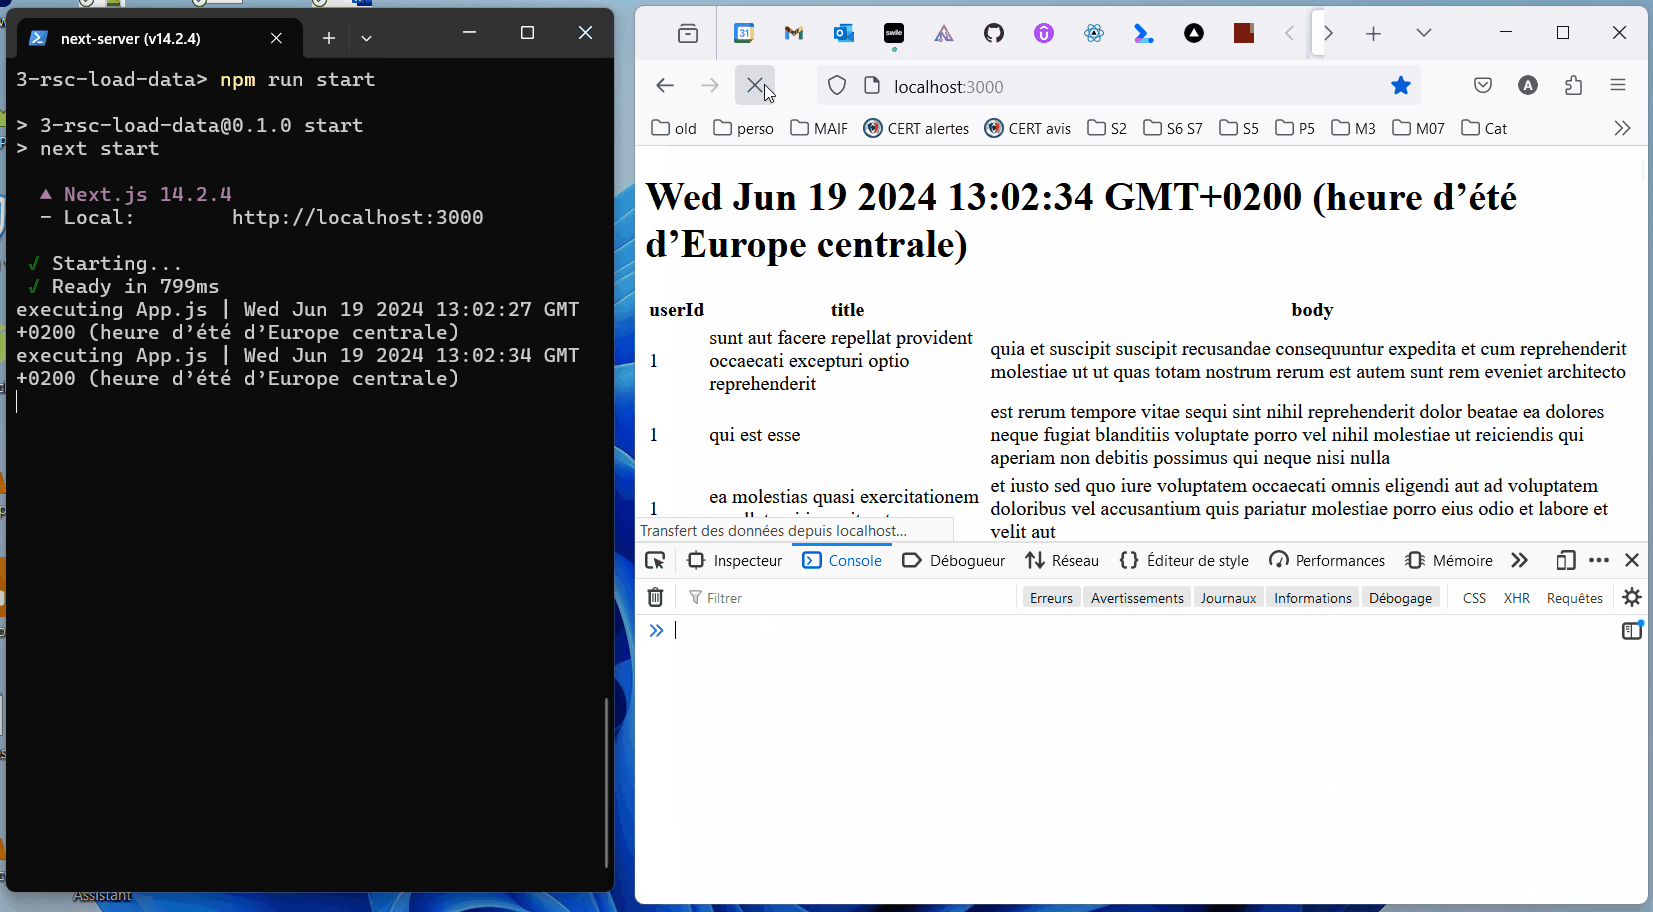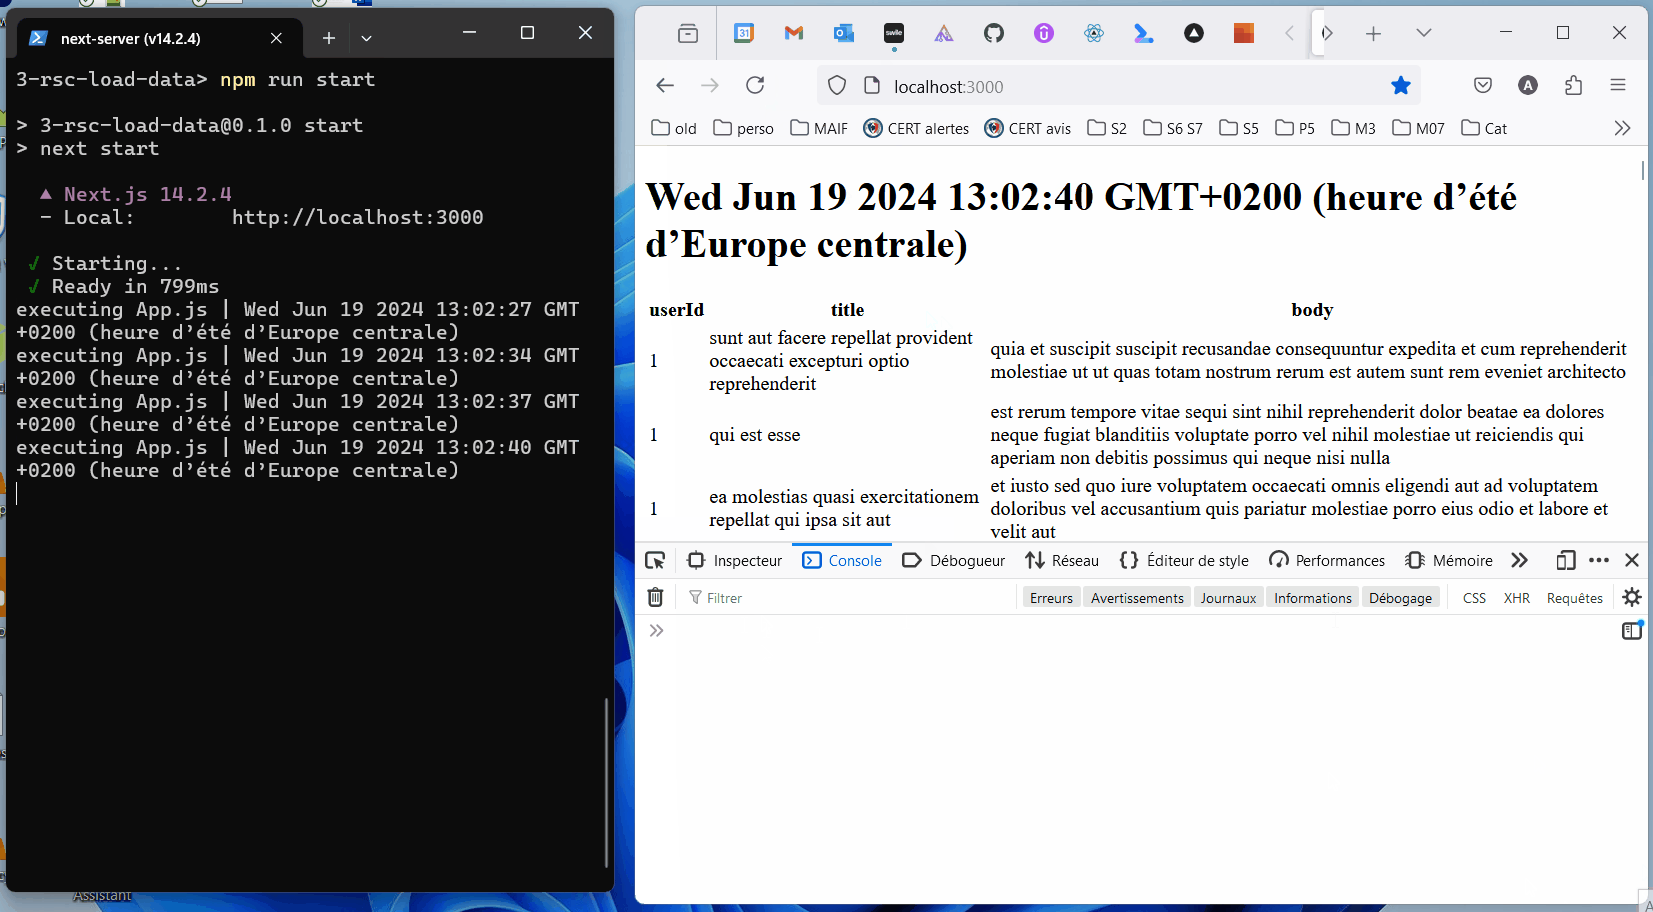
client side rendering routing

4-rsc-router React Server Components (Next.js impl) routing

mind map CSR

[!IMPORTANT] Components are executed only on the server. The default behavior is static rendering: components are executed at build time.

demostración

cd 4-rsc-router
npm run build
npm run start
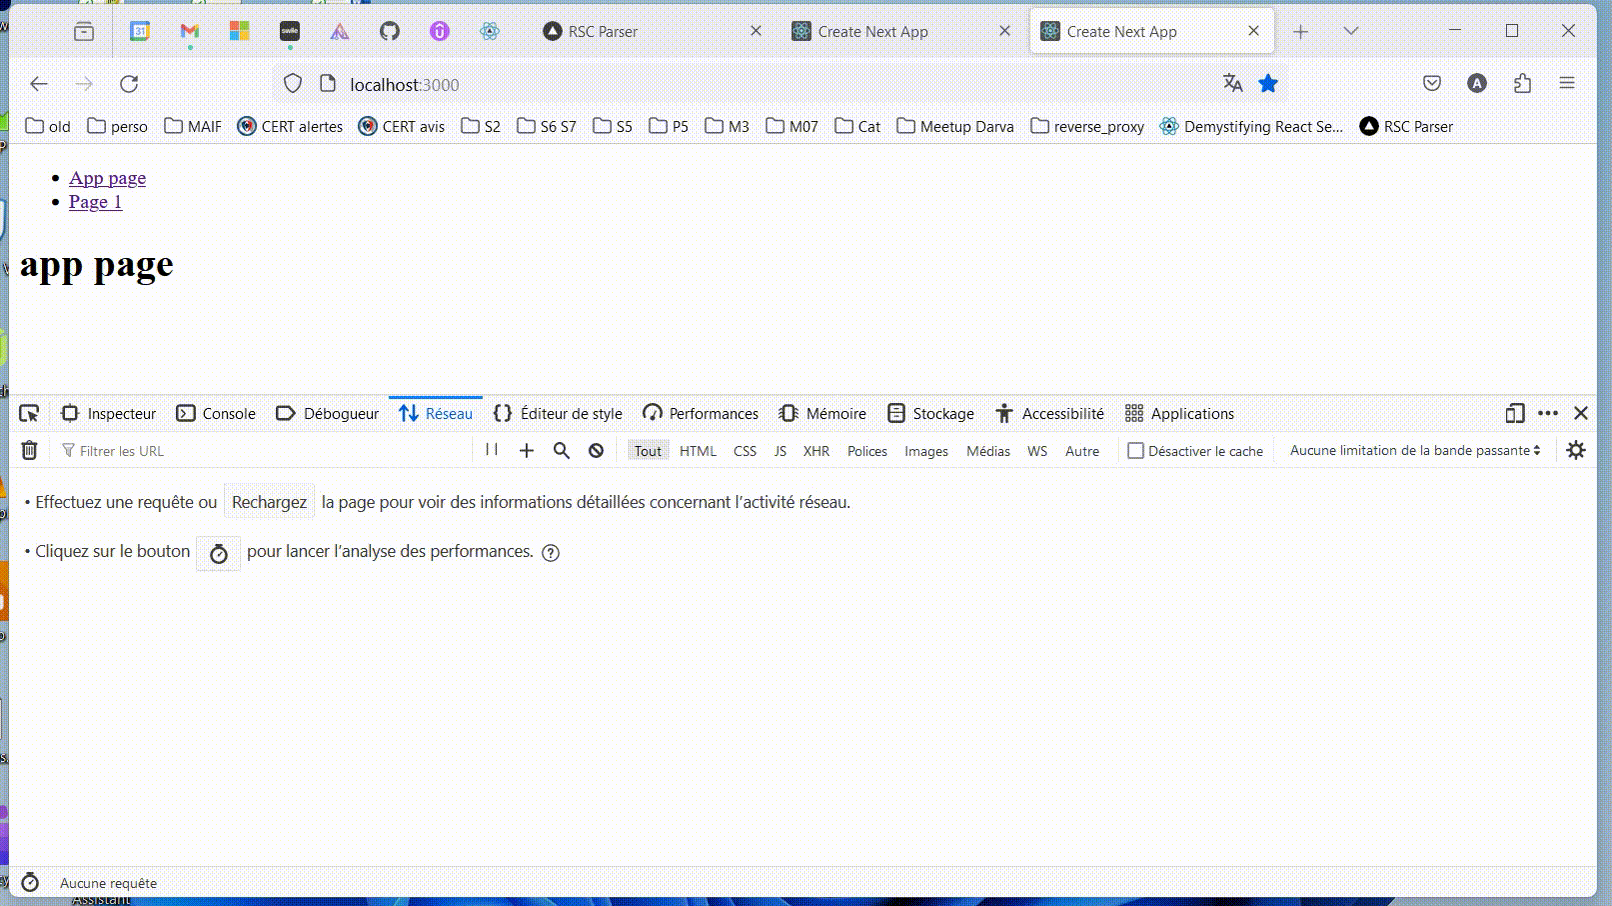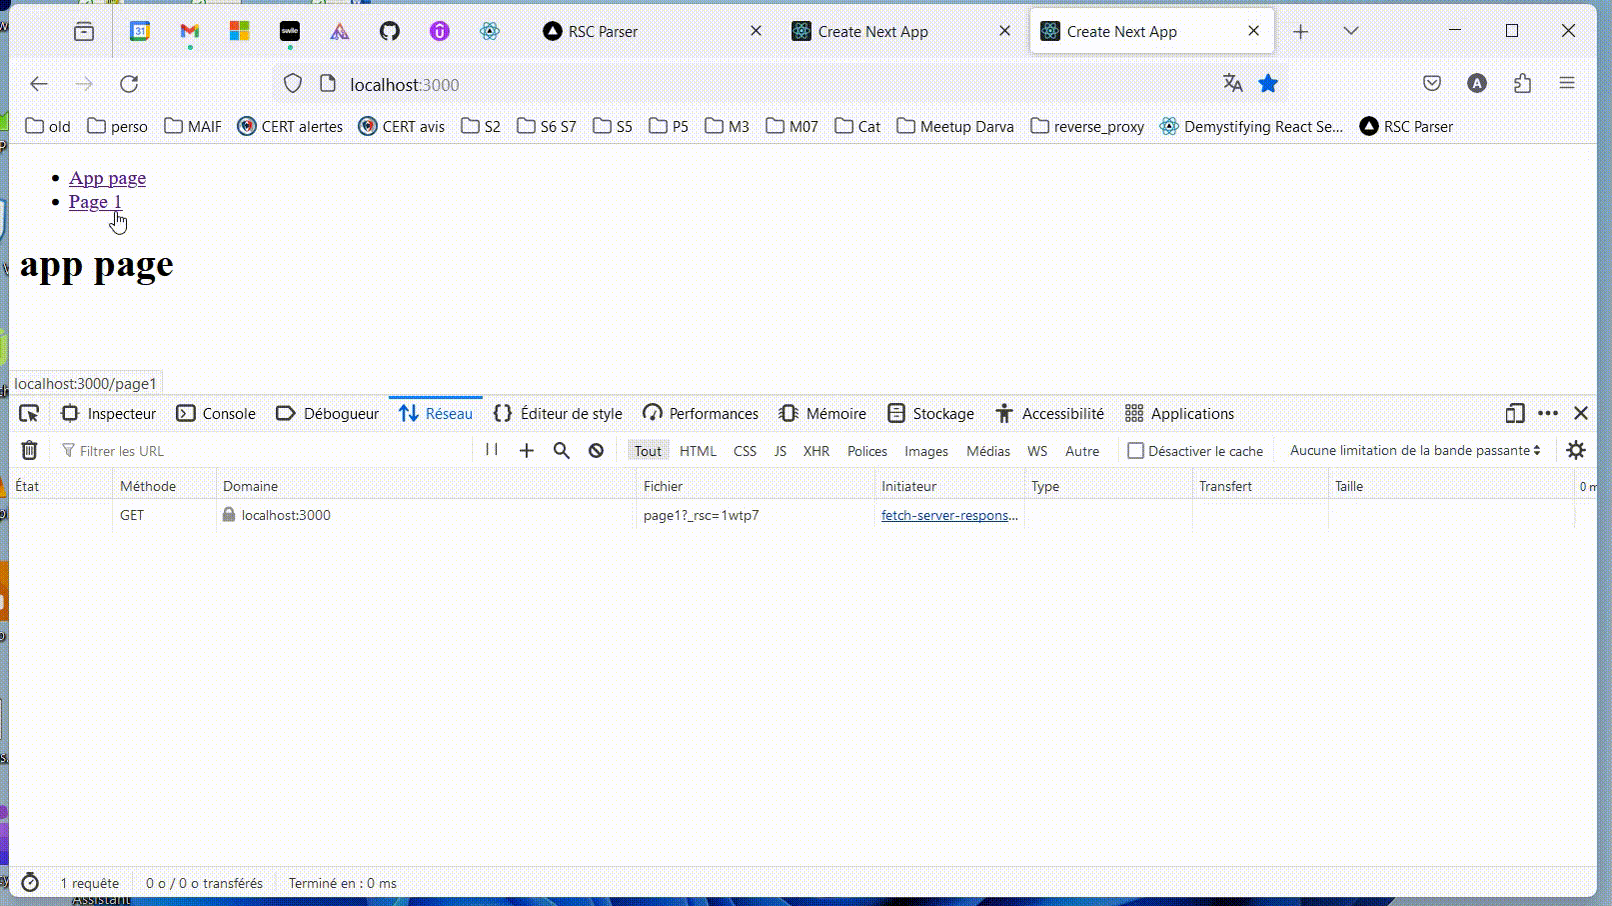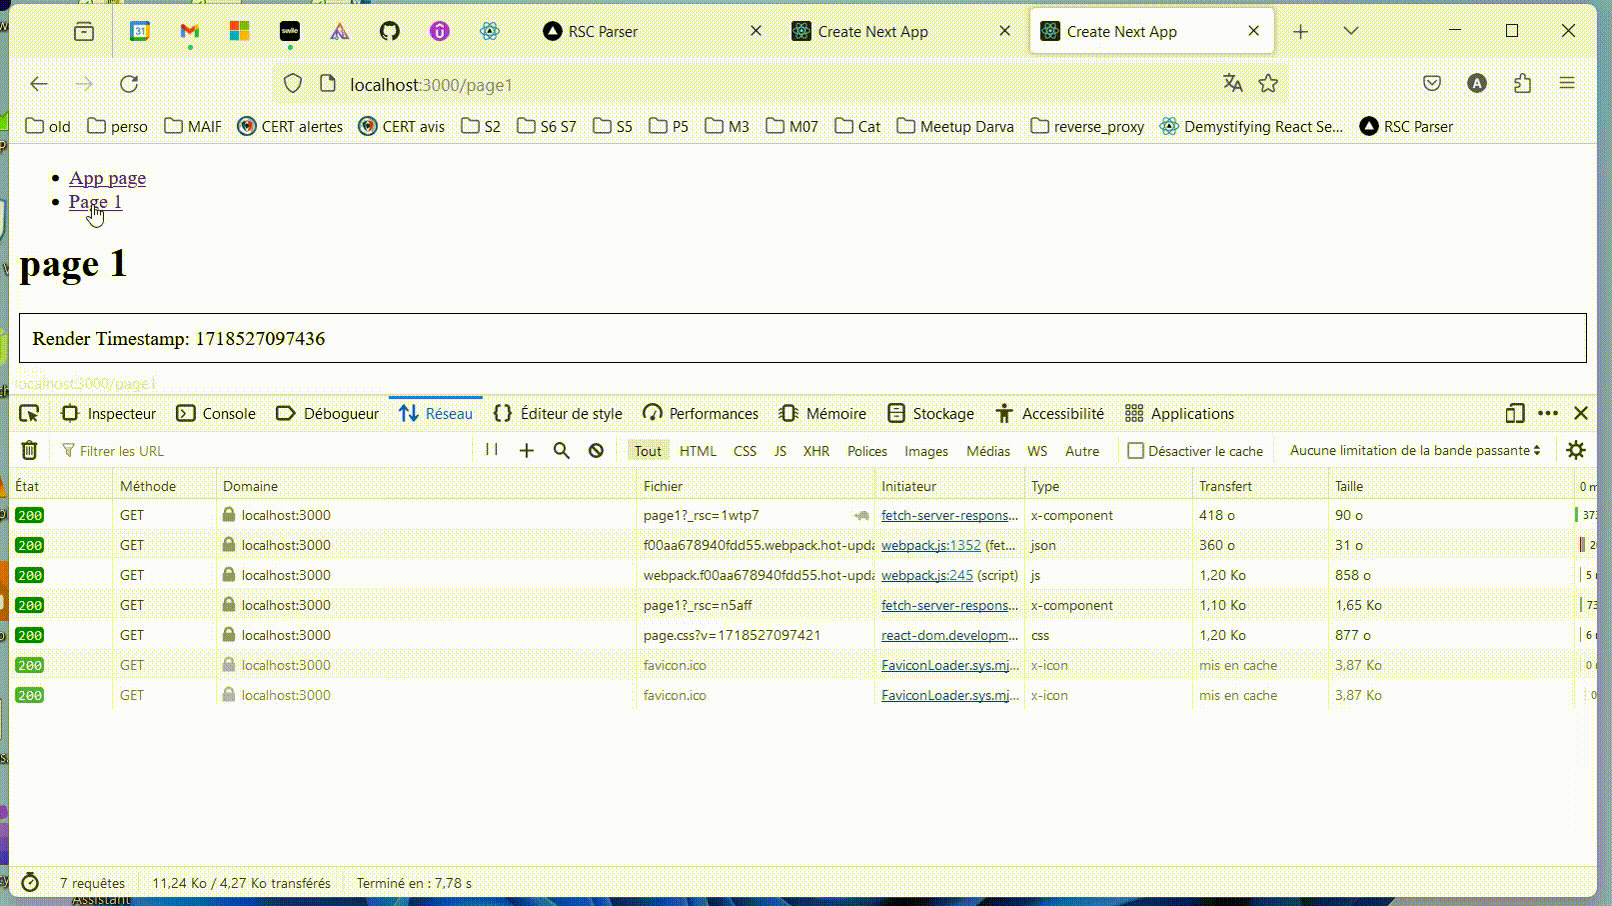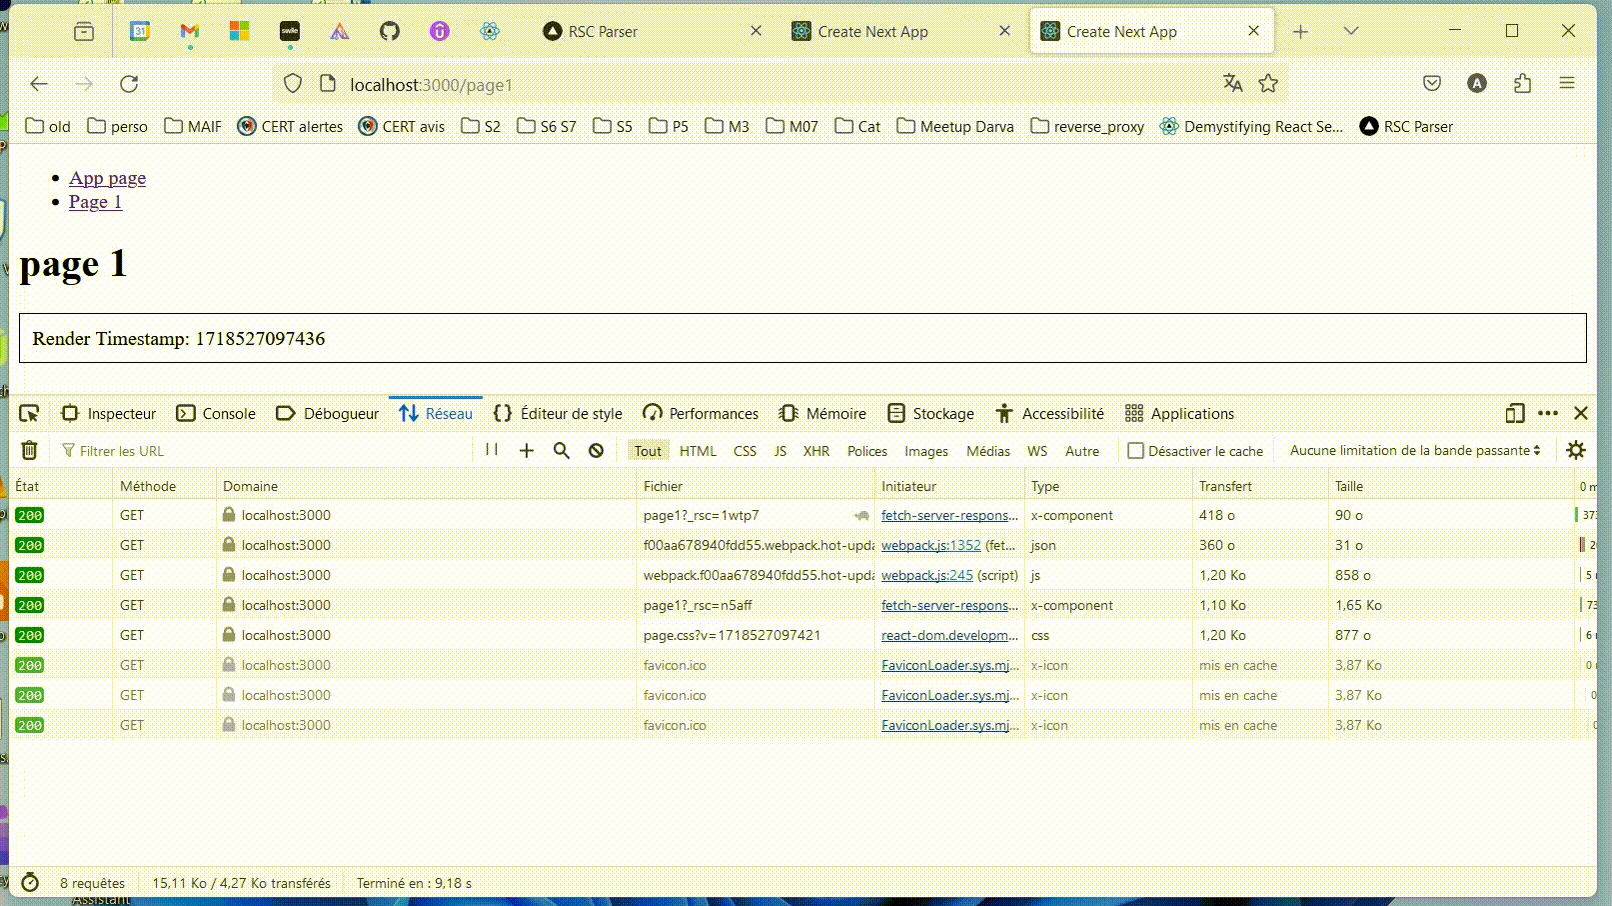
React server components routing

5-SSR SSR Server Side Rendering

mind map SSR

[!IMPORTANT] SSR means prerendering client components on the server. React code runs at the time it is requested. The result may be cached for future requests.

Best practice: define 'use client'; components as far down the component tree as possible.

https://nextjs.org/docs/app/building-your-application/rendering/composition-patterns#moving-client-components-down-the-tree

Hydration

[!IMPORTANT] "In React, “hydration” is how React “attaches” to existing HTML that was already rendered by React in a server environment. During hydration, React will attempt to attach event listeners to the existing markup and take over rendering the app on the client. In apps fully built with React, you will usually only hydrate one “root”, once at startup for your entire app."

https://react.dev/reference/react-dom/client/hydrateRoot

https://www.gatsbyjs.com/docs/conceptual/partial-hydration/

demostración

cd 5-ssr
npm run build
npm run start

SSR

6-pages-router-ssg (Next.js impl)

mind map page router SSG

[!IMPORTANT] SSG (Static Site Generation) using the pages router: React code is run when you build your application, and the generated output is static.

demostración

cd 6-pages-router-ssg
npm run build
npm run start

7-pages-router-isr (Next.js impl)

mind map page router ISR

[!IMPORTANT] ISR (using pages router): "Next.js allows you to create or update static pages after you’ve built your site. Incremental Static Regeneration (ISR) enables you to use static-generation on a per-page basis, without needing to rebuild the entire site. With ISR, you can retain the benefits of static while scaling to millions of pages."

demostración

cd 7-pages-router-isr
npm run build
npm run start

¿Por qué ISR?

"the data could become stale at request time"

https://vercel.com/blog/nextjs-server-side-rendering-vs-static-generation

Server actions

https://react.dev/reference/rsc/server-actions

SSRF (fixed in NextJS v14.1.1)

Definición SSRF

...

¿Por qué?

  • Si se tiene acceso a un servidor vulnerable pero no al servidor objetivo directamente (DMZ, Firewall...)
  • Si se quieren ejecutar peticiones ocultando el propio origen
  • ...

Demostración 8-ssrf-14.1.0

Contexto

SSRF A

https://www.assetnote.io/resources/research/digging-for-ssrf-in-nextjs-apps

Objetivo

SSRF B, objetivo

Condiciones para explotar la CVE-2024-34351

  • Una aplicación basada en Next.JS con versión inferior a 14.1.1
  • El uso de la función redirect, con una ruta absoluta. En la demo, en addTodo.js: redirect(/blog/${inputValue});

Funcionamiento de la función redirect

Descargar herramienta