

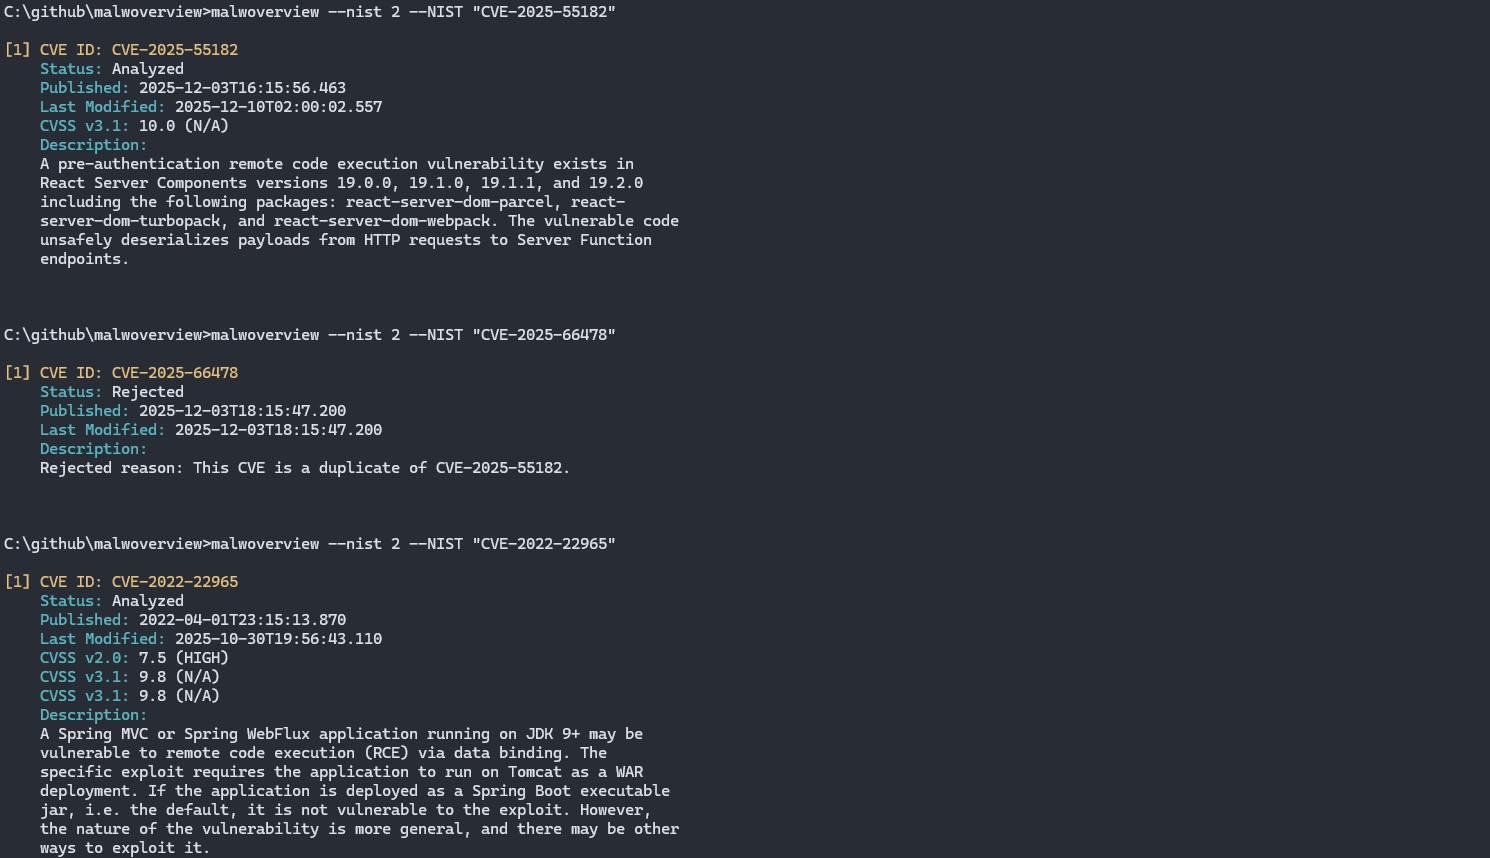
Malwoverview es una herramienta de primera respuesta para la caza de amenazas en VirusTotal, Hybrid Analysis, URLHaus, Polyswarm, Malshare, Alien Vault, Malpedia, Malware Bazaar, ThreatFox, Triage, IPInfo, Shodan, AbuseIPDB, GreyNoise, URLScan.io, Whois/RDAP, NIST y VulnCheck. Compatible con enriquecimiento mediante LLM, extracción de IOC, análisis con YARA y análisis de Android.






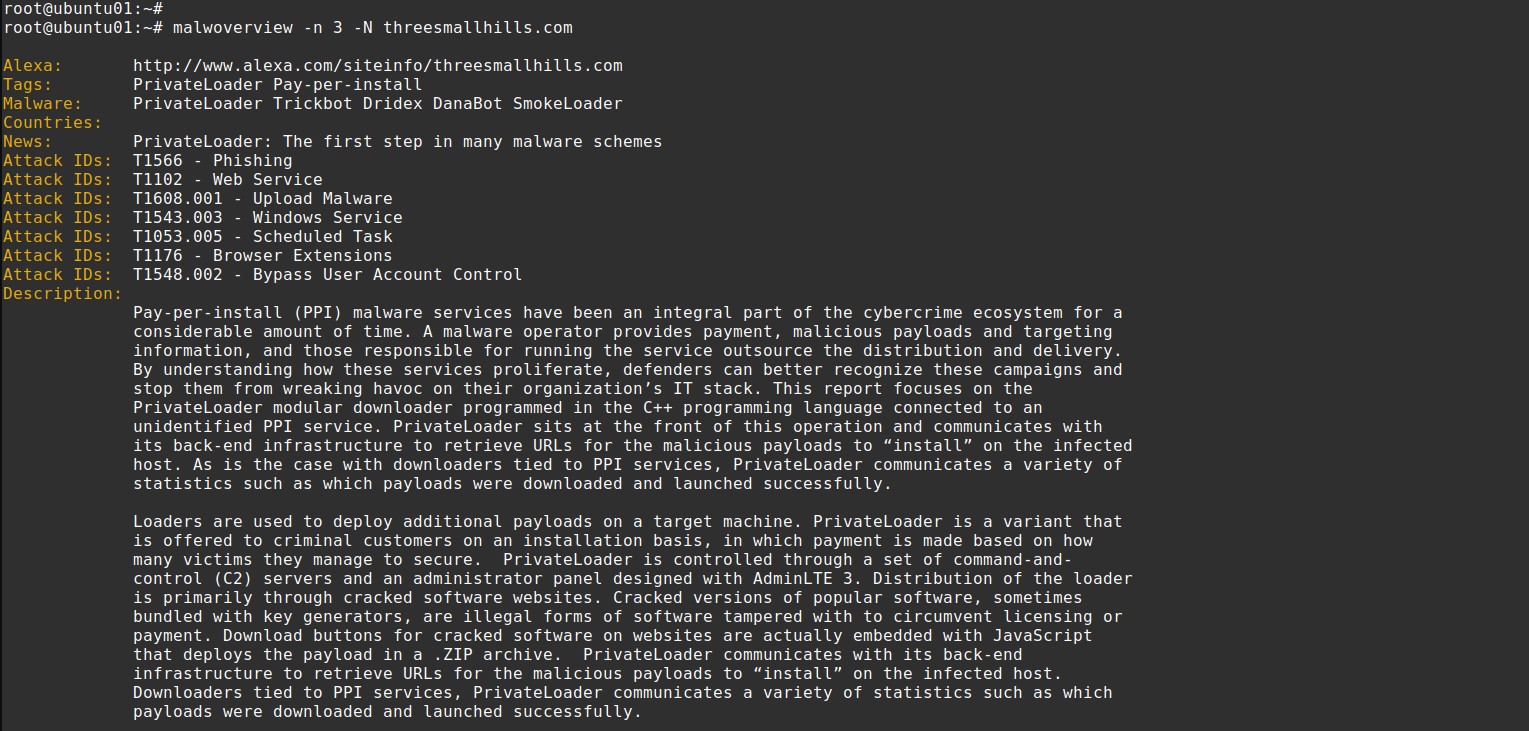
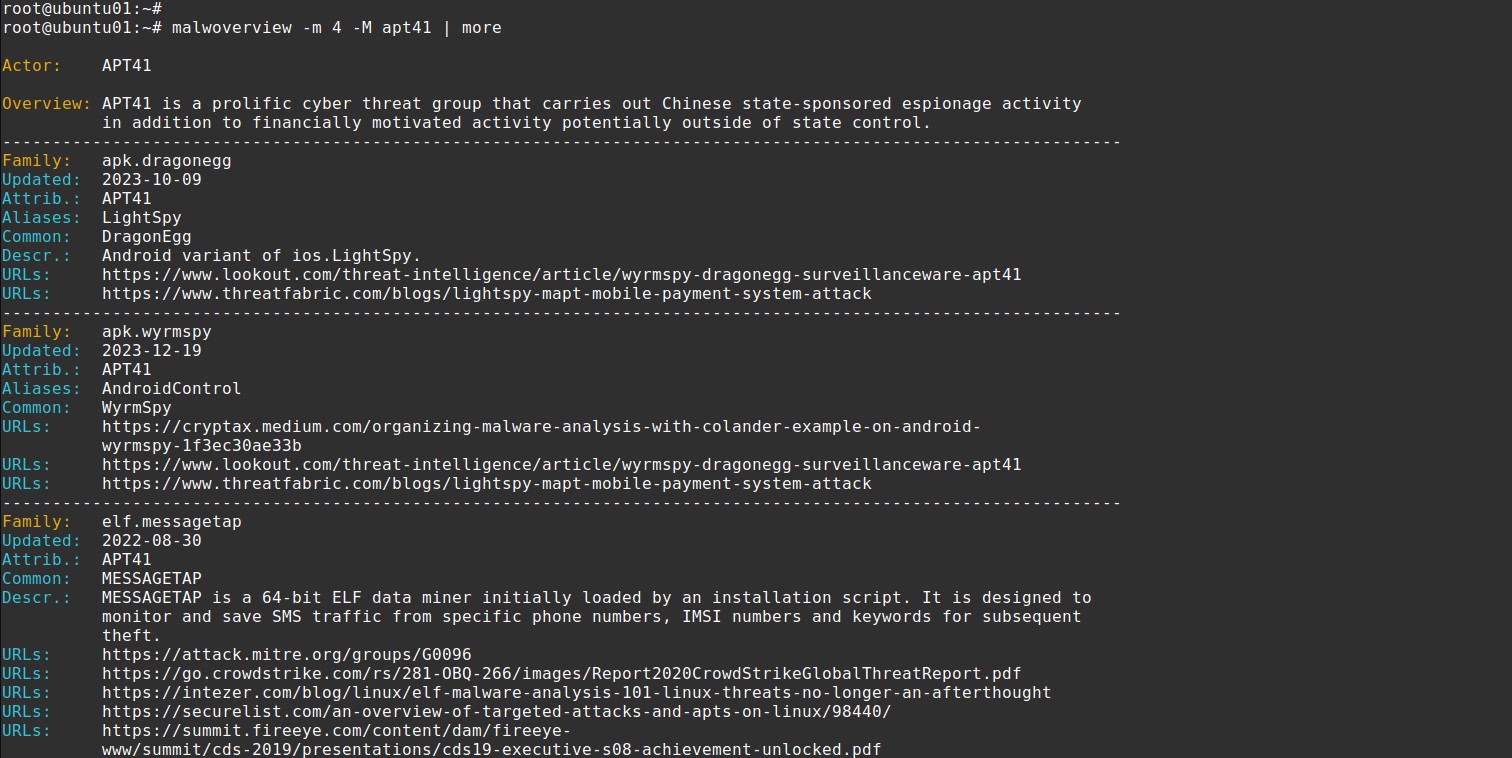
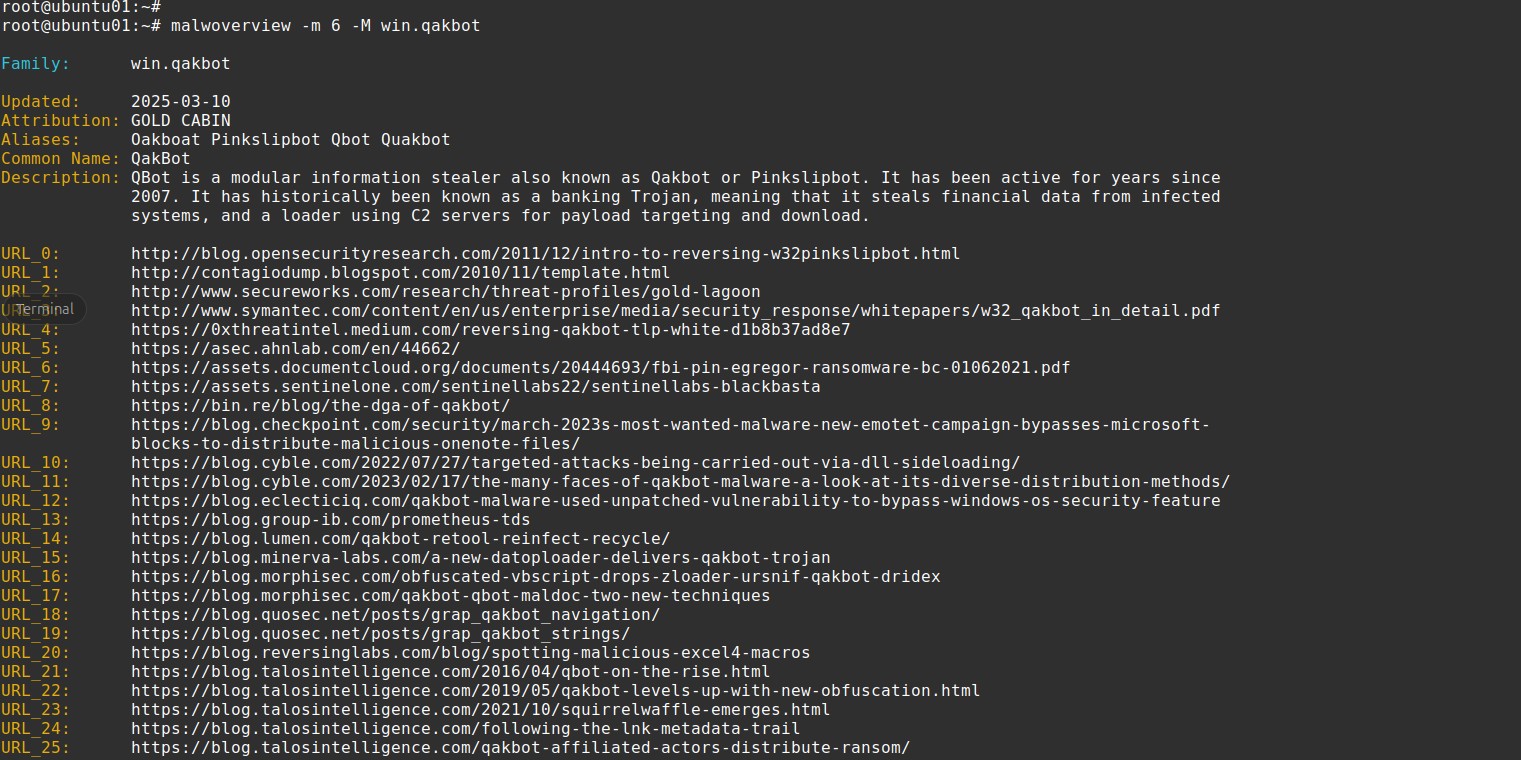
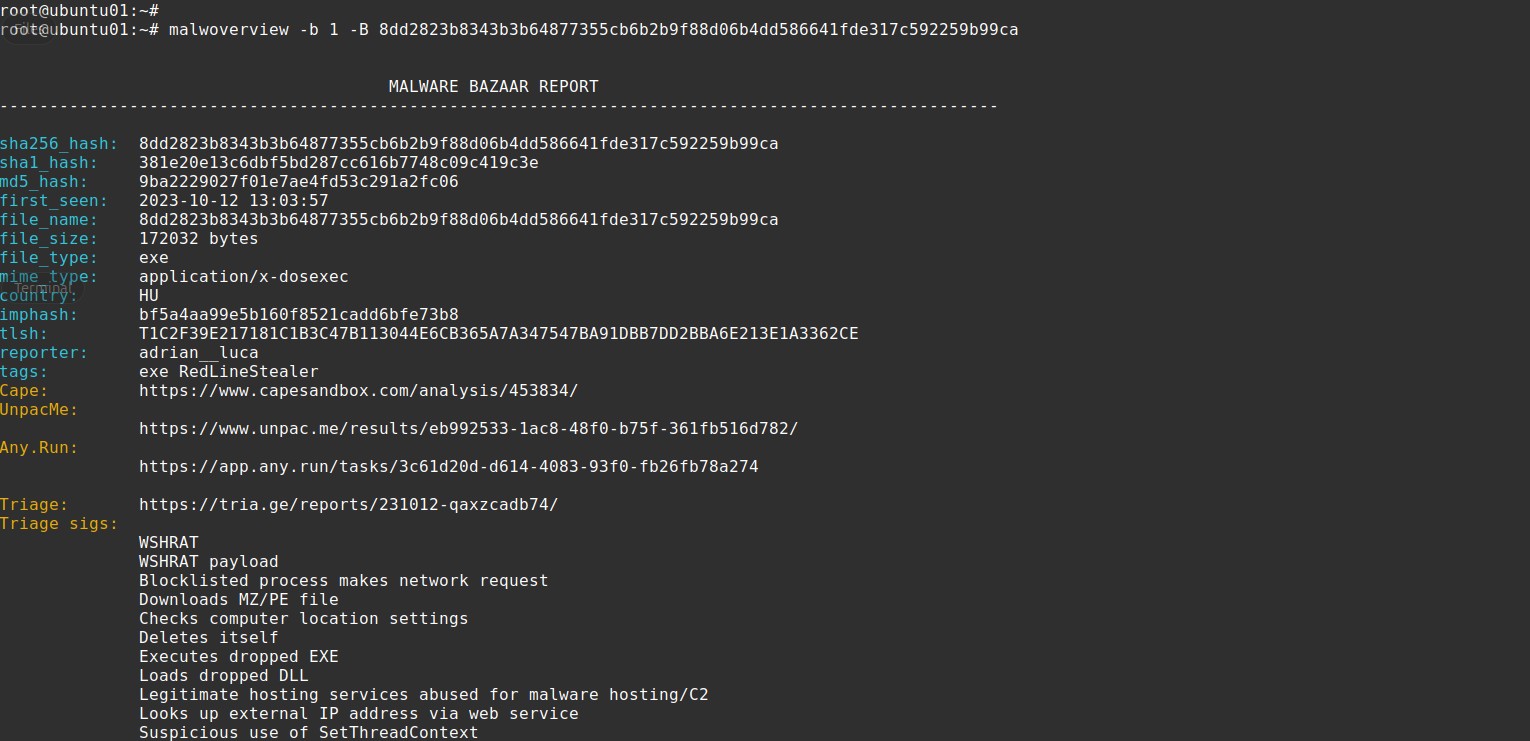




  Copyright (C)  2018-2026 Alexandre Borges (https://exploitreversing.com)

  This program is free software: you can redistribute it and/or modify
  it under the terms of the GNU General Public License as published by
  the Free Software Foundation, either version 3 of the License, or
  (at your option) any later version.

  This program is distributed in the hope that it will be useful,
  but WITHOUT ANY WARRANTY; without even the implied warranty of
  MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE.  See the
  GNU General Public License for more details.

  See GNU Public License on <http://www.gnu.org/licenses/>.
 Nota importante:  Malwoverview NO envía muestras a ningún endpoint de forma predeterminada,
 por lo que respeta posibles Acuerdos de Confidencialidad (NDAs). Existen opciones específicas
 que envían muestras de forma explícita, pero estas opciones se explican en la ayuda.
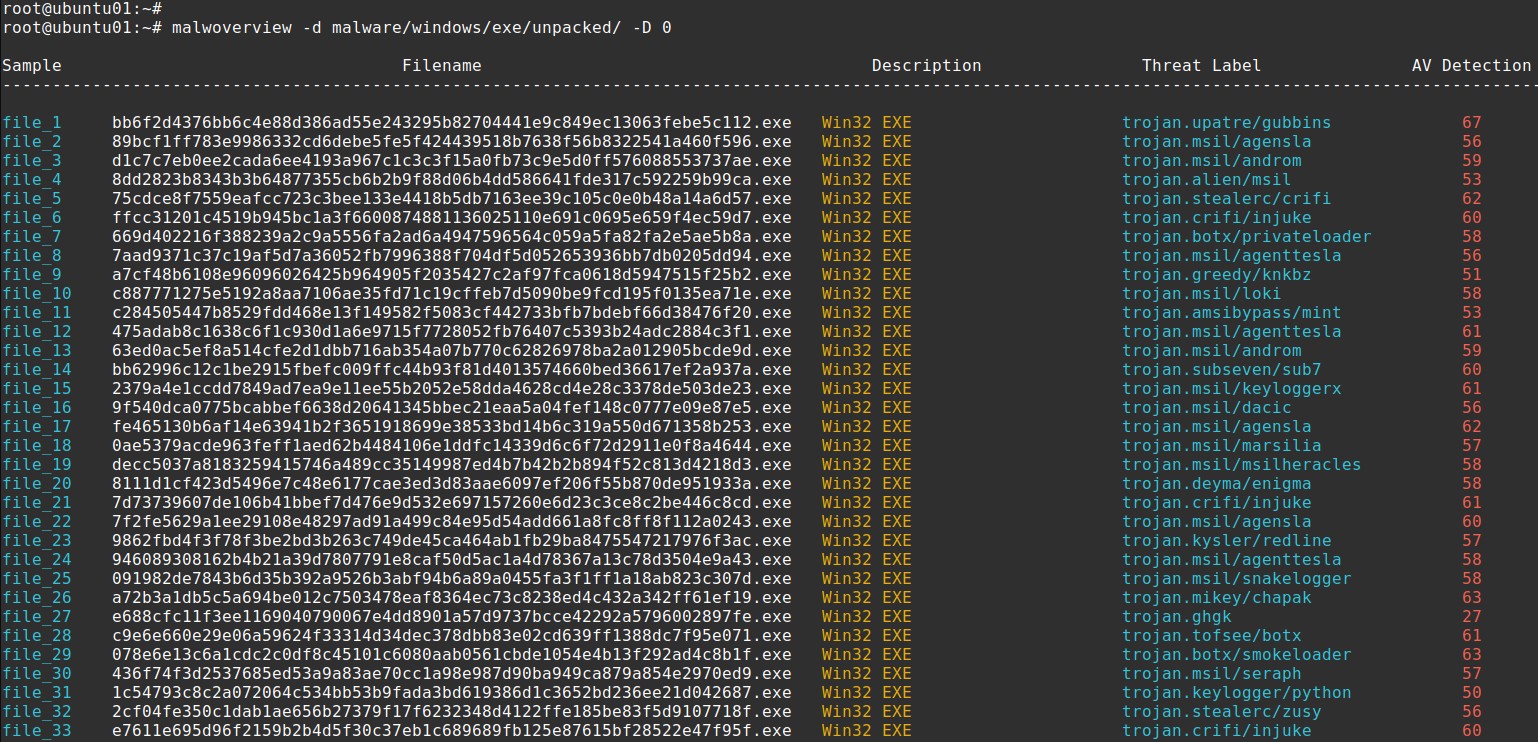
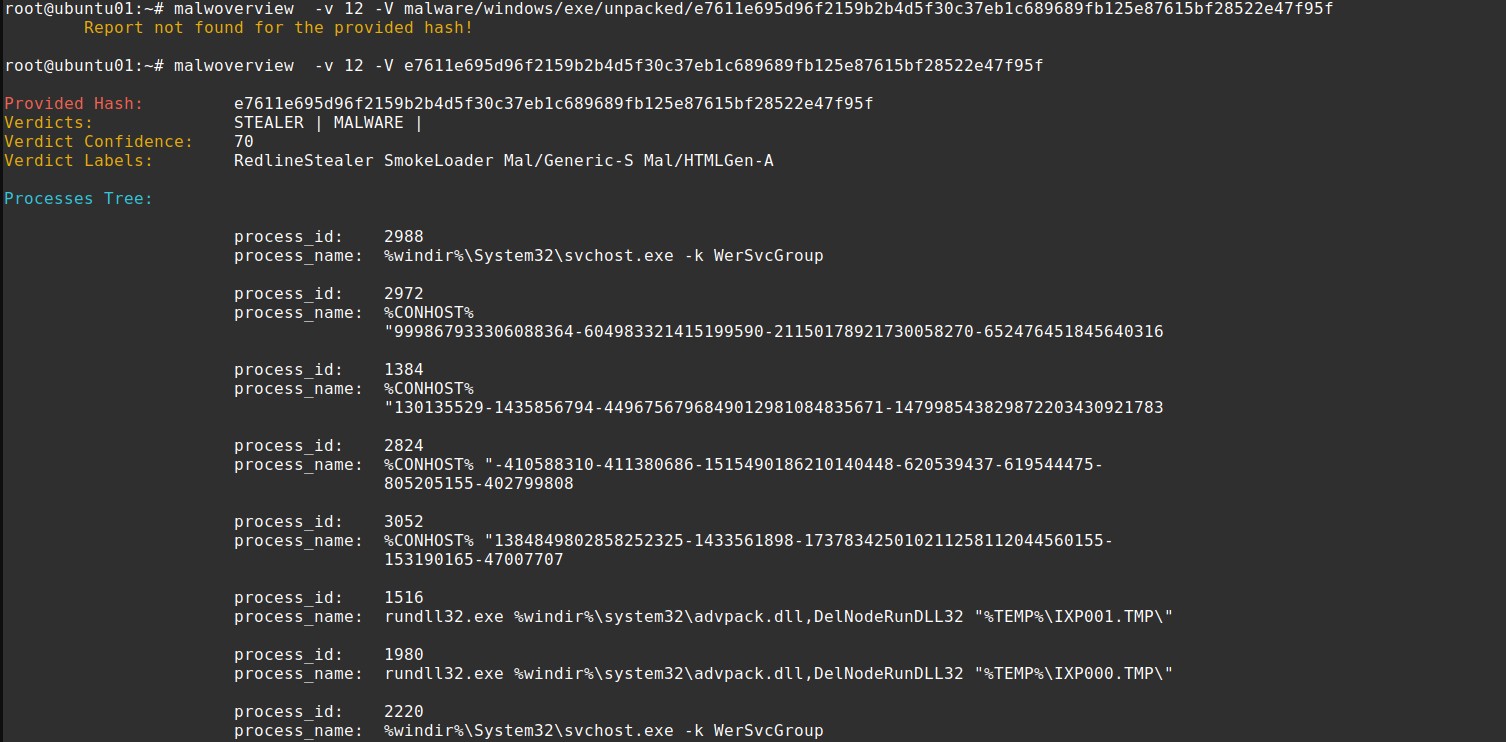
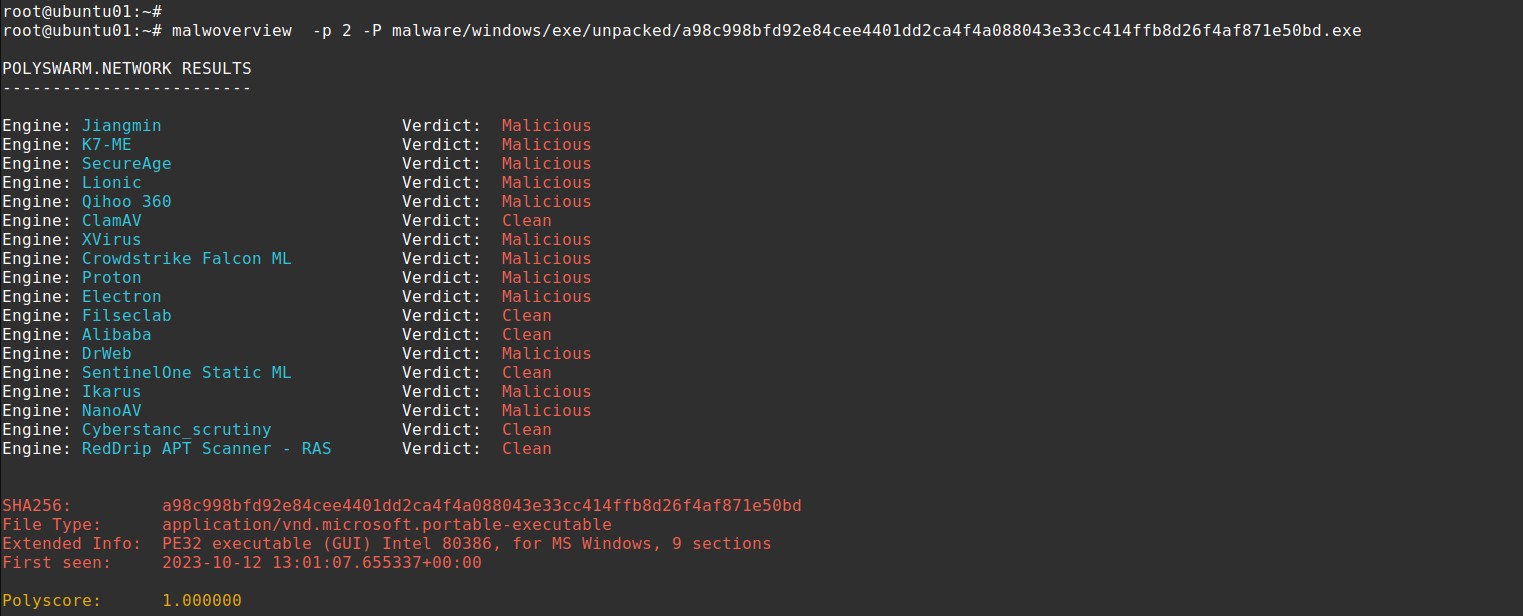
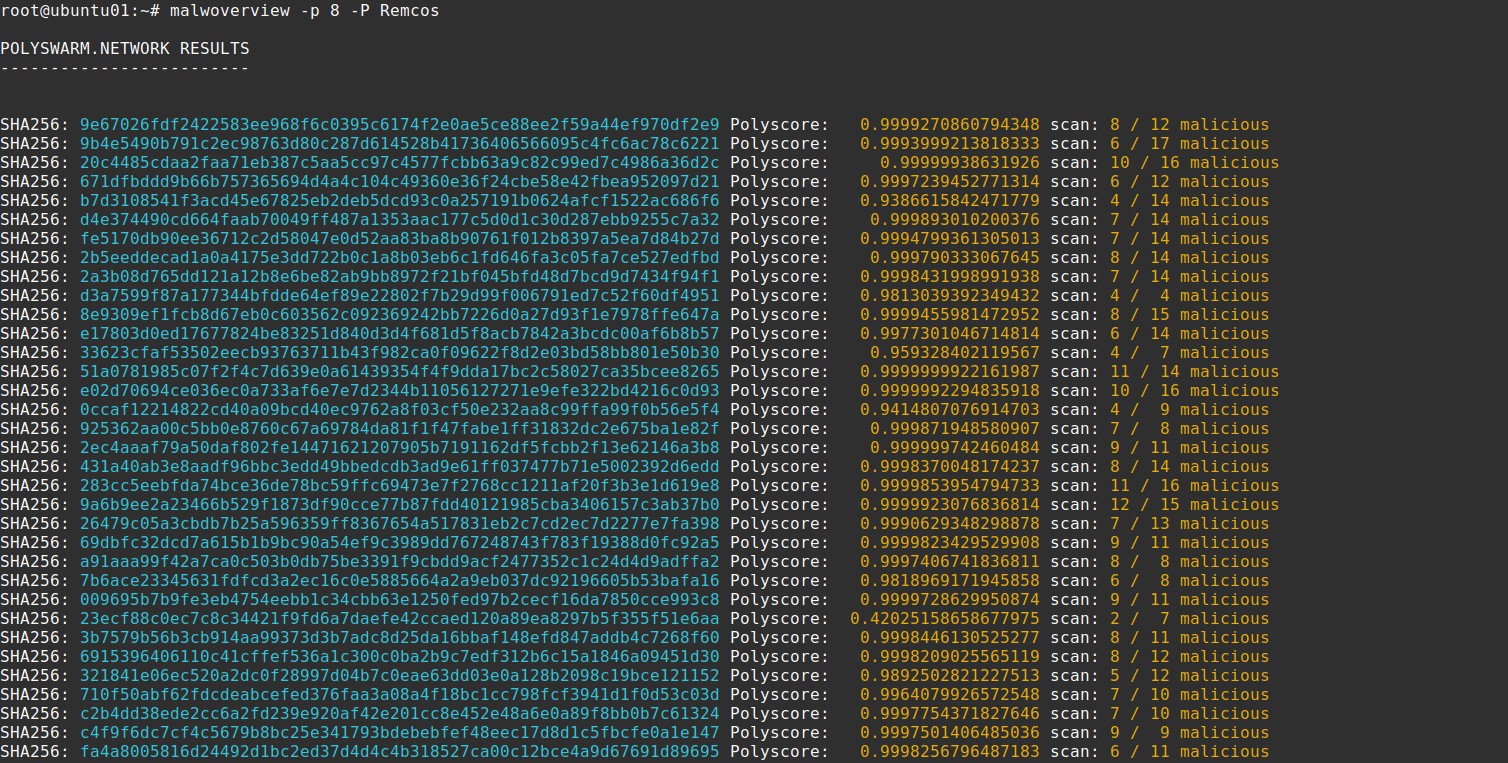
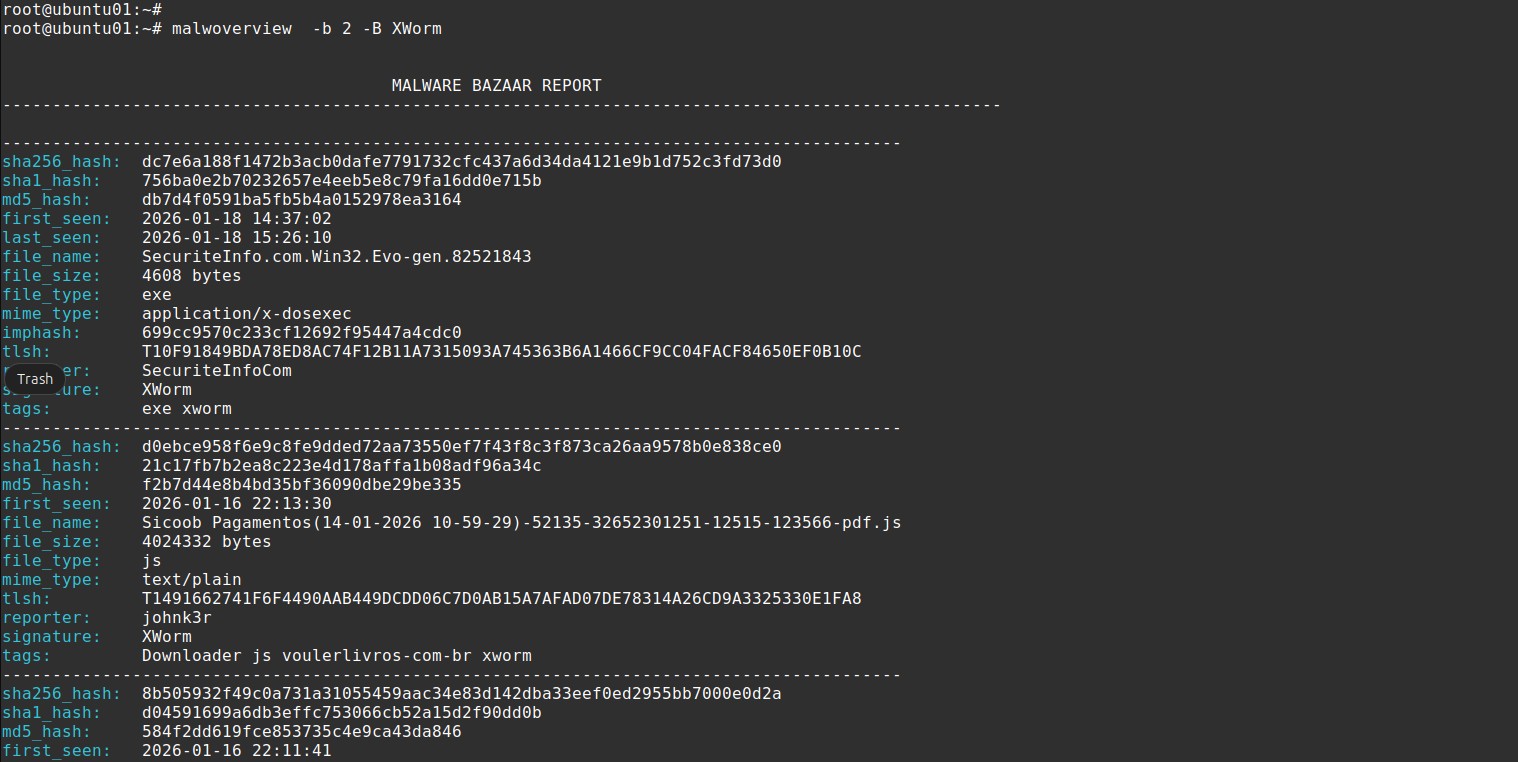
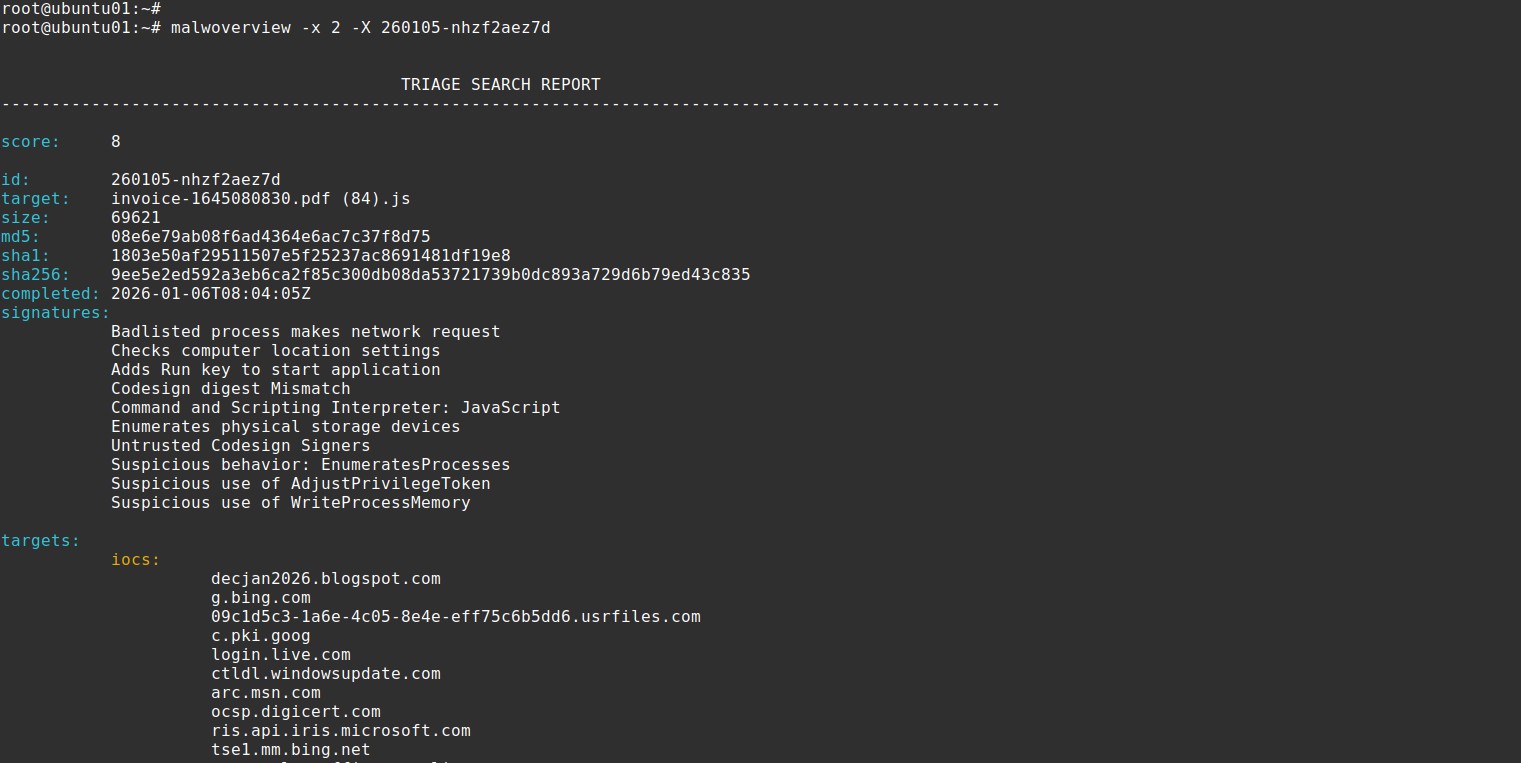
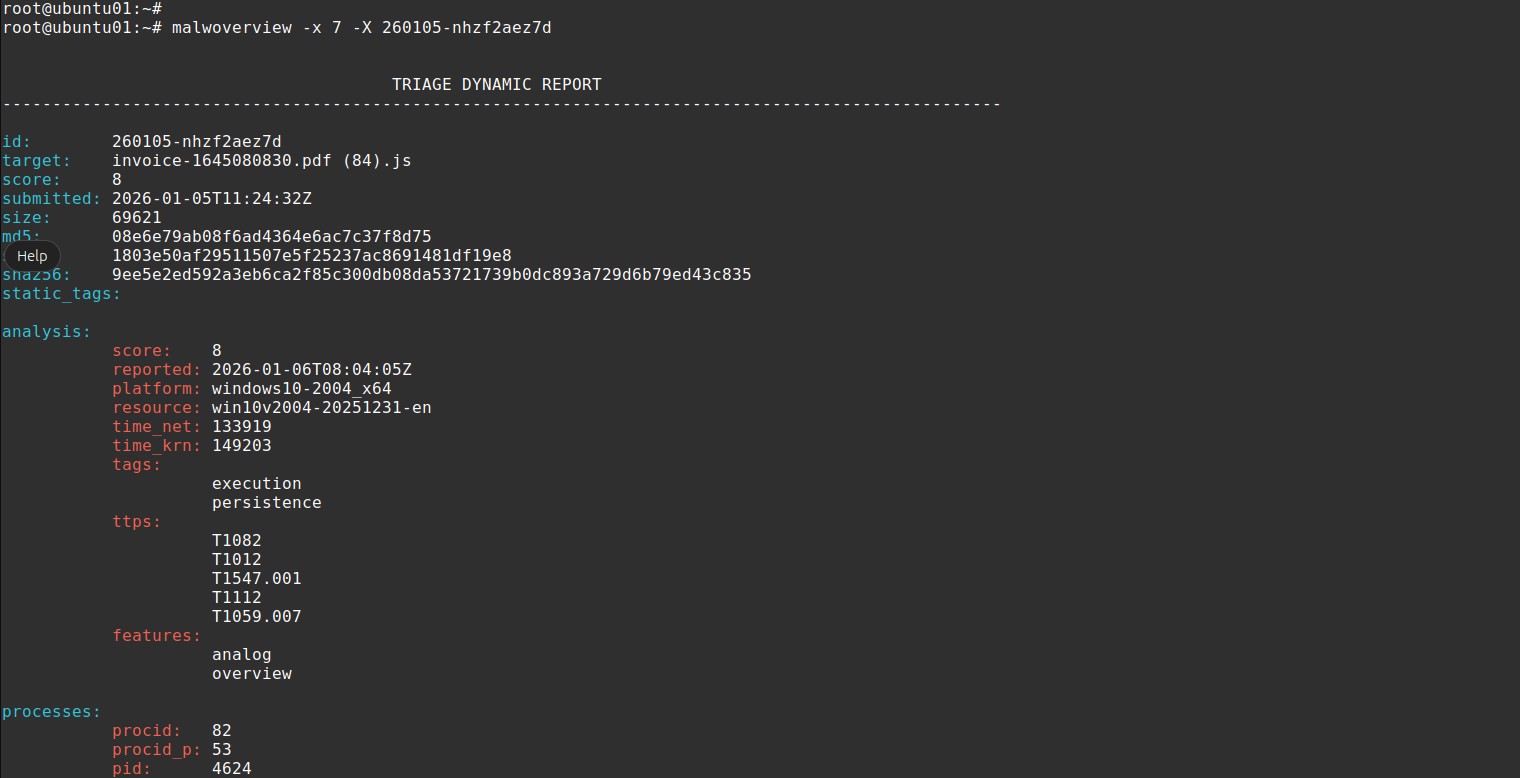
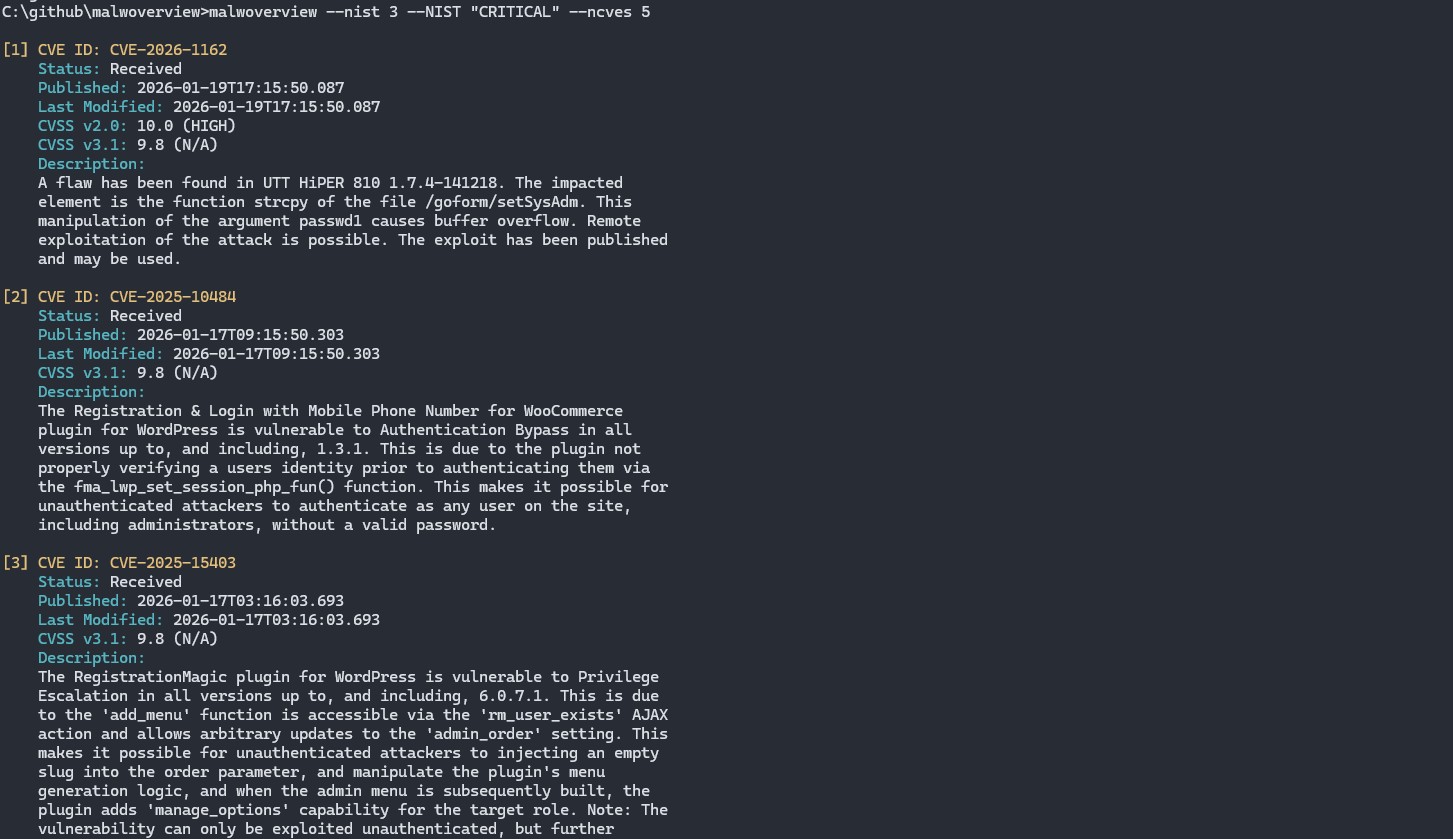
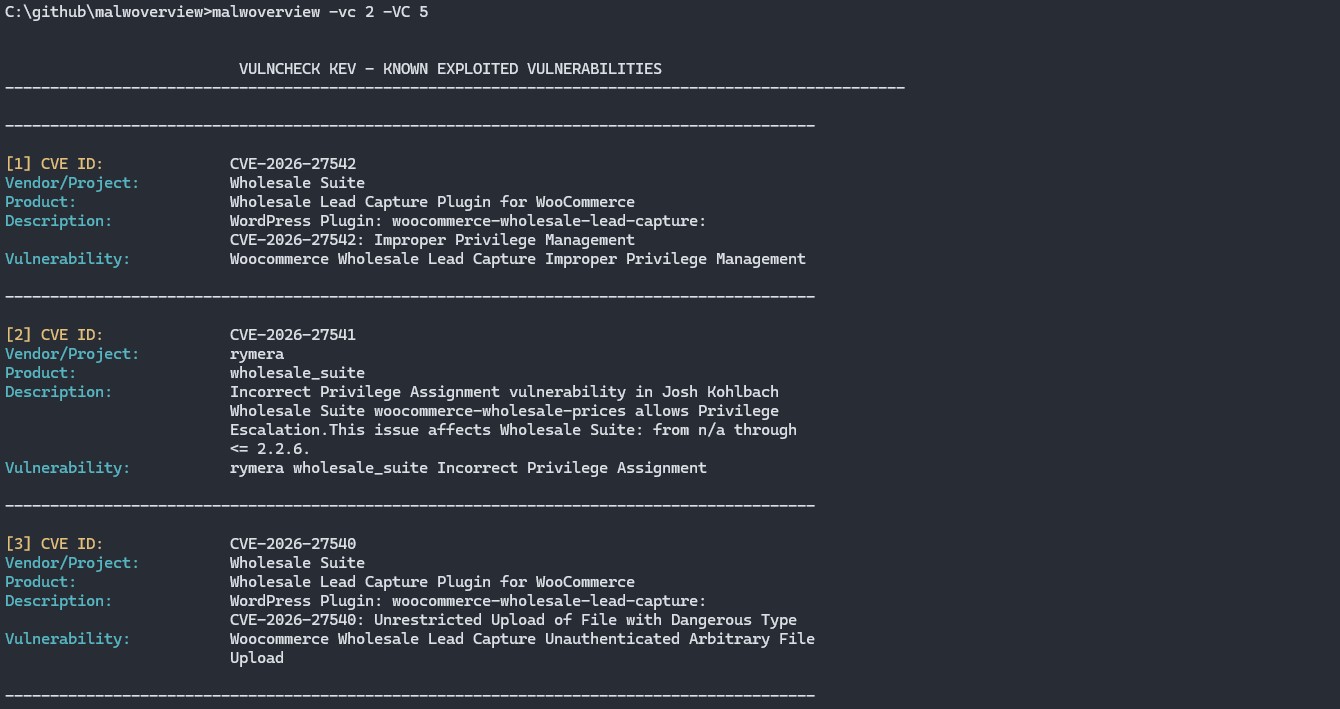
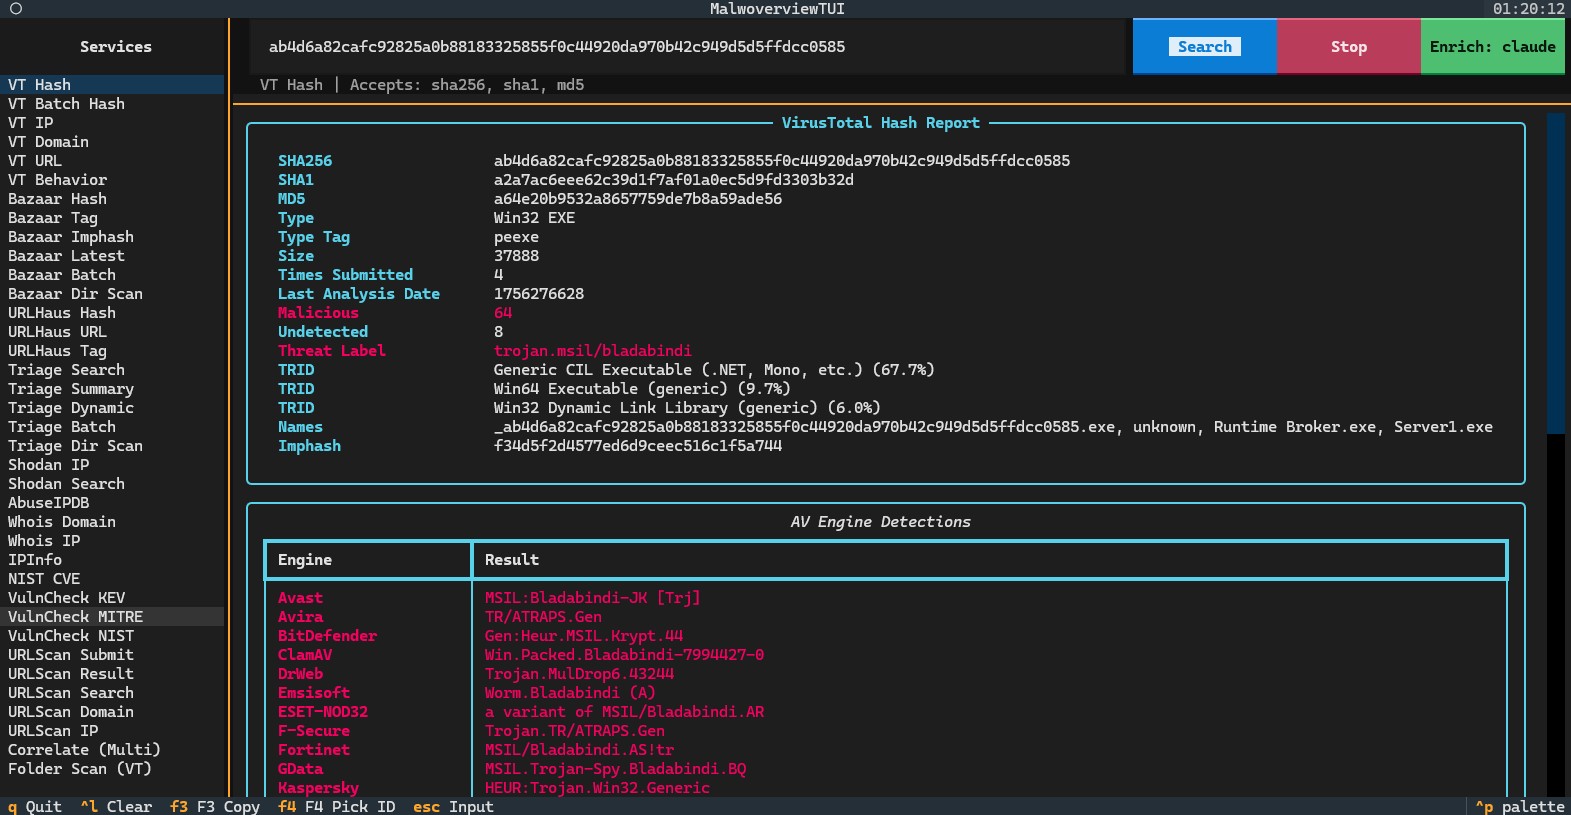
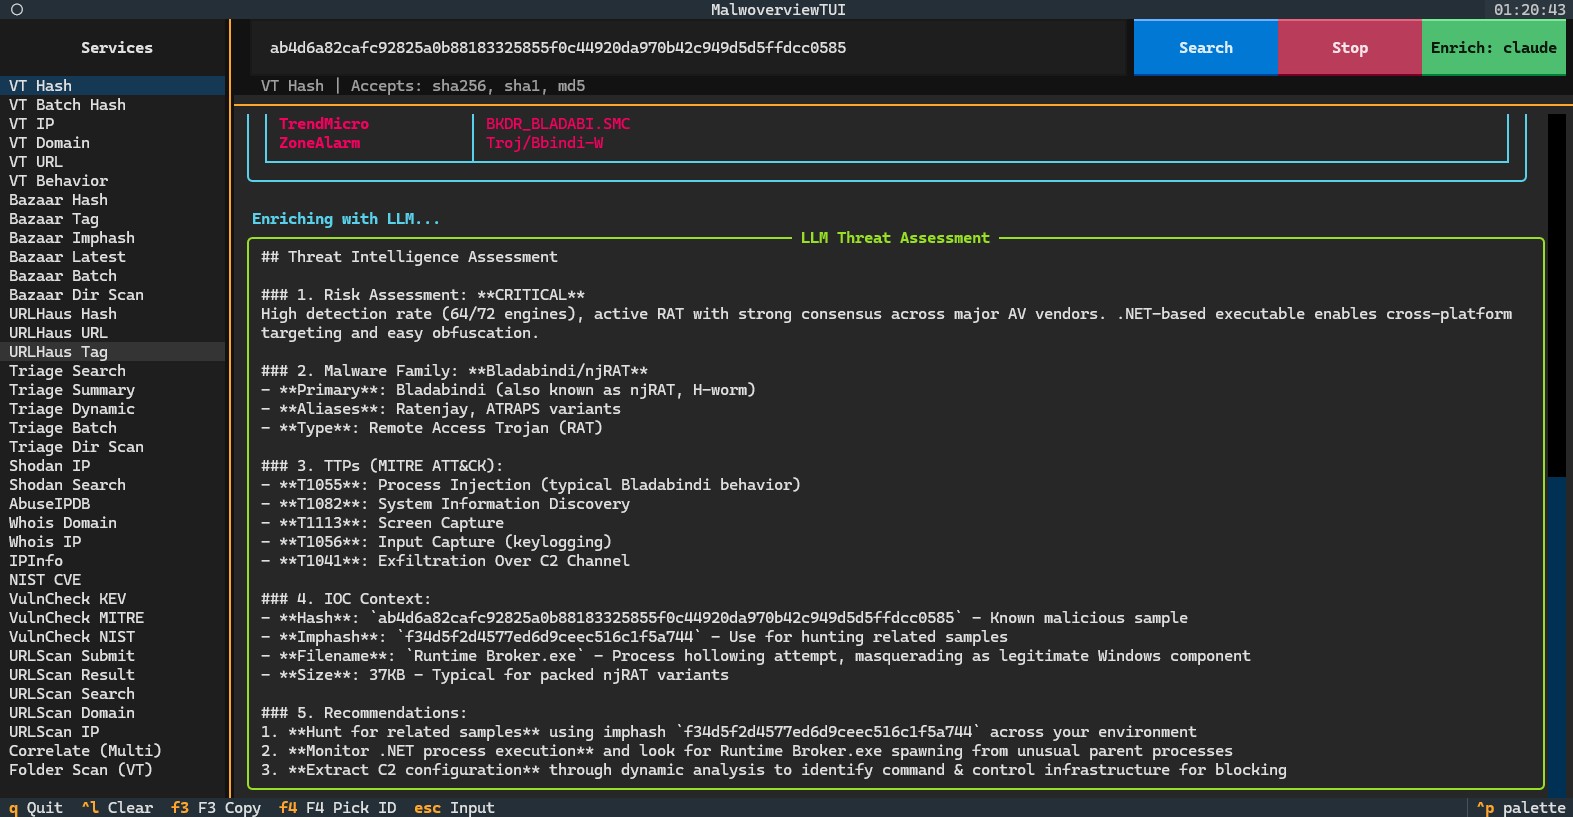
Malwoverview.py es una herramienta de primera respuesta para threat hunting, que realiza un triaje inicial y rápido de muestras de malware, URLs, direcciones IP, dominios, familias de malware, IOCs y hashes. Además, Malwoverview es capaz de obtener informes de comportamiento dinámico y estático, enviar y descargar muestras desde varios endpoints. En pocas palabras, funciona como un cliente para los principales sandboxes existentes.
Esta herramienta tiene como objetivo:

