 0vercl0k/cve-2021-31166
Prueba de concepto para CVE-2021-31166, un use-after-free en HTTP.sys desencadenado de forma remota.

Esta es una prueba de concepto para CVE-2021-31166 ("Vulnerabilidad de ejecución remota de código en la pila de protocolo HTTP"), una desreferencia de use-after-free en http.sys parcheada por Microsoft en mayo de 2021. Según este tuit, la vulnerabilidad fue encontrada por @_mxms y @fzzyhd1.

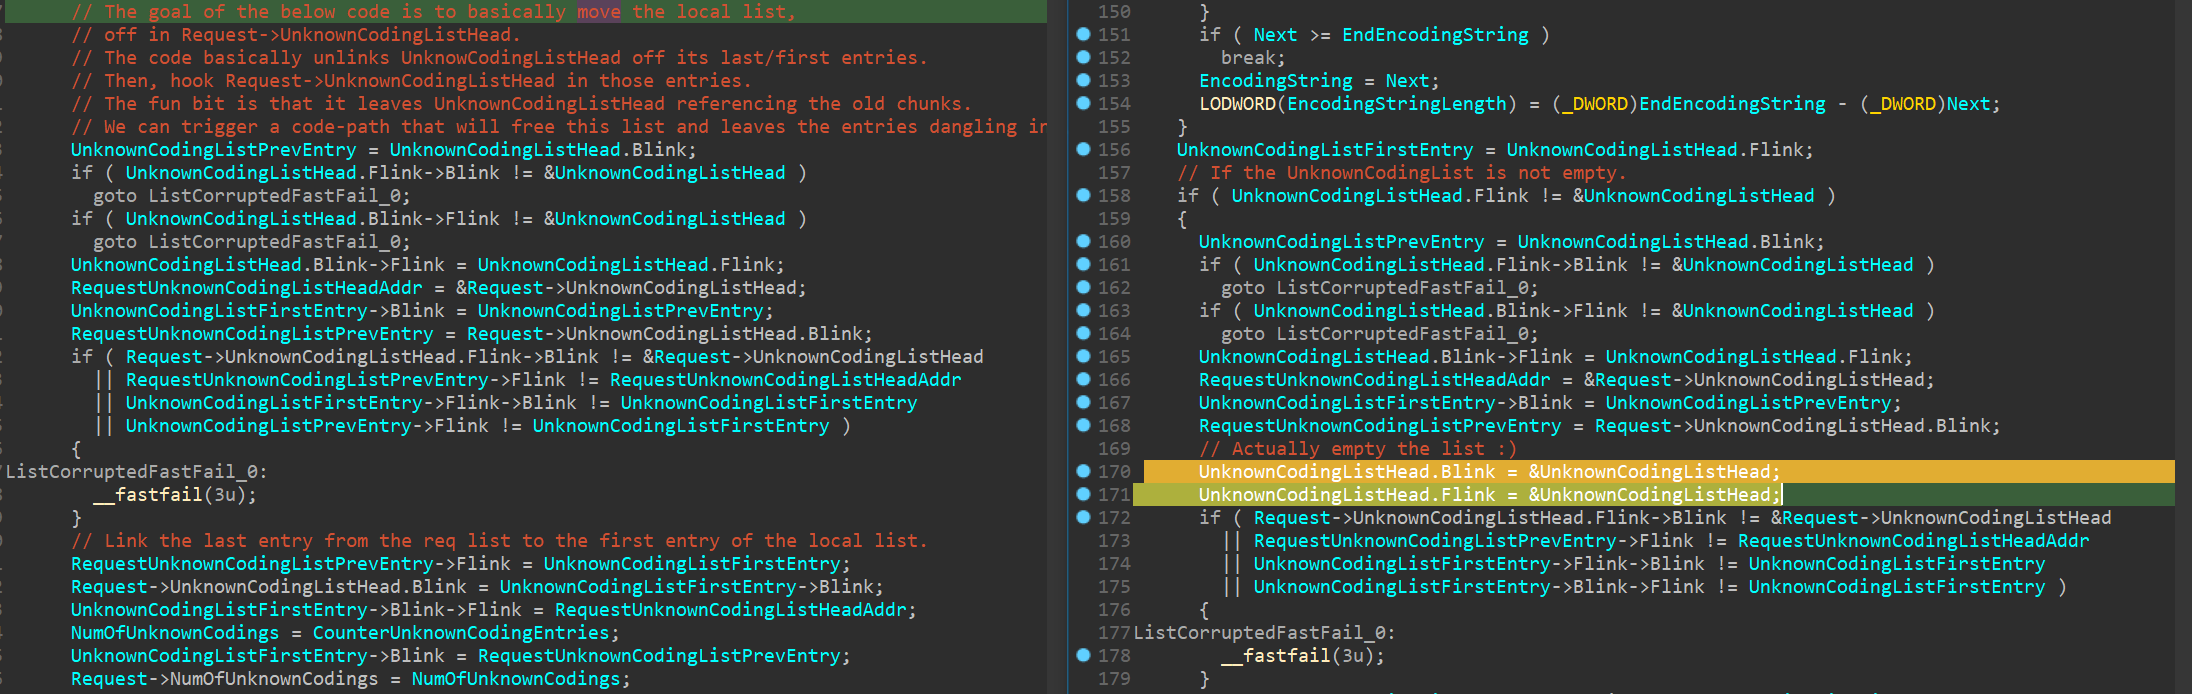
El error en sí ocurre en http!UlpParseContentCoding donde la función tiene un LIST_ENTRY local y añade un elemento a él. Cuando termina, lo mueve a la estructura Request; pero no pone a NULL la lista local. El problema con esto es que un atacante puede activar una ruta de código que libera todas las entradas de la lista local dejándolas colgando en el objeto Request.

Aquí está el bugcheck:
KDTARGET: Refreshing KD connection

*** Fatal System Error: 0x00000139
                       (0x0000000000000003,0xFFFFF90EA867EE40,0xFFFFF90EA867ED98,0x0000000000000000)

Break instruction exception - code 80000003 (first chance)

A fatal system error has occurred.
Debugger entered on first try; Bugcheck callbacks have not been invoked.

A fatal system error has occurred.

nt!DbgBreakPointWithStatus:
fffff804`19410c50 cc              int     3

kd> kp
 # Child-SP          RetAddr               Call Site
00 fffff90e`a867e368 fffff804`19525382     nt!DbgBreakPointWithStatus
01 fffff90e`a867e370 fffff804`19524966     nt!KiBugCheckDebugBreak+0x12
02 fffff90e`a867e3d0 fffff804`19408eb7     nt!KeBugCheck2+0x946
03 fffff90e`a867eae0 fffff804`1941ad69     nt!KeBugCheckEx+0x107
04 fffff90e`a867eb20 fffff804`1941b190     nt!KiBugCheckDispatch+0x69
05 fffff90e`a867ec60 fffff804`19419523     nt!KiFastFailDispatch+0xd0
06 fffff90e`a867ee40 fffff804`1db3f677     nt!KiRaiseSecurityCheckFailure+0x323
07 fffff90e`a867efd0 fffff804`1daf6c05     HTTP!UlFreeUnknownCodingList+0x63
08 fffff90e`a867f000 fffff804`1dacd201     HTTP!UlpParseAcceptEncoding+0x299c5
09 fffff90e`a867f0f0 fffff804`1daa93d8     HTTP!UlAcceptEncodingHeaderHandler+0x51
0a fffff90e`a867f140 fffff804`1daa8ab7     HTTP!UlParseHeader+0x218
0b fffff90e`a867f240 fffff804`1da04c5f     HTTP!UlParseHttp+0xac7
0c fffff90e`a867f3a0 fffff804`1da0490a     HTTP!UlpParseNextRequest+0x1ff
0d fffff90e`a867f4a0 fffff804`1daa48c2     HTTP!UlpHandleRequest+0x1aa
0e fffff90e`a867f540 fffff804`1932ae85     HTTP!UlpThreadPoolWorker+0x112
0f fffff90e`a867f5d0 fffff804`19410408     nt!PspSystemThreadStartup+0x55
10 fffff90e`a867f620 00000000`00000000     nt!KiStartSystemThread+0x28

kd> !analyze -v
[...]
*******************************************************************************
*                                                                             *
*                        Bugcheck Analysis                                    *
*                                                                             *
*******************************************************************************

KERNEL_SECURITY_CHECK_FAILURE (139)
A kernel component has corrupted a critical data structure.  The corruption
could potentially allow a malicious user to gain control of this machine.
Arguments:
Arg1: 0000000000000003, A LIST_ENTRY has been corrupted (i.e. double remove).
Arg2: fffff90ea867ee40, Address of the trap frame for the exception that caused the BugCheck
Arg3: fffff90ea867ed98, Address of the exception record for the exception that caused the BugCheck
Arg4: 0000000000000000, Reserved
P: ¿Está afectado Windows Remote Management (WinRM)?
Sí (gracias a @JimDinMN por compartir sus experimentos).
P: ¿Está afectado Web Services on Devices (WSDAPI)?
Sí (gracias a @HenkPoley por compartir sus resultados).
P: ¿Cuáles son las versiones afectadas de Windows?
Según la documentación de Microsoft, aquí están las plataformas afectadas:
