
New tool24 days ago
gvisor
 google/gvisor
Sandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
Cloud Infrastructure SecurityDefensive ToolsContainer Security+4
Short editorial updates from published cybersecurity tools.
google/gvisorSandboxes containers via a userspace application kernel that intercepts system calls, limits host kernel access, and integrates with…
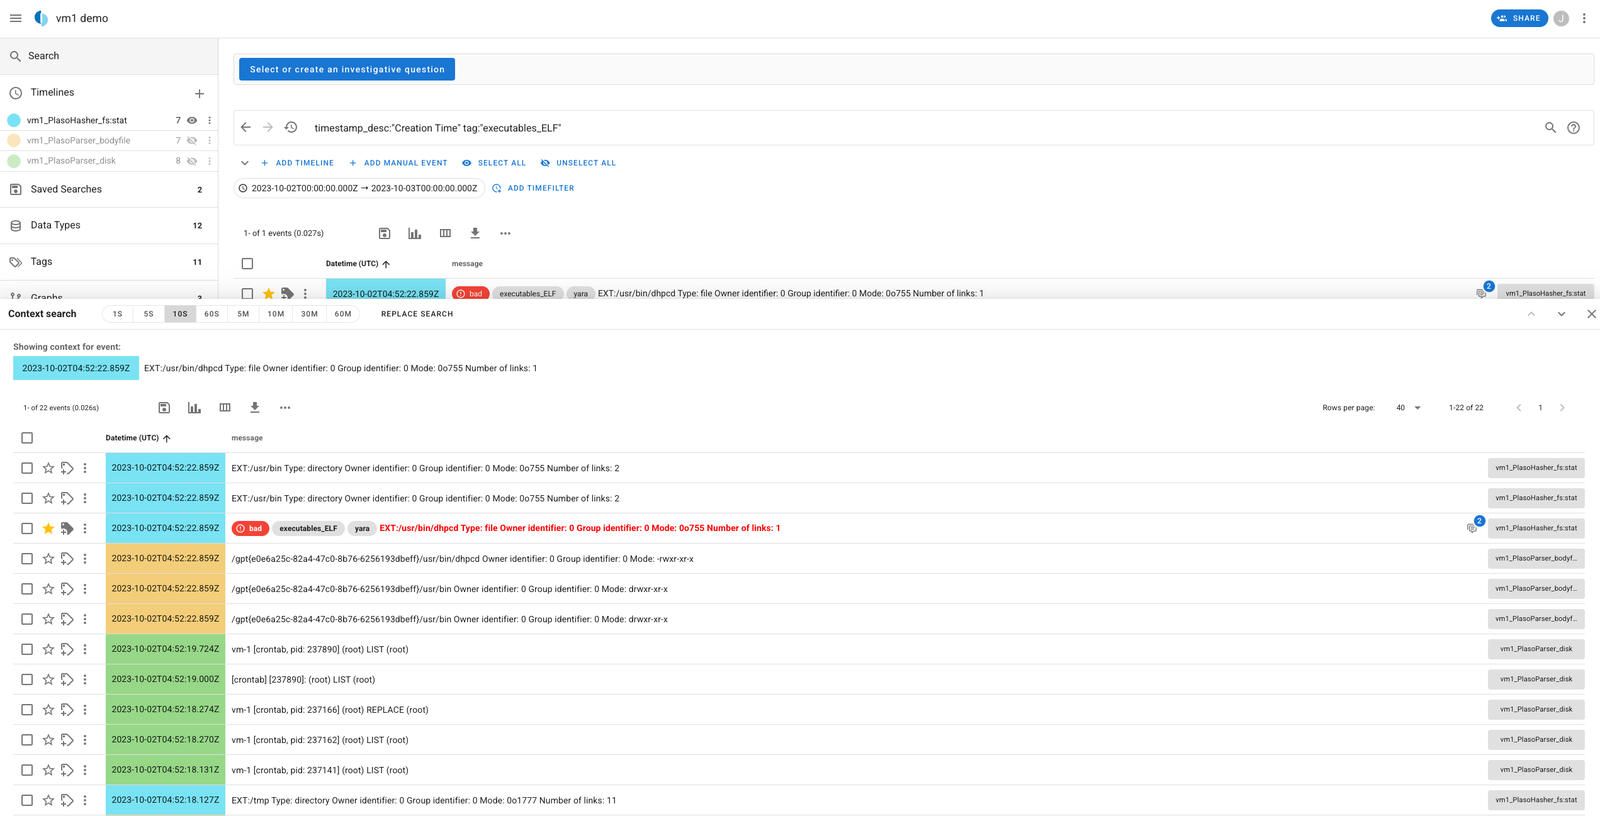 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 mvt-project/mvt
Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…
 cgsecurity/testdisk
Recovers lost partitions and repairs boot sectors; carves 480+ file formats from damaged disks and filesystems for data recovery and forensic use.
 abrignoni/aleapp
Android Logs Events And Protobuf Parser
 abrignoni/ileapp
Parses iOS and iPadOS forensic extractions into HTML, TSV, timeline, KML, and LAVA reports with modular artifact discovery and encrypted iTunes…
 blacktop/ipsw
iOS/macOS Research Swiss Army Knife
 rustls/rustls
Memory-safe TLS library in Rust implementing TLS 1.2 and 1.3 with pluggable crypto providers, client/server modes, and certificate-based…
 google/boringssl
Fork of OpenSSL implementing TLS, cryptographic primitives, and X.509 certificate handling for use in Chrome and Android, with no API/ABI…
 anchore/syft
CLI tool and library for generating a Software Bill of Materials from container images and filesystems