

CVE-2025
 dark-life944/cve-2025
This is POC for IOS 0click CVE-2025-43300
binary-exploitationeducationexploitation+3
dark-life944/cve-2025This is POC for IOS 0click CVE-2025-43300
 nhattanhh/cve-2022-22965
Spring4Shell
 niokagi/react-cve-2025-55182
Test & Analyze the CVE-2025-55182 vulnerability within Next.js Server Actions
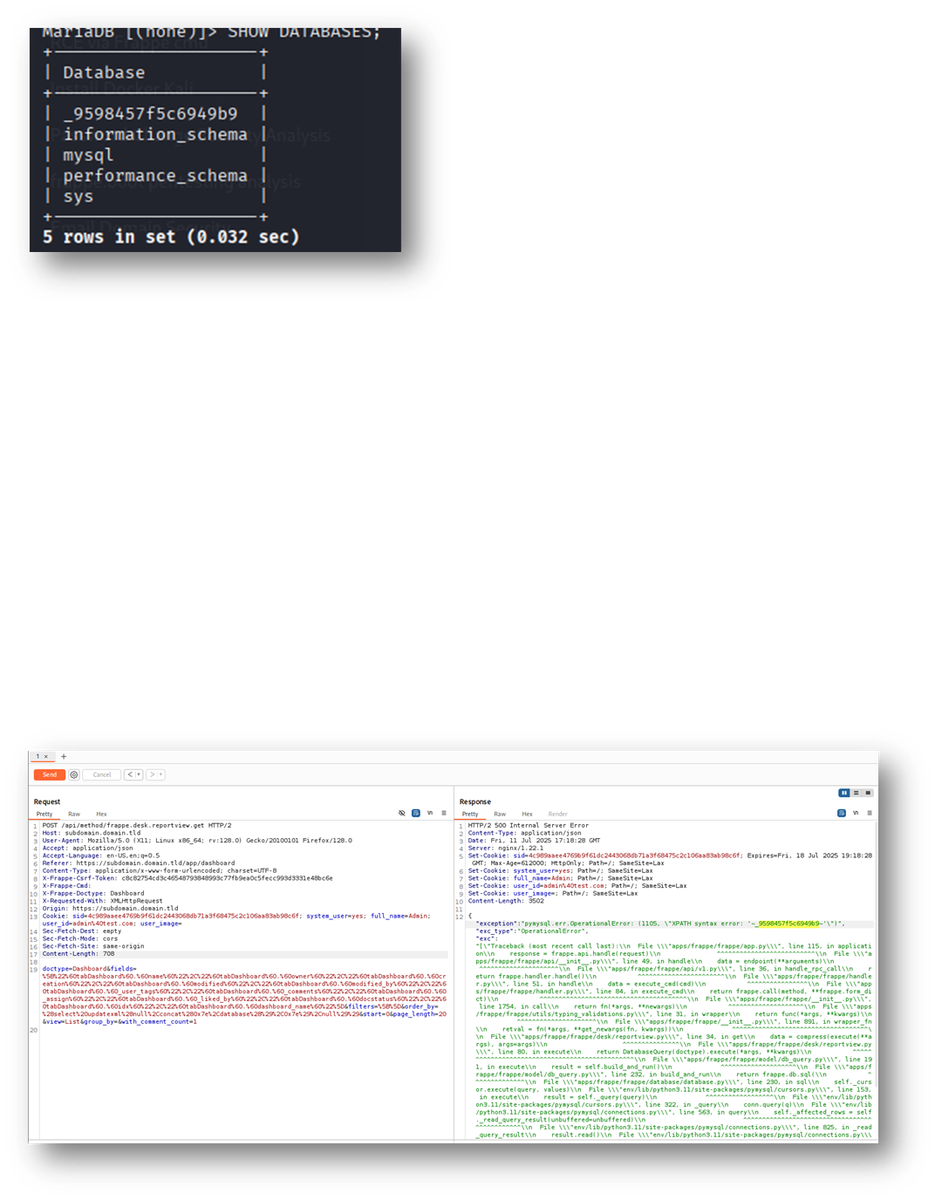 moalali/cve-2025-56381
ERPNEXT v15.67.0 was discovered to contain multiple SQL injection vulnerabilities in the /api/method/frappe.desk.reportview.get endpoint via the…
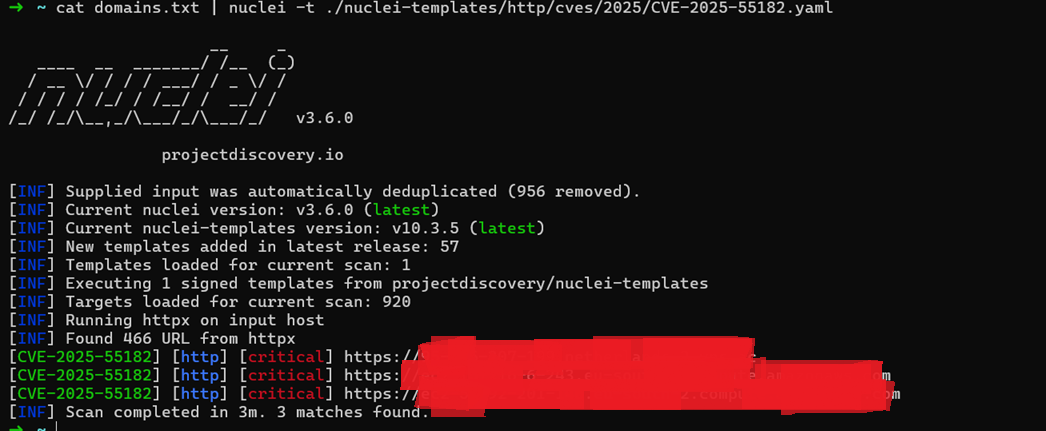 jaycelation/cve-2025-55182
PoC, Hunting React2Shell about CVE-2025-55182
 zs1n/cve-2025-29927
PoC | NextJS Middleware 15.2.2 - Authorization Bypass
 sonatype-workshops/struts2-rce
Exploitable target to CVE-2017-5638
 gmh5225/aether-c2-framework
🛠️ Explore custom C2 TTPs with Aether-C2-Framework, focusing on lightweight Rust implants and stealthy transport stacks to reduce forensic…
 thampakon/cve-2023-35674
ช่องโหว่ CVE-2023-35674 *สถานะ: ยังไม่เสร็จ*
 ifygecko/cve-2023-30226
Documentation of a denial-of-service vulnerability in the Rizin reverse engineering framework's ELF parser, caused by a forged DT_VERNEEDNUM value…
 funnydog896/cve-2024-36401-woodpeckerplugin
CVE-2024-36401-GeoServer Property 表达式注入 Rce woodpecker-framework 插件
 gmh5225/cve-2022-24716-2
CVE-2022-24716 (Arbitrary File Disclosure Icingaweb2)
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.
 raghvendra1207/cve-2022-22978
Proof-of-concept demonstrating authorization bypass in Spring Security's RegexRequestMatcher (CVE-2022-22978) using CRLF injection, with analysis and…
 secjoker/cve-2025-68613
基于Pocsuite3 框架编写的漏洞验证与利用脚本,用于检测 n8n工作流自动化工具中的认证后远程代码执行漏洞(RCE)
 terracatta/name_reverser
Silly Rails App to demonstrate vuln CVE-2013-0156
 redteamsecurity2023/cve-2022-26265
The first proof of concept of the Contao CMS RCE
 ally-petitt/cve-2023-45503
CVE-2023-45503 Reference