

CVE-2025-68664-LangGrinch-PoC
 ak-cybe/cve-2025-68664-langgrinch-poc
A testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
ai-securitycode-analysiseducation+6
3
ak-cybe/cve-2025-68664-langgrinch-pocA testing framework to identify and demonstrate deserialization vulnerabilities in LangChain Core (<0.3.81). Educational use only
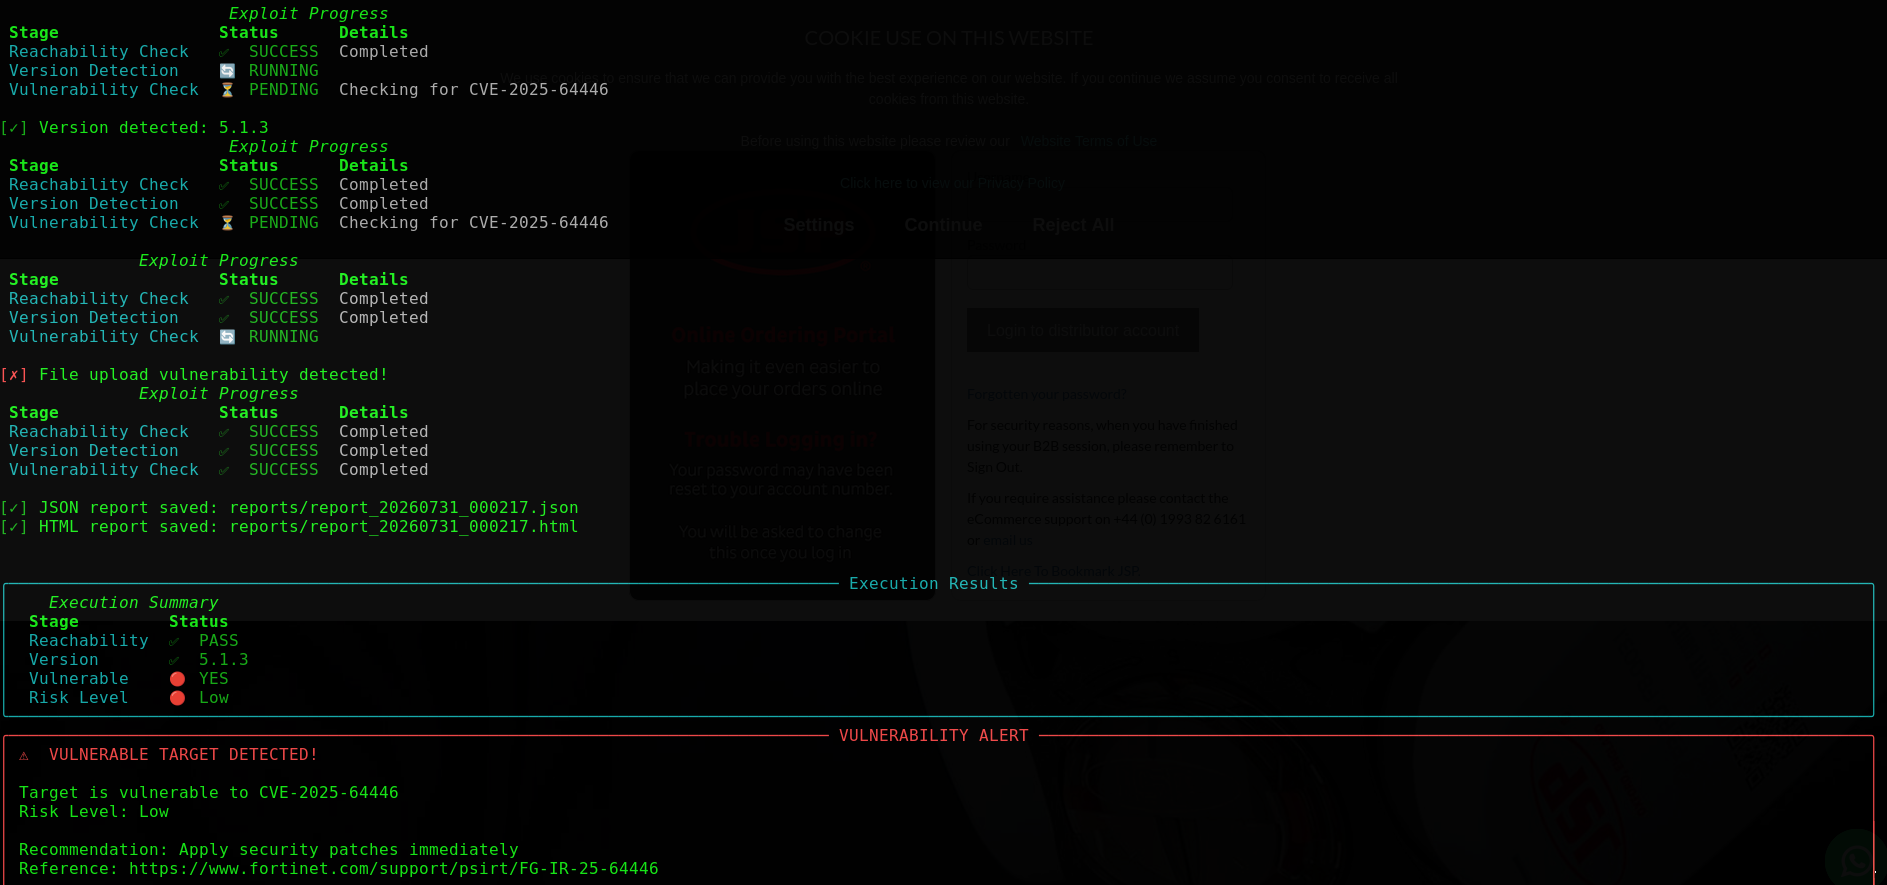 cerberusmrxi/fortiweb-cve-2025-64446-rce-exploit
Security research tool for FortiWeb CVE-2025-64446 vulnerability. Automated exploitation framework with advanced logging, real-time metrics, proxy…
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
 xkillbit/cve-2025-55182-scanner
Passive vulnerability scanner for CVE-2025-55182 and CVE-2025-66478, detecting unauthenticated RCE in React Server Components via framework…
 zoomdbz/aempwn
CVE-2025-54253 | CVE-2025-54254 | Adobe Experience Manager Forms XXE → RCE Framework
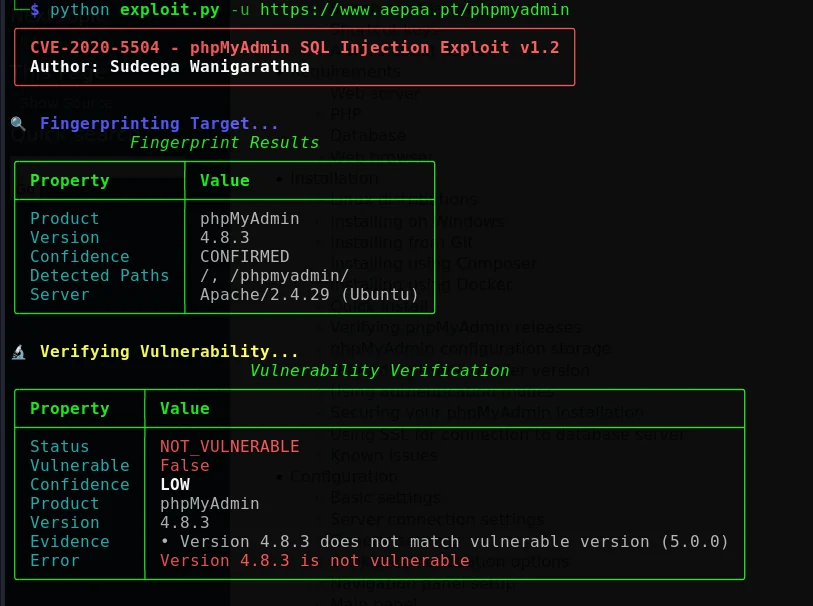 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 vulnquest58/vq-refluxcore
is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…
 dereeqw/bitlock-crypto-research
Framework de investigación sobre criptovirología avanzada. Implementación de Handshake ECDHE, cifrado autenticado AES-GCM y ejecución fileless en…
 leo-mitch/cve-2024-41570-havoc-c2-rce
This is a Chained RCE in the Havoc C2 framework using github.com/chebuya and github.com/IncludeSecurity pocs
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 themehackers/cve-2025-29972
CVE-2025-29927 is a critical security vulnerability affecting Next.js, a popular React framework for building full-stack web applications. This flaw…
 xiaobailovesstirring/cve-2025-48595-exploit
CVE-2025-48595 Android Framework Integer Overflow PoC - 优化版
 proxydom/supahunter
Automated reconnaissance and exploitation framework for misconfigured Supabase instances. Features schema enumeration, Selenium-based key extraction,…
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 dungsocool/cve-2026-8206
CVE-2026-8206: Kirki Customizer Framework - Unauthenticated Account Takeover (CVSS 9.8)
 mogwailabs/cve-2023-32692-codeigniter4
Example application, vulnerable to CVE-2023-32692 (Validation Rule Injection in the PHP Framework CodeIgniter)