
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
355 results
NamedPipePTH preview

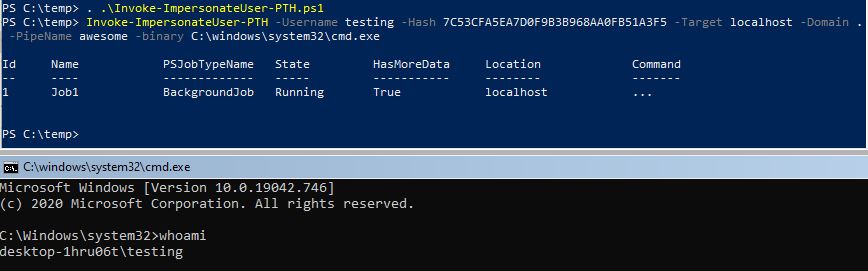
NamedPipePTH

GitHubs3cur3th1ssh1t/namedpipepth

Pass the Hash to a named pipe for token Impersonation
authenticationimpersonation-toolslateral-movement+4
146
5 years ago
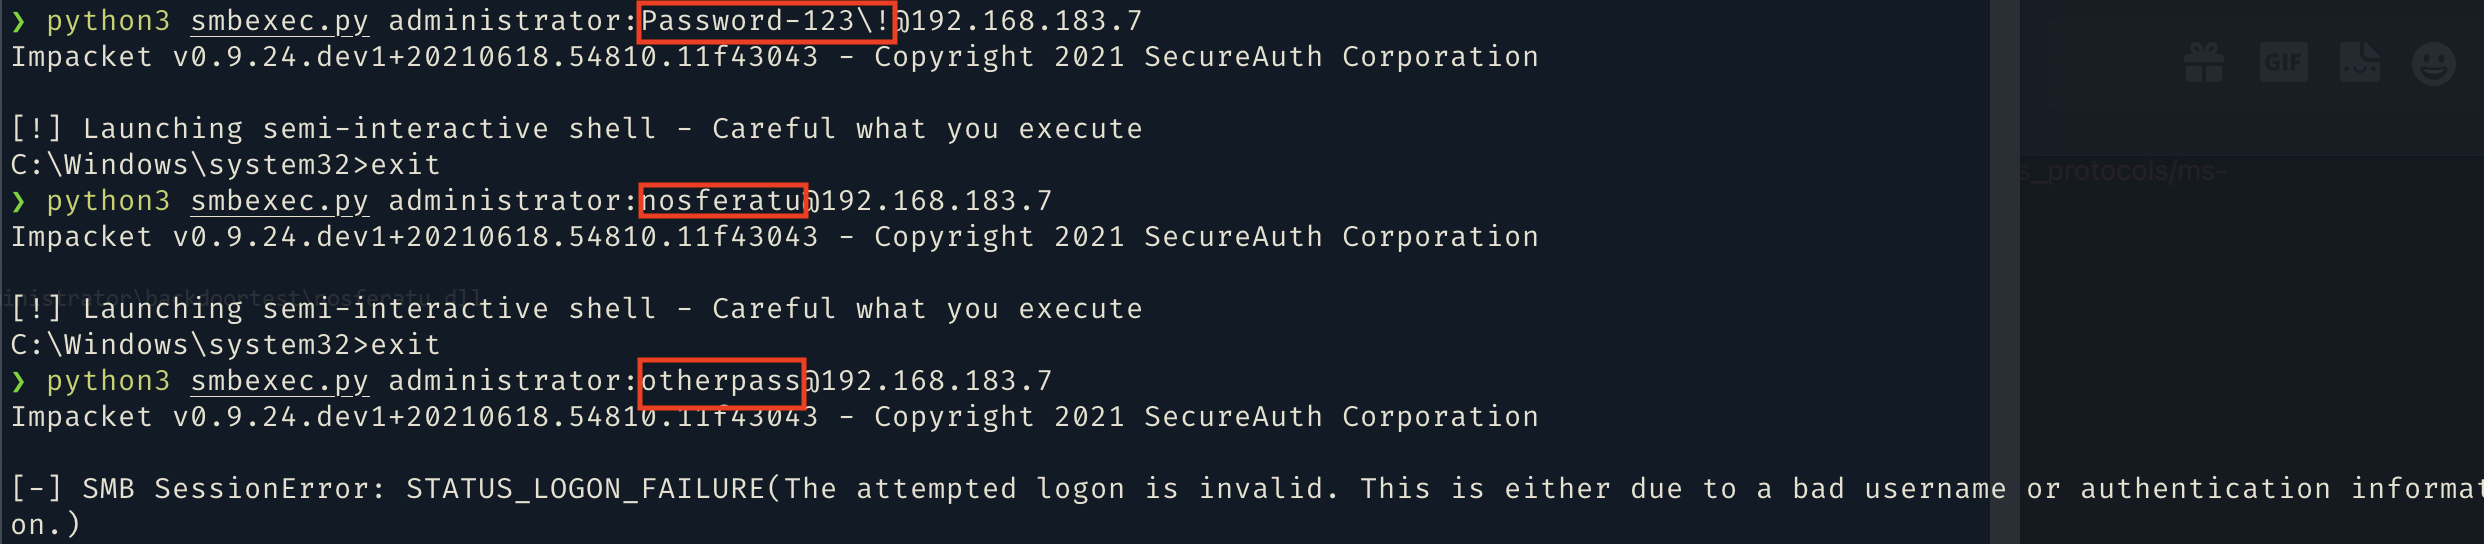
nosferatu preview

nosferatu

GitHubkindtime/nosferatu

DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.

authenticationlateral-movementpenetration-testing+2
2411 year ago
tgt-monitor-bof preview

tgt-monitor-bof

GitHubjakobfriedl/tgt-monitor-bof

Async BOF to automatically extract or renew Kerberos TGTs on a target system.
authenticationlateral-movementpayload-development+3
1351 month ago
Invoke-RunAsWithCert preview

Invoke-RunAsWithCert

GitHubsynacktiv/invoke-runaswithcert

A PowerShell script to perform PKINIT authentication with the Windows API from a non domain-joined machine.
authenticationlateral-movementpenetration-testing+2
1792 years ago
ColdWer preview

ColdWer

GitHub0xsh3llf1r3/coldwer

Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass

exploitationlateral-movementpayload-development+3
1467 months ago
BackupOperatorToolkit preview

BackupOperatorToolkit

GitHubimprosec/backupoperatortoolkit

Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
lateral-movementpenetration-testingpost-exploitation+1
1793 years ago
NoiseHound preview

NoiseHound

GitHubwarpedatom/noisehound

Detection-aware BloodHound attack-path scoring - the quietest route to your objective, calibrated across five detection tiers…
adversarial-attackdefensive-toolslateral-movement+4
6629 days ago
NegoExRelay preview

NegoExRelay

GitHubmorrubin/negoexrelay

Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
authenticationexploitationimpersonation-tools+4
914 years ago
TChopper preview

TChopper

GitHubzux0x3a/tchopper

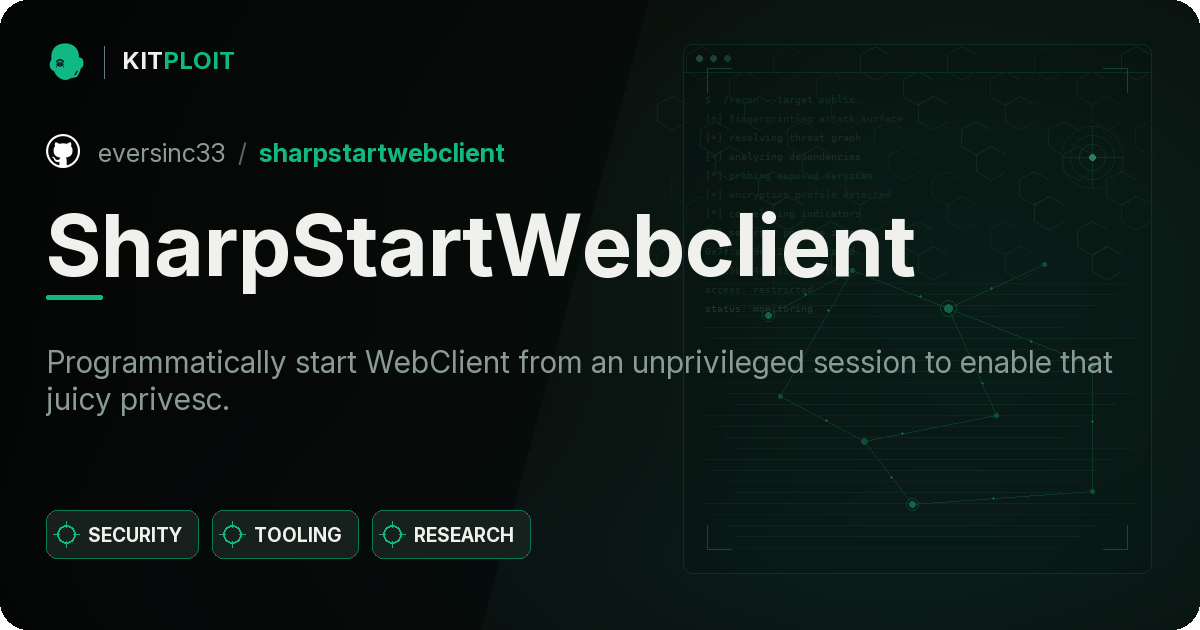
conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine
lateral-movementpenetration-testingred-teaming
555 years ago
SharpStartWebclient preview

SharpStartWebclient

GitHubeversinc33/sharpstartwebclient

Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
lateral-movementpenetration-testingpost-exploitation+2
783 years ago
CVE-2026-24294 preview

CVE-2026-24294

GitHub0xndi/cve-2026-24294

Local privilege escalation PoC for CVE-2026-24294, abusing SMB arbitrary port and NTLM reflection to achieve SYSTEM on Windows Server 2025.
exploitationlateral-movementpenetration-testing+3
544 months ago
CPLDCOMTrigger preview

CPLDCOMTrigger

GitHubklsecservices/cpldcomtrigger

Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
exploitationlateral-movementpenetration-testing+2
488 months ago
SMBRat preview

SMBRat

GitHuboperatorequals/smbrat

A Windows Remote Administration Tool in Visual Basic with UNC paths
command-and-controlexploitationlateral-movement+8
227 years ago
BadSamba preview

BadSamba

GitHubstrozfriedberg/badsamba

This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.

exploitationlateral-movementnetwork-security+3
226 years ago
printix-CVE-2022-29551 preview

printix-CVE-2022-29551

GitHubcomparedarray/printix-cve-2022-29551

A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
exploitationlateral-movementpenetration-testing+3
14 years ago
cve-2020-1472 preview

cve-2020-1472

GitHubshanfenglan/cve-2020-1472

Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…

exploitationlateral-movementpassword-attacks+3
25 years ago
CVE-2020-1472 preview

CVE-2020-1472

GitHubjiushill/cve-2020-1472

Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication bypass to escalate privileges and compromise Active Directory domain…
exploitationlateral-movementpenetration-testing+2
16 years ago
CVE-2021-46067 preview

CVE-2021-46067

GitHubsanupl/cve-2021-46067

CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.

authenticationexploitationimpersonation-tools+3
14 months ago
Previous1…567…20Next