
allsafe-android
 t0thkr1s/allsafe-android
Intentionally vulnerable Android application.
android-securitydynamic-analysis-sandboxingeducation+7
4421 year ago
t0thkr1s/allsafe-androidIntentionally vulnerable Android application.
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 ernw/androtickler
Penetration testing and auditing toolkit for Android apps.
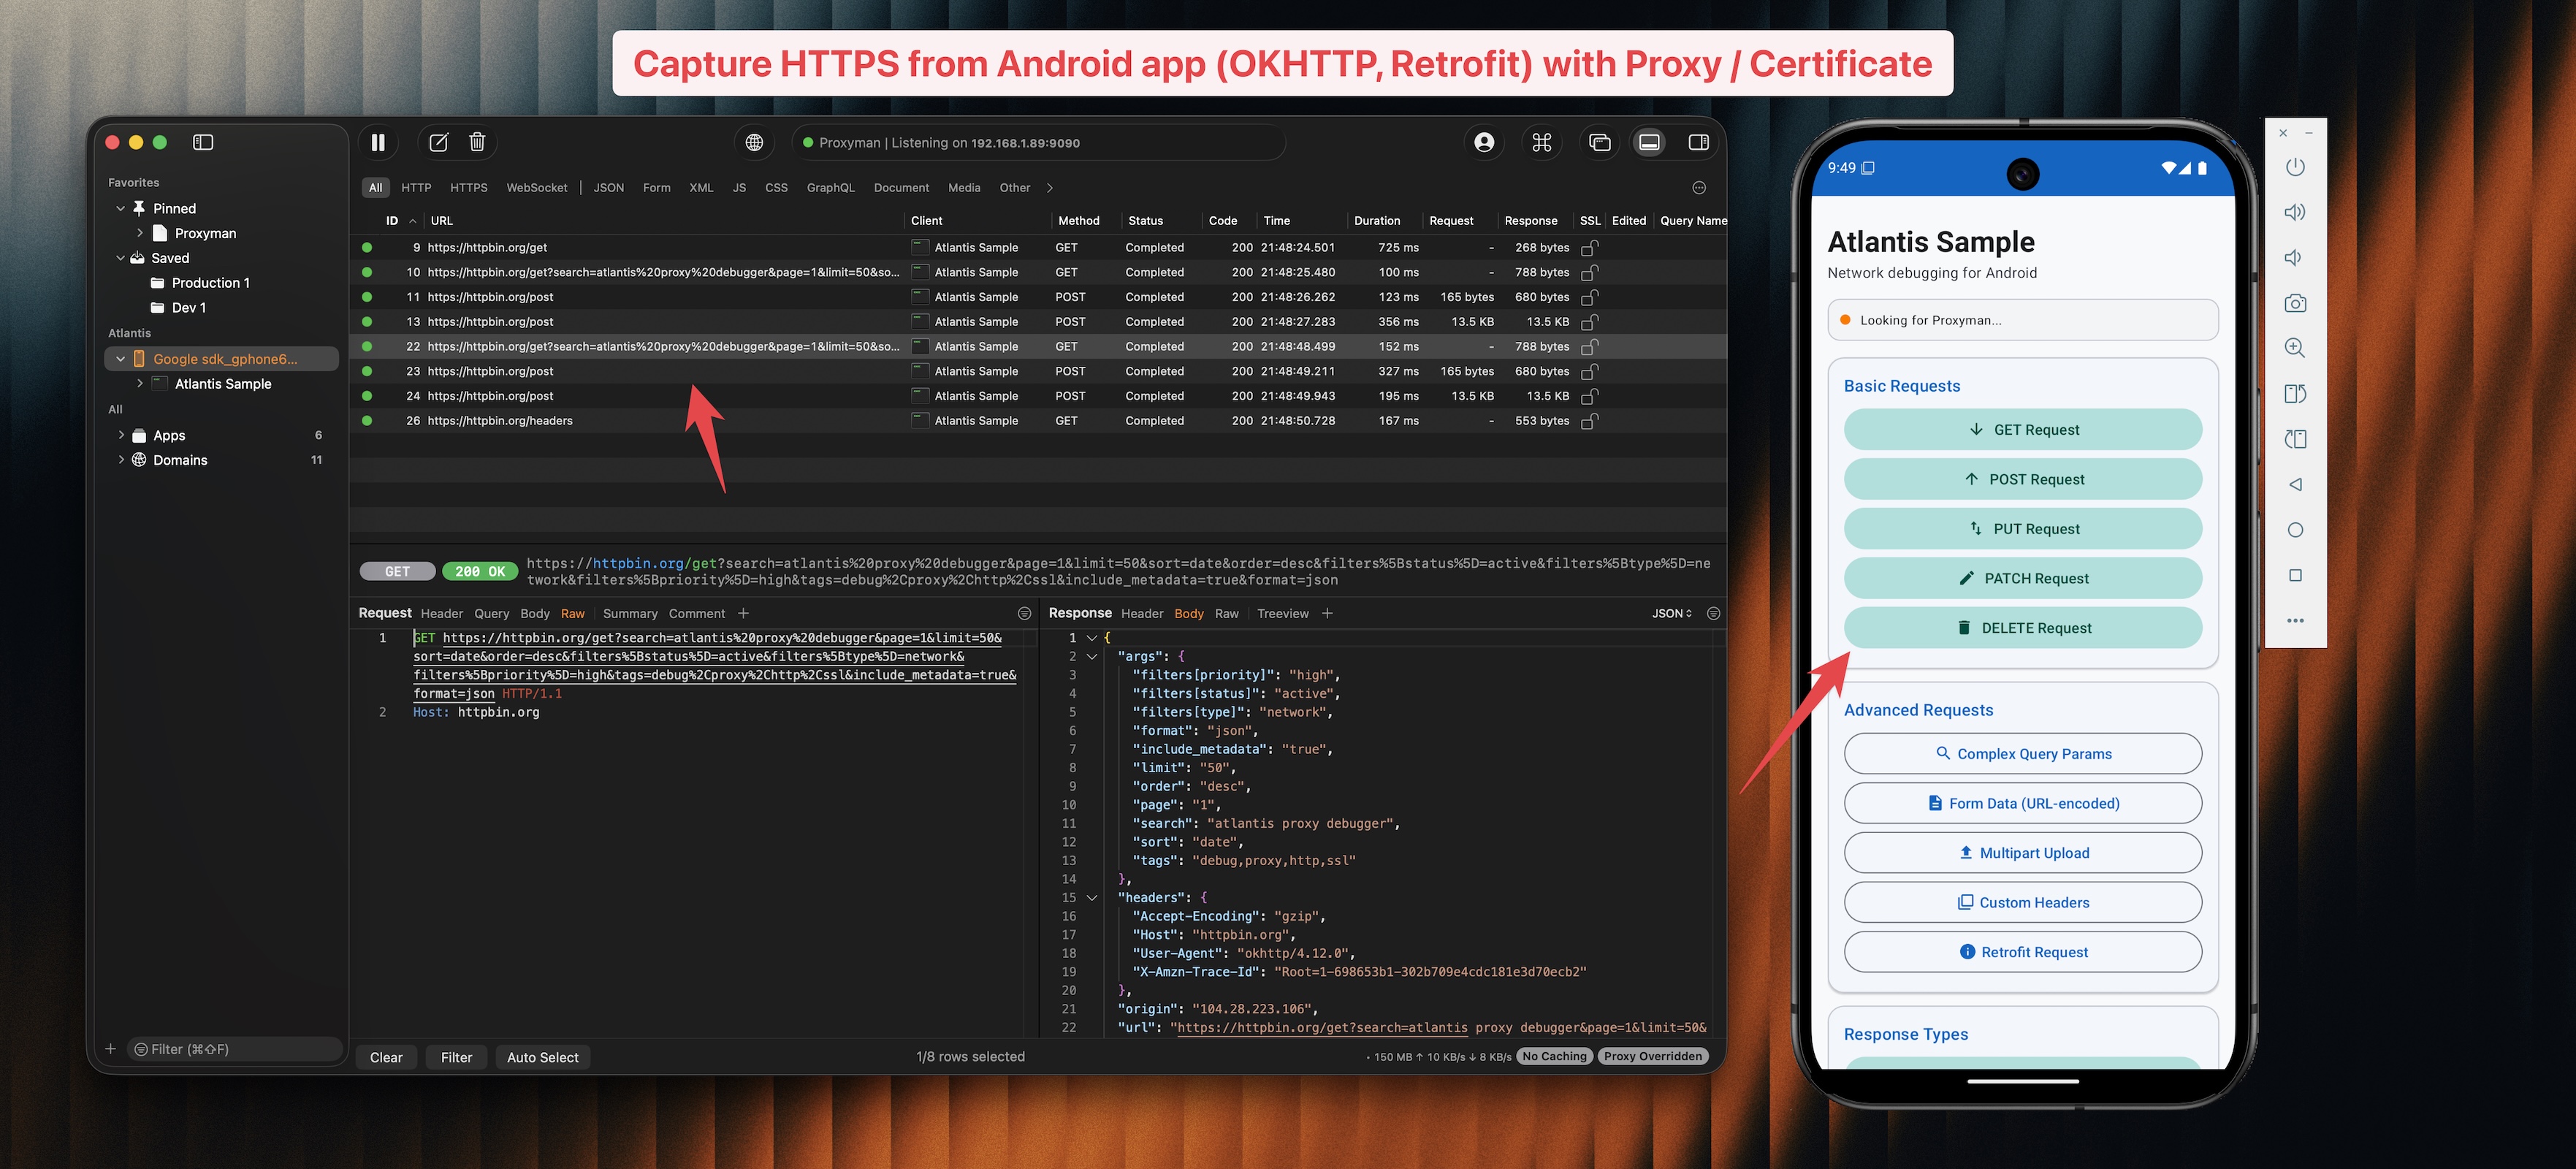 proxymanapp/atlantis-android
Capture HTTP/HTTPS traffic from Android apps and send to Proxyman for debugging.
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 marcog3/whatsdump
Extract WhatsApp private key from any non-rooted Android device (Android 7+ supported)
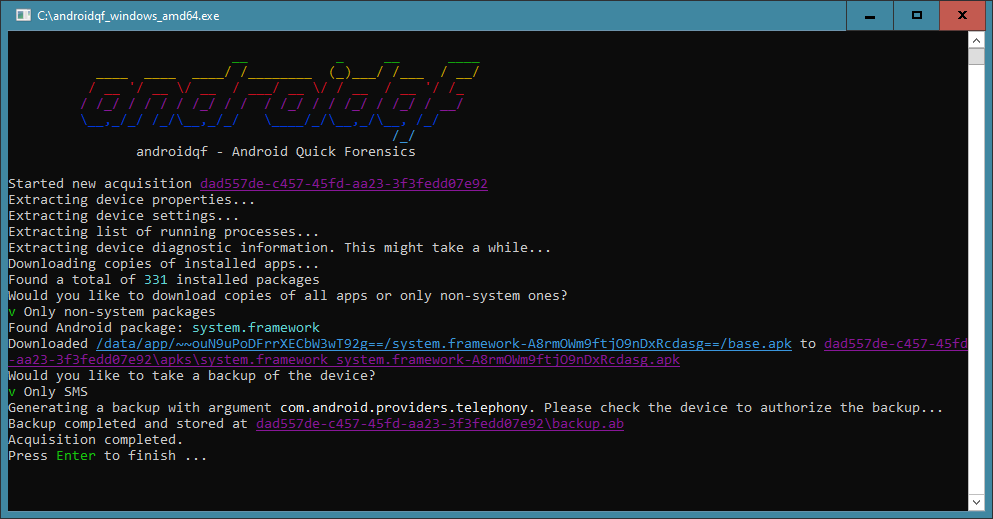 botherder/androidqf
Portable forensic acquisition tool for Android devices that collects relevant data via USB debugging to identify potential spyware or compromise…
 sultanahamer/opencontacts
Android contact manager that stores contacts in an isolated database, preventing other apps from accessing them. Provides call log and caller ID…
 logicalhacking/dvhma
Intentionally vulnerable hybrid Android app for security professionals to test tools and techniques, and for developers to learn common hybrid mobile…
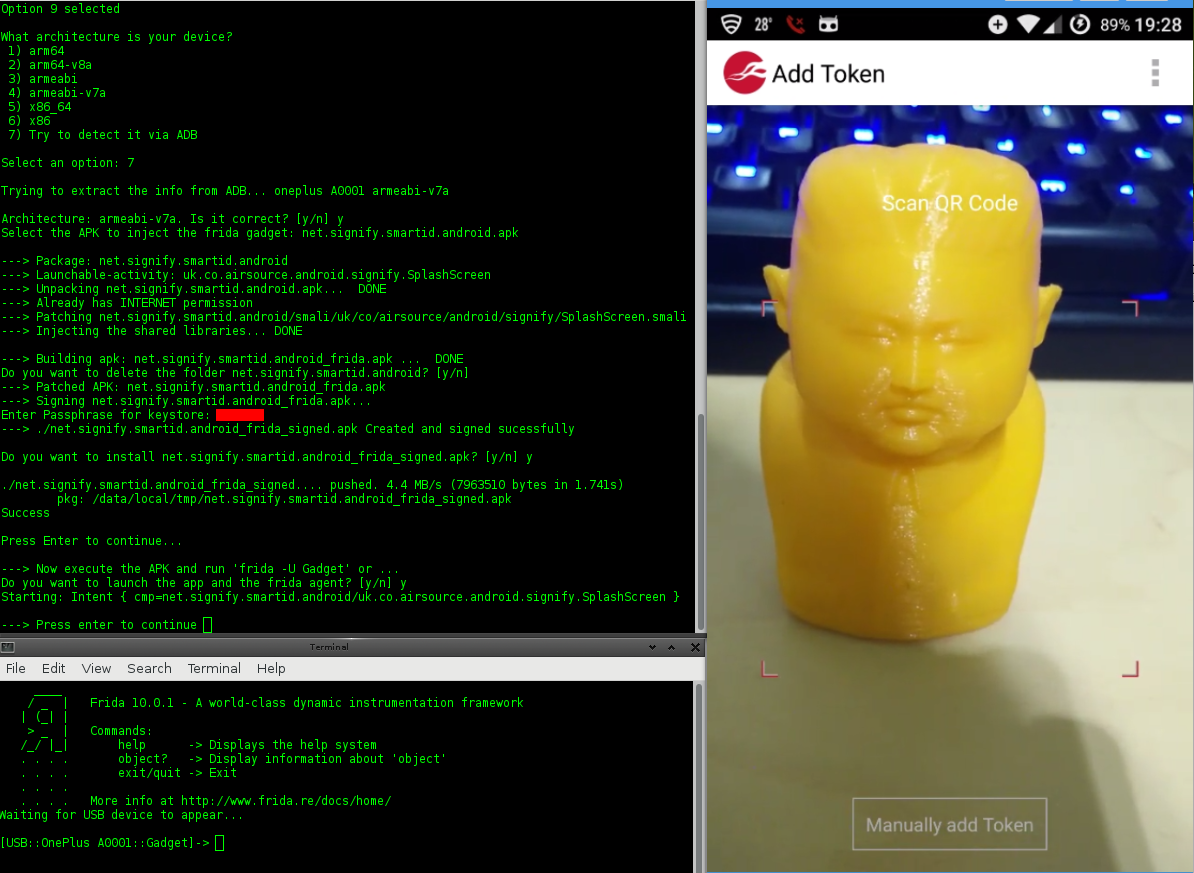 nccgroup/lazydroid
bash script to facilitate some aspects of an Android application assessment
 wheregoes/byd-dolphin-hacking
Reverse engineering the BYD Dolphin head unit — CAN bus, AVAS, NFC keys, OTA, and more. DiLink 3 / Android 10.
 iodn/tap-ducky
Turns any rooted phone into the legendary USB Rubber Ducky. Android USB HID Keystroke Injector
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…
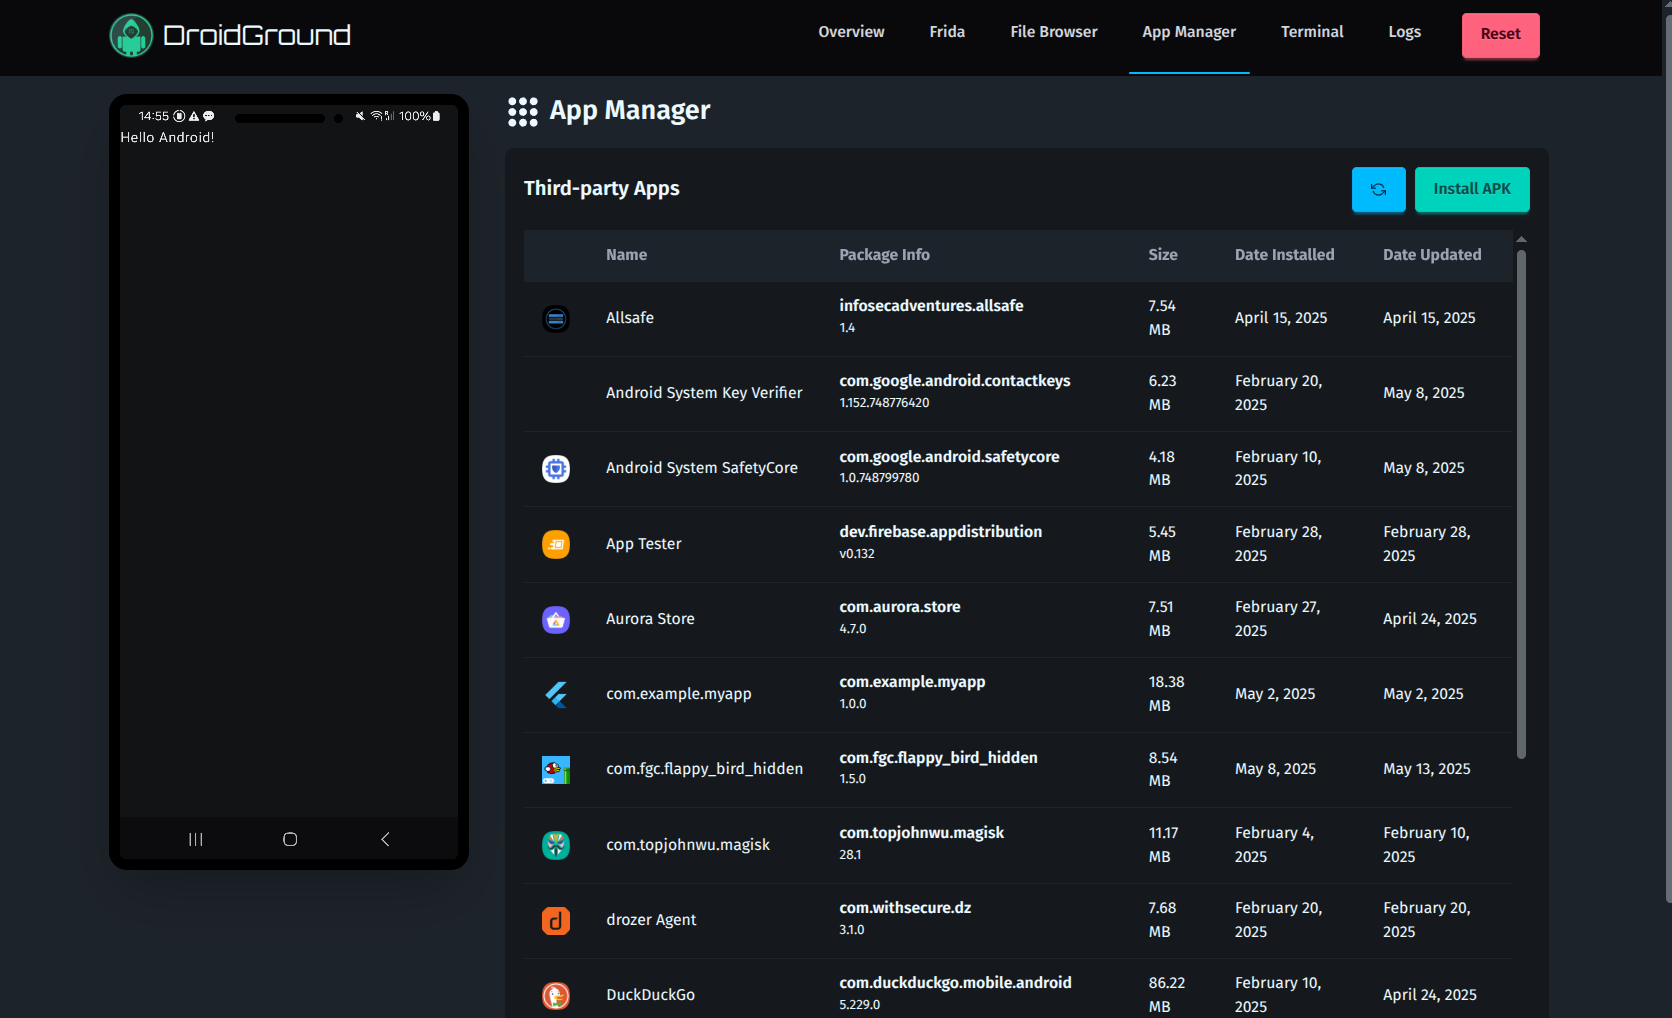 secforce/droidground
A flexible playground for Android CTF challenges.
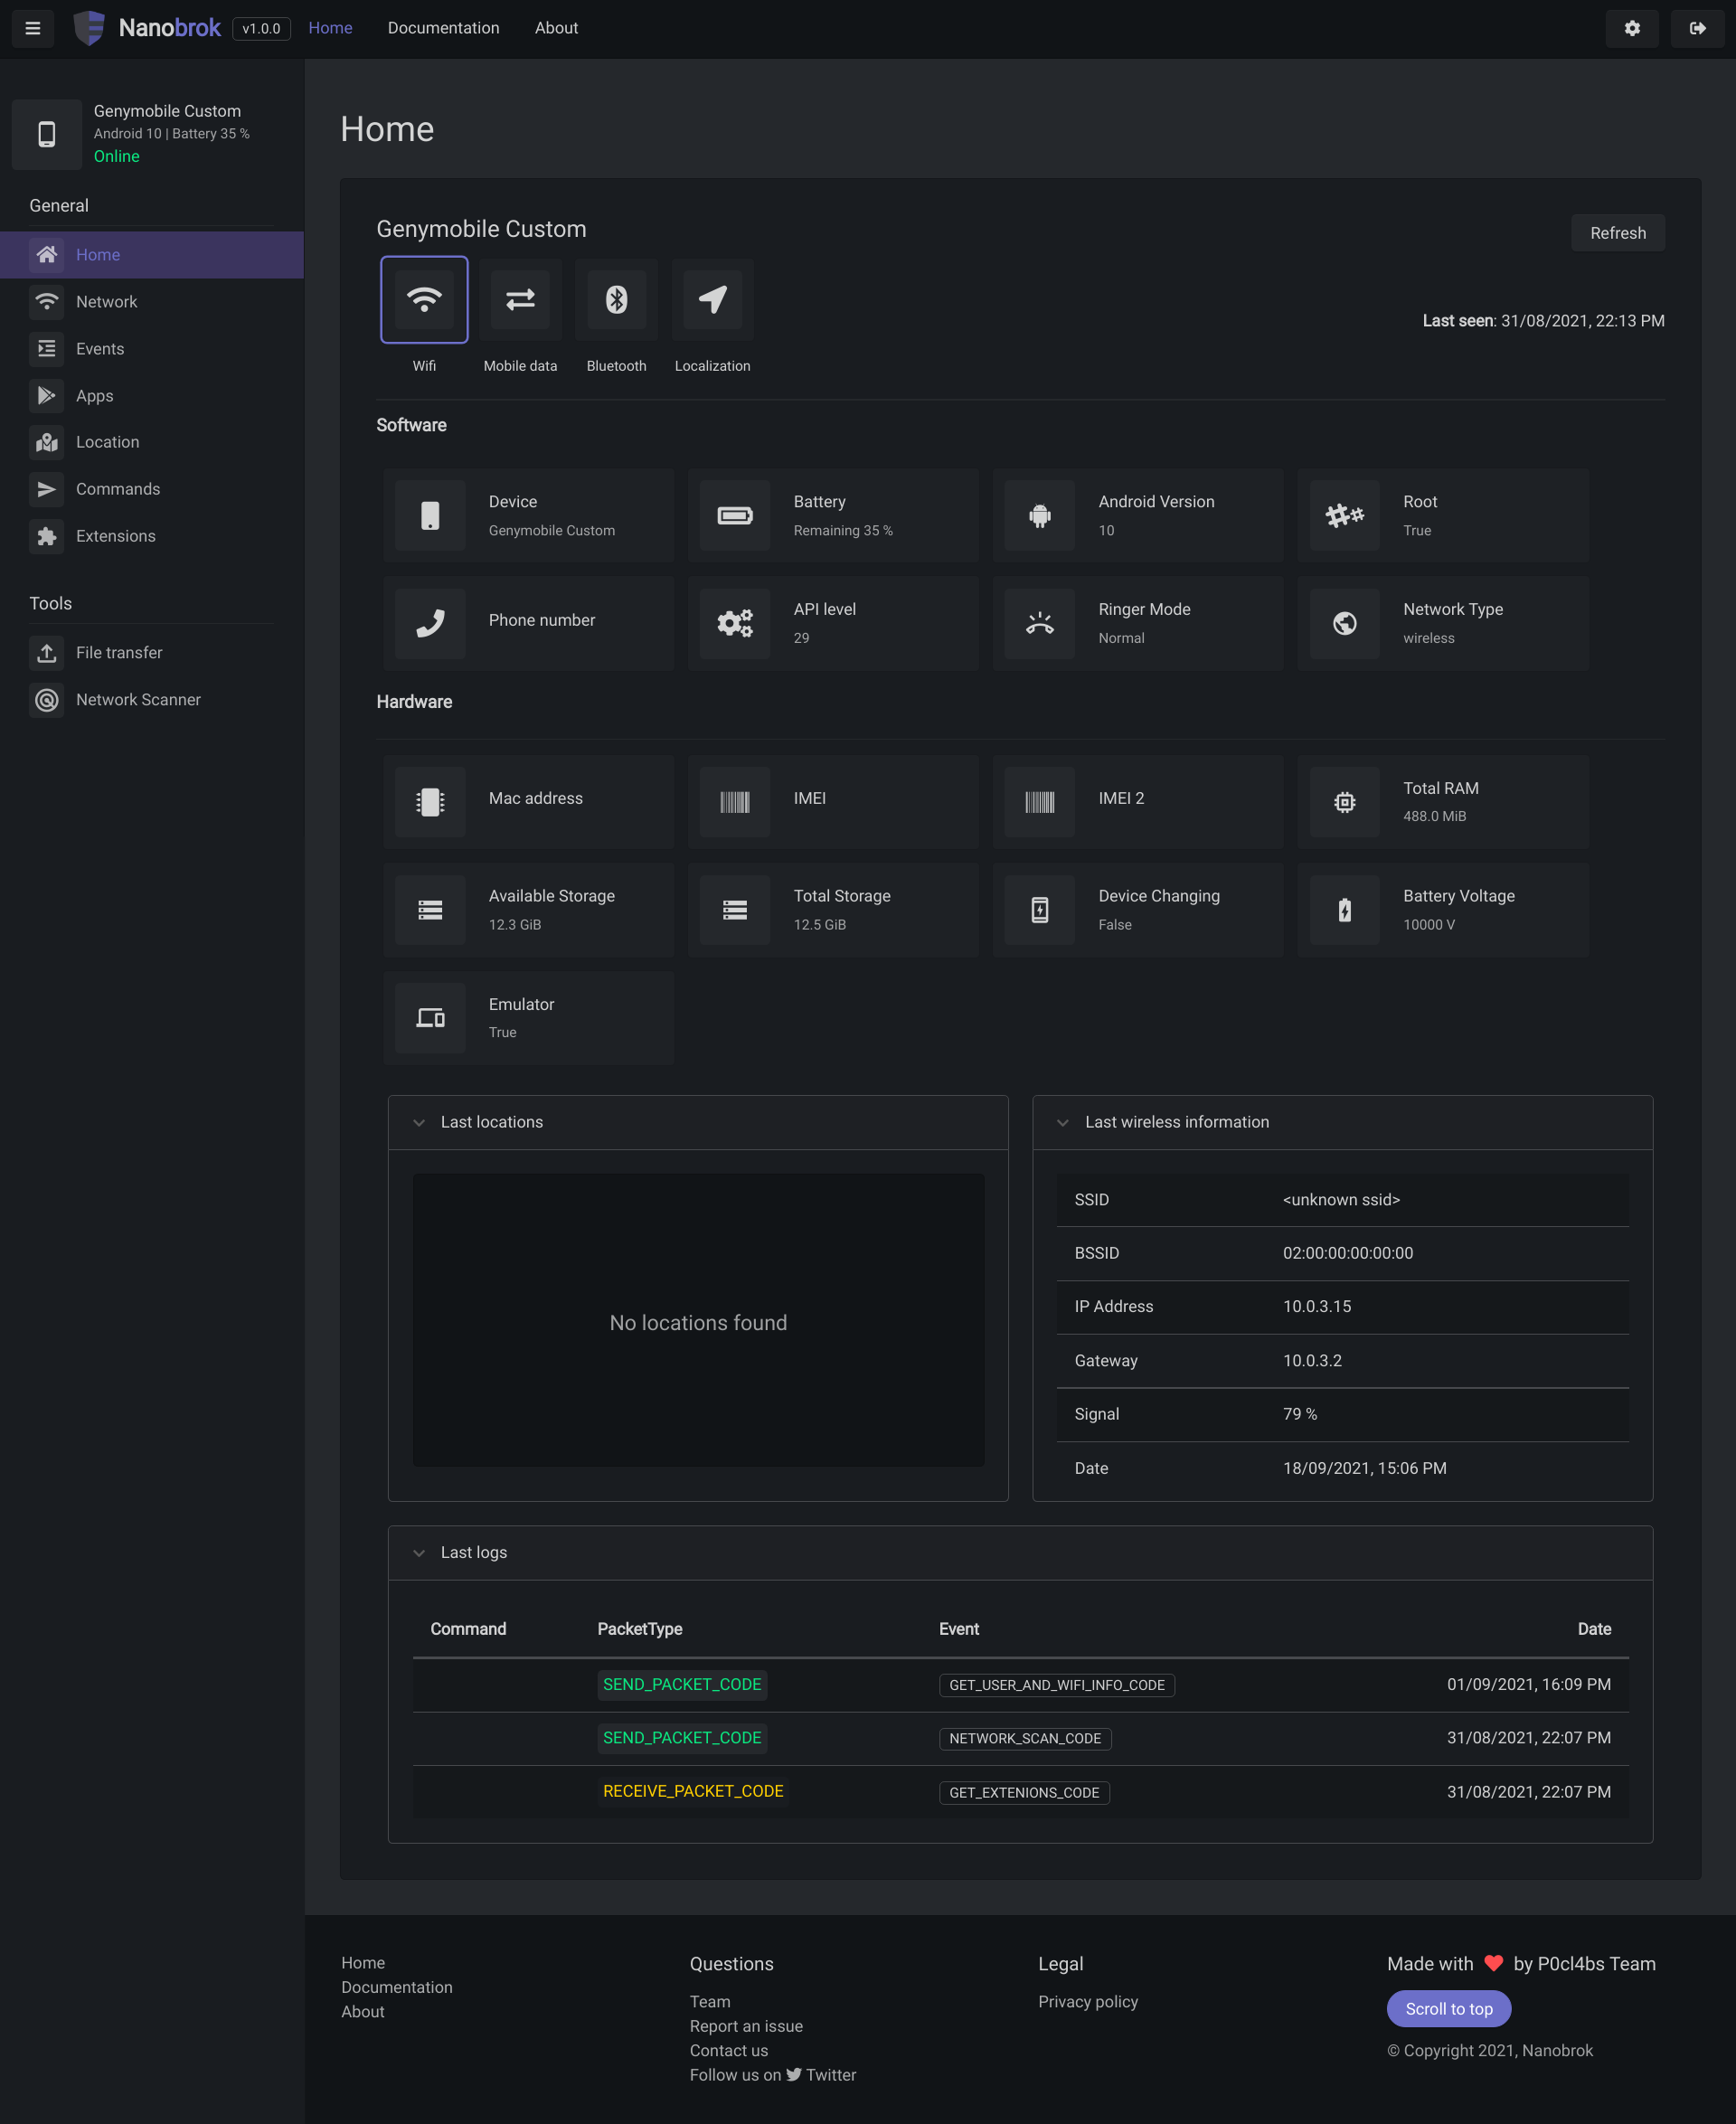 p0cl4bs/nanobrok
Web Service write in Python for control and protect your android device remotely.
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…