

CVE-2022-28346
 yougina/cve-2022-28346
SQL injection in QuerySet.annotate(), aggregate(), and extra()
educationlabs-practicepenetration-testing+2
24 years ago
yougina/cve-2022-28346SQL injection in QuerySet.annotate(), aggregate(), and extra()
 zer0qs/cve-2021-35042
A basic analysis about CVE-2021-35942. SQL injection in Django.
 error-inside/cve-2026-47670
Authenticated Remote Code Execution via loadReader functionName code injection in DbGate
 cc3305/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua scripting enabling remote code execution. Targets specific Redis…

 themehackers/cve-2026-34038
CVE-2026-34038: Authenticated Remote Command Injection in Coolify
 typicalsmc/cve-2025-49132-poc
Proof-of-concept exploit for CVE-2025-49132, a path traversal vulnerability in Pterodactyl panel. Forges session cookies using exposed Redis server…
 yunus-a1i/veeam-cve-2023-27532-mock
Nuclei-based detection template for CVE-2023-27532 in Veeam Backup & Replication, enabling automated credential extraction vulnerability scanning…
 snailsploit/cve-2025-9776
CVE-2025-9776 — CatFolders WordPress Plugin: Authenticated SQL Injection via CSV Import | POC + Walkthrough
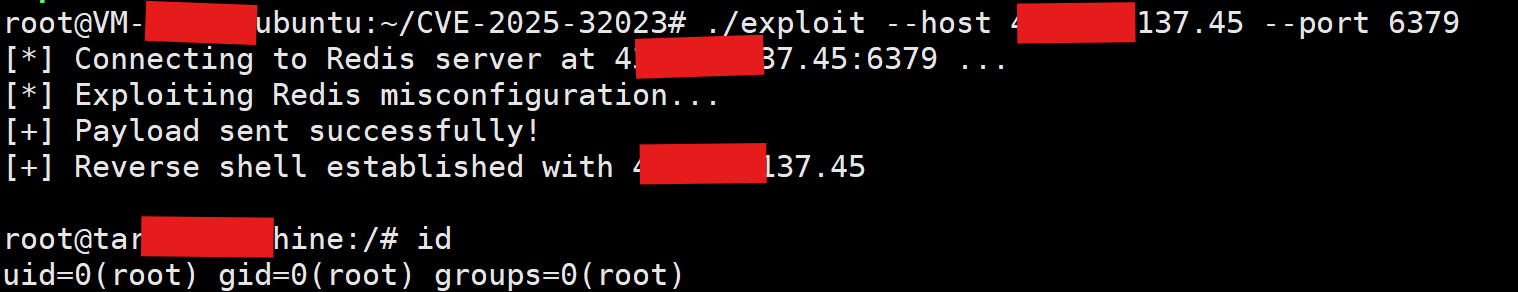 lordbheem/cve-2025-32023
Exploit for CVE-2025-32023
 gmh5225/actions-secrets
Adding this GitHub Action will scan your repository for sensitive data in your source code. We find things like passwords, server host strings, API…
 0xdtc/sqlpad-6.10.0-exploit-cve-2022-0944
Refurbish
 kai2er/cve-2024-0044-exp
利用CVE-2024-0044 在Android12、13 没有root'下进行数据备份 用法./CVE-2024-0044-EXP.sh <package_name>
 terracatta/name_reverser
Silly Rails App to demonstrate vuln CVE-2013-0156
 echo-devim/cve-2022-48429_poc
Proof-of-concept exploit for CVE-2022-48429, a stored cross-site scripting vulnerability in JetBrains YouTrack dashboards enabling low-privileged…

 roxanne_ardary/real-estate
Specifications and open-source platforms for self-sovereign, encrypted real estate data management with blockchain-inspired verification, enabling…