
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
308 results
CVE-2025-61148 preview

CVE-2025-61148

GitHubsharma19d/cve-2025-61148

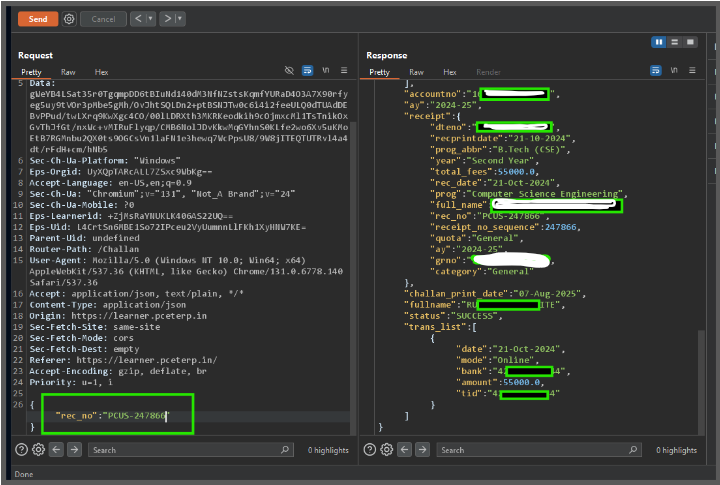
The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
api-security-testingeducationinformation-gathering+3
11 months ago
CVE-2025-12720 preview

CVE-2025-12720

GitHubd0n601/cve-2025-12720

g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
api-security-testingauthenticationexploitation+3
0 years ago
CVE-2023-45857-Demo preview

CVE-2023-45857-Demo

GitHubfuyuooumi1027/cve-2023-45857-demo

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
api-security-testingctfeducation+3
12 years ago
CVE-2025-51867 preview

CVE-2025-51867

GitHubsecsys-fdu/cve-2025-51867

Demonstrates an Insecure Direct Object Reference (IDOR) vulnerability in Deepfiction AI's chat API, allowing attackers to consume other users'…
api-security-testinginformation-gatheringpenetration-testing+3
1 year ago
CVE-2025-51862 preview

CVE-2025-51862

GitHubsecsys-fdu/cve-2025-51862

Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…
api-security-testingexploitationpenetration-testing+3
1 year ago
CVE-2024-50633 preview

CVE-2024-50633

GitHubcetinpy/cve-2024-50633

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
api-security-testingexploitationinformation-gathering+3
1 year ago
Swagger-HTML-Injection-CVE-2025-8191 preview

Swagger-HTML-Injection-CVE-2025-8191

GitHubmayank-s16/swagger-html-injection-cve-2025-8191

XSS Test Swagger 3.14.1 to 3.37.0
api-security-testingexploitationvulnerability-analysis+2
10 months ago
CVE-2024-9707-Poc preview

CVE-2024-9707-Poc

GitHubnxploited/cve-2024-9707-poc

he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)
api-security-testingeducationexploitation+3
1 year ago
CVE-2024-54369 preview

CVE-2024-54369

GitHubrandomrobbiebf/cve-2024-54369

Zita Site Builder <= 1.0.2 - Missing Authorization to Arbitrary Plugin Installation
api-security-testingexploitationmisconfiguration+3
1 year ago
Burp_CVE-2025-31324 preview

Burp_CVE-2025-31324

GitHubblueowl-overlord/burp_cve-2025-31324

Python-based Burp Suite extension is designed to detect the presence of CVE-2025-31324
api-security-testingexploitationpenetration-testing+3
1 year ago
CVE-2023-6289 preview

CVE-2023-6289

GitHubrandomrobbiebf/cve-2023-6289

Swift Performance Lite <= 2.3.6.14 - Missing Authorization to Unauthenticated Settings Export
api-security-testingexploitationinformation-gathering+3
2 years ago
burp-rest-api preview
Archived

burp-rest-api

GitHubvmware-archive/burp-rest-api

REST/JSON API to the Burp Suite security tool.
api-security-testingpenetration-testingscripting-automation+4
5661 year ago
selenium-wire preview
Archived

selenium-wire

GitHubwkeeling/selenium-wire

Extends Selenium's Python bindings to give you the ability to inspect requests made by the browser.
api-security-testinginformation-gatheringpenetration-testing+2
2.0k2 years ago
frida-fuzzer preview
Archived

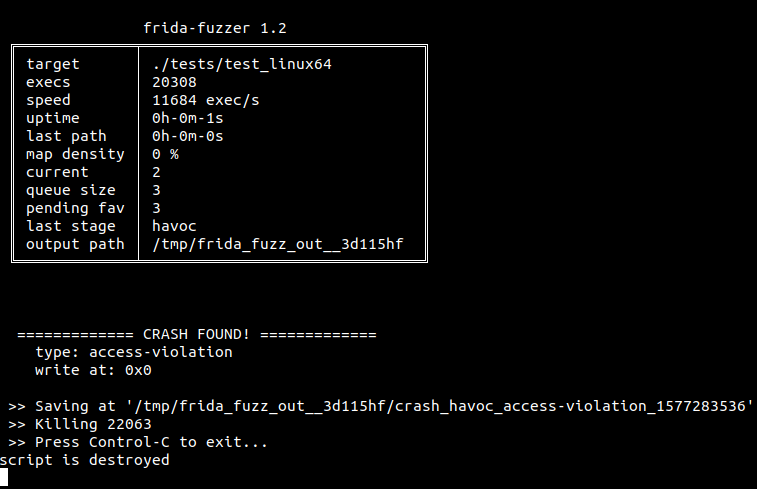
frida-fuzzer

GitHubandreafioraldi/frida-fuzzer

This experimetal fuzzer is meant to be used for API in-memory fuzzing.
api-security-testingbinary-analysisdynamic-analysis-sandboxing+3
5776 years ago
restler-fuzzer preview

restler-fuzzer

GitHubmicrosoft/restler-fuzzer

RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
api-security-testingcloud-securityfuzzing+2
2.9k8 months ago
GraphQLmap preview

GraphQLmap

GitHubswisskyrepo/graphqlmap

Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
api-security-testingctffuzzing+3
1.7k3 years ago
inql preview

inql

GitHubdoyensec/inql

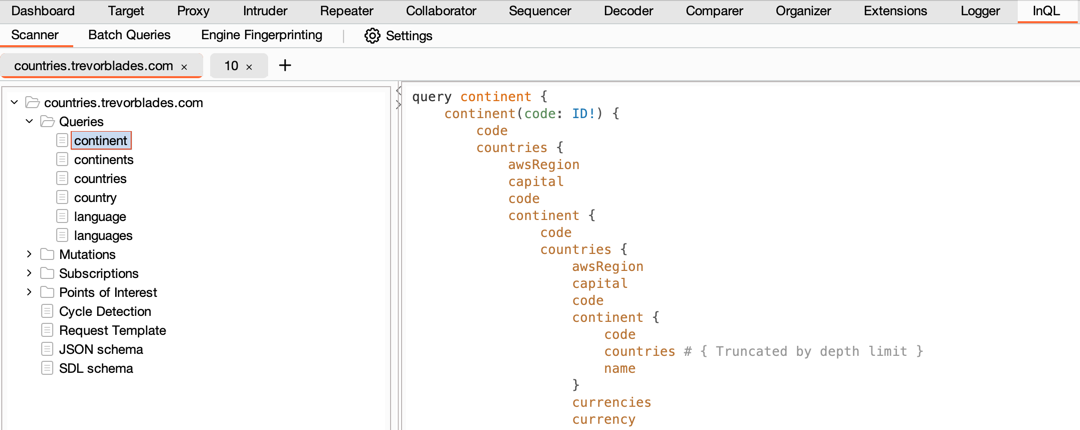
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
api-security-testingpenetration-testingvulnerability-scanners
1.8k8 months ago
waf-bypass preview

waf-bypass

GitHubnemesida-waf/waf-bypass

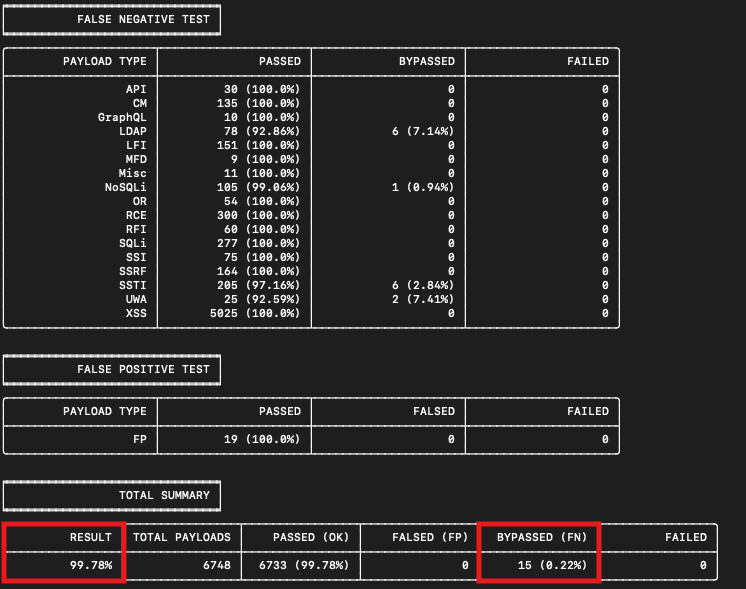
Automated WAF security testing tool that detects false positives and false negatives using 15+ payload categories including SQLi, XSS, RCE, and…

api-security-testingpenetration-testingvulnerability-scanners+2
1.5k3 months ago
Previous1…345…18Next