
SigFlip
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k
med0x2e/sigflipSigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 joelgmsec/evilnovnc
Real-time phishing platform that bypasses 2FA via a live noVNC browser session, capturing cookies, saved passwords, browsing history, and downloaded…
 hannob/snallygaster
Tool to scan for secret files on HTTP servers
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 trustedsec/cs-remote-ops-bof
Remote operations commands implemented using Beacon Object Files
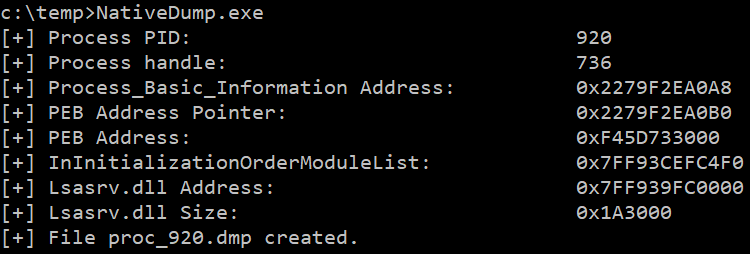 ricardojoserf/nativedump
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
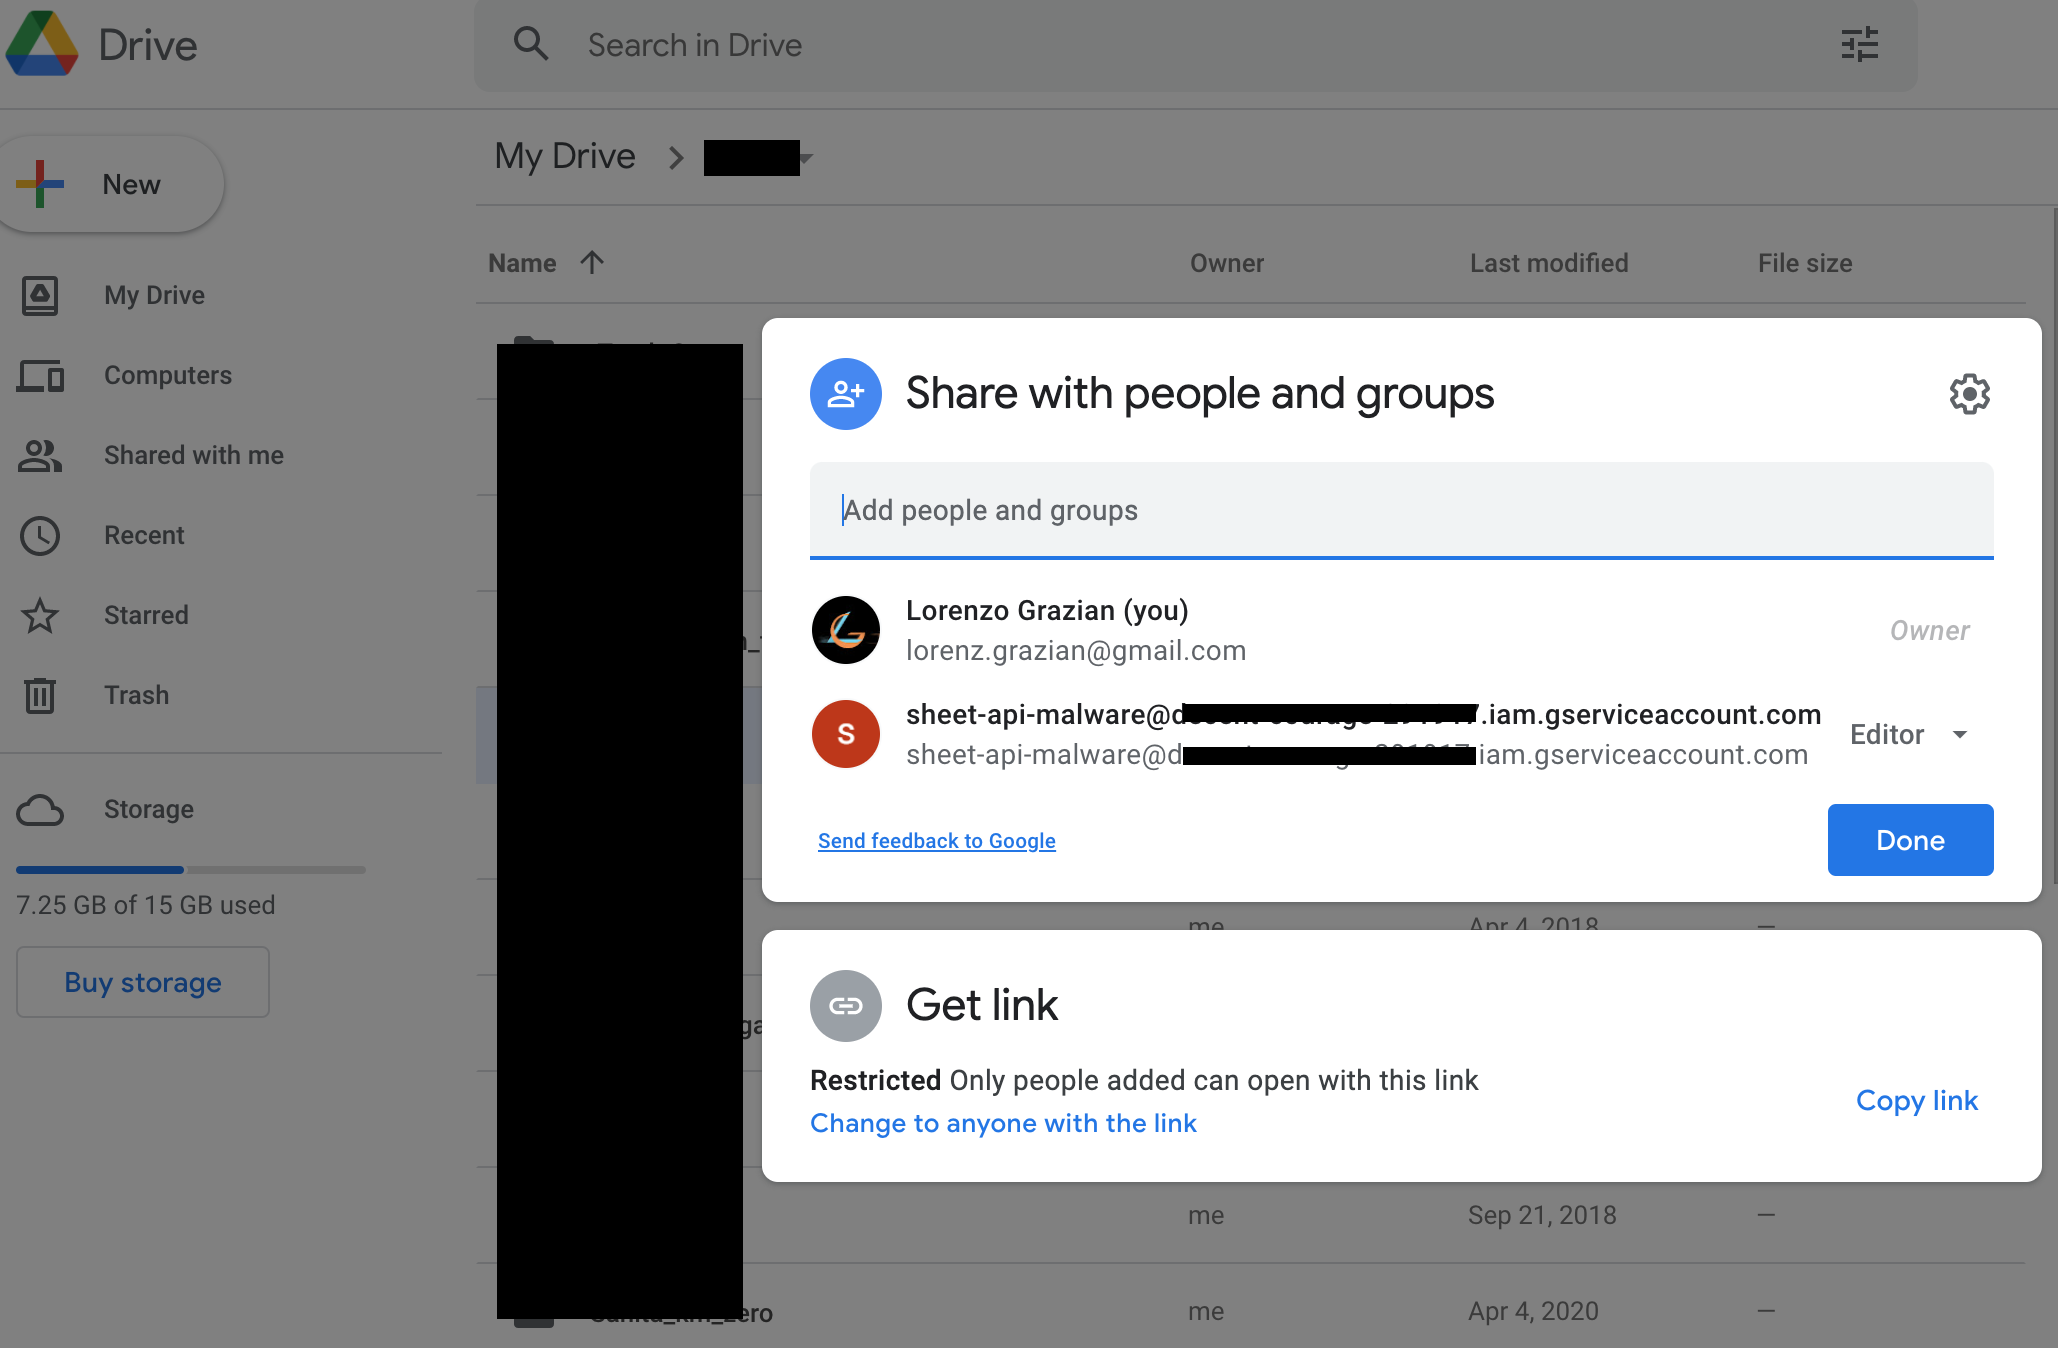 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
 syvaidya/openstego
OpenStego is a steganography application that provides two functionalities: a) Data Hiding: It can hide any data within an image file. b)…
 robre/scripthunter
Tool to find JavaScript files on Websites
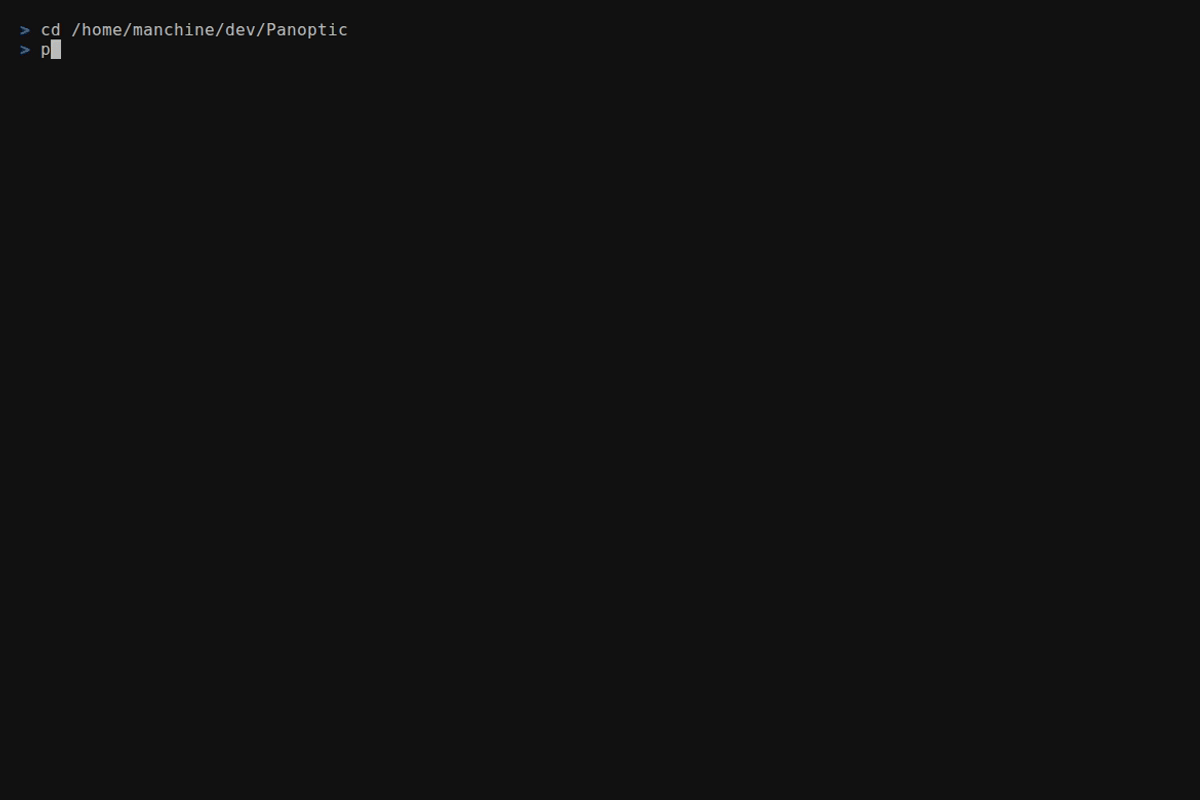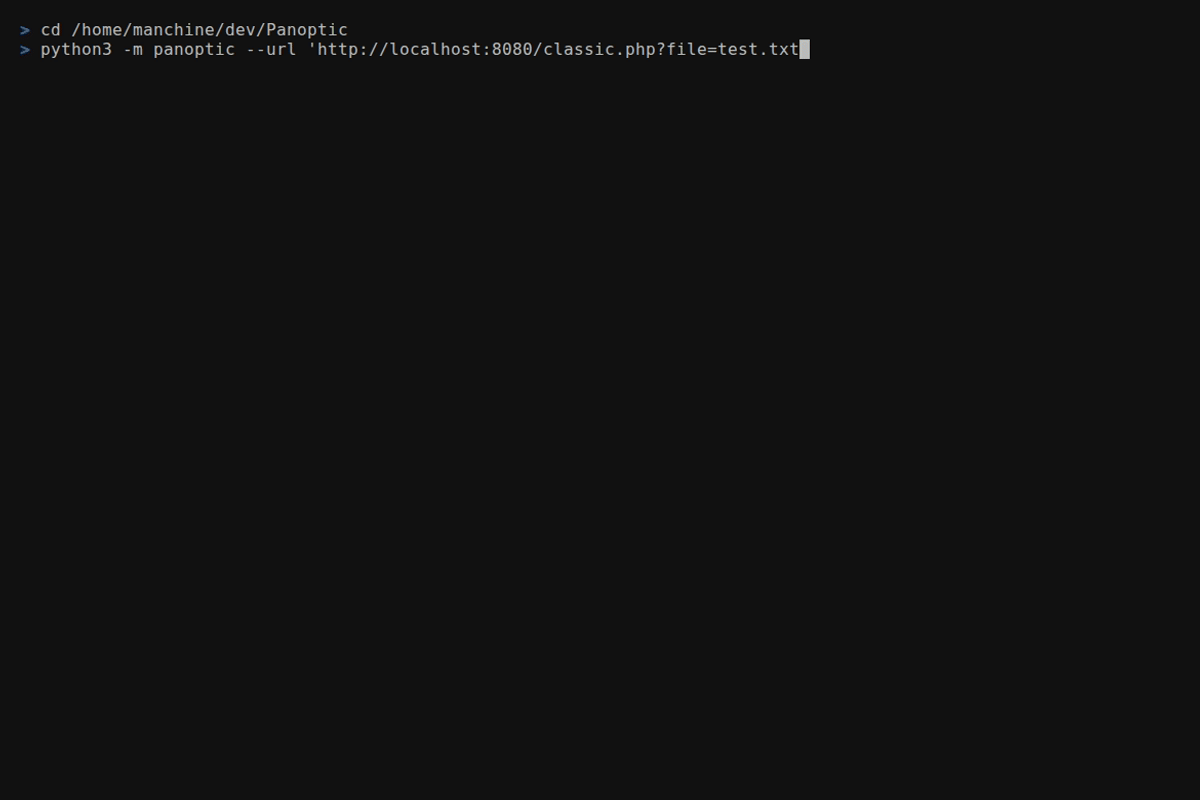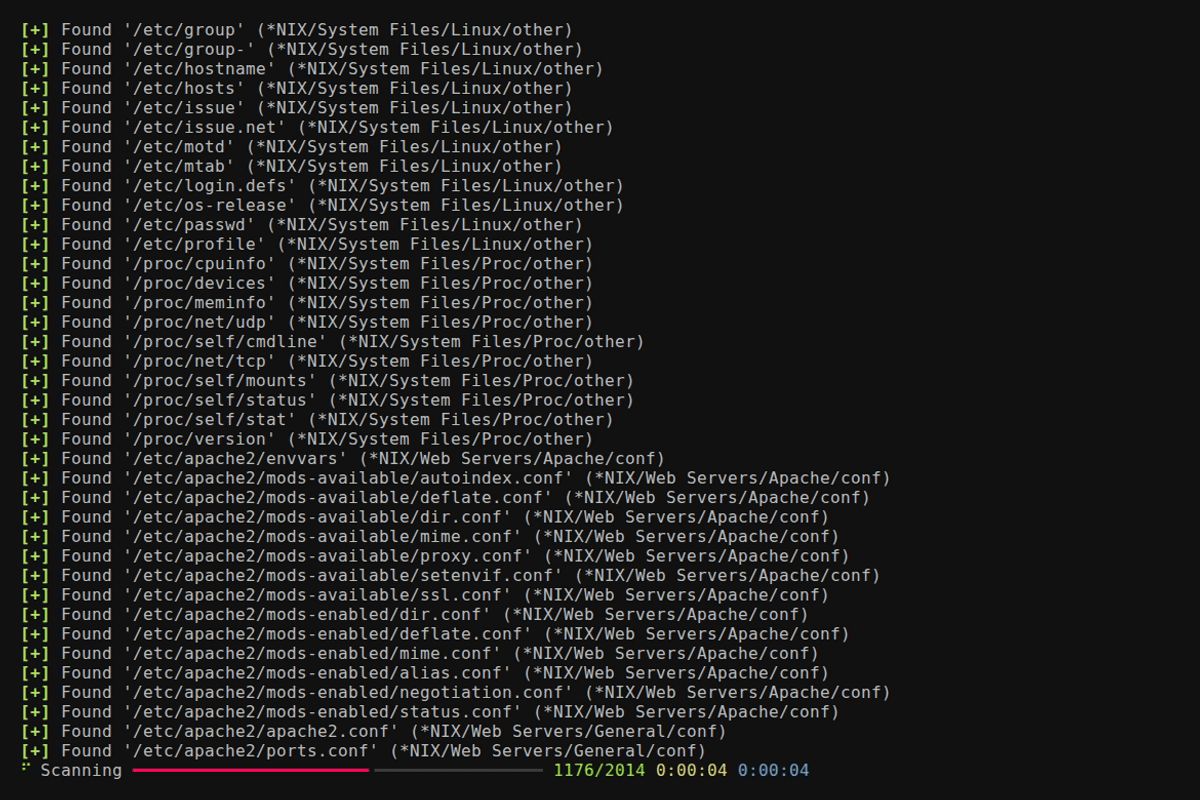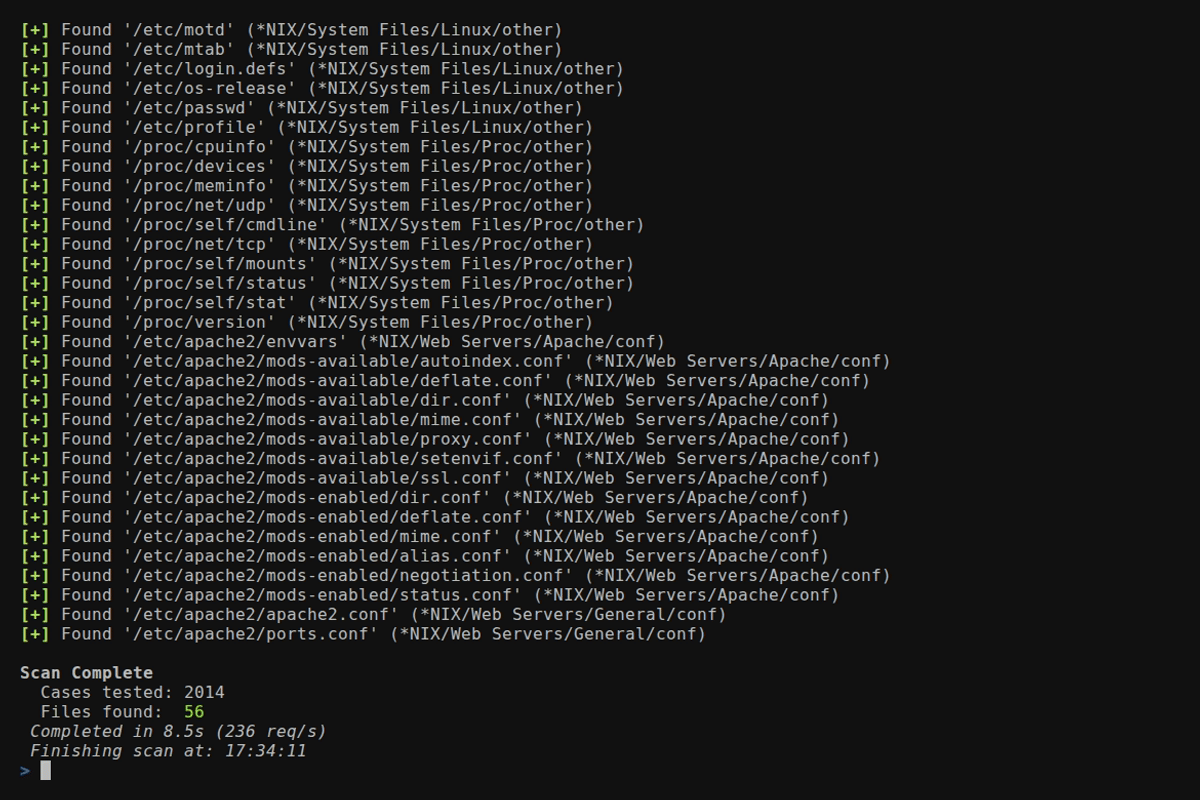 lightos/panoptic
Panoptic is an open source penetration testing tool that automates the process of search and retrieval of content for common log and config files…
 frkngksl/shoggoth
Polymorphic encryptor that transforms shellcode, PE, and COFF files into obfuscated, position-independent payloads with RC4 and random block cipher…
 webbreacher/obsidian-osint-templates
These templates are suggestions of how the Obsidian notetaking tool can be used during an OSINT investigation. The example data in those files should…
 intel/intel-linux-processor-microcode-data-files
Official Intel microcode data files for updating processor firmware to mitigate security vulnerabilities and address functional issues on Linux…
 pedrib/poc
Advisories, proof of concept files and exploits that have been made public by @pedrib.
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc