
CVE-2023-31594
 yozarseef95/cve-2023-31594
IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
exploitationhardware-securityiot-security+3
yozarseef95/cve-2023-31594IC Realtime ICIP-P2012T 2.420 is vulnerable to Incorrect Access Control
 b0marek/cve-2023-4631
Repository for CVE-2023-4631 vulnerability.
 chinayozz/cve-2020-25078
Batch exploit script for CVE-2020-25078 targeting D-Link DCS series cameras to extract account credentials via information disclosure vulnerability.
 biitts/poc-ingressnightmare-cve-2025-1974
Builds a shell.so reverse shell payload for CVE-2025-1974 (IngressNightmare) using Alpine Linux in Docker, with hardcoded IP and port configuration.
 bootedup420/tcpdominate2024
USED BY IP STRESSER & IP BOOTER TOOLS, TCP DOMINATE FLOOD UPDATED IN 2025 BY AI SAME ONE USED IN https://top10booters.co
 snailsploit/cve-2026-33693
CVE-2026-33693: SSRF via 0.0.0.0 Bypass in activitypub-federation-rust v4_is_invalid() (CVSS 6.5 Moderate)
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
 featherstark/cve-2024-21793
Proof-of-concept exploit for CVE-2024-21793 targeting F5 BIG-IP vulnerabilities, enabling security researchers to test and validate exposure in…
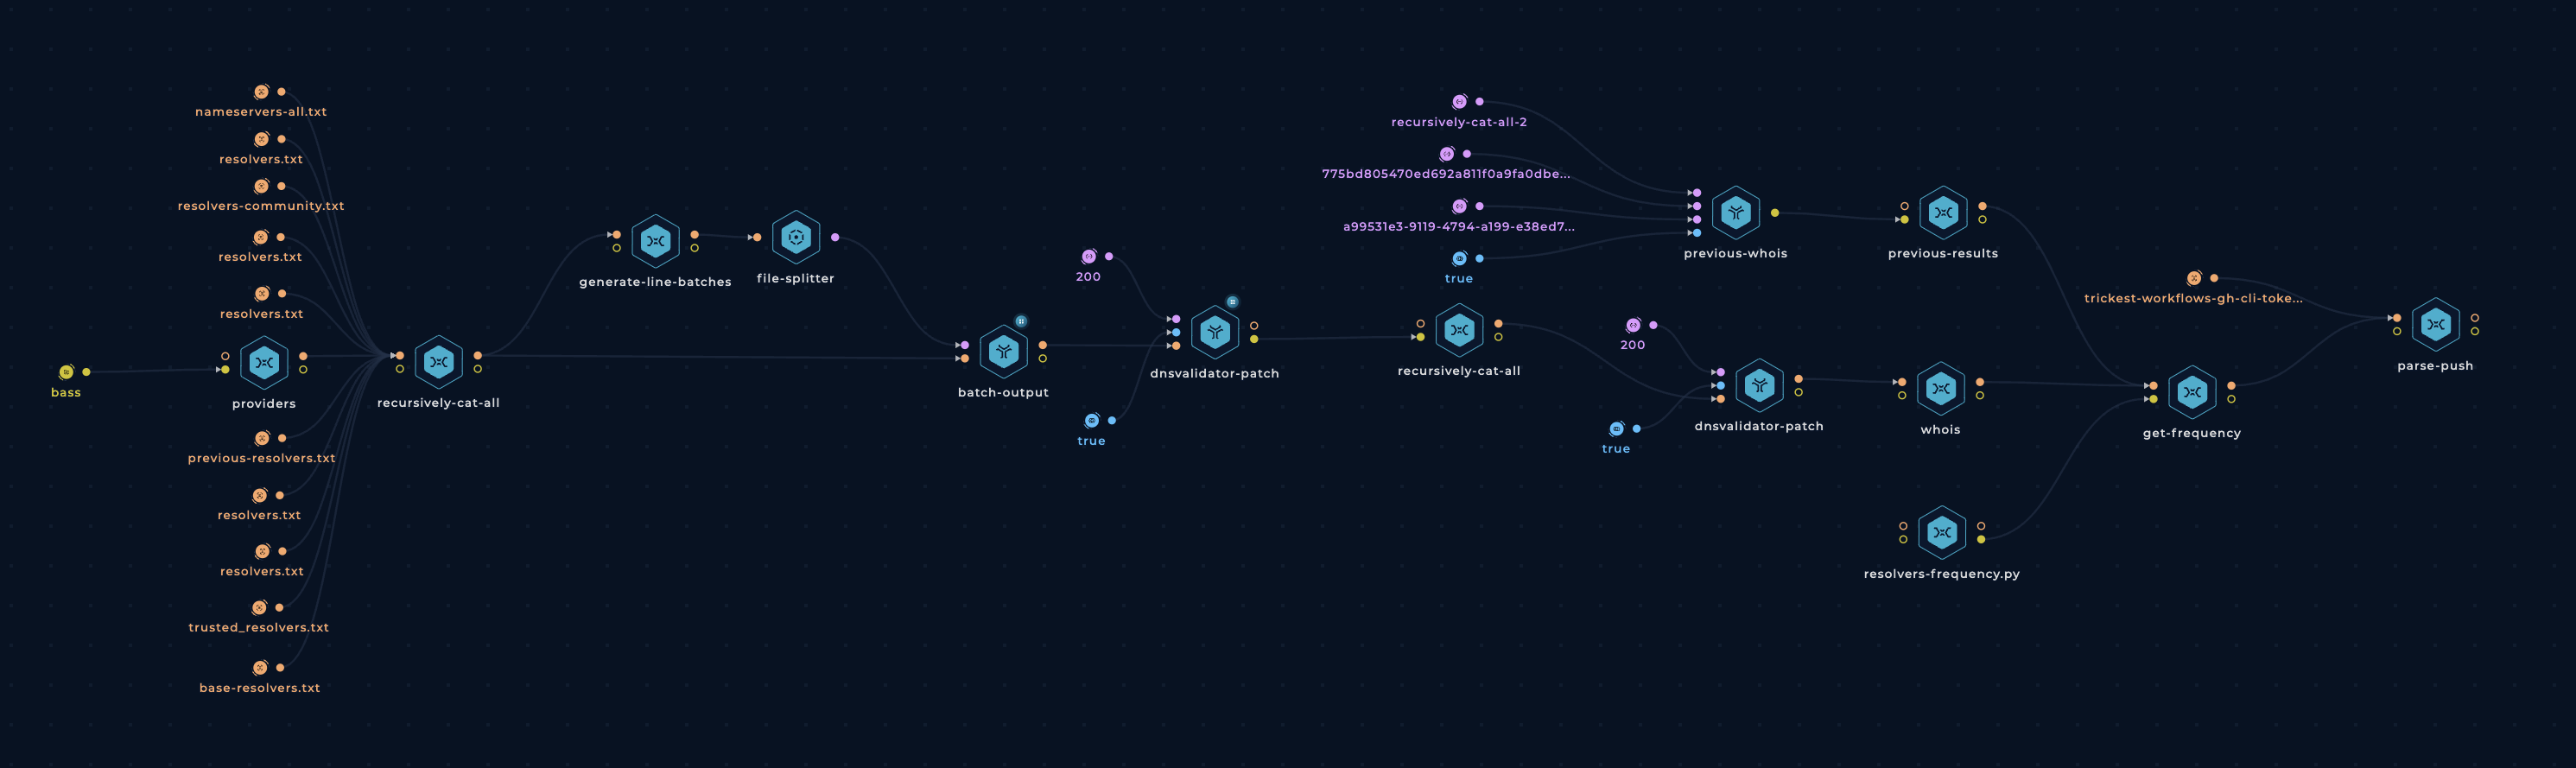 trickest/resolvers
The most exhaustive list of reliable DNS resolvers.
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 passwa11/cve-2024-26026
CVE-2024-26026: BIG-IP Next Central Manager API UNAUTHENTICATED SQL INJECTION
 sic4rio/cve-2015-3224
Ruby on Rails Web Console Exploit (CVE-2015-3224)
 0xblackash/cve-2020-5902
CVE-2020-5902
 234329a423853/cve-2021-4045
CVE-2021-4045 CVE-2021-4045 is a Command Injection vulnerability that allows Remote Code Execution in the TP-Link Tapo c200 IP camera. It affects all…
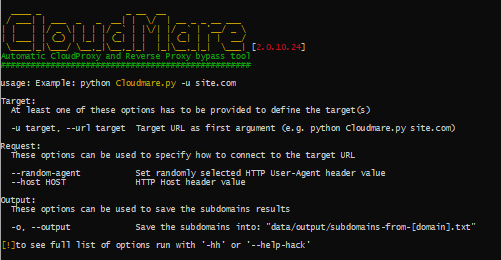 mrh0wl/cloudmare
Cloudflare, Sucuri, Incapsula real IP tracker.
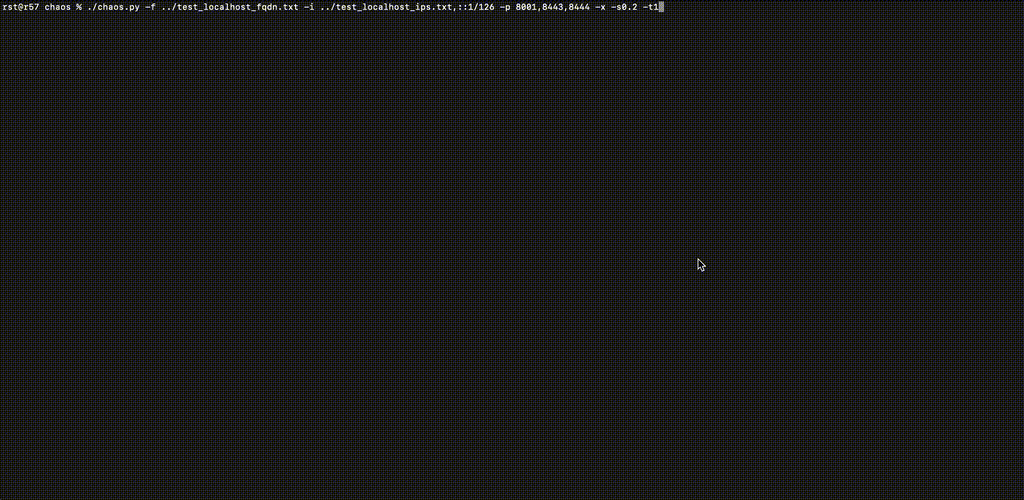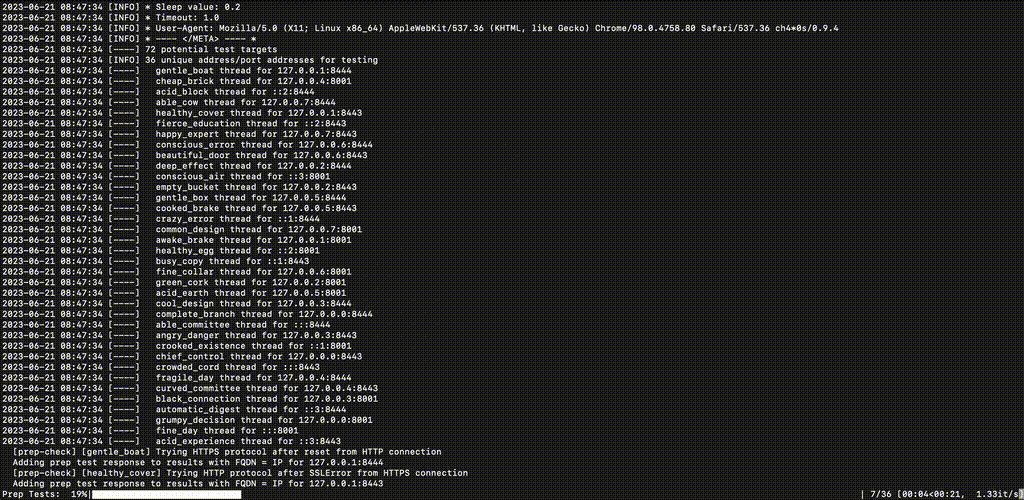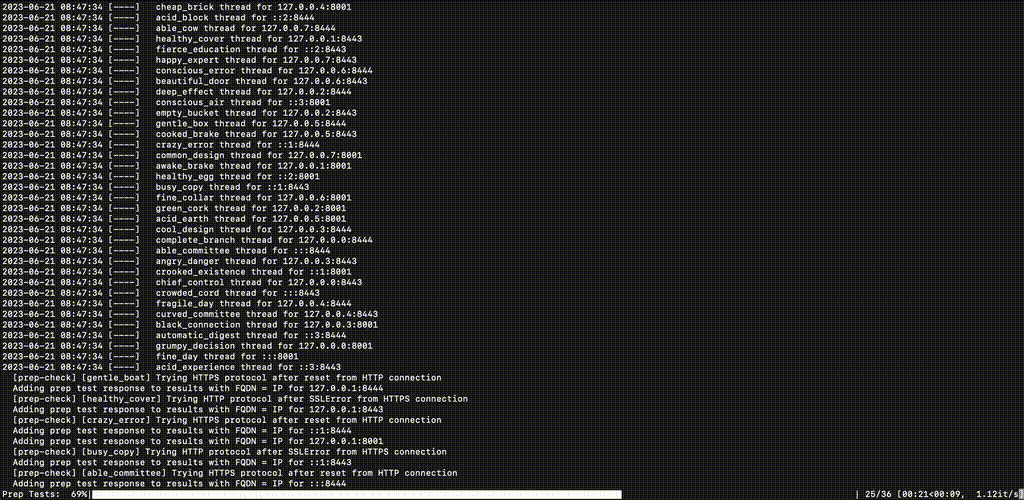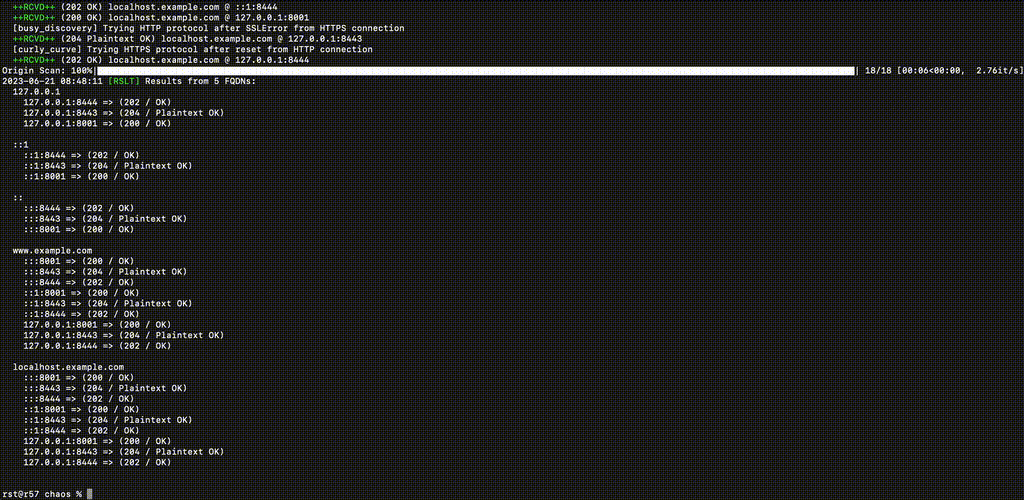 r57-labs/chaos
Origin IP scanning utility developed with ChatGPT
 l1-0/cve-2023-30146
Some Assmann manufactured IP-Cams leak the administrator password in their backup.
 herculesrd/vsftpd2.3.4pyexploit
An exploit to get root in vsftpd 2.3.4 (CVE-2011-2523) written in python