CVE-2026-48908-by-yora
 yora1928/cve-2026-48908-by-yora
Passive security checker for CVE-2026-48908 affecting SP Page Builder.
exploitationinformation-gatheringpayload-generation+7
2
yora1928/cve-2026-48908-by-yoraPassive security checker for CVE-2026-48908 affecting SP Page Builder.
 i3it/cve-2026-18322
Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…
 akashsingh0454/cve-2026-0257-poc
Passive, read-only remote detection tool for CVE-2026-0257, an authentication bypass in Palo Alto Networks PAN-OS GlobalProtect. Fingerprints PAN-OS…
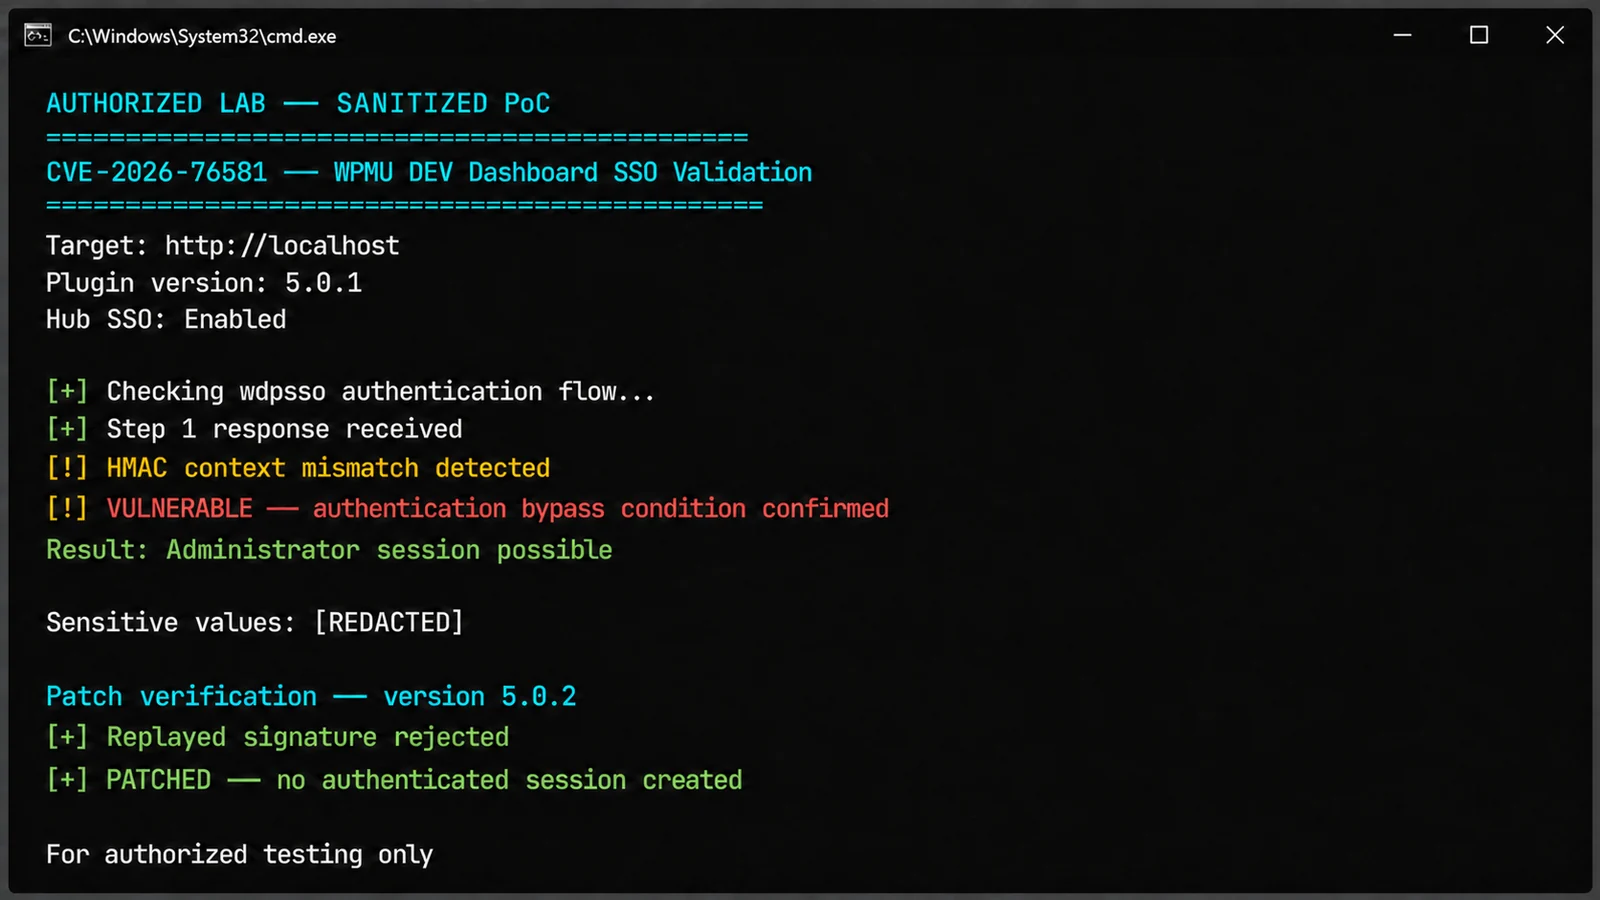 hackersroot/cve-2026-76581-detector
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.
 0xdenis77/cve-2026-56291
Mendeteksi versi (passive detection) & Exploitation CVE POC
 aa022/cve-2026-23918-passive-audit
Passive HTTP metadata auditor for CVE-2026-23918 exposure triage
 rav1010/cve-2026-27636
Passive reconnaissance and fingerprinting tool for detecting FreeScout deployments and analyzing exposure related to CVE-2026-28289, aiding…
 rxerium/cve-2025-58360
Passive detection for CVE-2025-58360
 intelligent-ears/cve-2025-68613
Nuclei-based detection template for CVE-2025-68613, a critical RCE in n8n workflow automation. Uses multi-layered passive fingerprinting to identify…
 kannthu/cve-2021-44228-apache-log4j-rce
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) with JNDI injection payloads, WAF bypass techniques, and passive scanning integration for…

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 elmasy-com/columbus-server
API-first subdomain discovery service using Certificate Transparency logs for fast, passive enumeration of subdomains via a REST API with JSON or…
 ankhcorp/nuke.sh
Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).
 portswigger/active-scan-plus-plus
Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…
 guelfoweb/knockpy
Knock Subdomain Scan
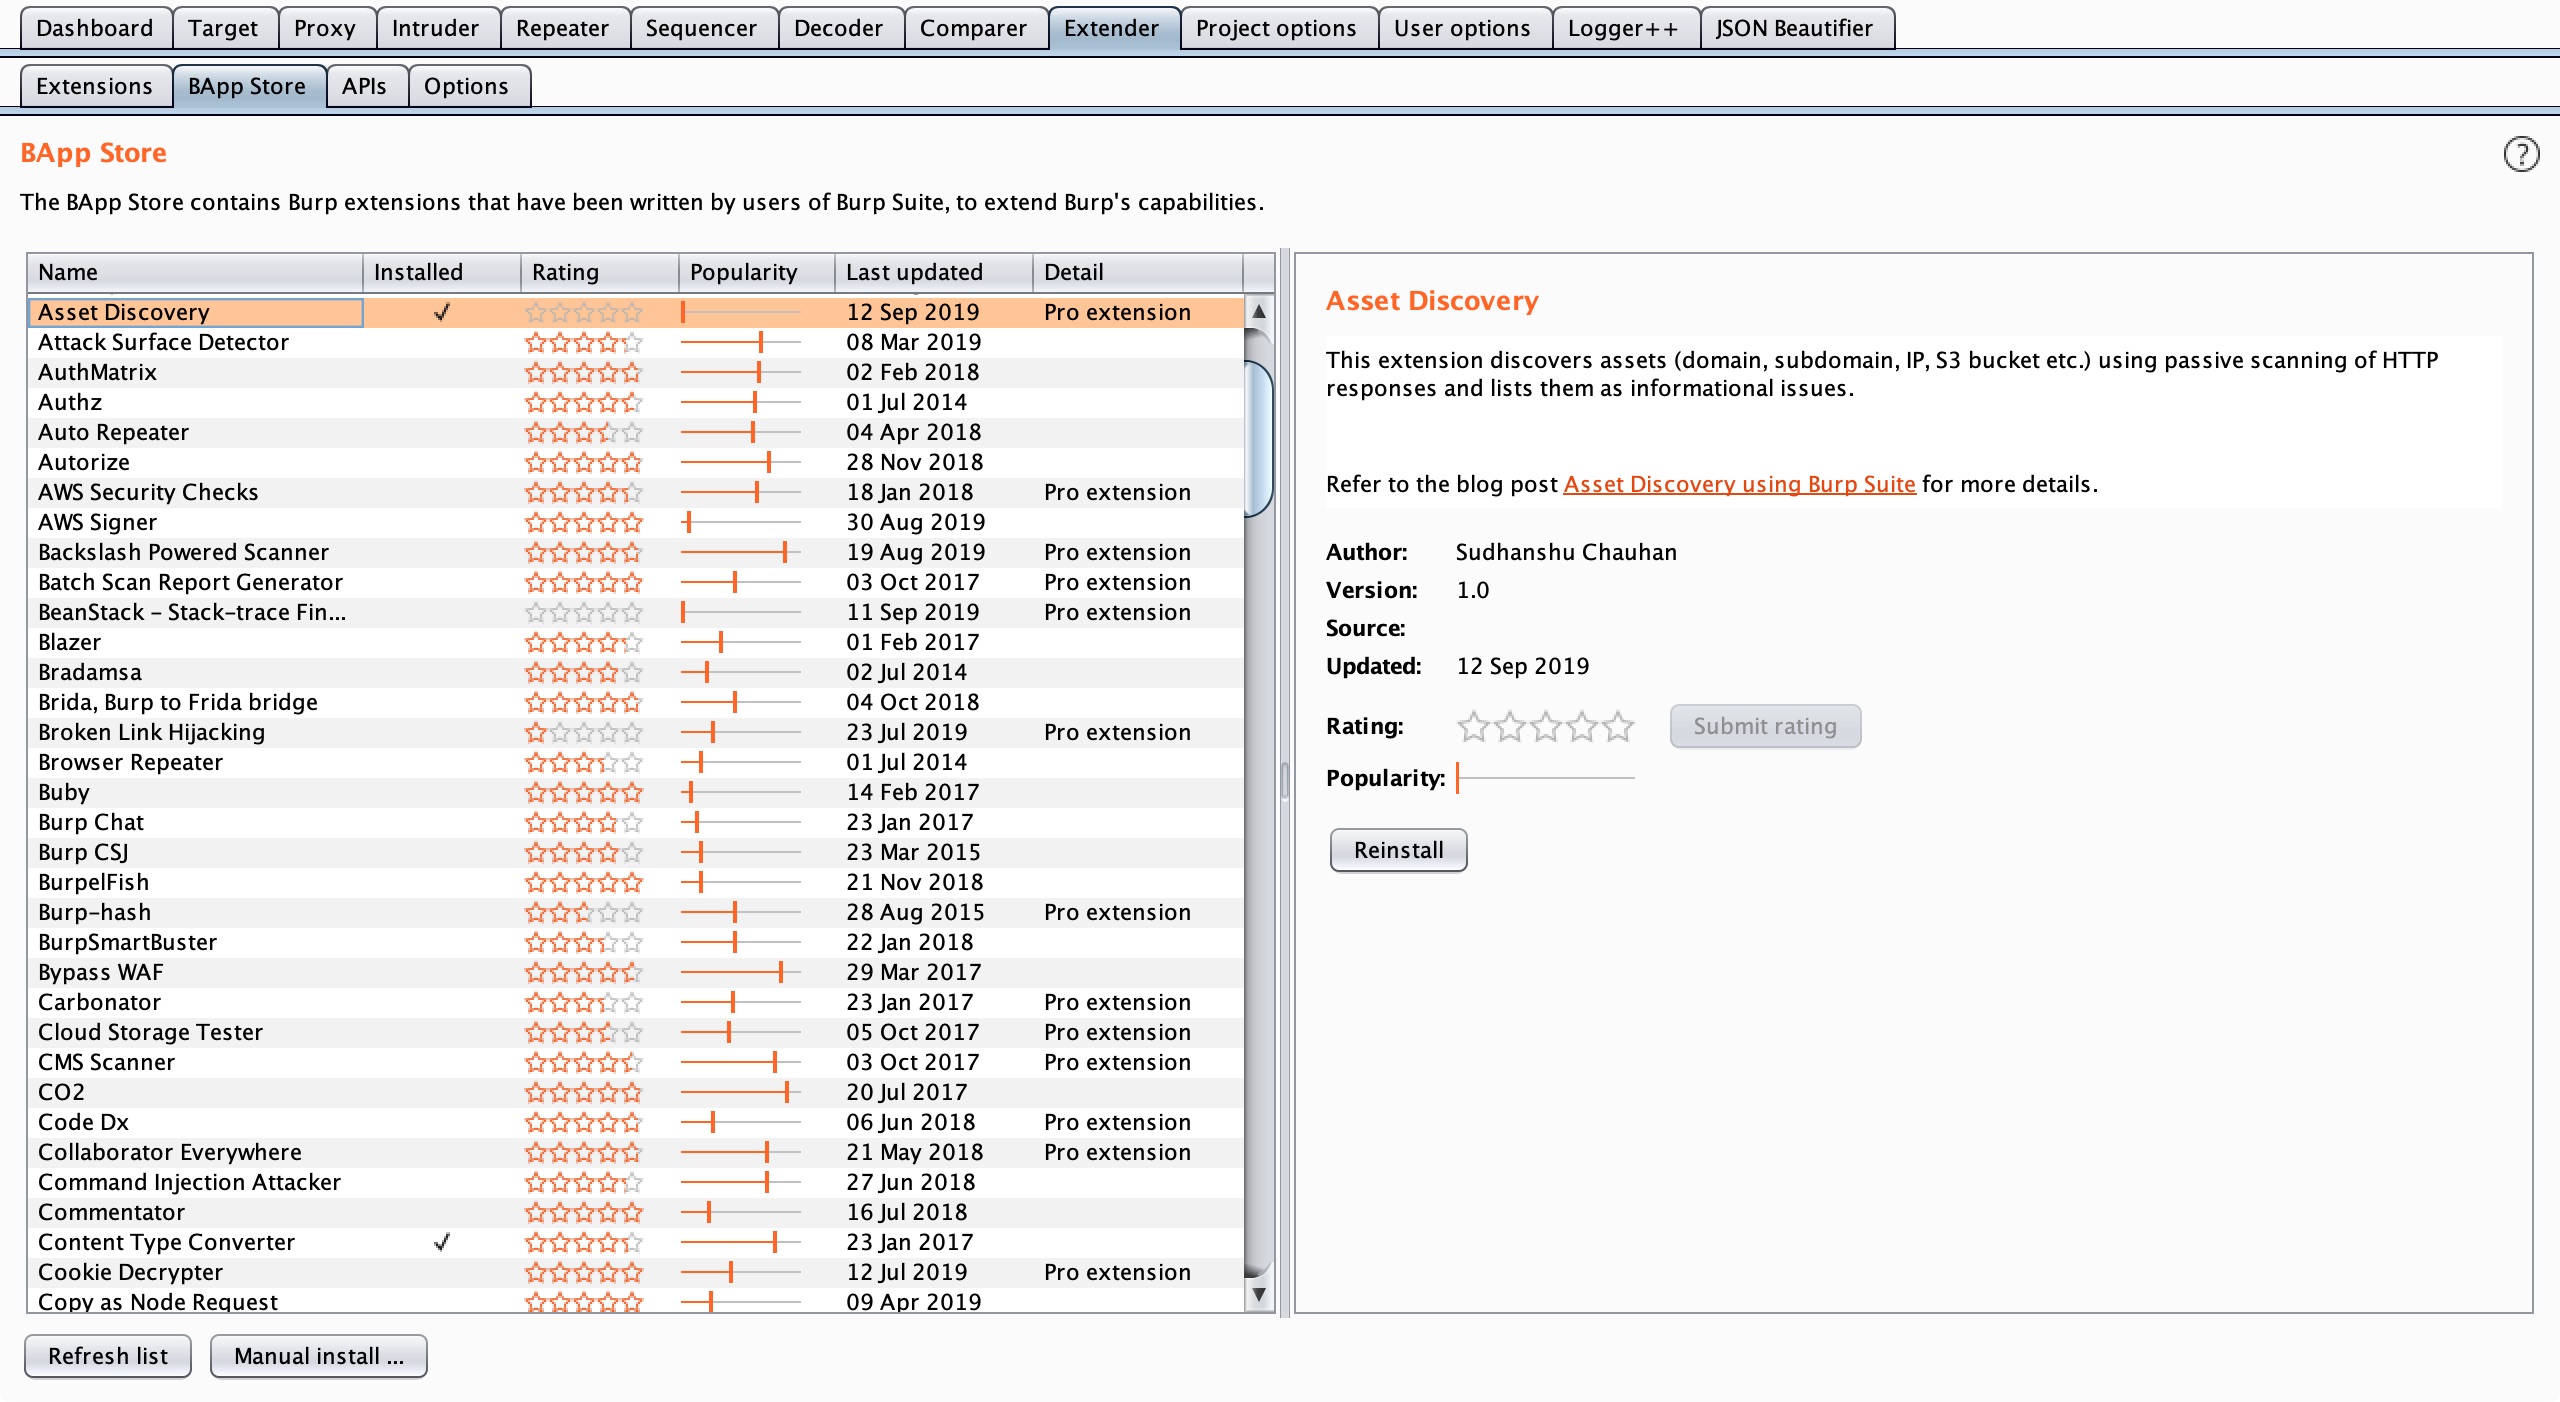 redhuntlabs/burpsuite-asset_discover
Burp Suite extension to discover assets from HTTP response.