SessionHop
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
lateral-movementpenetration-testingpost-exploitation+2
3lp4tr0n/sessionhopWindows Session Hijacking via COM
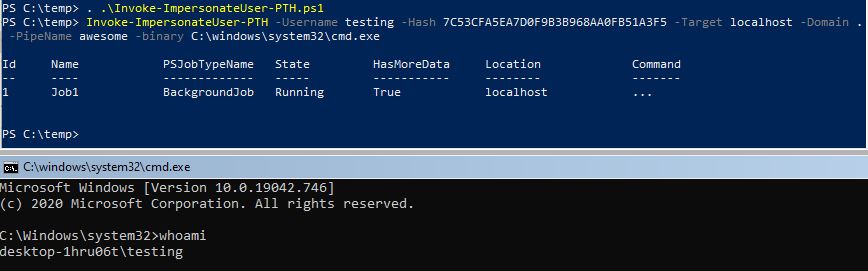 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 nccgroup/keimpx
Check for valid credentials across a network over SMB
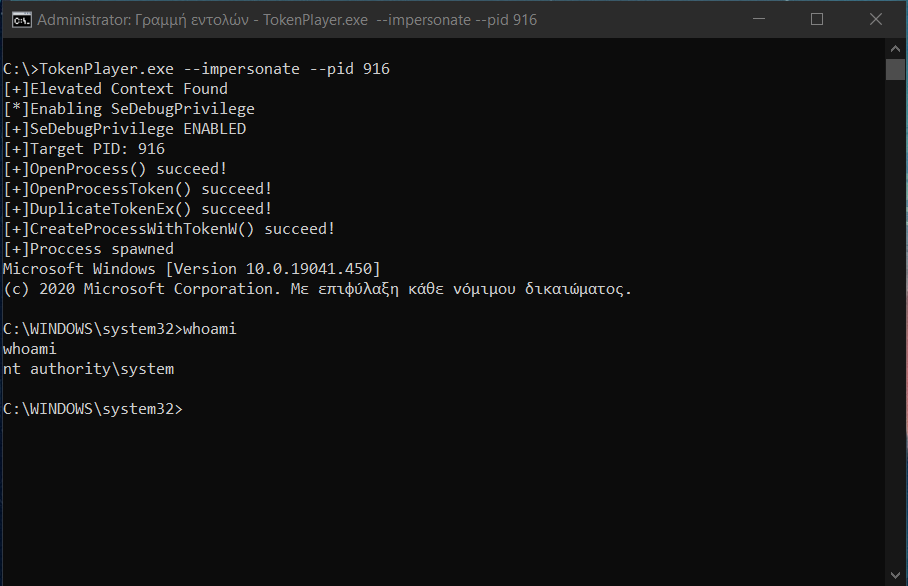 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.
 zettahack/pastezort
Pastejacking - PasteZort
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 synacktiv/prox-ez
HTTP/HTTPS interception proxy for testing Windows authentication mechanisms, supporting NTLM, Kerberos, pass-the-hash, pass-the-ticket and relay…
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 carmaa/nacker
Nacker is a tool to circumvent 802.1x Network Access Control (NAC) on a wired LAN. Nacker will help you locate any non-802.1x configurable hosts on…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
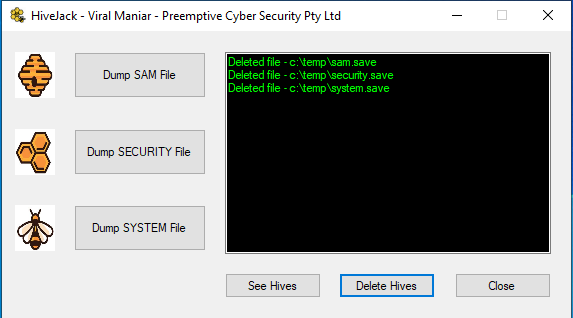 viralmaniar/hivejack
This tool can be used during internal penetration testing to dump Windows credentials from an already-compromised host. It allows one to dump SYSTEM,…
 rweijnen/createdump
Leverage WindowsApp createdump tool to obtain an lsass dump
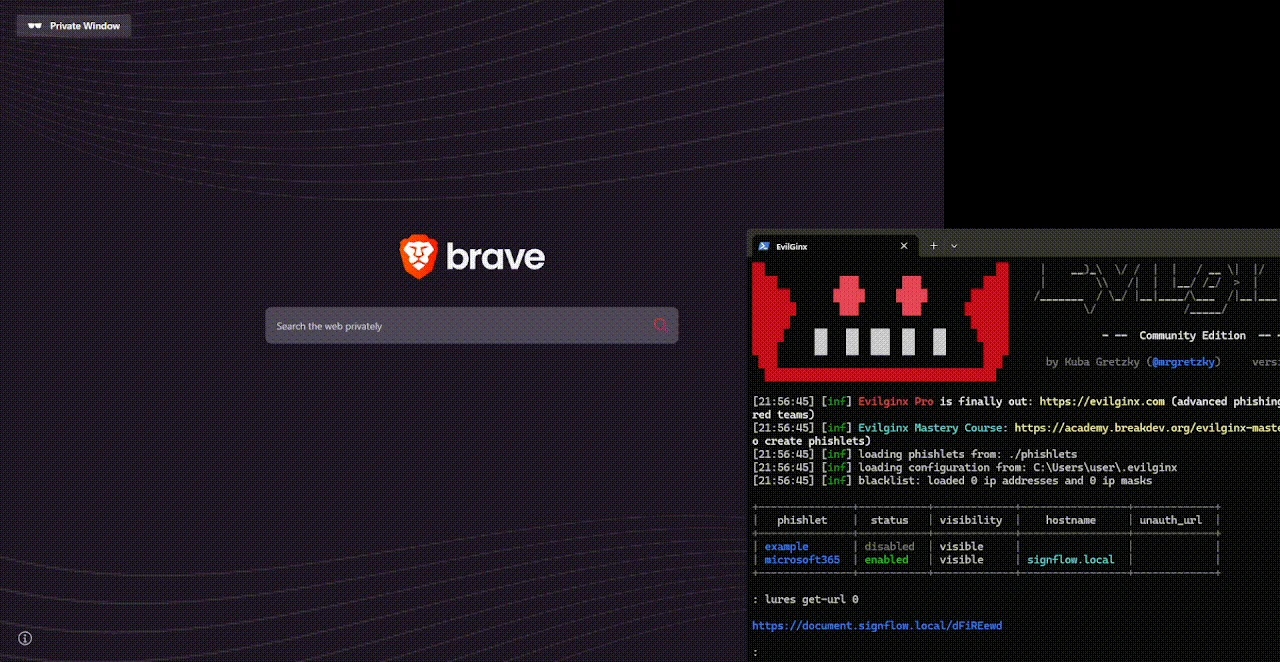 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
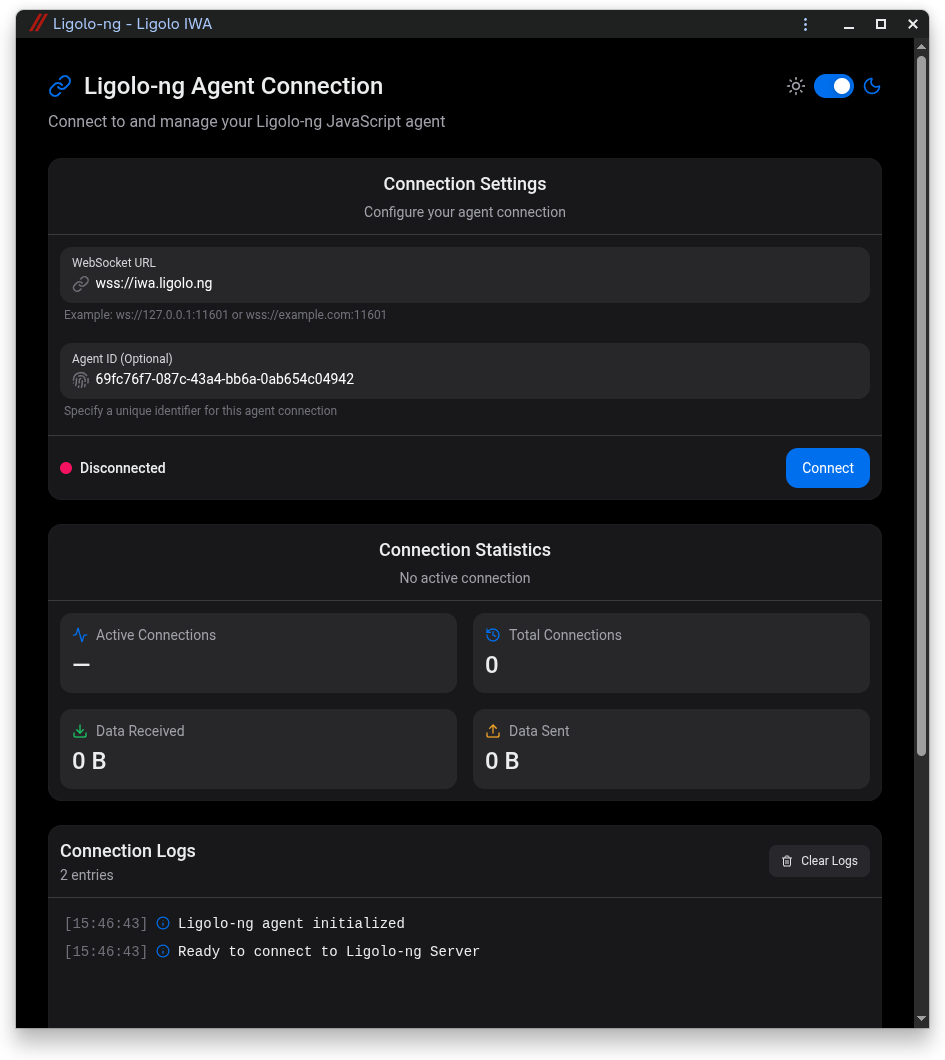 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.
 eversinc33/sharpstartwebclient
Programmatically start WebClient from an unprivileged session to enable that juicy privesc.
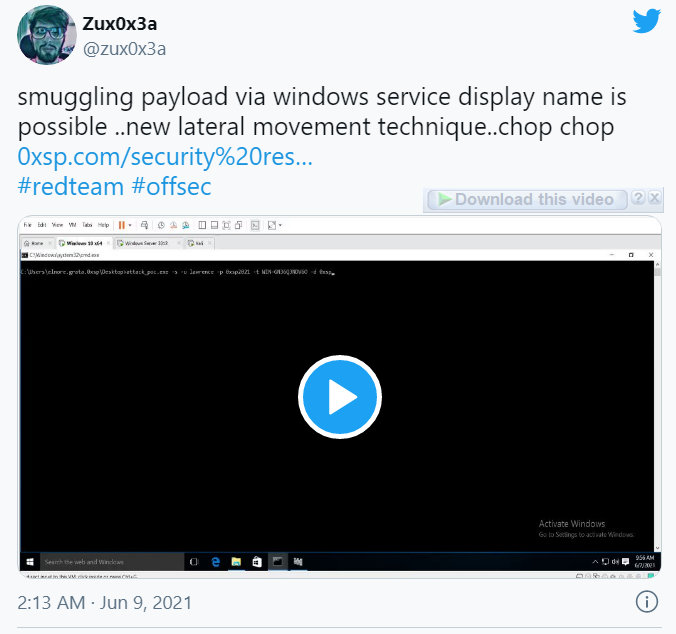 zux0x3a/tchopper
conduct lateral movement attack by leveraging unfiltered services display name to smuggle binaries as chunks into the target machine