
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
588 results
CVE-2024-51665 preview

CVE-2024-51665

GitHubrandomrobbiebf/cve-2024-51665

Magical Addons For Elementor <= 1.2.1 - Authenticated (Subscriber+) Server-Side Request Forgery

api-security-testingexploitationinformation-gathering+3
1
1 year ago
CVE-2018-7691 preview

CVE-2018-7691

GitHubalt3kx/cve-2018-7691

The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10
api-security-testingexploitationinformation-gathering+3
14 years ago
CVE-2018-7690 preview

CVE-2018-7690

GitHubalt3kx/cve-2018-7690

The SSC REST API contains Insecure Direct Object Reference (IDOR) vulnerabilities in Fortify Software Security Center (SSC) 17.10, 17.20 & 18.10

api-security-testingexploitationinformation-gathering+3
14 years ago
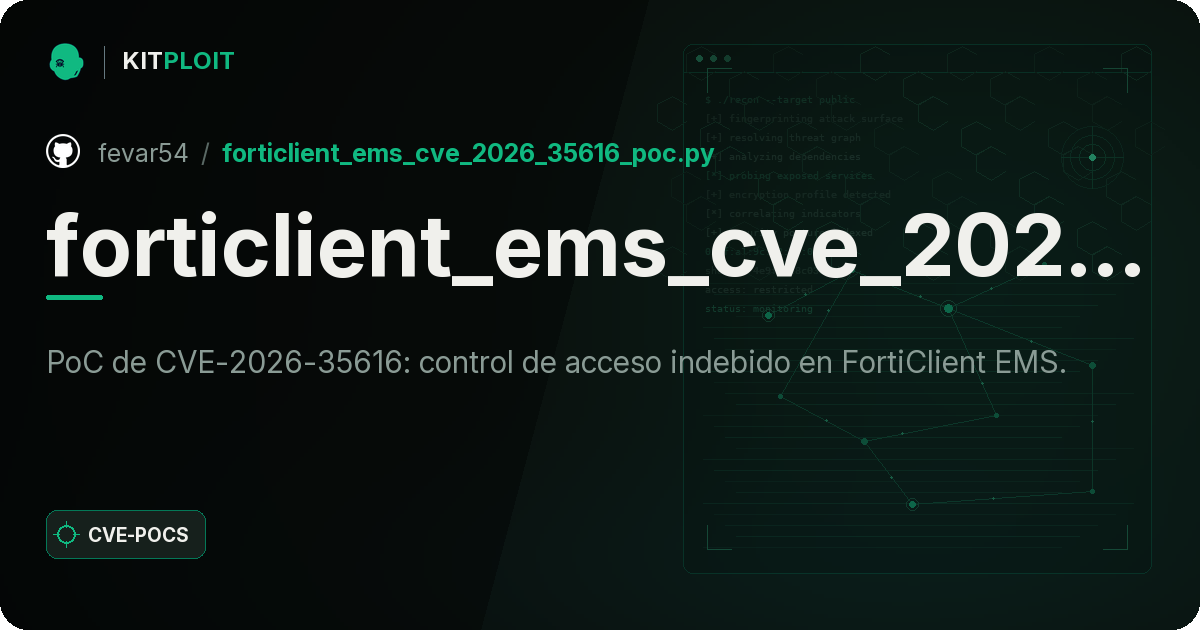
wp2shell-lab preview

wp2shell-lab

GitHubananay/wp2shell-lab

Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
api-security-testingcode-analysiseducation+3
2 months ago
forticlient_ems_cve_2026_35616_poc.py preview

forticlient_ems_cve_2026_35616_poc.py

GitHubfevar54/forticlient_ems_cve_2026_35616_poc.py

PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
api-security-testingexploitationpenetration-testing+2
5 months ago
URL_CHECKER preview

URL_CHECKER

GitHubmannansainicyber/url_checker

Hybrid ML and heuristic-based URL phishing detector with real-time analysis, explainable confidence scores, and REST API for programmatic security…
api-security-testingeducationmachine-learning+3
16 months ago
CVE-2026-26012 preview

CVE-2026-26012

GitHubdiegobaelen/cve-2026-26012

Proof-of-concept exploit for CVE-2026-26012, demonstrating an authenticated organization collection permissions bypass and cipher enumeration in…

api-security-testingexploitationinformation-gathering+3
7 months ago
r2s preview

r2s

GitHubmxm0z/r2s

A web-based vulnerability scanner for CVE-2025-55182, a critical Remote Code Execution (RCE) vulnerability in React Server Components.

api-security-testingcloud-securityexploitation+3
9 months ago
CVE-2025-61148 preview

CVE-2025-61148

GitHubsharma19d/cve-2025-61148

The vulnerability exists in the Student Payment API. The application fails to properly validate whether the user requesting a receipt is authorized…
api-security-testingeducationinformation-gathering+3
9 months ago
CVE-2026-30944-PoC preview

CVE-2026-30944-PoC

GitHubfilipegaudard/cve-2026-30944-poc

Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.

api-security-testingexploitationpenetration-testing+4
6 months ago
CVE-2025-11771 preview

CVE-2025-11771

GitHubjfriedli/cve-2025-11771

Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…

api-security-testingexploitationpenetration-testing+2
6 months ago
CVE-2025-12720 preview

CVE-2025-12720

GitHubd0n601/cve-2025-12720

g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
api-security-testingauthenticationexploitation+3
10 months ago
CVE-2026-24134-PoC preview

CVE-2026-24134-PoC

GitHubfilipegaudard/cve-2026-24134-poc

Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…

api-security-testingeducationexploitation+3
8 months ago
CVE-2025-6783 preview

CVE-2025-6783

GitHubjfriedli/cve-2025-6783

Proof-of-concept exploit for CVE-2025-6783 demonstrating SQL injection via crafted HTTP headers and JSON payload against WordPress GoZen Forms REST…
api-security-testingexploitationpenetration-testing+2
6 months ago
CVE-2025-6792 preview

CVE-2025-6792

GitHubjfriedli/cve-2025-6792

Proof-of-concept exploit for CVE-2025-6792 demonstrating unauthorized Pusher channel subscription and event eavesdropping in a WordPress plugin via…
api-security-testingexploitationinformation-gathering+3
6 months ago
CVE-2023-45857-Demo preview

CVE-2023-45857-Demo

GitHubfuyuooumi1027/cve-2023-45857-demo

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…

api-security-testingctfeducation+3
12 years ago
cve-2025-55182 preview

cve-2025-55182

GitHubprestonhashworth/cve-2025-55182

CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
api-security-testingexploitationpenetration-testing+3
9 months ago
CVE-2021-4191_Exploits preview

CVE-2021-4191_Exploits

GitHubadelittle/cve-2021-4191_exploits

Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.

api-security-testingexploitationinformation-gathering+3
3 years ago
Previous1…293031…33Next