
RedTeamToolkit
 owasp/redteamtoolkit
The WASM Based Security Toolkit for the Web First Paradigm
exploit-frameworksinformation-gatheringpenetration-testing-frameworks+3
37
owasp/redteamtoolkitThe WASM Based Security Toolkit for the Web First Paradigm
 juice-shop/juice-shop
Intentionally vulnerable web application covering OWASP Top 10 vulnerabilities for security training, CTF competitions, and penetration testing…
 owasp/wstg
The Web Security Testing Guide is a comprehensive Open Source guide to testing the security of web applications and web services.
 microsoft/agent-governance-toolkit
Policy enforcement, zero-trust identity, execution sandboxing, and audit logging for autonomous AI agents. Covers 10/10 OWASP Agentic Top 10 with…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 owasp/wrongsecrets
Vulnerable app with examples showing how to not use secrets
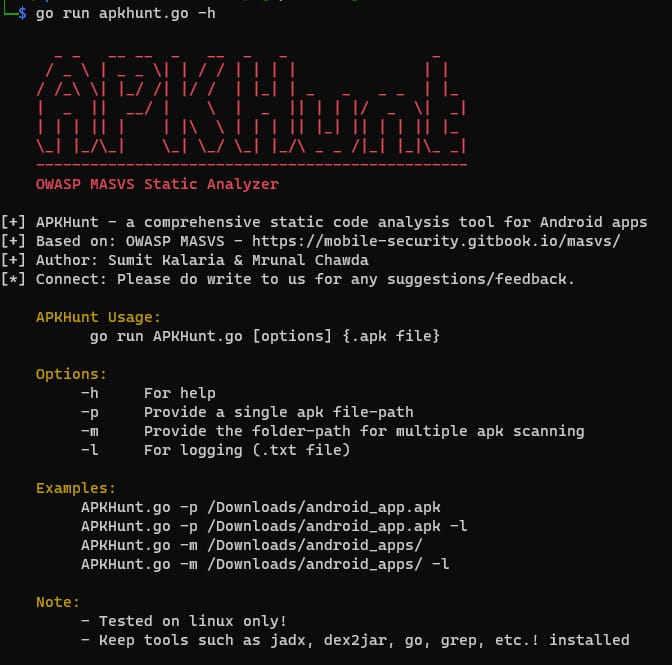 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 microcosm-cc/bluemonday
bluemonday: a fast golang HTML sanitizer (inspired by the OWASP Java HTML Sanitizer) to scrub user generated content of XSS
 roottusk/vapi
vAPI is Vulnerable Adversely Programmed Interface which is Self-Hostable API that mimics OWASP API Top 10 scenarios through Exercises.
 owasp/securecodingdojo
The Secure Coding Dojo is a platform for delivering secure coding knowledge.
 securityrat/securityrat
OWASP SecurityRAT (version 1.x) - Tool for handling security requirements in development
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
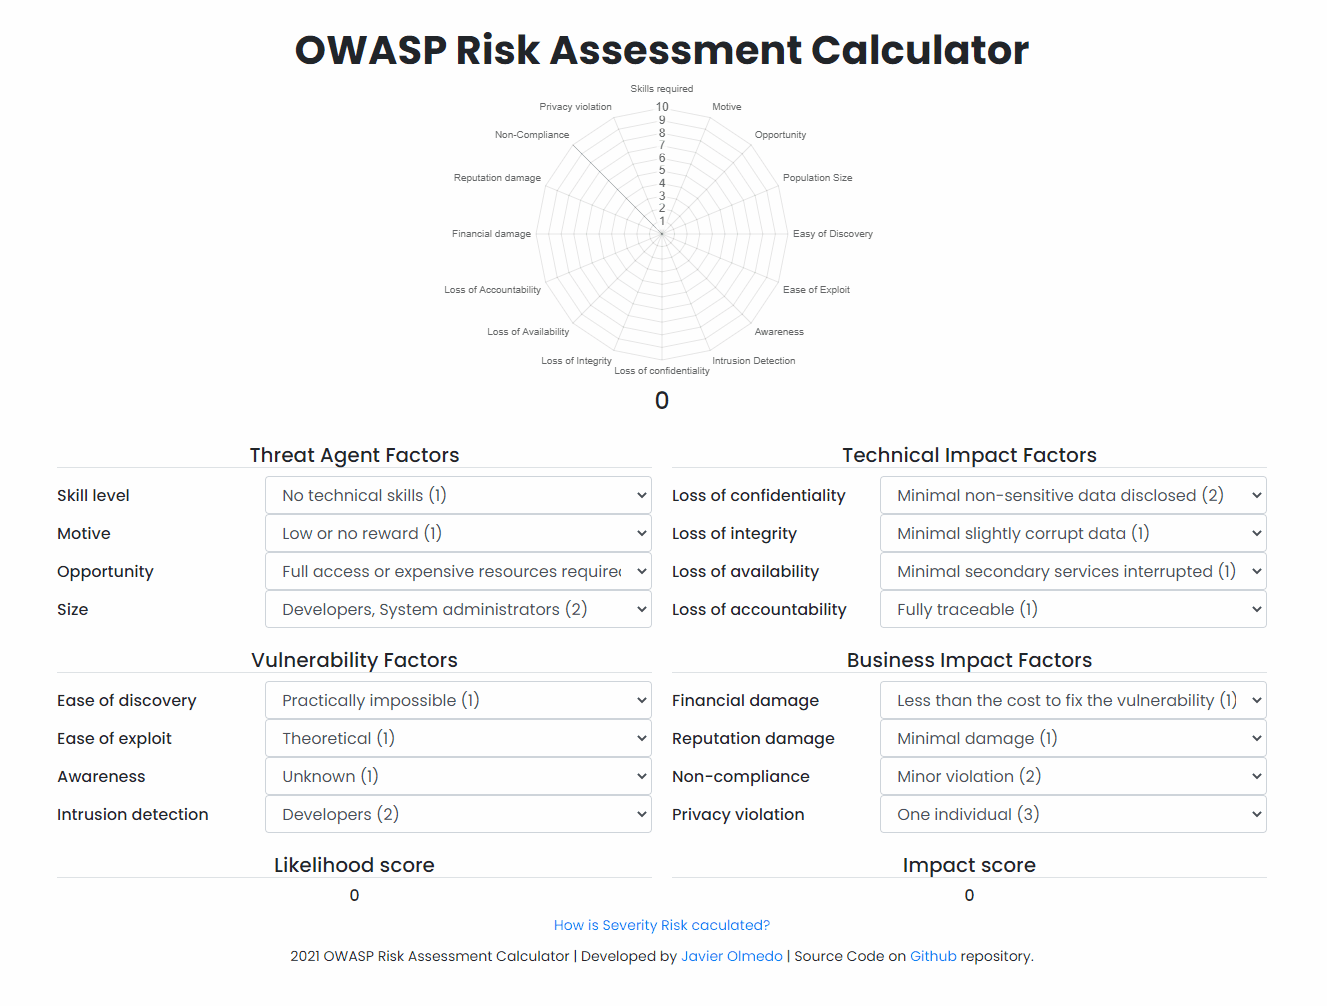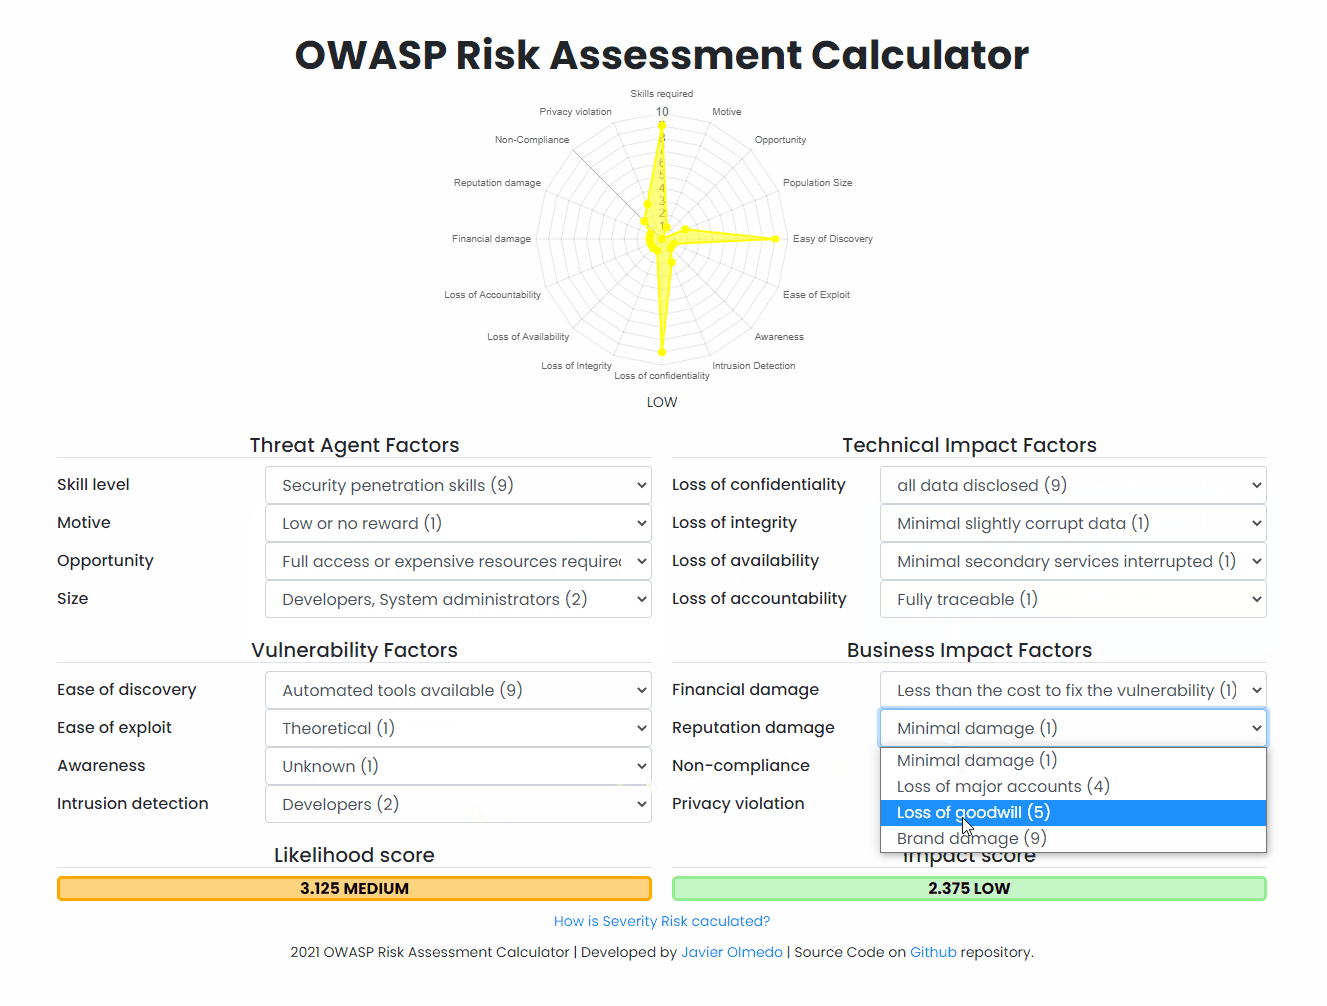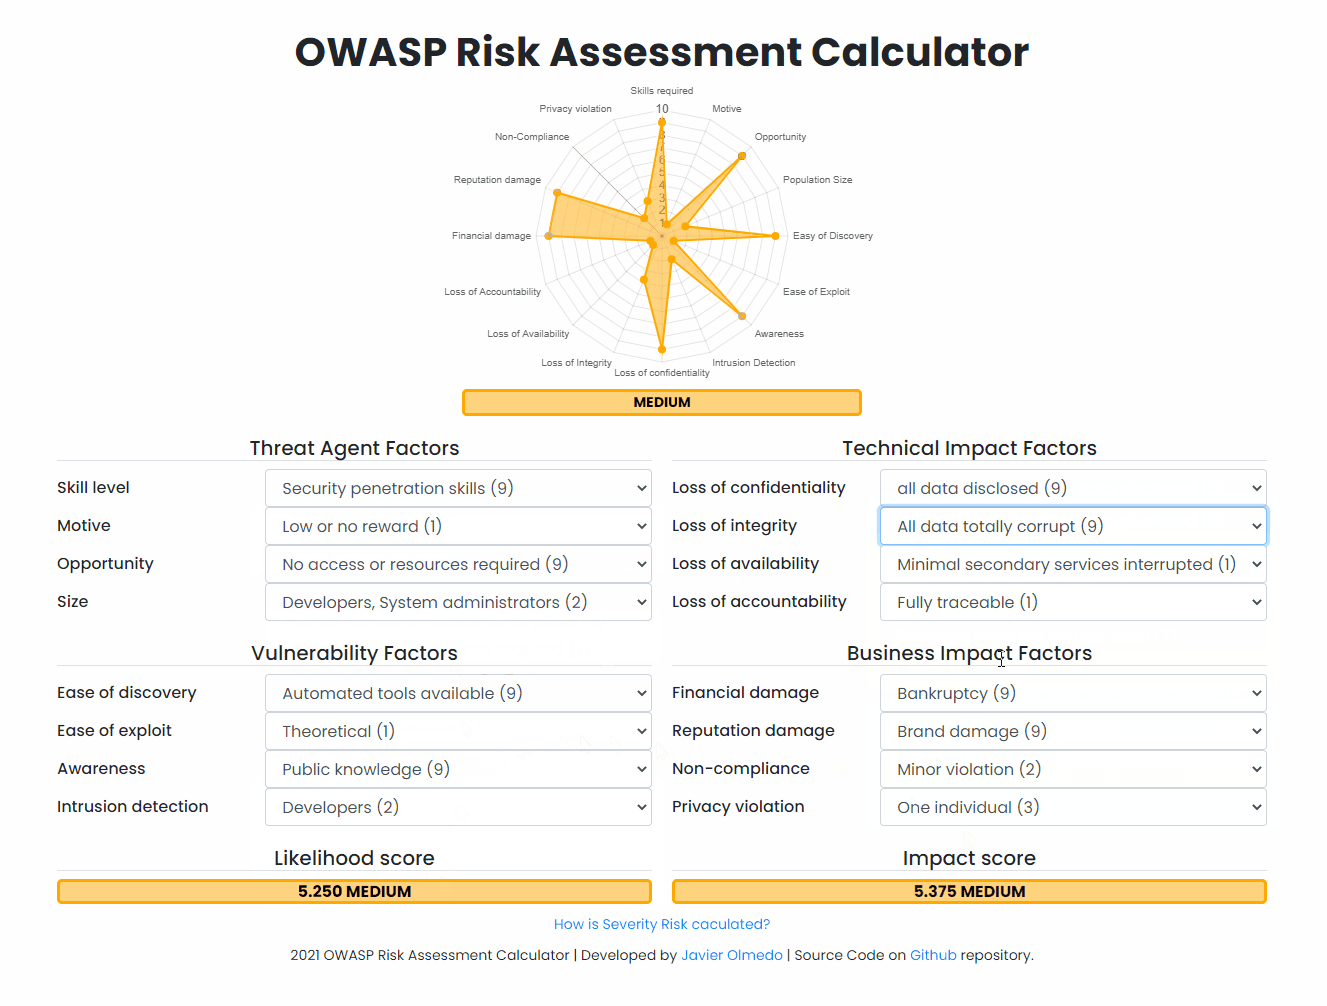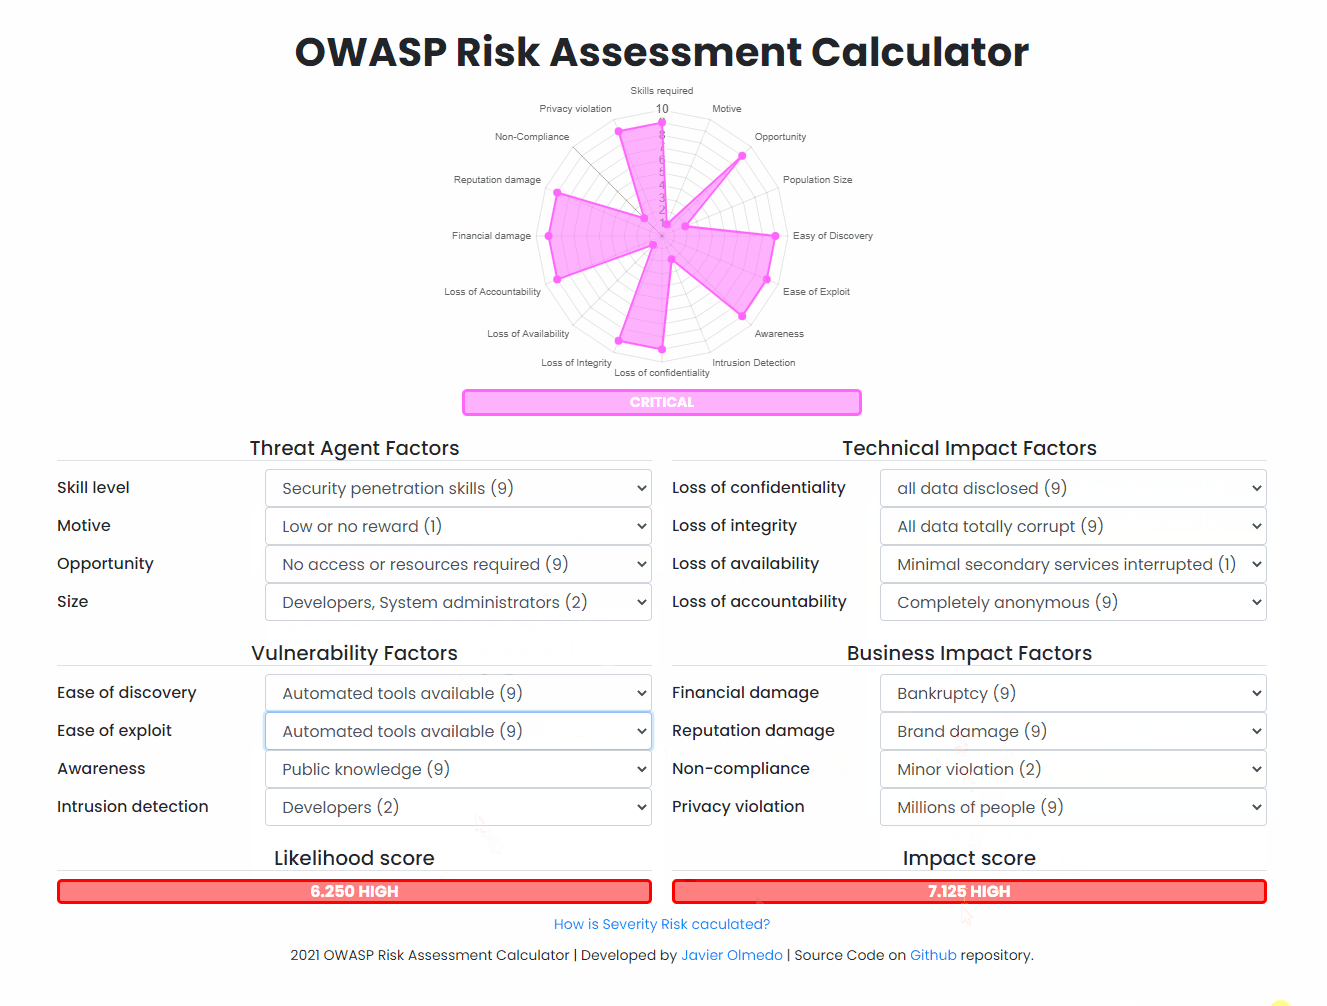 javierolmedo/owasp-calculator
🧮 An online calculator to assess the risk of web vulnerabilities based on OWASP Risk Assessment
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.