
teletunnel
 mhdgning131/teletunnel
Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
command-and-controldata-exfiltrationids-ips-evasion+7
45
mhdgning131/teletunnelBypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
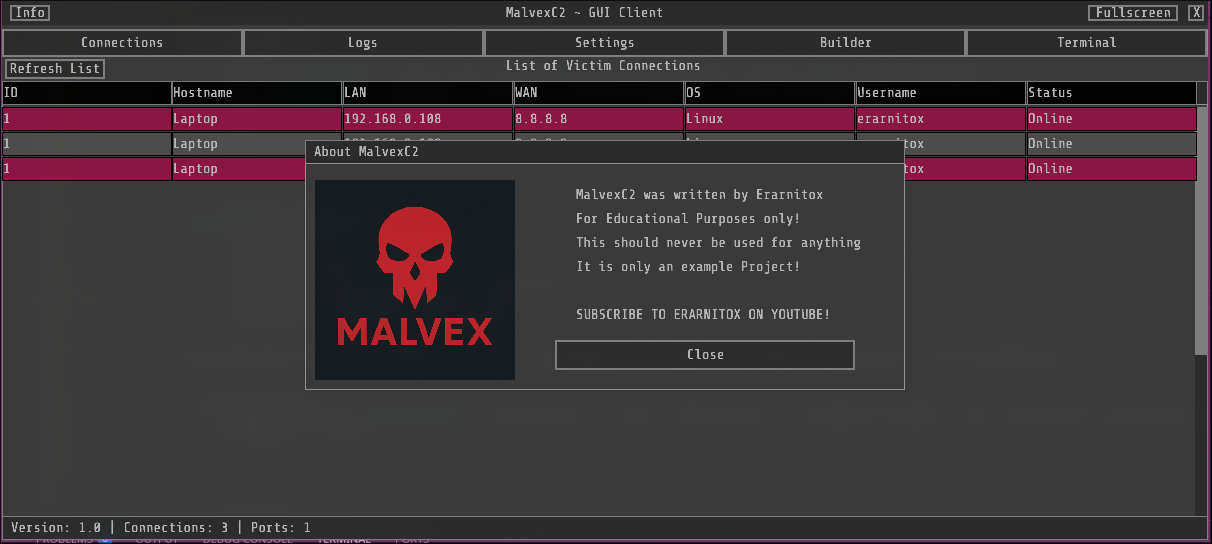 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 melardev/xeytanwin32-rat
WORK IN PROGRESS. RAT written in C++ using Win32 API
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
 artbitrage/stealth-kid-rat
Stealth Kid RAT (SKR) is an open-source multi-platform Remote Access Trojan (RAT) written in C#. Released under MIT license. The SKR project is fully…
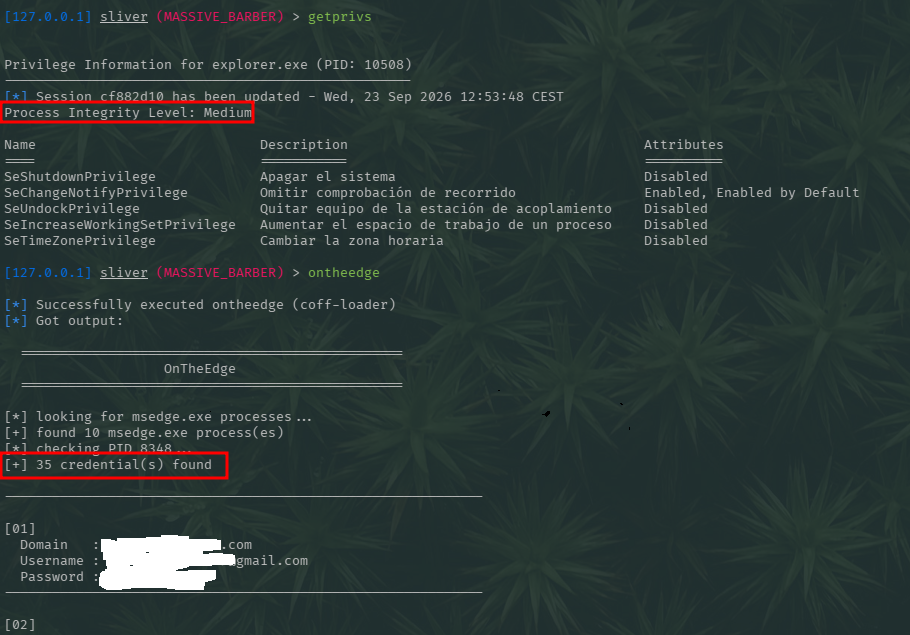 jssngc/ontheedge
Windows research PoC in C that scans Microsoft Edge process memory for credential-related data, with a standalone executable and a BOF variant for C2…
 stuub/cve-2024-29895-cactirce-poc
CVE-2024-29895 PoC - Exploiting remote command execution in Cacti servers using the 1.3.X DEV branch builds
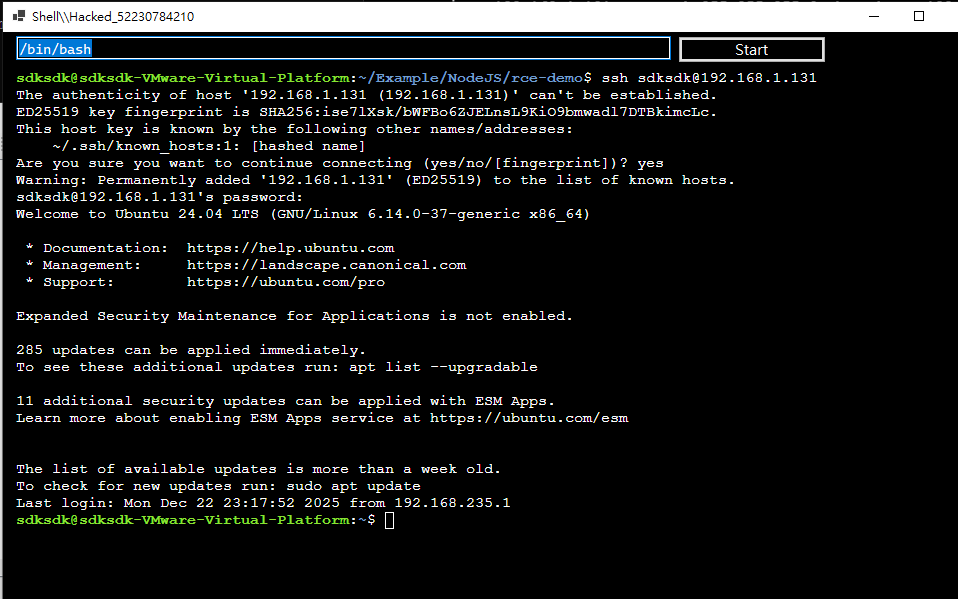 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
 lorddemon/drupalgeddon2
Remote code execution exploit for Drupal CVE-2018-7600 (Drupalgeddon2) with command injection via HTTP requests.
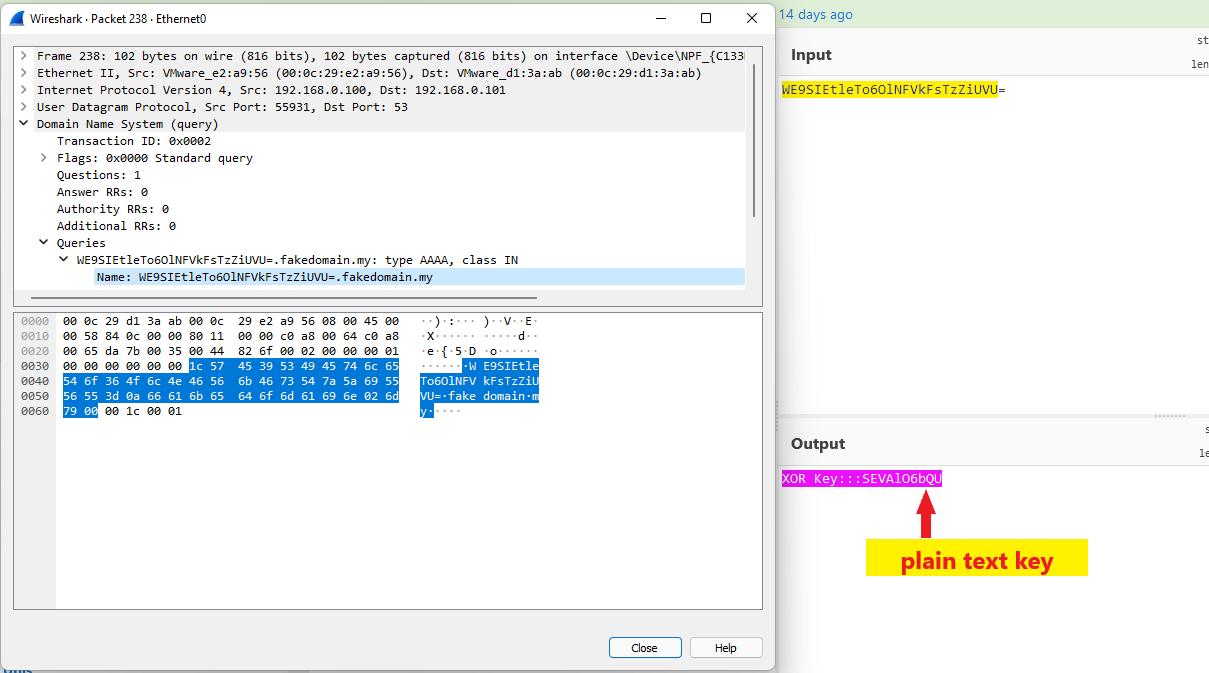 aniqfakhrul/sharpdnsexfil
C# tool for exfiltrating files over DNS using XOR and asymmetric encryption, designed for red team engagements with restricted outbound connections.
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
 qurtidev/wsus-cve-2025-59287-rce
Exploit script written in C# to aid gaining a reverse shell on targets with Windows Server Update Service(WSUS) CVE-2025-59287.
 cai-niao98/cve-2022-26134
Exploit for CVE-2022-26134 targeting Confluence Server with remote command execution and reverse shell capabilities. Supports batch scanning and…
 whokilleddb/cve-2019-15107
CVE-2019-15107 Webmin Exploit in C
 exploitwritter/cve-2022-29337
C-DATA FD702XW-X-R430 v2.1.13_X001 was discovered to contain a command injection vulnerability via the va_cmd parameter in formlanipv6. This…
 nikopmpm/fsociety-cve-2024-0670-checkmk-lpe
🔍 Exploit CVE-2024-0670 in CheckMK agents for local privilege escalation using a robust C++ tool designed for security professionals.
 netomize/http-basma
In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…
 jeffli1024/log4j-rce-test
Quick test environment for CVE-2021-44228 Log4j RCE vulnerability with a built-in exploit server and customizable payload execution.