

CVE-2019-11043
 fairyming/cve-2019-11043
Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
exploitationpayload-developmentpenetration-testing+2
1
fairyming/cve-2019-11043Proof-of-concept exploit for CVE-2019-11043, a PHP-FPM underflow vulnerability, built on the pocsuite framework for automated web application…
 vutiendat323/int14107_cve-2021-35042
Django-based CTF blog platform with integrated CVE-2021-35042 exploit tool for learning web application security and vulnerability exploitation.
 owasp/mimosa
Open-source web application security challenge platform with auto-approved registration, SQL dump generation, and Docker deployment for hands-on…
 shoucheng3/vert-x3__vertx-web_cve-2019-17640_3-9-3
Analysis and exploitation code for CVE-2019-17640, a vulnerability in Vert.x-Web. Provides a targeted test case for security researchers validating…
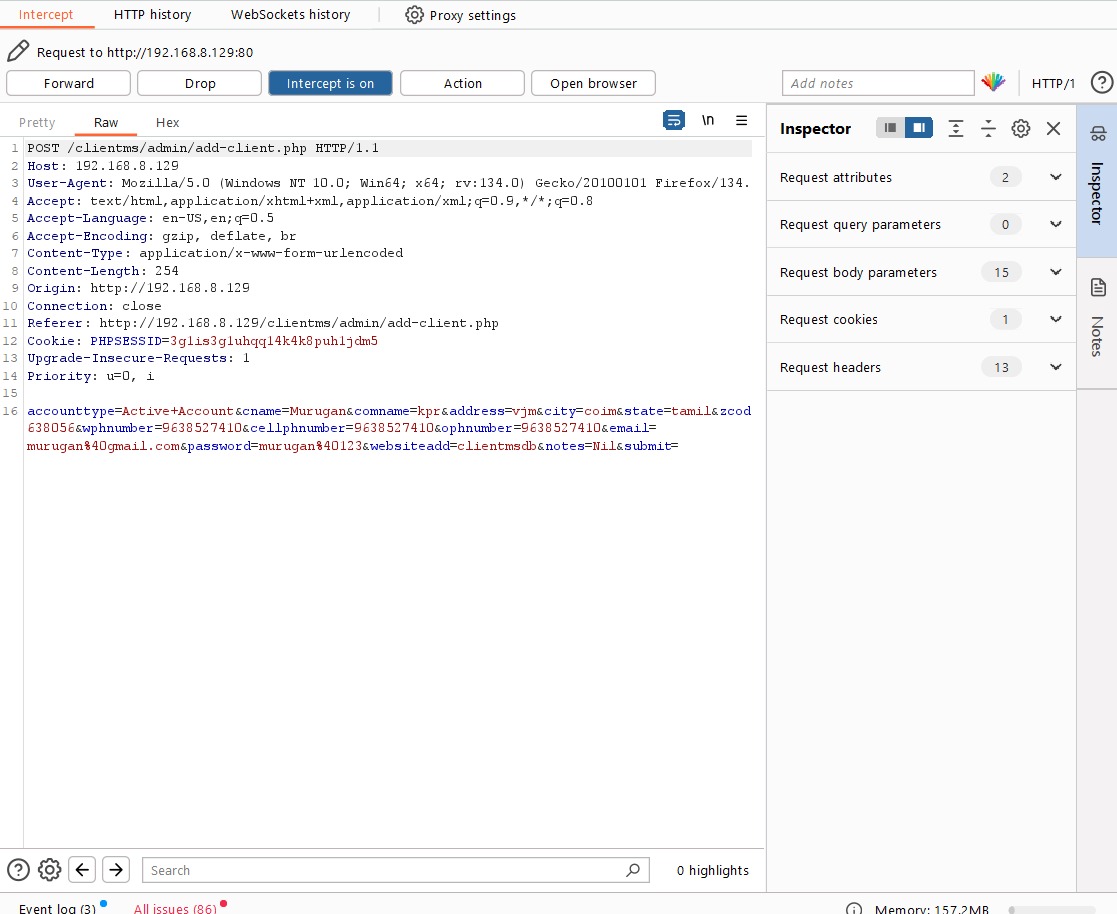 moulish2004/cve-2025-44603-csrf-leads_to_create_fakeusers
Proof-of-concept demonstrating a CSRF vulnerability in a PHP-based Client Management System, with HTML exploit code and mitigation strategies for web…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…
 costacoco/adiscon
SQL injection exploit for Adiscon LogAnalyzer v4.1.13 and earlier (CVE-2023-34600). Provides proof-of-concept code for testing web application…
 shoucheng3/apache__jspwiki_cve-2022-46907_2-11-3
Exploit module for Apache JSPWiki CVE-2022-46907, targeting a Java-based wiki platform with JAAS security integration. Provides vulnerability…
 huyvo2910/cve-2525-25748-cross-site-request-forgery-csrf-vulnerability-in-hoteldruid-3.0.7
Detailed CVE-2025-25748 proof-of-concept and analysis of a CSRF vulnerability in HotelDruid 3.0.7, including exploitation flow, impact assessment,…
 h3x0v3rl0rd/xss-payload-list
Curated collection of XSS payload vectors for web application security testing, covering various contexts and bypass techniques.
 arachni/arachni
Web Application Security Scanner Framework
 fportantier/vulpy
Vulnerable Python Application To Learn Secure Development
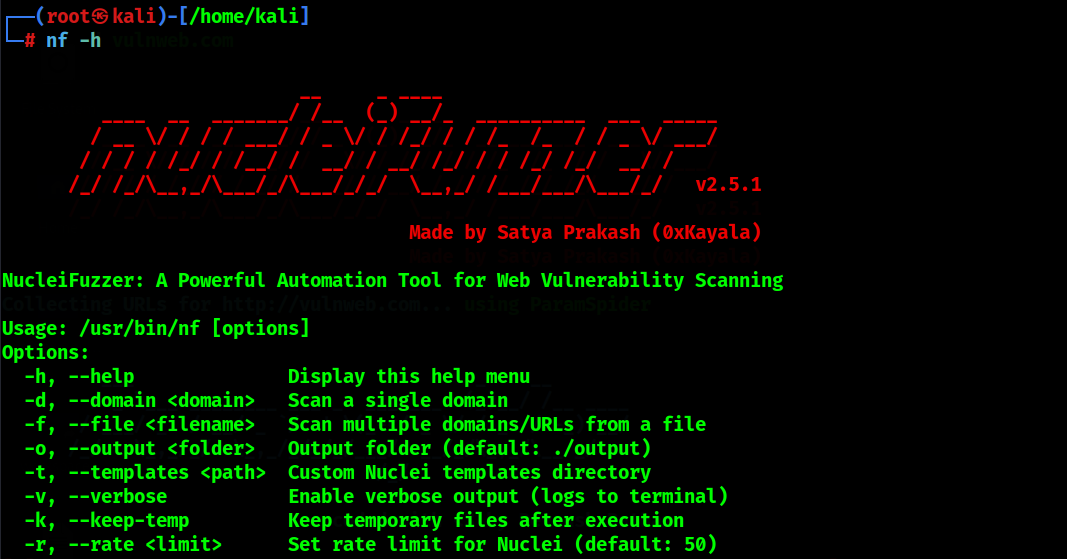 0xkayala/nucleifuzzer
Automated web vulnerability scanner combining URL discovery tools (ParamSpider, waybackurls, gauplus, hakrawler, katana) with Nuclei fuzzing…
 ransomleak/training-application-security
Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…

 delvelabs/tachyon
Fast http dead file finder.
 syn-4ck/wvctf
WVCTF or WebVulnCTF is a gamified web platform which promotes training in pentesting and web application development security in an entertaining way.…
 mbrandner-group/juiceshopgl
Intentionally vulnerable web application for security training, CTF competitions, and testing security tools. Covers OWASP Top Ten vulnerabilities…