
log4j2-exploit
 spasam/log4j2-exploit
log4j2 Log4Shell CVE-2021-44228 proof of concept
educationexploitationpayload-development+3
spasam/log4j2-exploitlog4j2 Log4Shell CVE-2021-44228 proof of concept
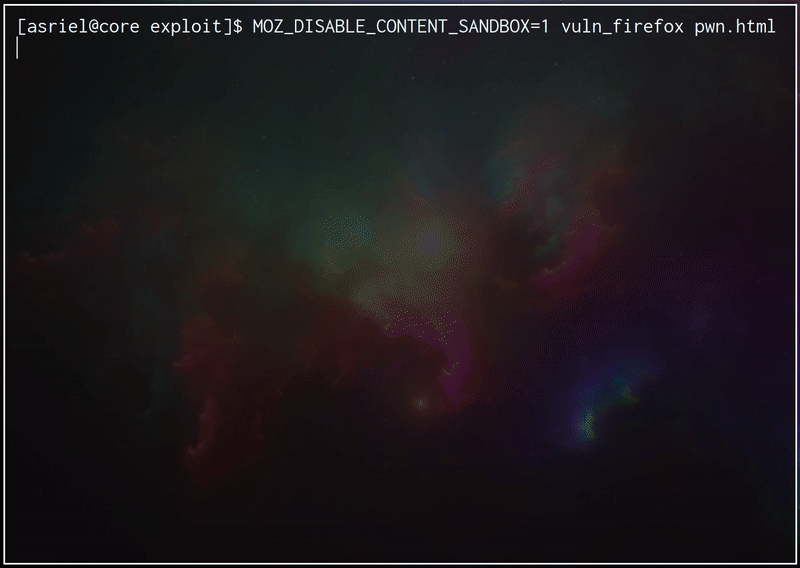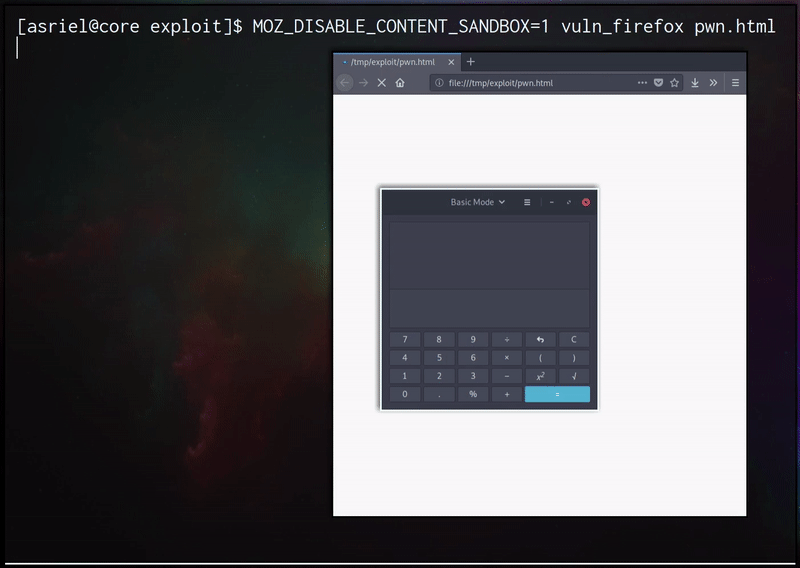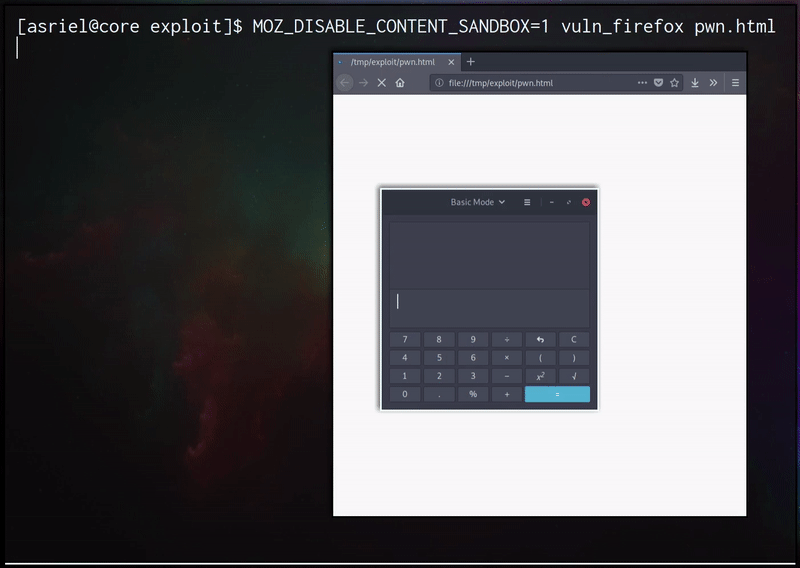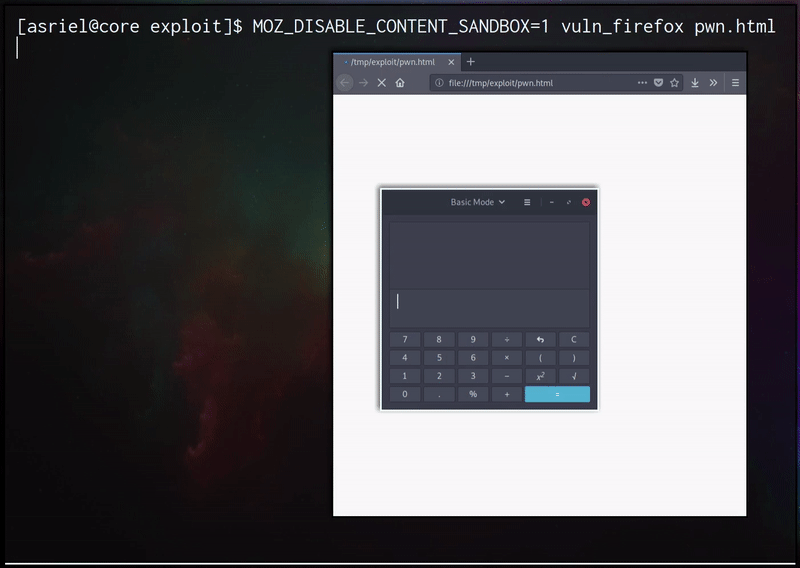 hydra3evil/cve-2018-12386
CVE-2018-12386 - Firefox Sandboxed RCE Exploit for Linux (Firefox <v62.0.3)
 ggolawski/struts-rce
Apache Struts CVE-2017-5638 RCE exploitation
 kamal-418/vulnerable-lab-nextjs-cve-2025-29927
Deliberately vulnerable Next.js application designed for practicing exploitation of CVE-2025-29927, with a tutorial video for guided learning.
 kovachvl/cve-2026-55168
Proof-of-concept exploit for CVE-2026-55168 demonstrating authenticated arbitrary file write via symlink planting during backup restore in Runtipi.
 0xmrma/cve-2026-32722
Bloomberg Memray’s Stored XSS via Unescaped Command-Line Metadata
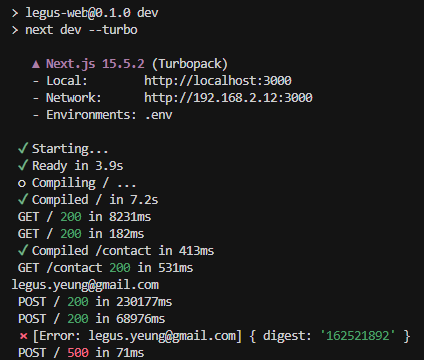 legus-yeung/cve-2025-55182-exploit
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes a Python script demonstrating…
 elamani-drawing/cve-2024-4367-poc-pdfjs
PoC (Proof of Concept) de la CVE-2024-4367 - Vulnérabilité RCE dans libwebp. Démonstration complète incluant : création de payloads, scénarios…
 tkomlodi/cve-2022-23305_poc
CVE-2022-23305 Log4J JDBCAppender SQl injection POC
 mn-io/log4j-spring-vuln-poc
POC for CVE-2021-44228 within Springboot
 ahmedshamsddin/cve-2025-55182
Python exploit for CVE-2025-55182 in React Server Components, injecting a shell into Next.js 16.0.6 applications. Includes a vulnerable app for…
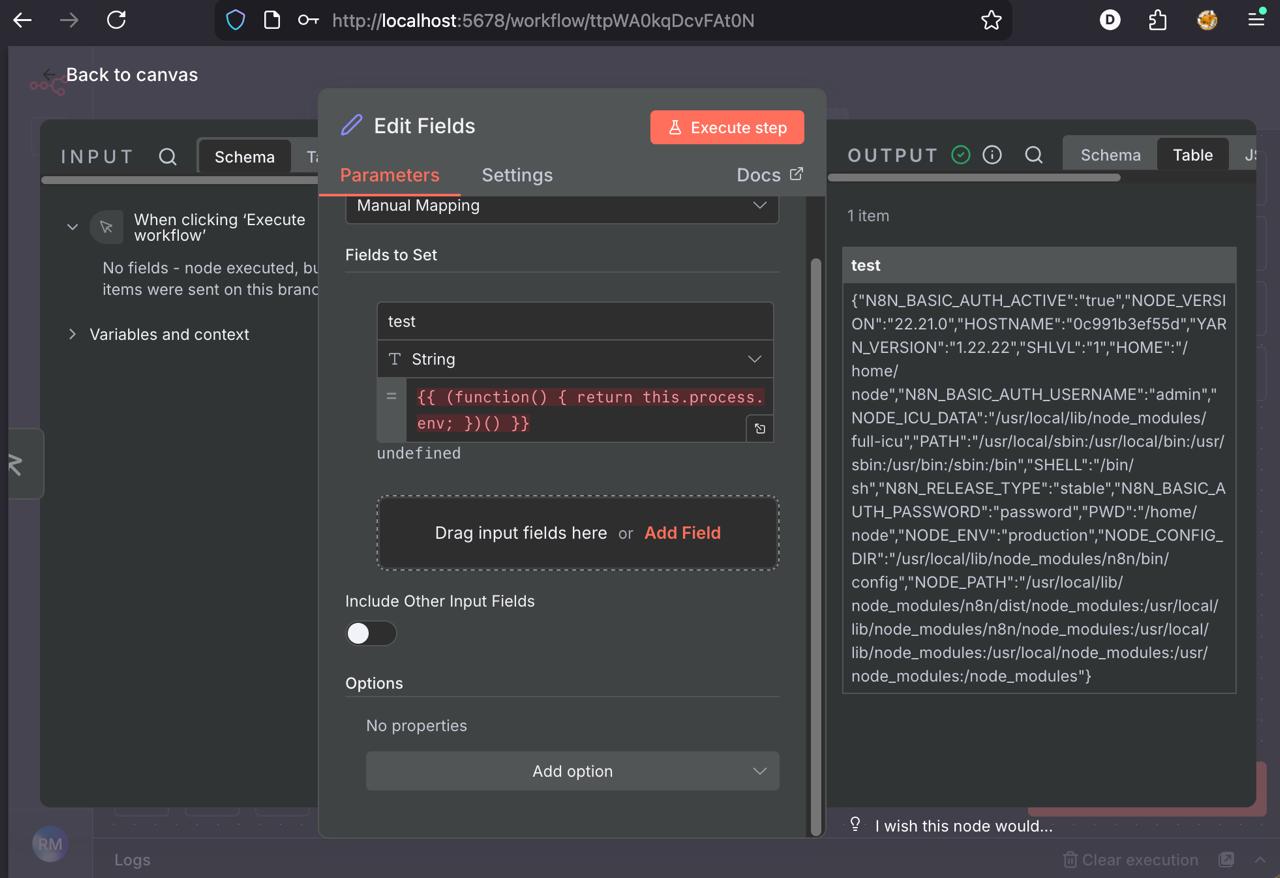 r4j3sh-com/cve-2025-68613-n8n-lab
Analysis of CVE-2025-68613
 mah4nzfr/cve-2021-41773
Bash POC script for RCE vulnerability in Apache 2.4.49
 qhxdr-dz/cve-2017-5638
Python-based proof-of-concept exploit for CVE-2017-5638, a remote code execution vulnerability in Apache Struts 2, enabling command injection against…
 del0x3/cve-2019-9053-port-py3
CVE-2019-9053.
 kanitan/log4j2-web-vulnerable
A vulnerable web app for log4j2 RCE(CVE-2021-44228) exploit test.
 urholaukkarinen/docker-log4shell
Dockerized Go app for testing the CVE-2021-44228 vulnerability
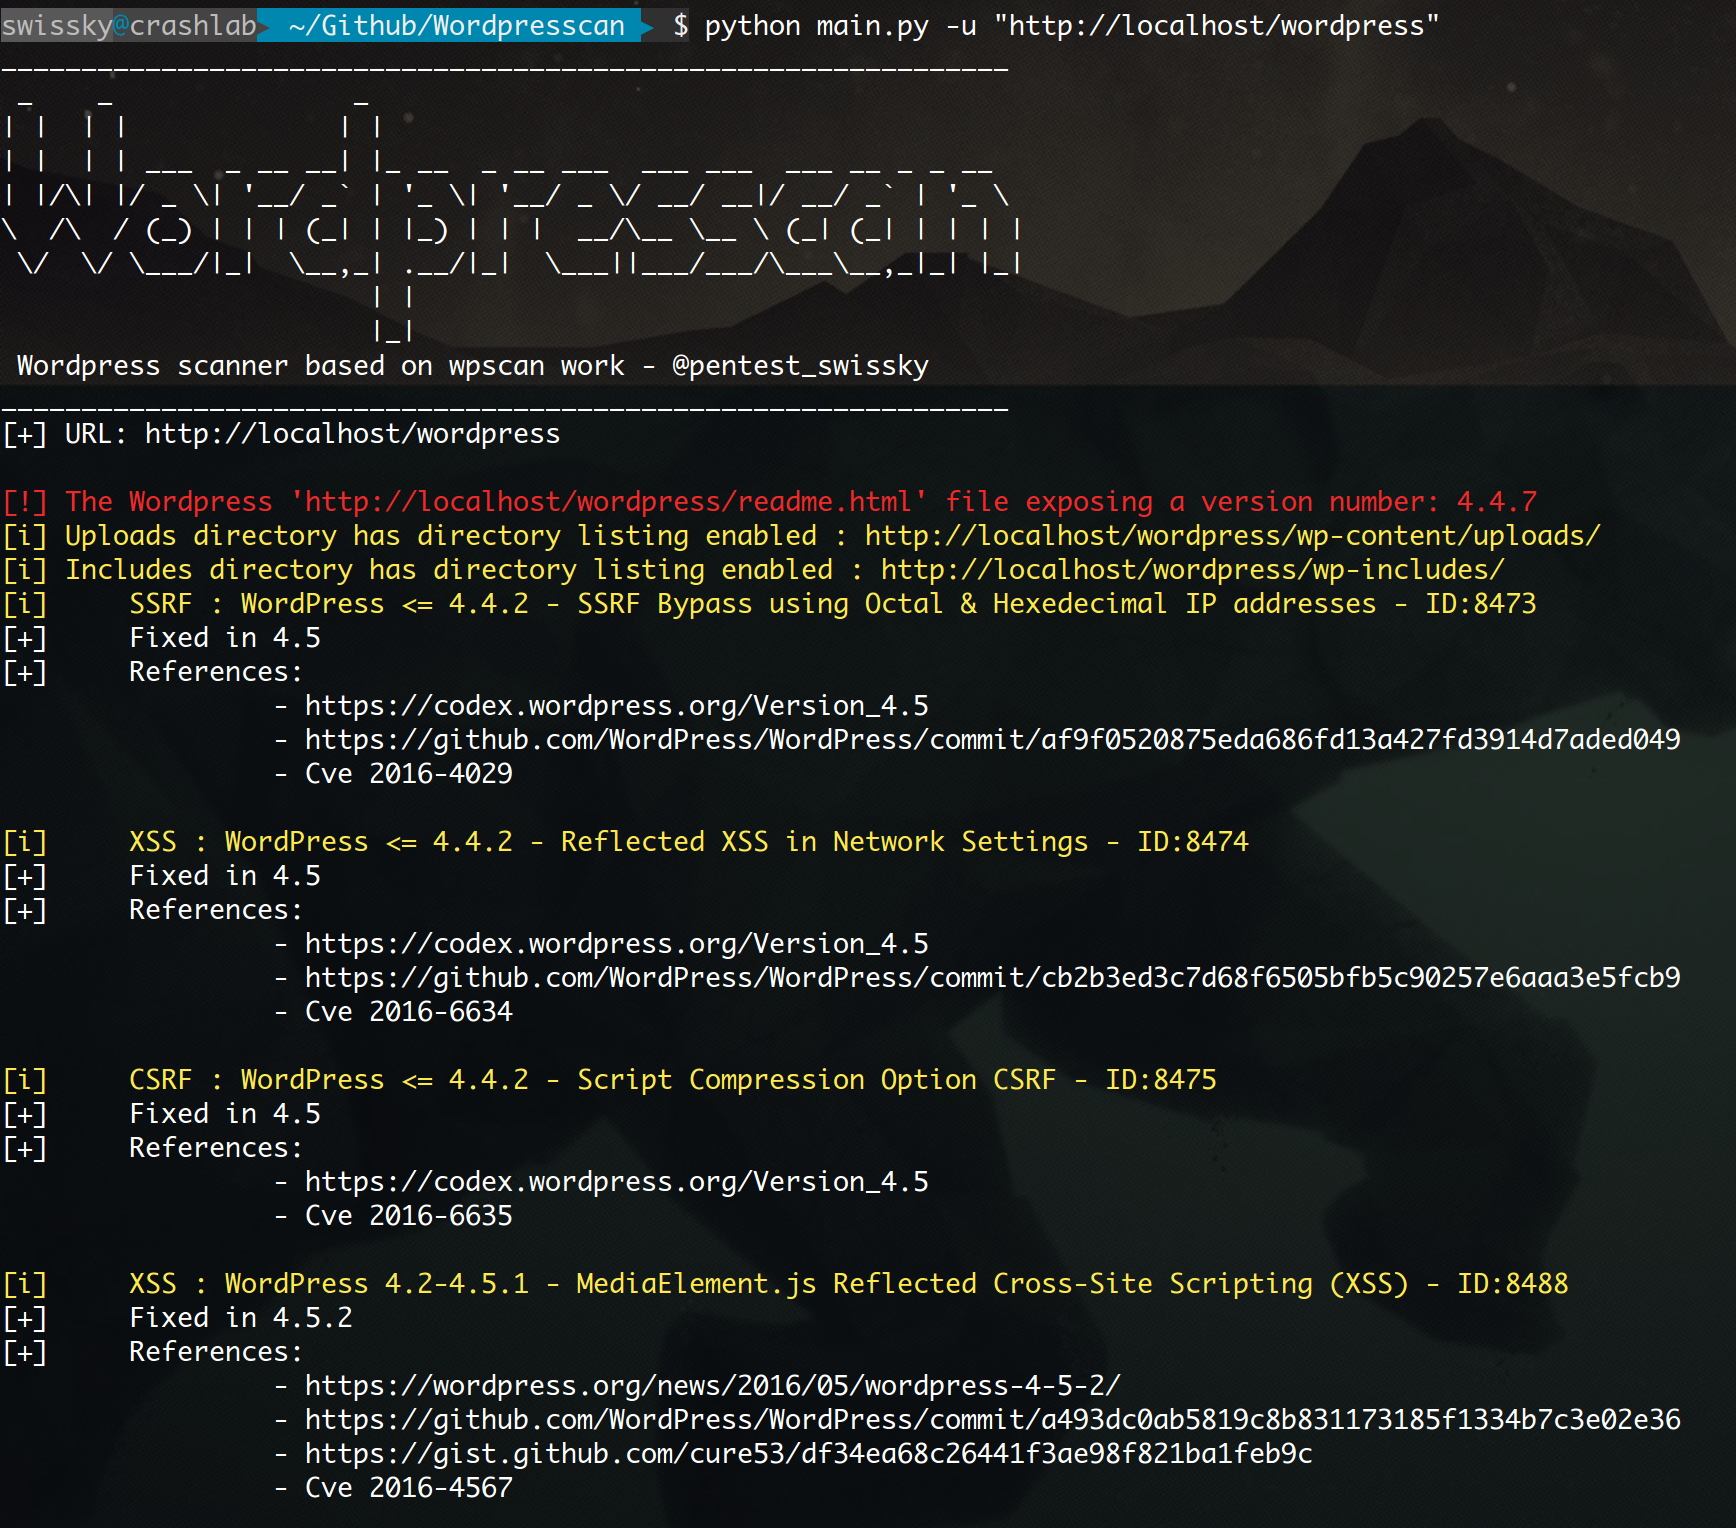 swisskyrepo/wordpresscan
WPScan rewritten in Python + some WPSeku ideas