Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
49 results
Ethical-Hacking-Tools preview

Ethical-Hacking-Tools

GitHubhhhrrrttt222111/ethical-hacking-tools

Complete Listing and Usage of Tools used for Ethical Hacking
cryptographyctfcurated-resources+6
2.2k
2 years ago
PacketSpy preview

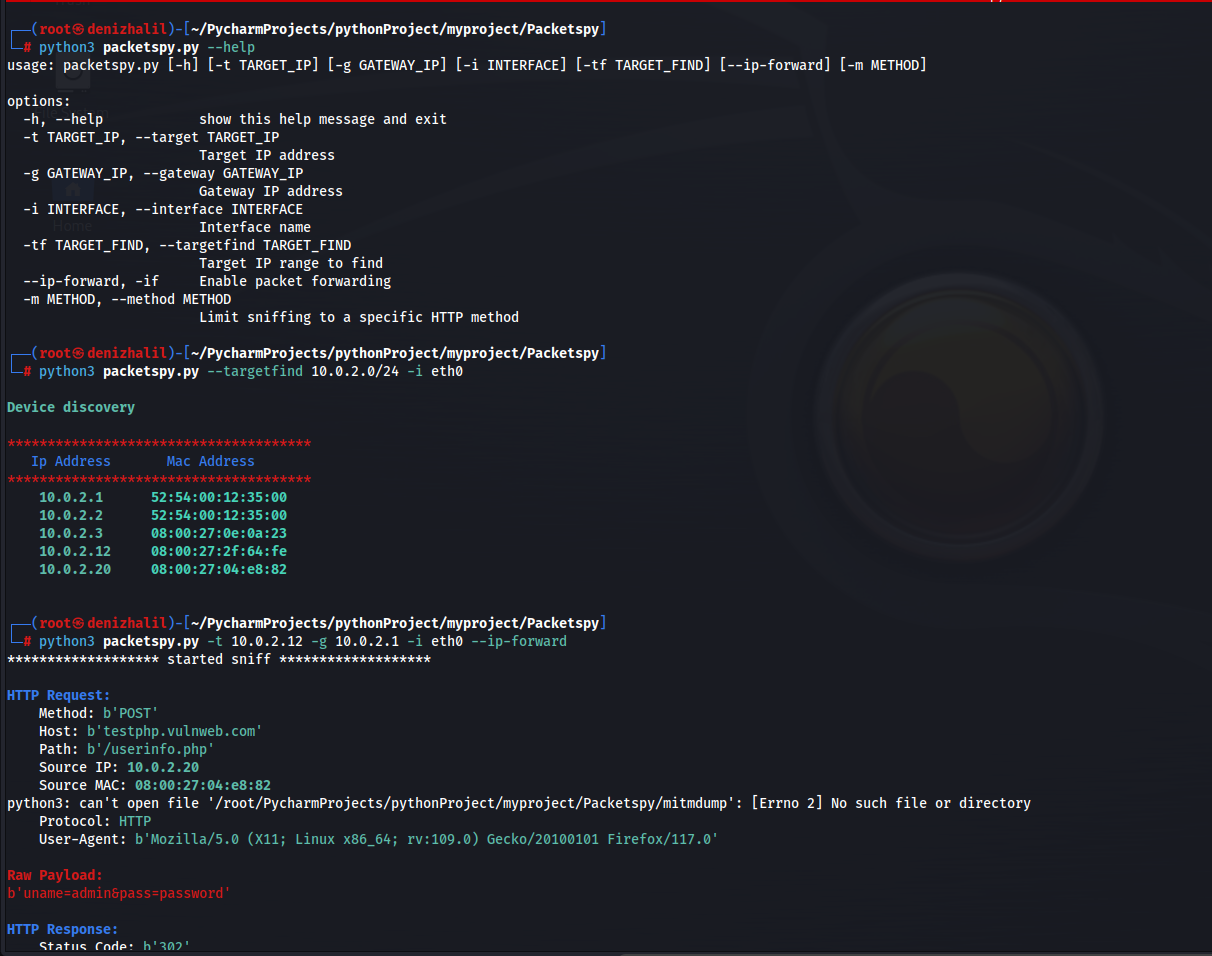
PacketSpy

GitHubhalildeniz/packetspy

Network packet sniffer for real-time traffic capture, HTTP inspection, raw payload analysis, and device discovery with built-in man-in-the-middle…
information-gatheringnetwork-securitypacket-sniffing-analysis
1592 years ago
TrafficWatch preview

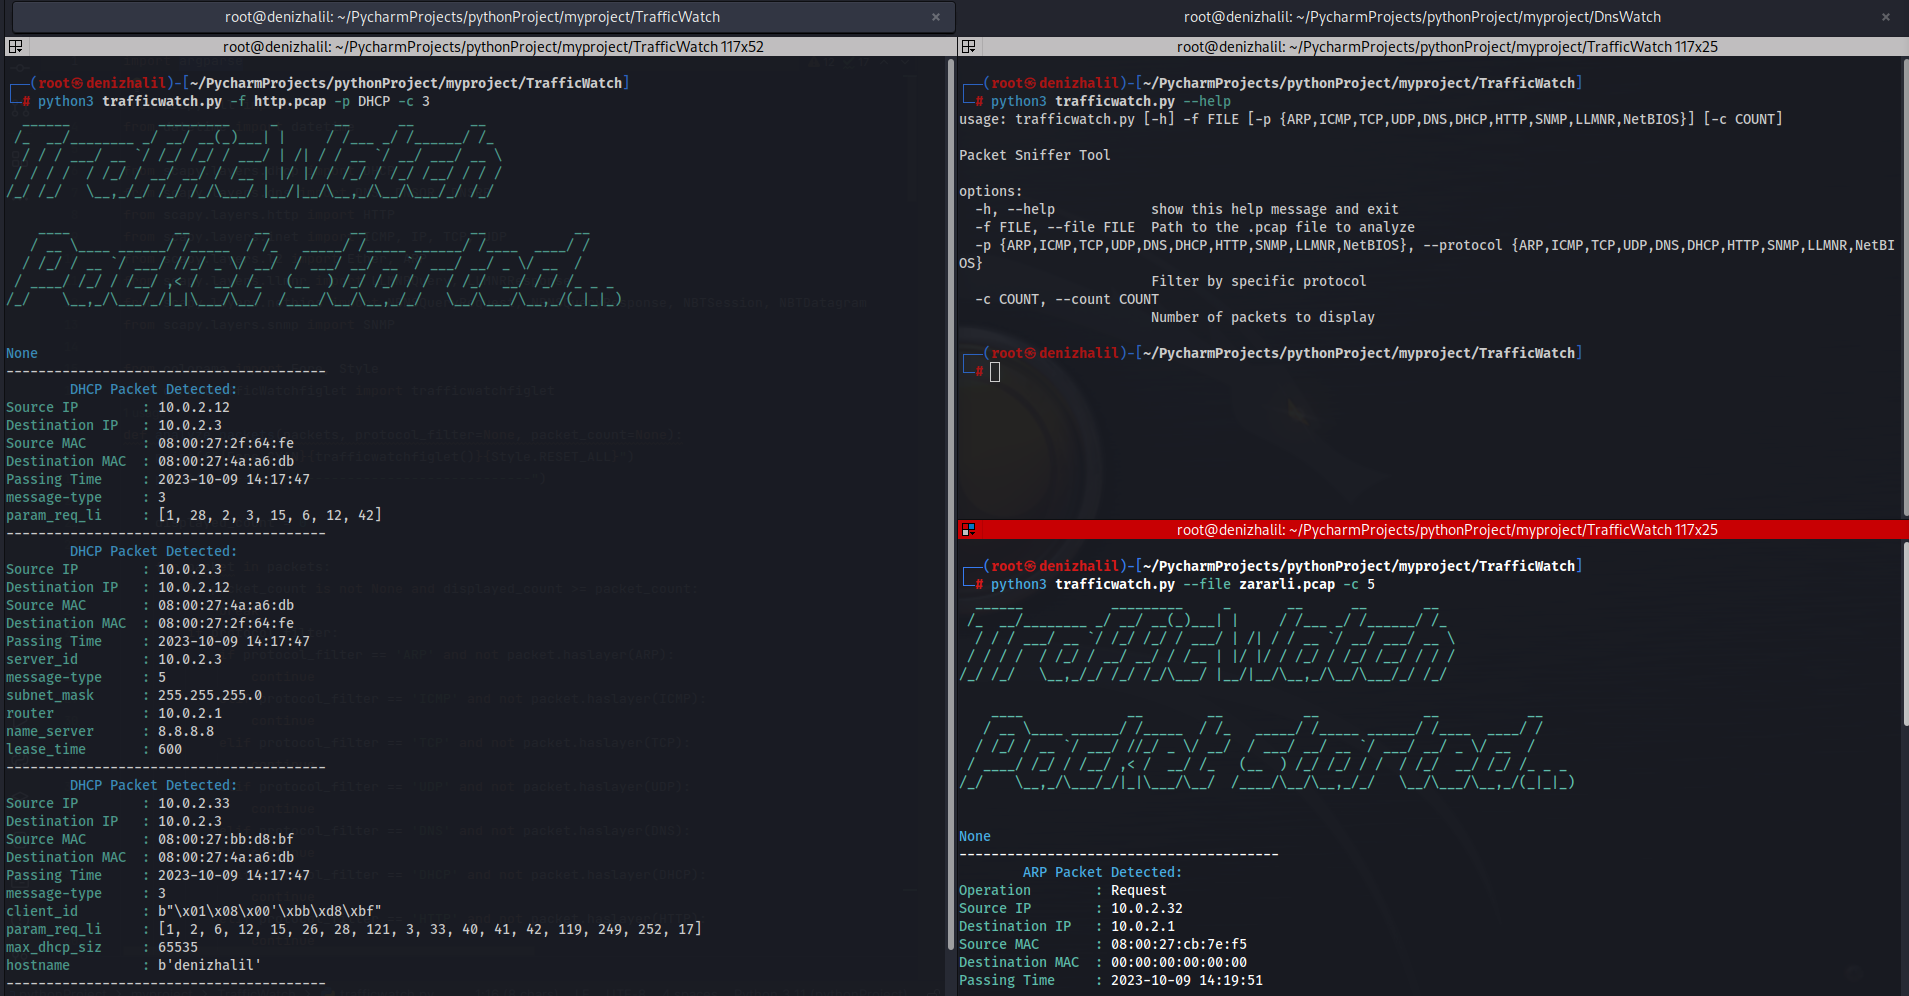
TrafficWatch

GitHubhalildeniz/trafficwatch

PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
information-gatheringnetwork-mappingnetwork-security+1
1362 years ago
Dosinator preview

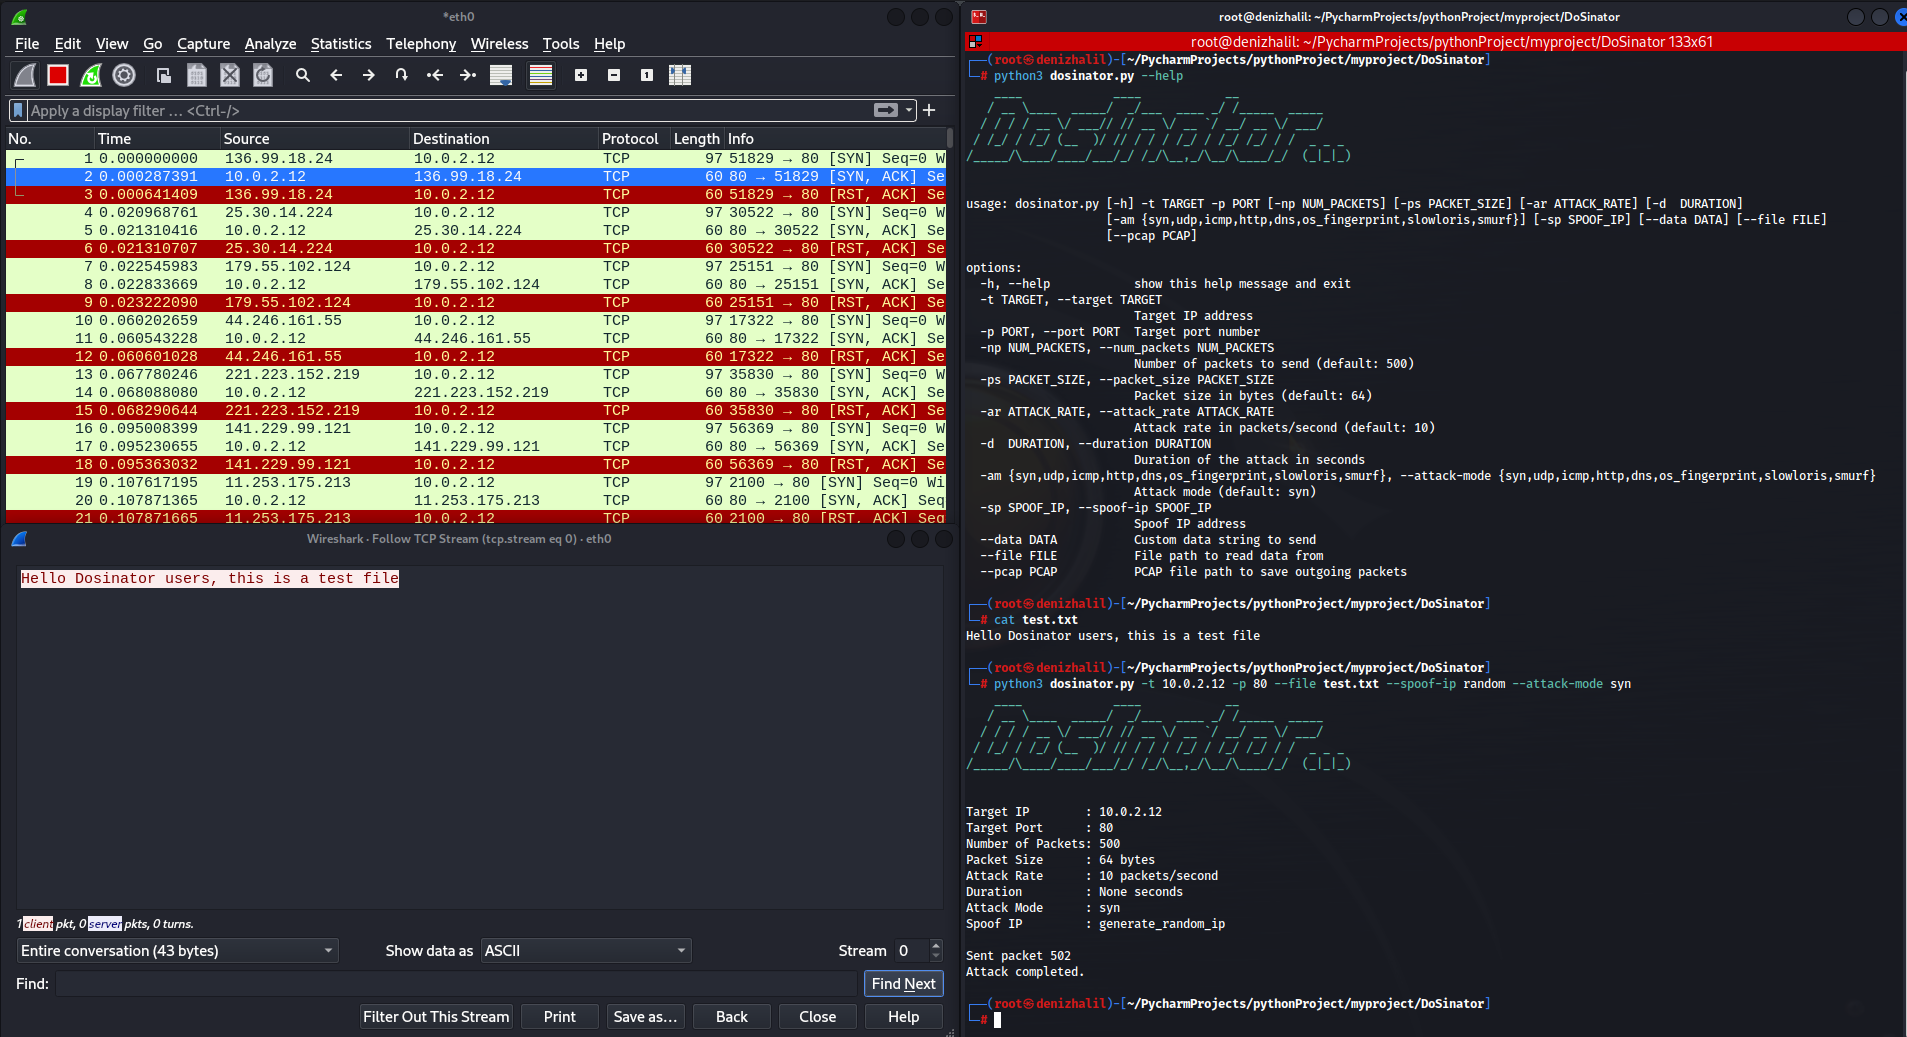
Dosinator

GitHubhalildeniz/dosinator

DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
exploitationinformation-gatheringnetwork-security+3
1442 years ago
Bryobio preview

Bryobio

GitHubemrekybs/bryobio

It was developed to speed up the processes of SOC Analysts during analysis
forensicsinformation-gatheringnetwork-forensics+3
476 months ago
BlueFish preview

BlueFish

GitHubemrekybs/bluefish

Automation tool designed to simplify the analysis of PCAP (Packet Capture) files
forensicsincident-responseinformation-gathering+2
206 months ago
printnightmare-detection-mitigation-lab preview

printnightmare-detection-mitigation-lab

GitHubkaritamw/printnightmare-detection-mitigation-lab

Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
digital-forensicseducationidentity-access-management+5
2 months ago
windows-malware-behavioral-analysis preview

windows-malware-behavioral-analysis

GitHub0x0allenace/windows-malware-behavioral-analysis

Behavioral Malware Analysis of a Simulated Multi-Stage Windows Malware Sample using FLARE-VM and REMnux. Evidence-driven DFIR investigation with IOC…

digital-forensicsdynamic-analysis-sandboxingeducation+8
12 months ago
ilk-toolkit preview

ilk-toolkit

GitLabilk-toolkit/ilk-toolkit

A ToolKit that automatically installs & configures all the Tools needed to turn your Daily Driver Linux Distro into a Pentesting Machine
information-gatheringnetwork-securitypassword-cracking+5
4 years ago
tplink-smartplug preview

tplink-smartplug

GitHubsoftscheck/tplink-smartplug

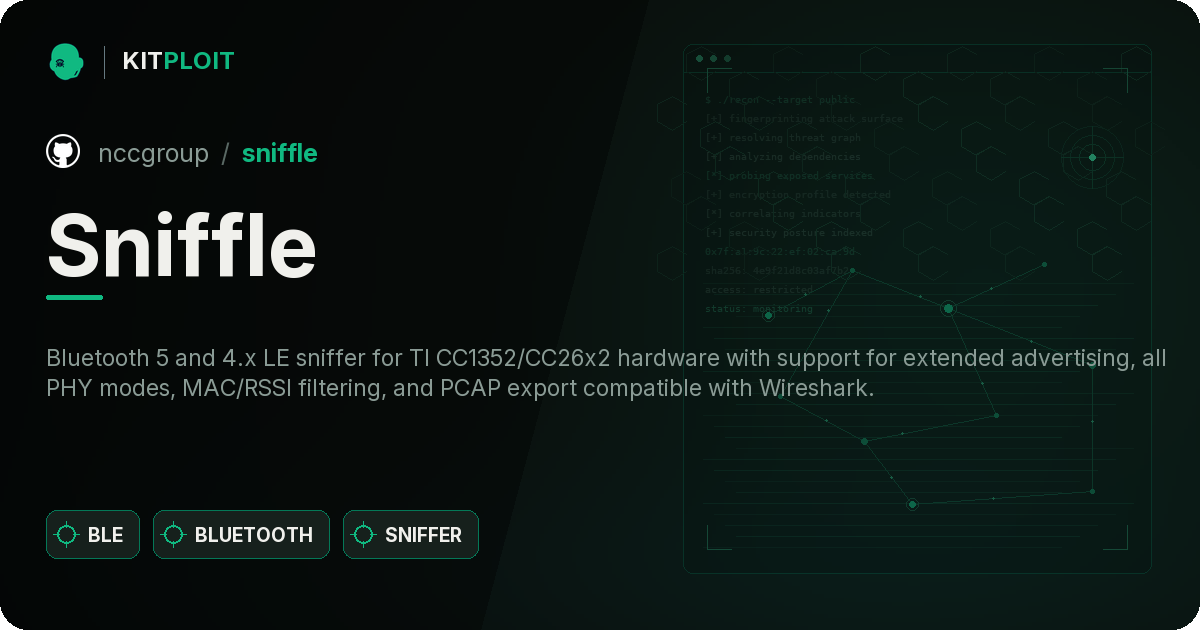
TP-Link WiFi SmartPlug Client and Wireshark Dissector
encryption-decryption-toolsfirmware-analysishardware-iot-security+6
1.2k1 year ago
Sniffle preview

Sniffle

GitHubnccgroup/sniffle

Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
bluetooth-securityembedded-systems-securityhardware-hacking+5
1.2k1 year ago
binder-trace preview

binder-trace

GitHubfoundryzero/binder-trace

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".

android-securitybinary-analysisdynamic-analysis-sandboxing+3
7701 year ago
mcpsnoop preview

mcpsnoop

GitHubkerlenton/mcpsnoop

Wireshark for MCP. A transparent proxy that shows every real tool call between your AI client and your MCP servers, live in your terminal.
api-security-testingdebuggersdynamic-analysis-sandboxing+5
35919h 17m ago
wireshark-rdp preview

wireshark-rdp

GitHubawakecoding/wireshark-rdp

Wireshark RDP resources
authenticationcurated-resourceseducation+3
2231 year ago
wireshark-forensics-plugin preview

wireshark-forensics-plugin

GitHubrjbhide/wireshark-forensics-plugin

Wireshark plugin that correlates network traffic with threat intelligence, asset tags, and vulnerability data to accelerate forensic analysis of PCAP…
digital-forensicsforensicsnetwork-forensics+3
1024 years ago
Network_Assessment preview

Network_Assessment

GitHubalperenugurlu/network_assessment

With Wireshark or TCPdump, you can determine whether there is harmful activity on your network traffic that you have recorded on the network you…
anomaly-detectionintrusion-detectionnetwork-security+2
1473 years ago
wiremax preview

wiremax

GitHubinfobyte/wiremax

Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
forensicsgeneral-purpose-utilitiesnetwork-security+2
102 months ago
pyshark-legacy preview

pyshark-legacy

GitHubkiminewt/pyshark-legacy

Python wrapper for tshark, allowing python packet parsing using wireshark dissectors (Python2 legacy version)

network-securitypacket-sniffing-analysisutilities-frameworks
68 years ago
Previous123Next