

Nettacker
 owasp/nettacker
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
api-securityapi-security-testingdynamic-code-analysis+14
5.6k
owasp/nettackerAutomated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management
 jonpichel/cve-2017-7358
Proof-of-concept exploit for CVE-2017-7358, demonstrating a specific vulnerability in a software application. Intended for security research and…
 btar1gan/exploit_cve-2022-35914
Exploit code for CVE-2022-35914, a vulnerability in a software component. Provides proof-of-concept implementation for security testing and research.
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
 shoucheng3/apache__jspwiki_cve-2019-10077_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10077, targeting a Java-based wiki platform with JAAS authentication and access control. Enables…
 shoucheng3/apache__jspwiki_cve-2019-10089_2-11-0-m4
Java-based wiki platform with detailed access control and JAAS security integration, provided as a vulnerable version for security testing and CVE…
 imjdl/cve-2012-4431
Apache Tomcat source code repository for CVE-2012-4431, a Java servlet container vulnerability. Provides the vulnerable codebase for analysis and…
 kudelskisecurity/cdf
Automated differential fuzzing tool for cryptographic software that detects implementation errors, compliance failures, and side-channel leaks…
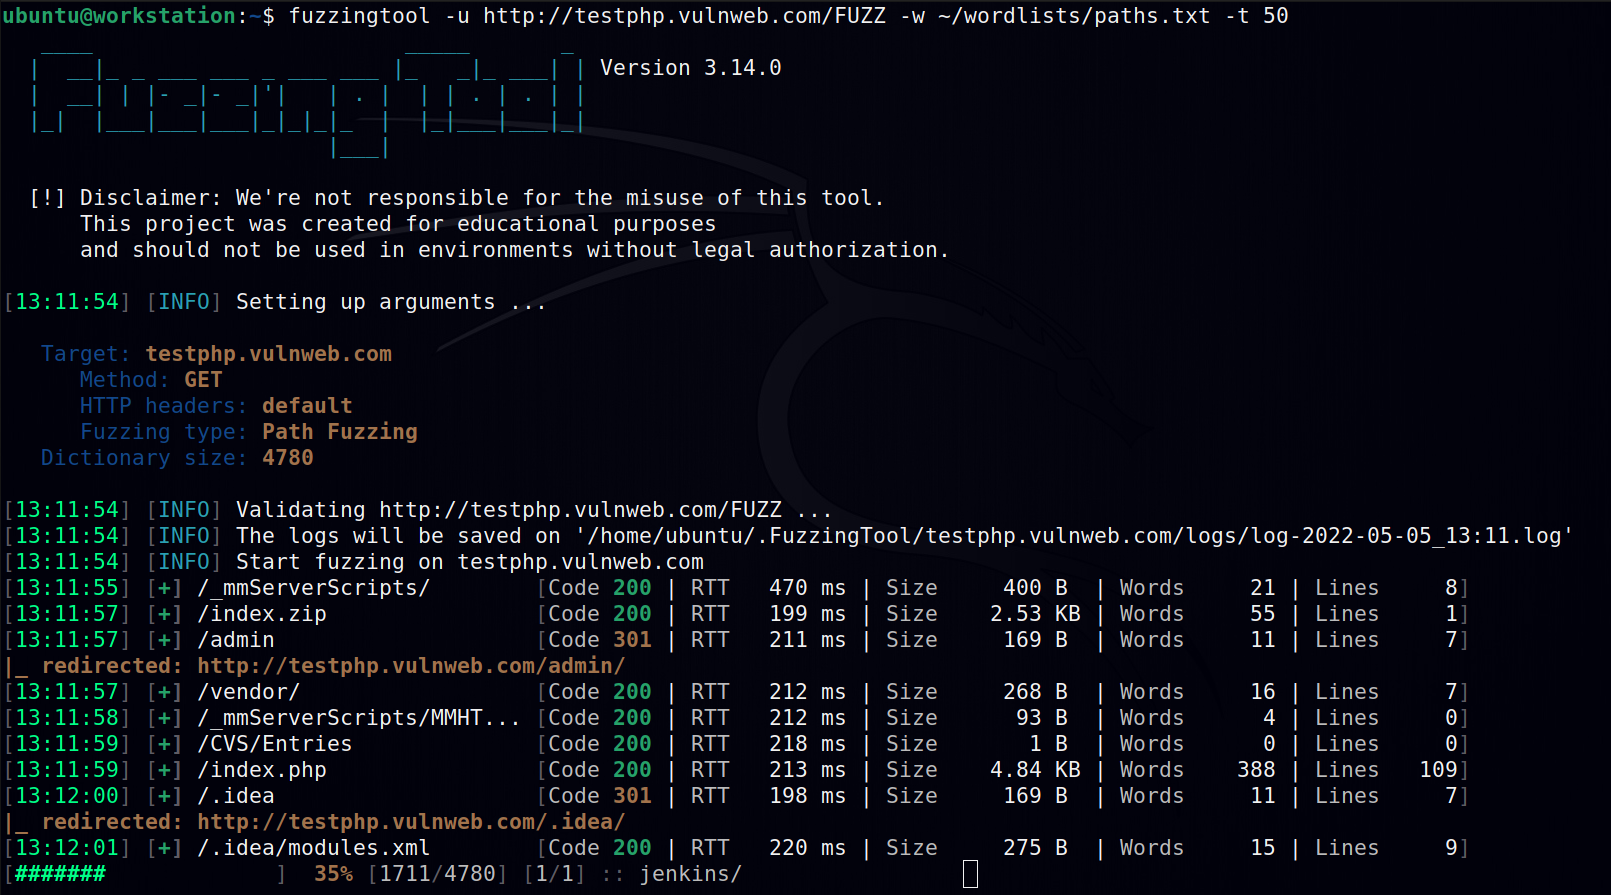 nescau-ufla/fuzzingtool
Software for fuzzing, used on web application pentestings.
 shoucheng3/apache__jspwiki_cve-2019-0225_2-11-0-m2
Exploit module for Apache JSPWiki CVE-2019-0225, enabling remote code execution via crafted requests. Designed for penetration testing and…
 shoucheng3/apache__jspwiki_cve-2019-10078_2_11_0_m4_fixed
Exploit testing repository for Apache JSPWiki CVE-2019-10078, demonstrating a cross-site scripting vulnerability in a Java-based wiki platform with…
 shoucheng3/apache__jspwiki_cve-2019-10078_2-11-0-m3
Exploit module for Apache JSPWiki CVE-2019-10078, enabling security testing of Java-based wiki platforms through targeted vulnerability exploitation…
 adamlaurie/rfidiot
Python library and tools for exploring RFID/NFC tags and readers: read, write, clone, and analyze supported ACG serial hardware for research and…
 alessiodallapiazza/wpscan
WordPress security scanner that enumerates vulnerable plugins, themes, and users to identify misconfigurations and known vulnerabilities for…
 nochemax/bluekeep-gui
vulnerabilidad CVE-2019-0708 testing y explotacion
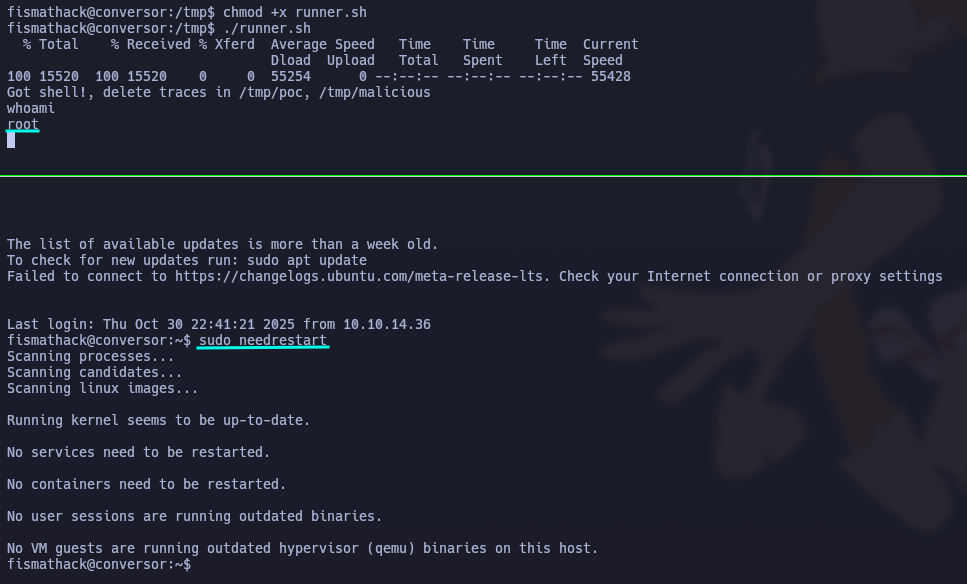 loaxert/cve-2024-48990-poc
Proof-of-concept exploit for CVE-2024-48990, demonstrating local privilege escalation in needrestart via PYTHONPATH manipulation. Includes runner…
 rishi-kaul/cve-2022-23779
CVE-2022-23779 is a security vulnerability in Zoho ManageEngine Desktop Central ,Testing for CVE-2022-23779 using curl
 p0dalirius/cve-2022-36446-webmin-software-package-updates-rce
A Python script to exploit CVE-2022-36446 Software Package Updates RCE (Authenticated) on Webmin < 1.997.