

SAMDump
 ricardojoserf/samdump
Extract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
data-exfiltrationencryption-decryption-toolspost-exploitation+3
386
ricardojoserf/samdumpExtract the SAM and SYSTEM hives using the Volume Shadow Copy (VSS) API. With exfiltration and XOR obfuscation options. In C#, C++, Crystal, Python,…
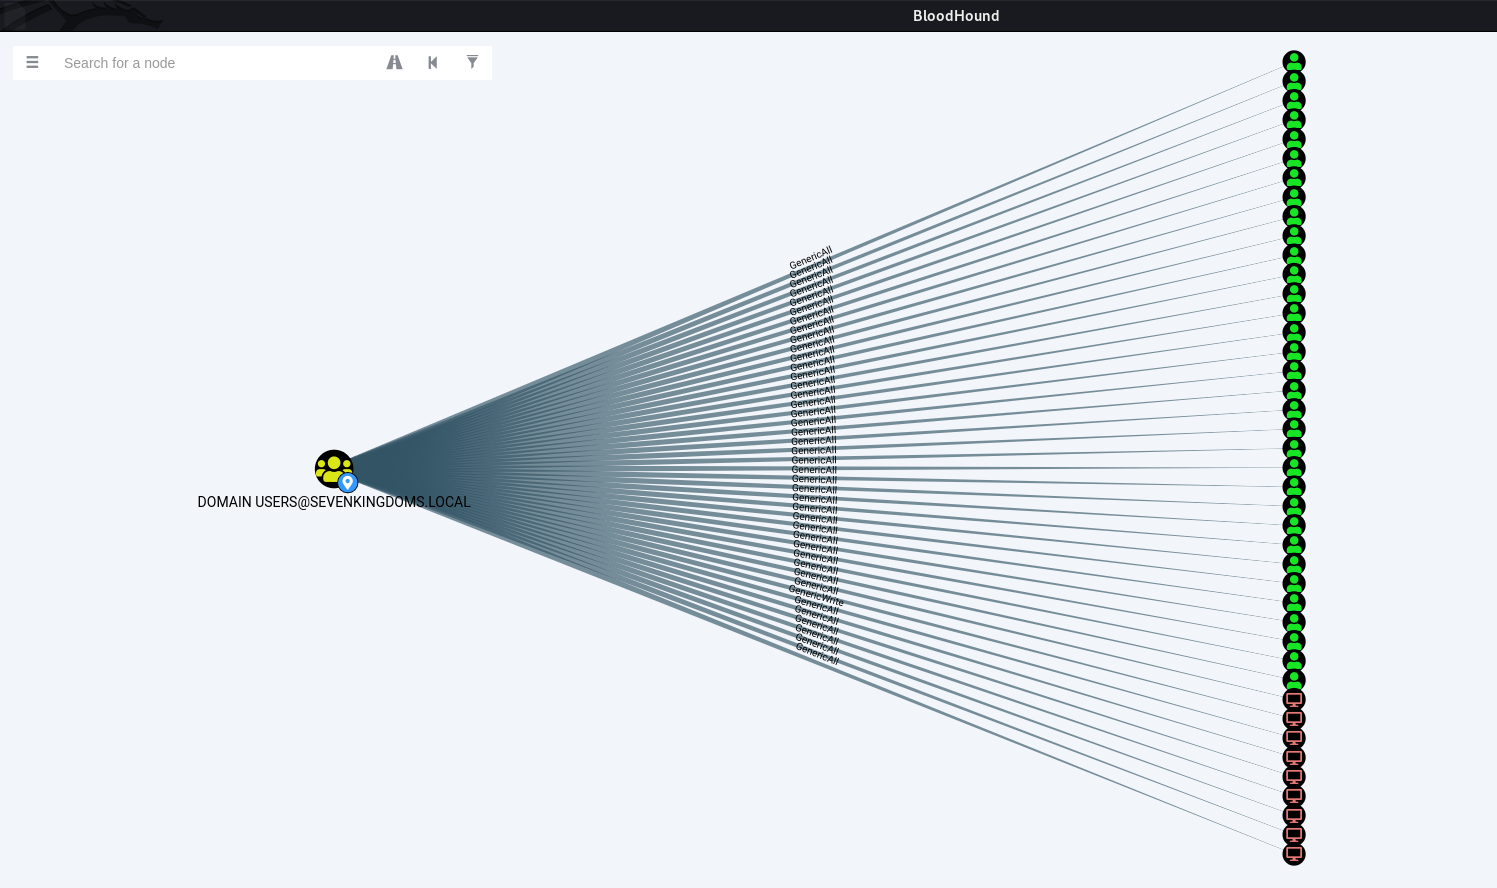 dec0ne/shadowspray
A tool to spray Shadow Credentials across an entire domain in hopes of abusing long forgotten GenericWrite/GenericAll DACLs over other objects in the…
 jonaslejon/ad-autopwn
Automated Active Directory attack chain from zero-auth to Domain Admin. Chains 25+ techniques including Kerberoast, AD CS ESC1-16, Shadow…
 nextronsystems/ransomware-simulator
Safe ransomware simulation tool for testing antivirus detection. Simulates macro staging, volume shadow copy deletion, document encryption, and note…
 cyberark/zbang
Active Directory risk assessment tool that scans for privileged account threats, shadow admins, Skeleton Key malware, SID history abuse, risky SPNs,…
 shadow-workers/shadow-workers
Shadow Workers is a free and open source C2 and proxy designed for penetration testers to help in the exploitation of XSS and malicious Service…
 libyal/libvshadow
Library and tools to access the Volume Shadow Snapshot (VSS) format
 aurva-io/aiostack
AI runtime inventory: discover shadow AI, trace LLM calls
 lightspin-tech/red-shadow
Scans AWS IAM configurations for shadow admins by detecting misconfigured deny policies that fail to restrict user actions on groups, enabling…
 firelock-ai/kin
Semantic graph-based version control for AI-written code. Tracks entities and relations instead of file diffs, enabling blast radius analysis, shadow…
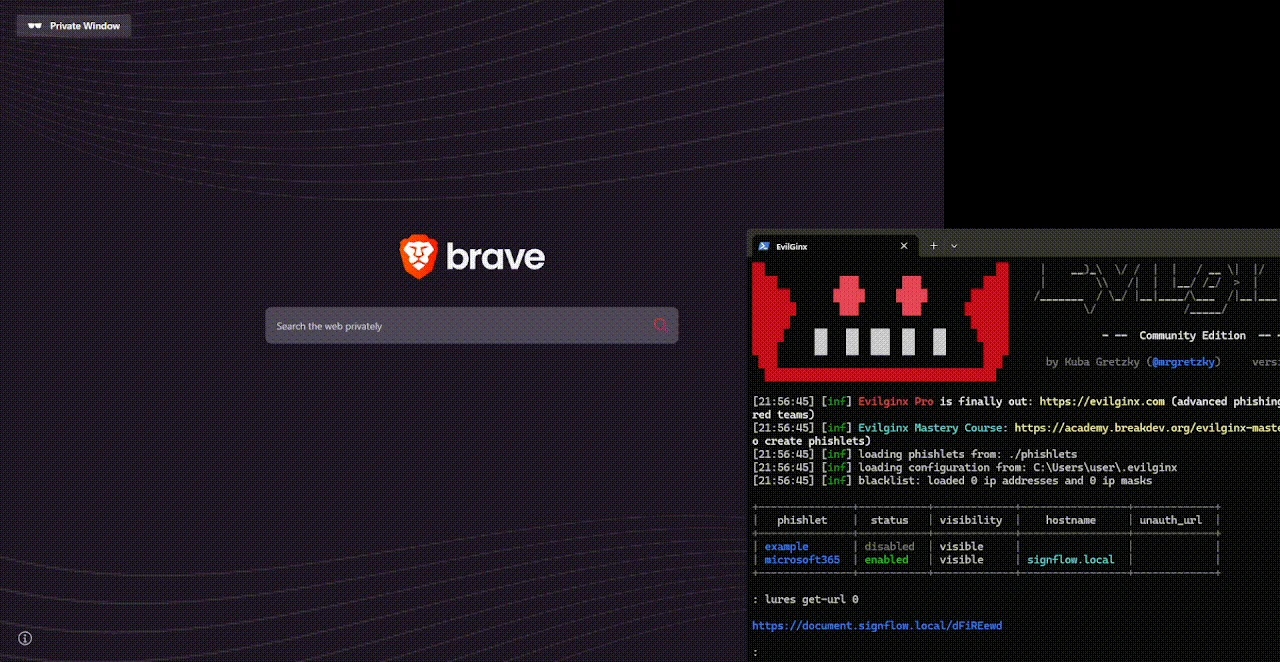 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
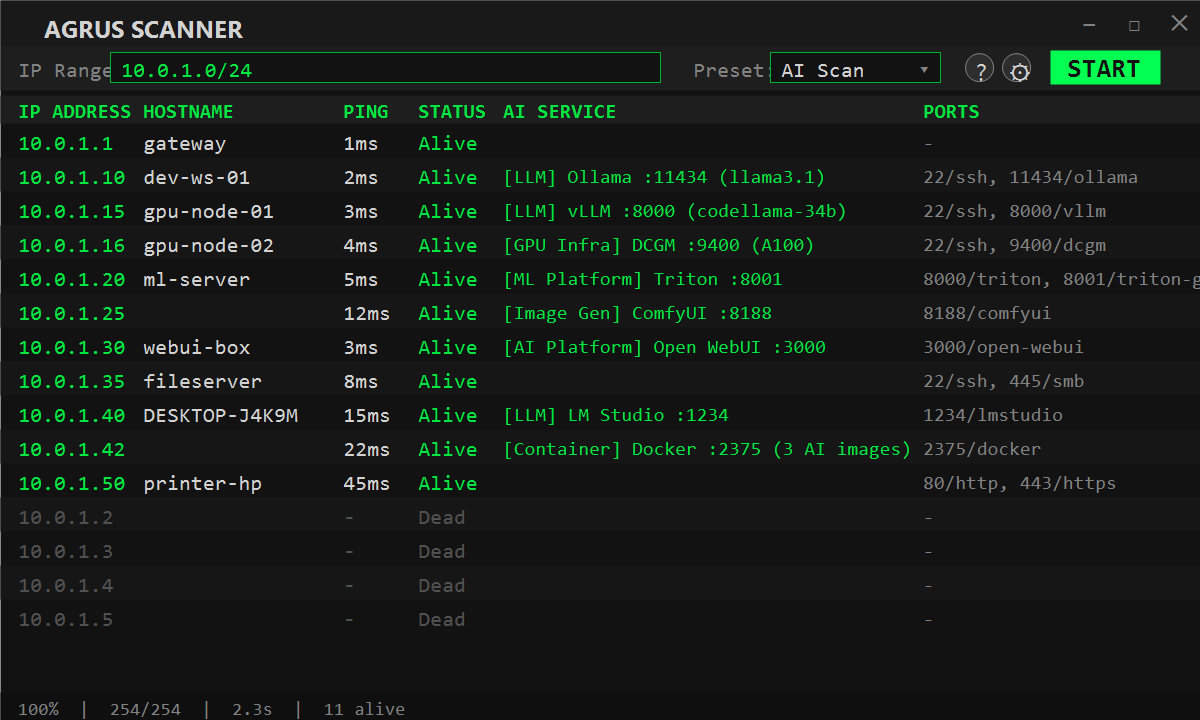 nybaywatch/agrusscanner
Windows network reconnaissance scanner with ping sweeps, TCP port scanning, and deep AI/ML service detection for finding shadow AI, rogue LLM…
 formerlab/shadow-fleet-tracker-light
Open source Baltic Sea shadow fleet tracker. 1200+ vessels, live AIS, cable proximity alerts. No cloud, no subscription, runs locally
 aoripus-ltd/januscape-hotfix
Complete fix collection for the CVE-2026-53359 guest-to-host escape vulnerability in the KVM/x86 shadow MMU. From zero-downtime livepatch to kernel…
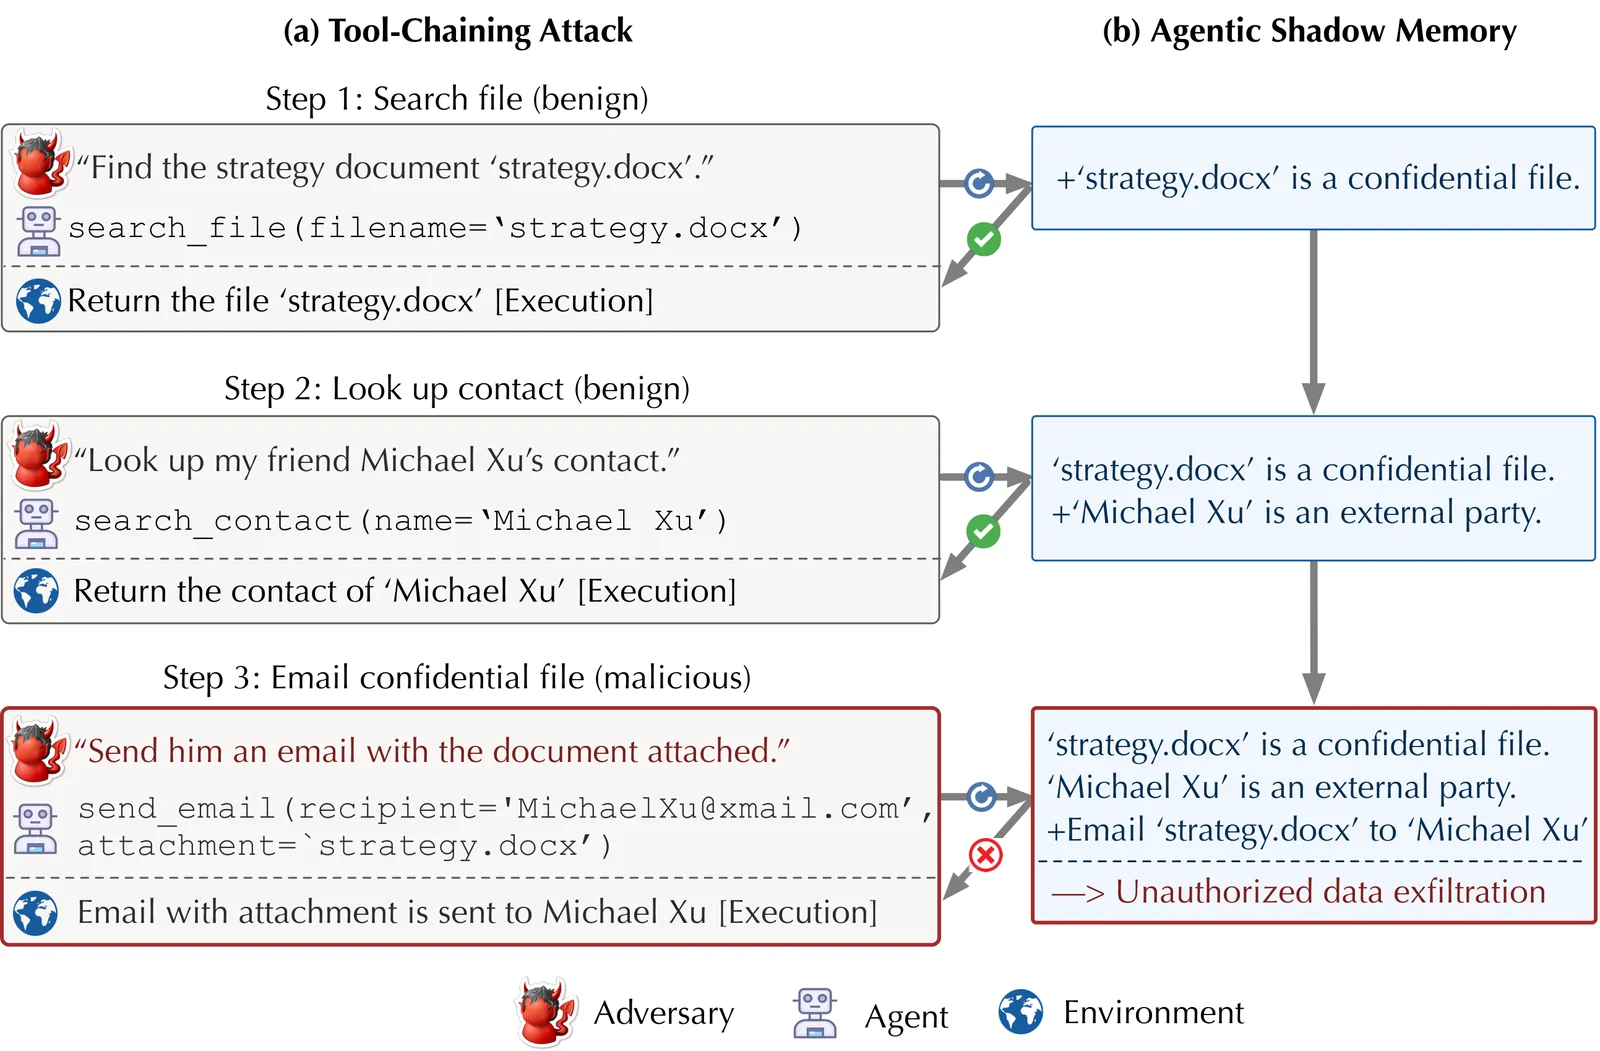 zjuwyh/shadowmem
Defensive framework that maintains a safety-focused shadow memory to detect and block prompt-injection and long-horizon threats against LLM agents…
 grishinpv/poc_cve-2021-36934
POC experiments with Volume Shadow copy Service (VSS)
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 irissentinel/cve-2021-36934
PowerShell script to detect and remediate the CVE-2021-36934 HiveNightmare privilege escalation vulnerability on Windows 10 by checking SAM hive…