fad-checker
 9pings/fad-checker
Buildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
code-analysisconfiguration-auditingdefensive-tools+6
2
9pings/fad-checkerBuildless dependency auditor that scans 10 ecosystems offline, reporting CVEs prioritized by CISA KEV and EPSS, EOL packages, licenses, committed…
 kabiri-labs/sshfinder
Parallel SSH service discovery and security auditor that scans any port, validates SSH banners, and audits authentication methods, weak cryptography,…
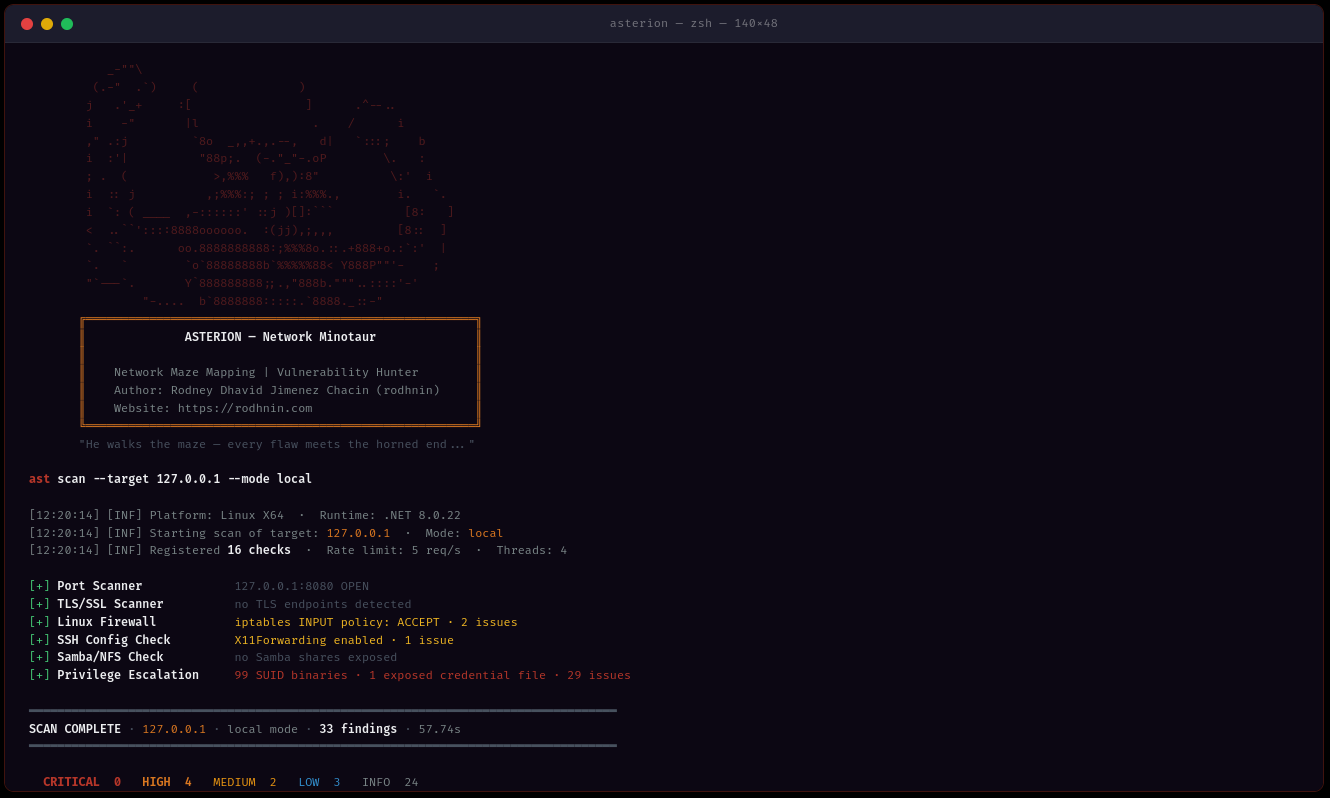 rodhnin/asterion-network-minotaur
Network and domain security auditor scanning Windows Active Directory, Linux systems, and network infrastructure with AI-powered hardening guides…
 mahdi13830510/cve-2026-31431-mitigation-suite
Kernel-runtime defense framework for AF_ALG vulnerabilities, featuring eBPF socket tracing, Ansible hardening, and a crypto auditor for drift…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 hackwarts12/escepcion
Passive AD CS auditor detecting ESC1–ESC16 and Shadow Credentials via read-only LDAP/ACL/registry checks, with prioritized remediation and SIEM-ready…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
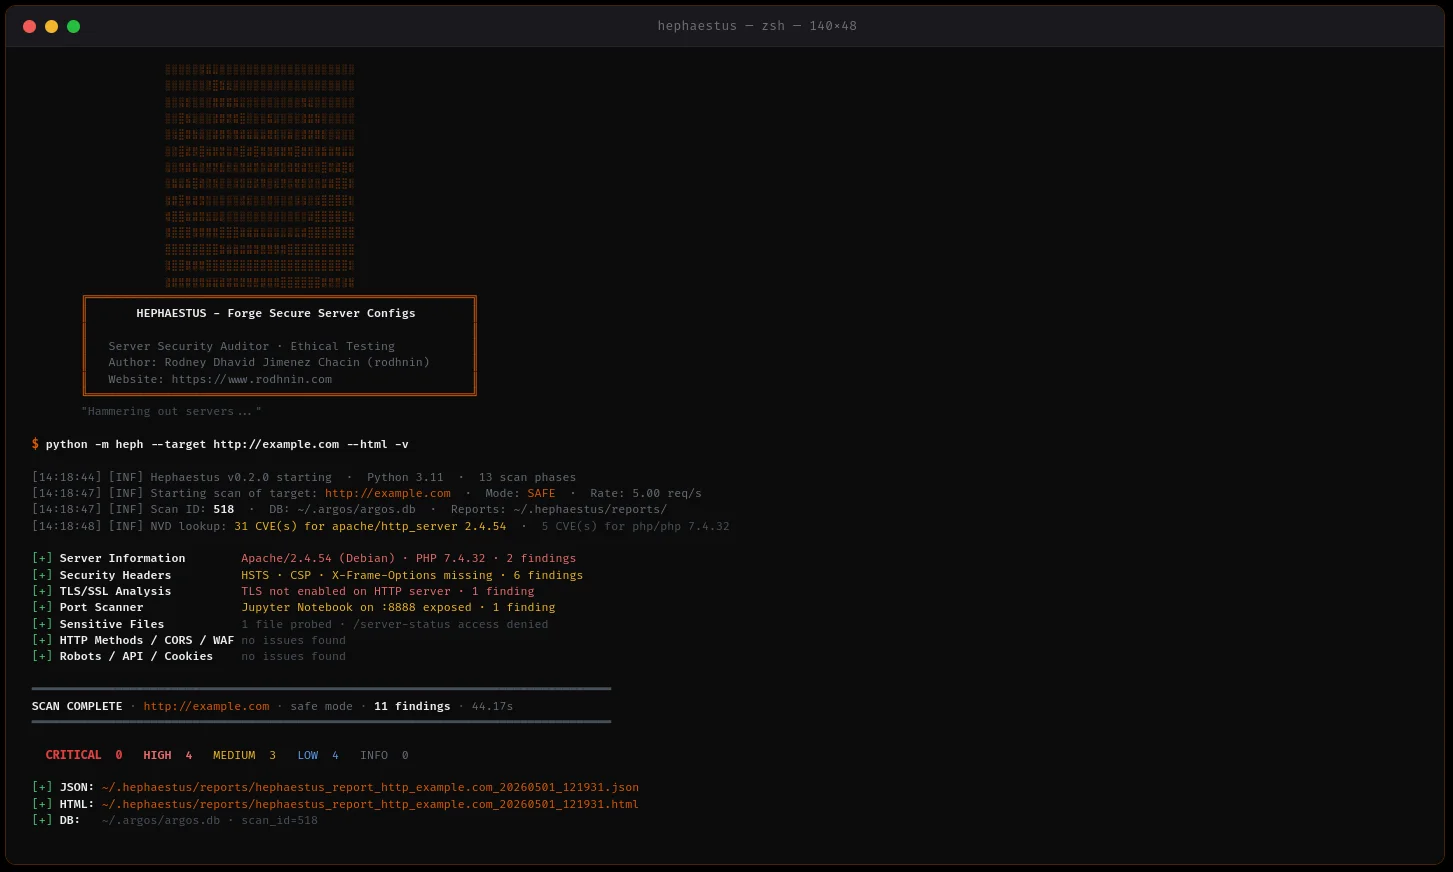 rodhnin/hephaestus-server-forger
server security auditor scanning Apache, Nginx, and IIS configurations with AI-powered hardening guides and professional reporting.
 aa022/cve-2026-23918-passive-audit
Passive HTTP metadata auditor for CVE-2026-23918 exposure triage
 ayinedjimi-consultants/ldaprecon-ai
Active Directory LDAP Security Auditor with AI-Powered Analysis - By Ayi NEDJIMI https://ayinedjimi-consultants.fr
 developerfred/cve-2022-31199
Proof-of-concept exploits for CVE-2022-31199, a critical .NET deserialization RCE in Netwrix Auditor. Includes Python and PowerShell scripts, payload…
 sibersan/apache_audit_cve-2026-23918
Python toolkit to audit Apache HTTP Server against CVE-2026-23918 (HTTP/2 double-free RCE) and 4 related CVEs. Passive scanner with ALPN verification…
 fevar54/cve-2026-48172---litespeed-cpanel-plugin-version-auditor
Auditor de version para CVE-2026-48172: verifica localmente si el plugin LiteSpeed de cPanel es vulnerable, sin explotar.
 0xby7eme/windows-lpe-auditor
A small Windows local-privilege-escalation (LPE) misconfiguration auditor with a terminal UI, built with C++20 and FTXUI
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 d0rb/shellscope
Defensive exposure auditor for Plex2Shell and php2shell — find your own before they find you.