

Xenon
 mythicagents/xenon
A Mythic agent for Windows written in C
command-and-controldata-exfiltrationdefensive-tools+9
mythicagents/xenonA Mythic agent for Windows written in C
 aahmad097/badoutlook
Proof-of-concept C# tool that reads Outlook emails via COM interface, extracts base64-encoded shellcode from trigger subject lines, and executes…
 redsiege/cimplant
C# port of WMImplant which uses either CIM or WMI to query remote systems
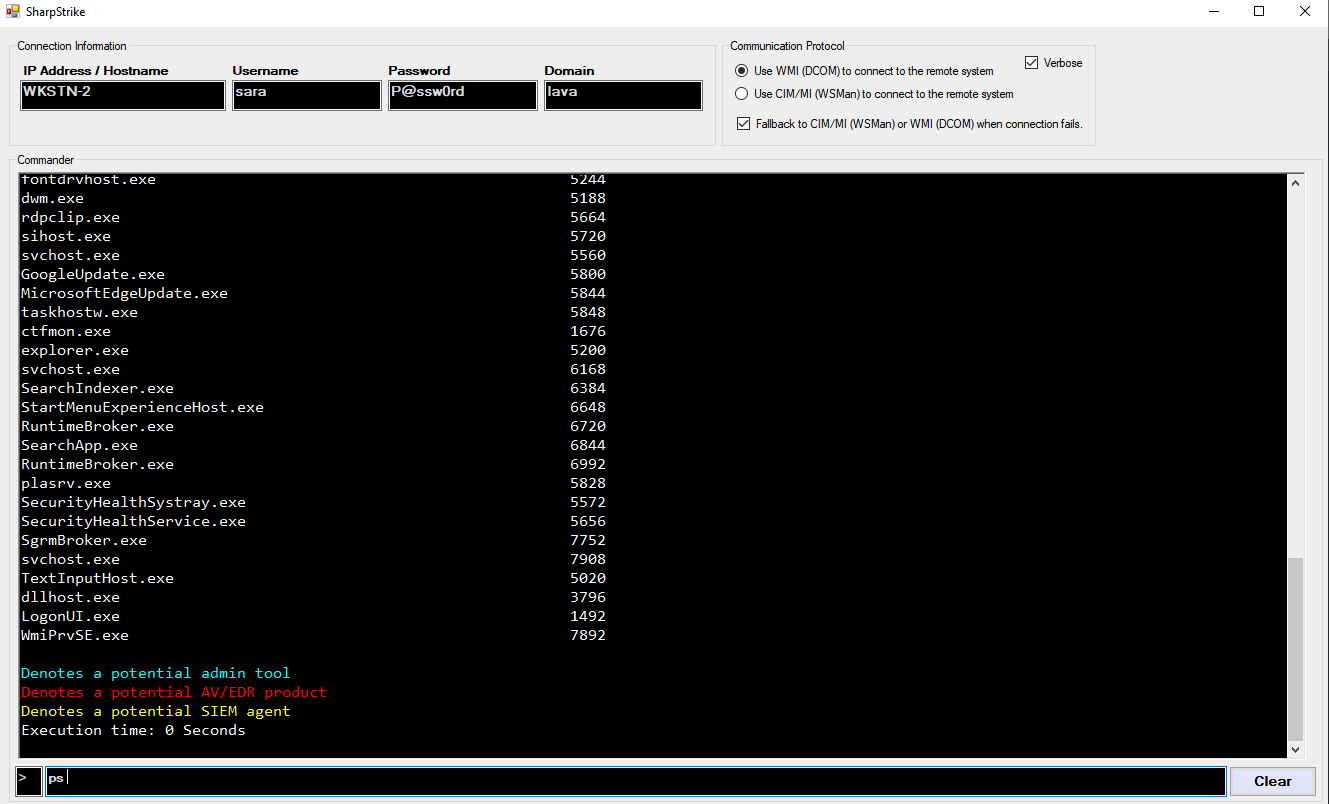 iomoath/sharpstrike
A Post exploitation tool written in C# uses either CIM or WMI to query remote systems.
 mertdas/redpersist
C# tool for establishing Windows persistence via multiple techniques including scheduled tasks, WMI events, startup folders, and registry hijacking,…
 anthemtotheego/sharpsploitconsole
C# console application for post-exploitation and red team operations, integrating SharpSploit to execute Mimikatz commands, perform Kerberoasting,…
 abhishekkr/n00brat
Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 d4rk007/sak1to-shell
Multi-threaded, multi-os/platform (Linux/Windows) c2 server and Windows reverse TCP shell client both written in C.
 watersalesman/aura-botnet
A super portable botnet framework with a Django-based C2 server. The client is written in C++, with alternate clients written in Rust, Bash, and…
 nyan-x-cat/revengerat-stub-cssharp
Revenge-RAT C# Stub - Fixed
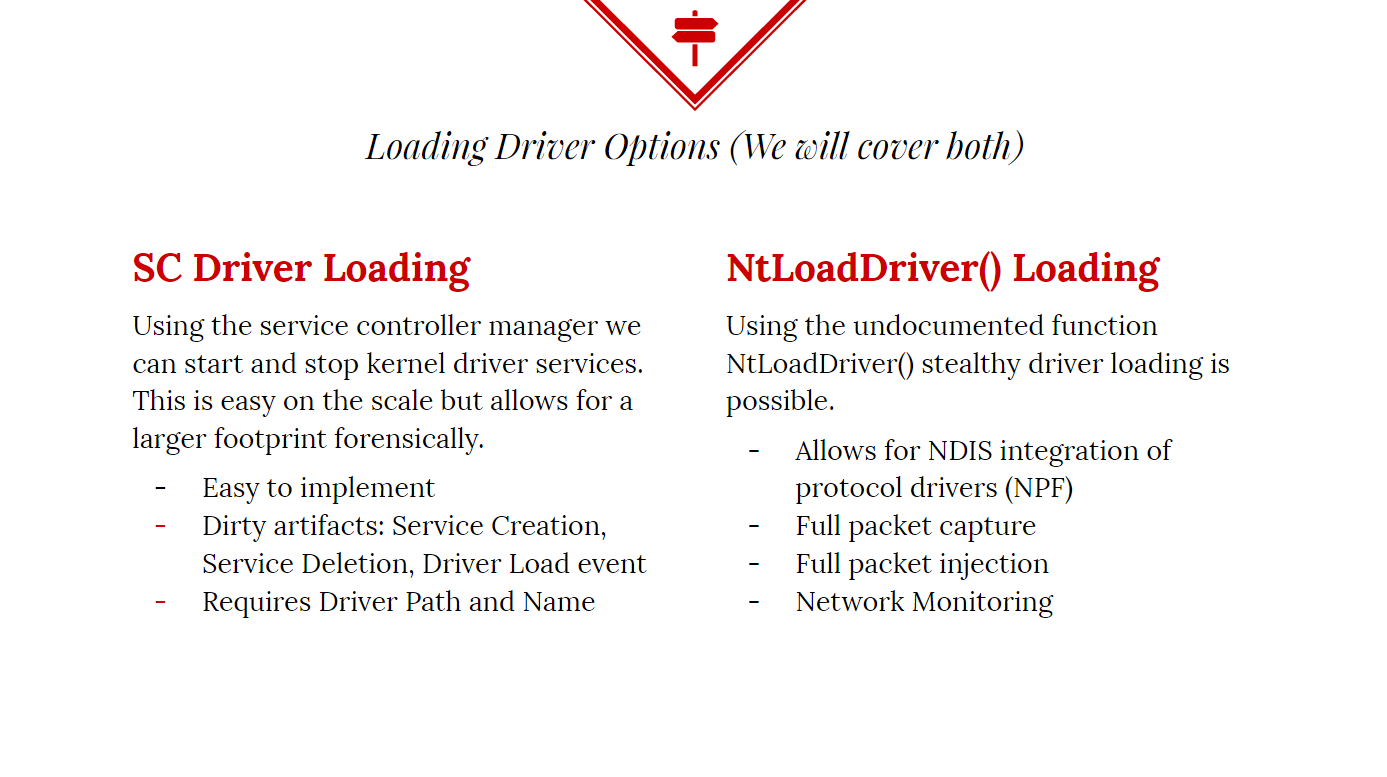 killswitch-gui/hotload-driver
C++
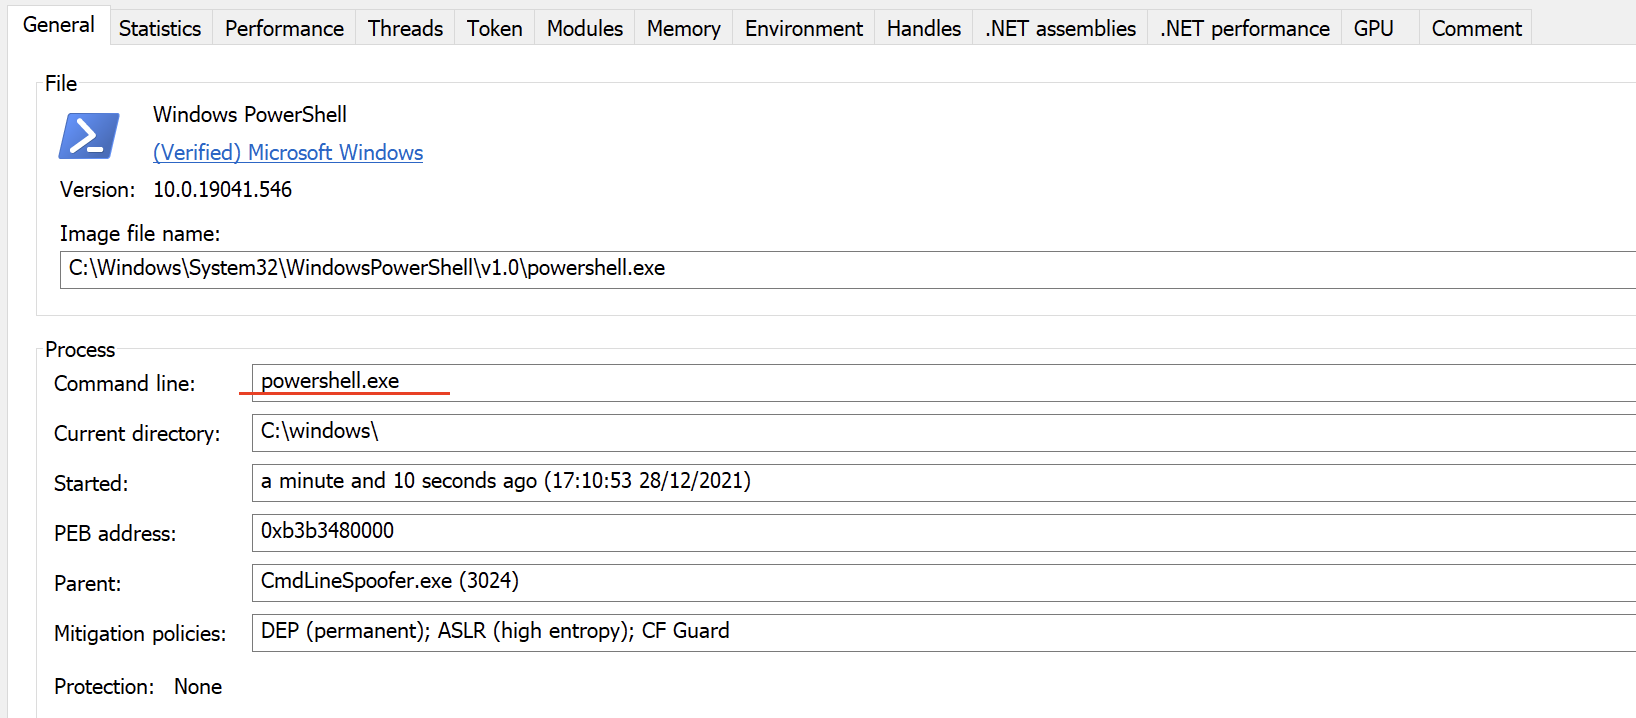 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
 praetorian-inc/wasmforge
WasmForge — compile Go and C# programs to single-binary, WASM-sandboxed native executables with polymorphic output.
 nyan-x-cat/njrat-0.7d-stub-csharp
njRAT C# Stub - Fixed For PowerShell
 ivancabrera02/r2socks
SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…