
caido
 caido/caido
Lightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
penetration-testingweb-proxies-interceptionweb-security
caido/caidoLightweight web proxy for intercepting, inspecting, and modifying HTTP traffic to audit web applications during penetration testing and bug bounty…
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 galkan/crowbar
Crowbar is brute forcing tool that can be used during penetration tests. It is developed to support protocols that are not currently supported by…
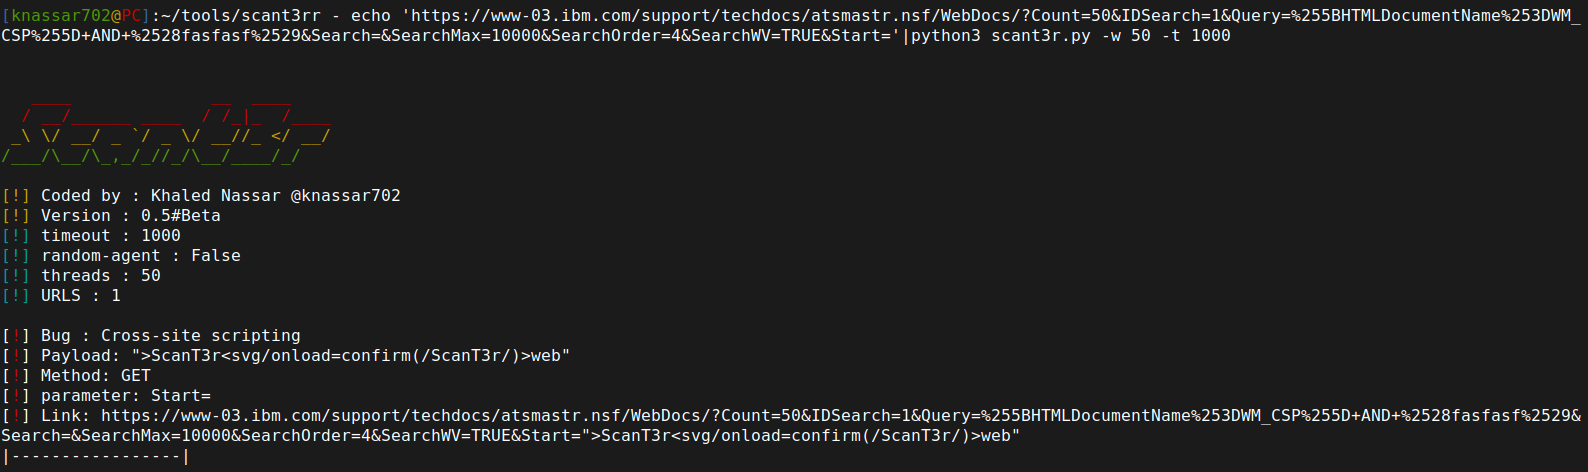 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
 flock4h/freeway
WiFi Penetration Testing & Auditing Tool
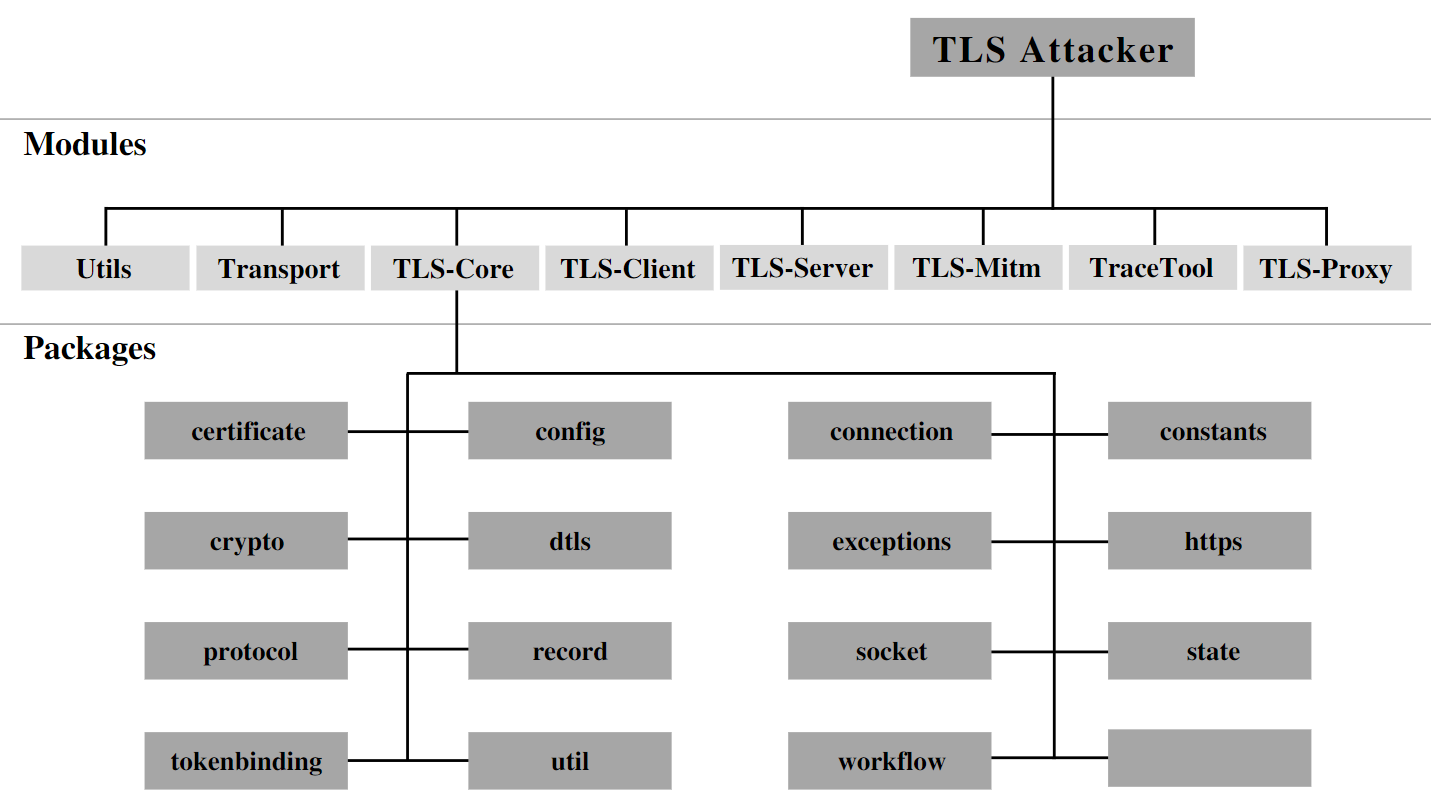 tls-attacker/tls-attacker
Java-based framework for systematic fuzzing and analysis of TLS libraries. Enables arbitrary protocol message crafting, modification, and testing of…
 vanhoefm/fragattacks
Automated vulnerability tester for Wi-Fi clients and access points, detecting FragAttacks fragmentation/aggregation flaws through frame injection,…
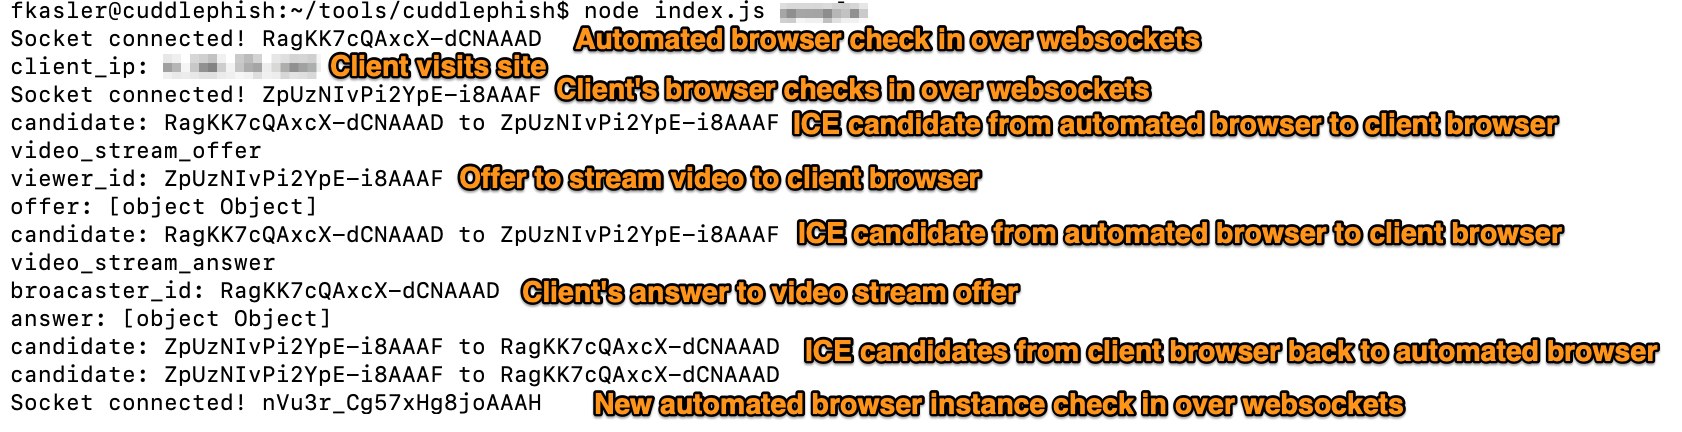 fkasler/cuddlephish
Weaponized Browser-in-the-Middle (BitM) for Penetration Testers
 hackmanit/web-cache-vulnerability-scanner
Go-based CLI scanner for web cache poisoning and deception. Supports 10 poisoning techniques, multiple deception methods, built-in crawler, JSON…
 edoardottt/missing-cve-nuclei-templates
Weekly updated list of missing CVEs in nuclei templates official repository. Mainly built for bug bounty, but useful for penetration tests and…
 jas502n/cve-2020-14882
Weblogic CVE-2020-14882 unauthorized RCE exploit with patch bypass, command execution, and webshell deployment for penetration testing.
 datadog/threatest
CLI and Go framework for end-to-end testing of threat detection rules. Detonates attack techniques and verifies alerts in security platforms like…
 jewel591/xssmap
Python-based XSS vulnerability scanner with support for POST/GET requests, parameter injection in cookies/referer/user-agent, and multiple encoding…
 mdsecactivebreach/regpwn
Windows local privilege escalation exploit targeting CVE-2026-24291, with support for Windows 10/11 and Server 2016-2022 for authorized security…
 secdec/adapt
ADAPT is a tool that performs automated Penetration Testing for WebApps.
 rub-nds/ws-attacker
WS-Attacker is a modular framework for web services penetration testing. It is developed by the Chair of Network and Data Security, Ruhr University…
 dzonerzy/gowapt
Go Web Application Penetration Test