
Archived
BypassFuzzer
 intrudir/bypassfuzzer
Fuzz 401/403/404 pages for bypasses
fuzzingids-ips-evasionpenetration-testing+3
431
intrudir/bypassfuzzerFuzz 401/403/404 pages for bypasses
 portswigger/turbo-intruder
High-speed Burp Suite extension for sending large volumes of HTTP requests with a custom stack, Python-based attack configuration, and advanced…
 portswigger/http-request-smuggler
Burp Suite extension for automated detection and exploitation of HTTP request smuggling vulnerabilities, supporting HTTP/1.1 and HTTP/2-downgrade…
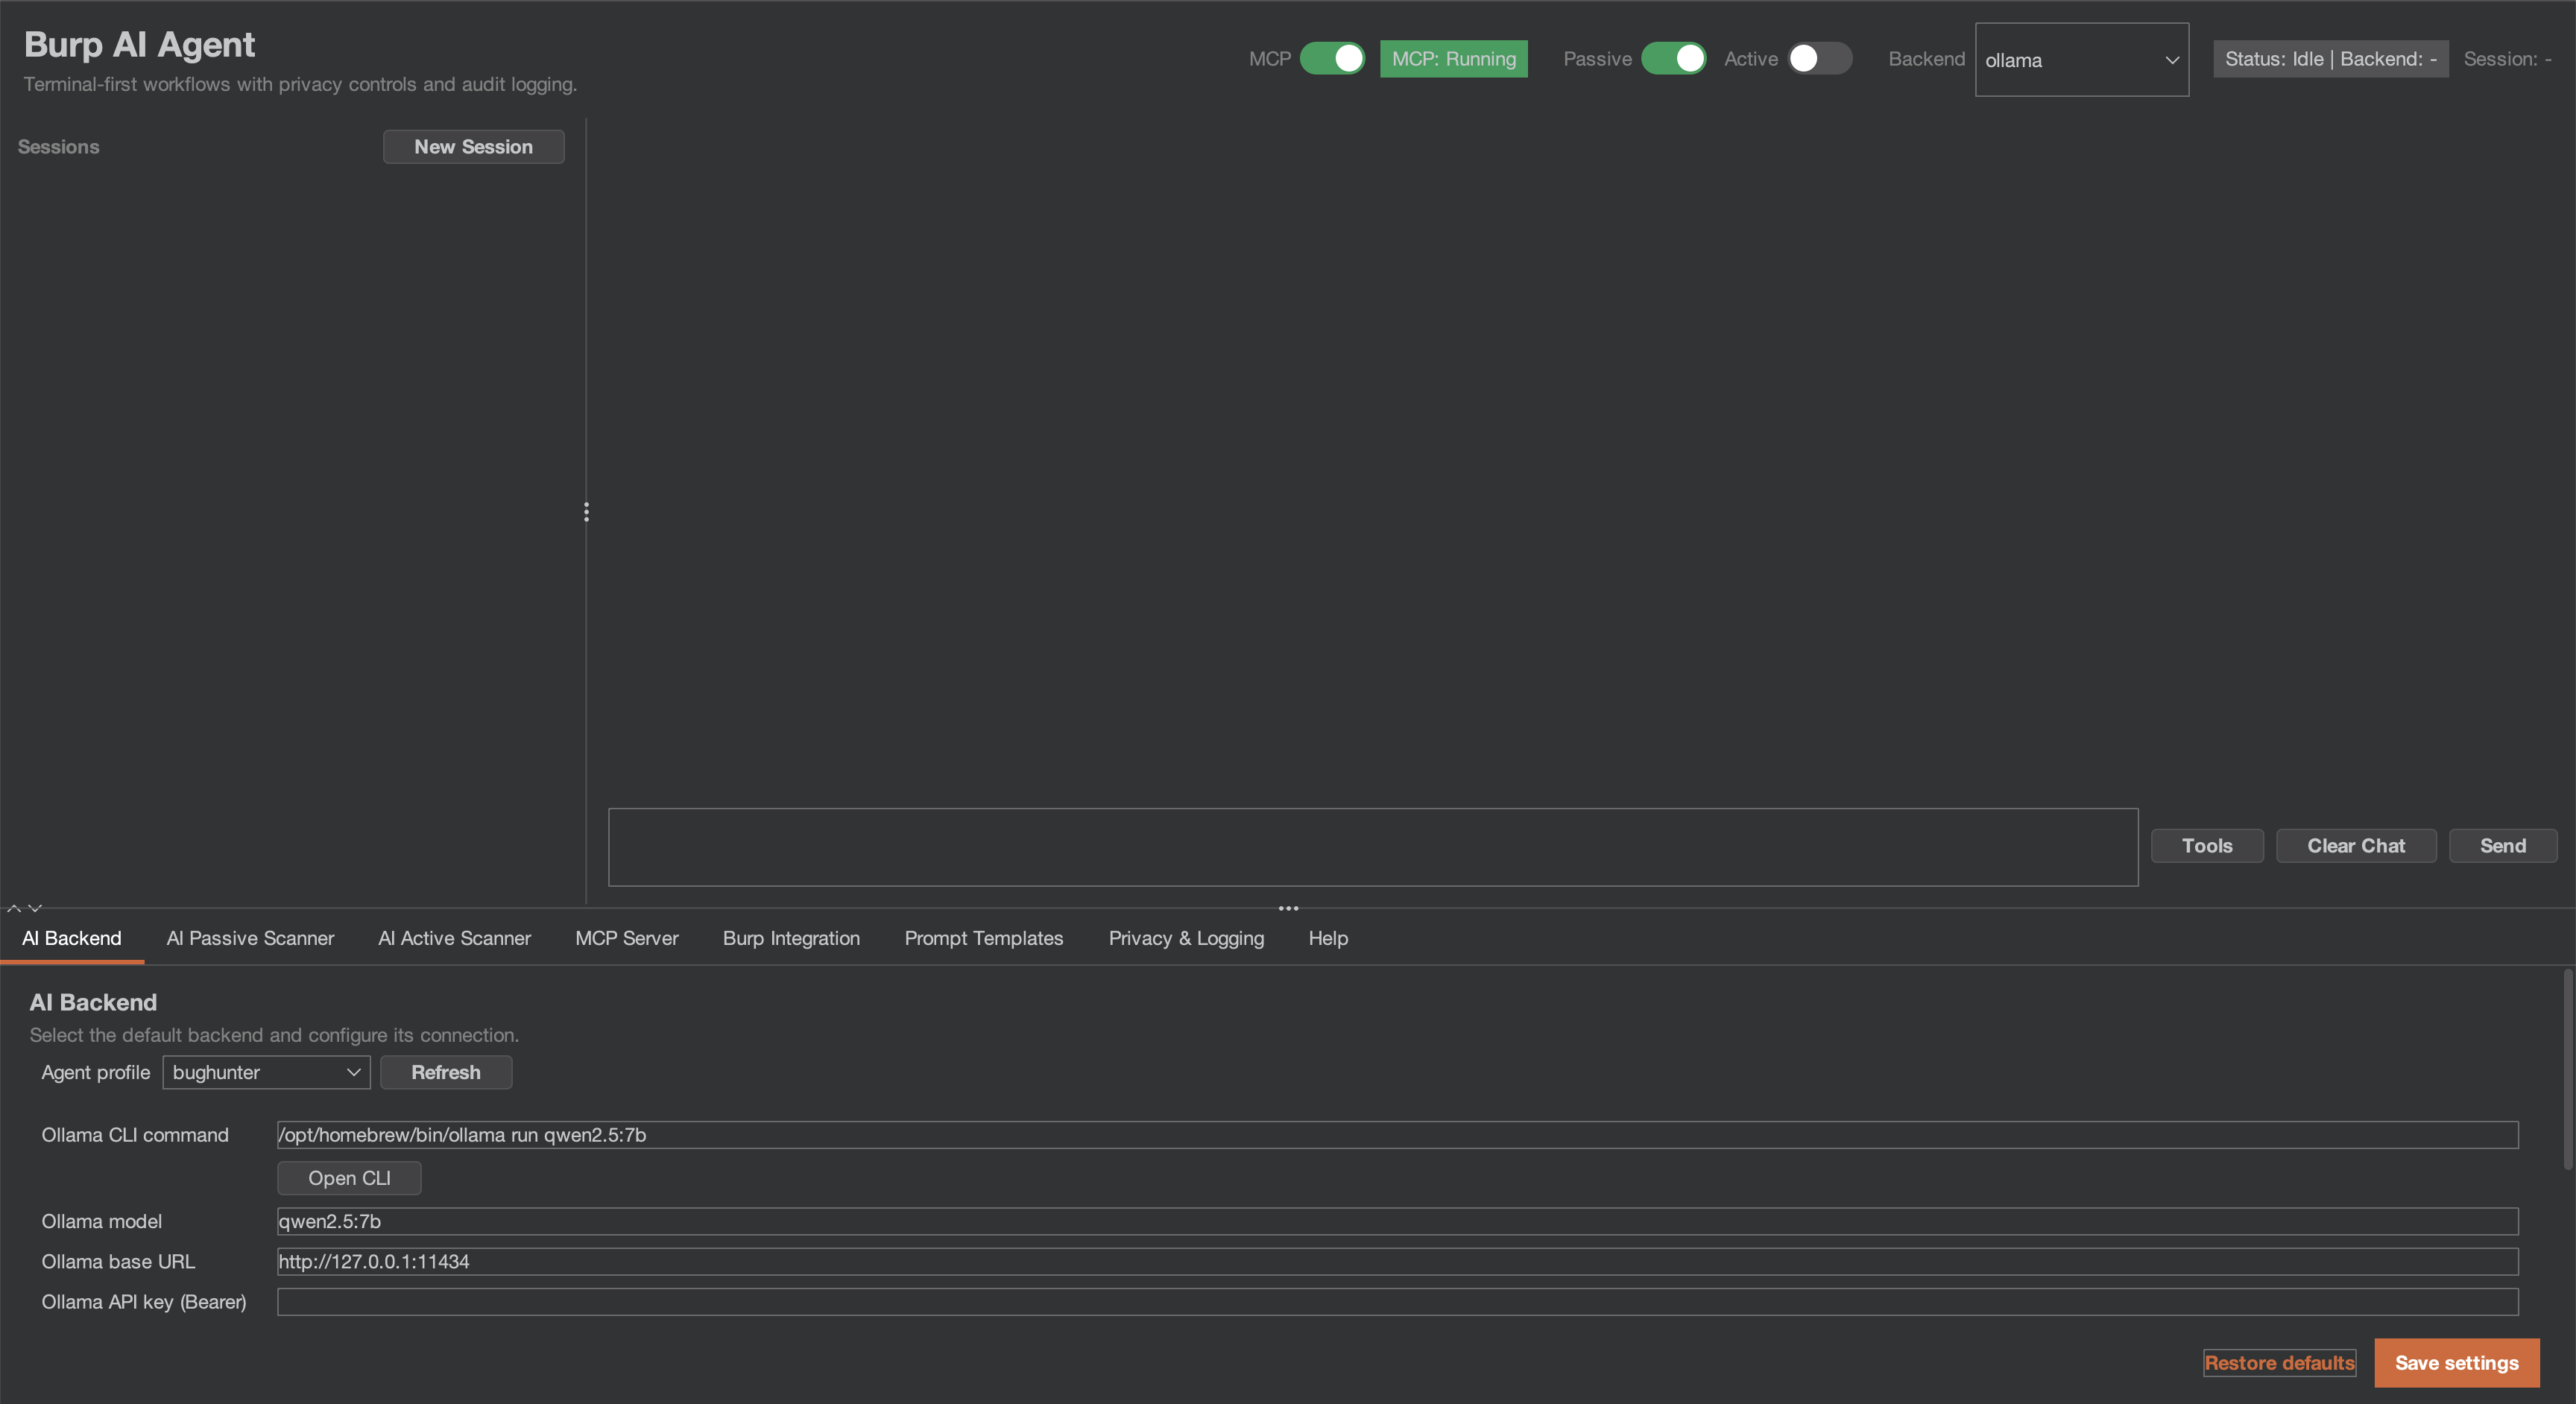 six2dez/burp-ai-agent
Burp Suite extension that adds built-in MCP tooling, AI-assisted analysis, privacy controls, passive and active scanning and more
 portswigger/param-miner
Burp Suite extension that discovers hidden, unlinked parameters using advanced diffing and binary search, enabling detection of web cache poisoning…
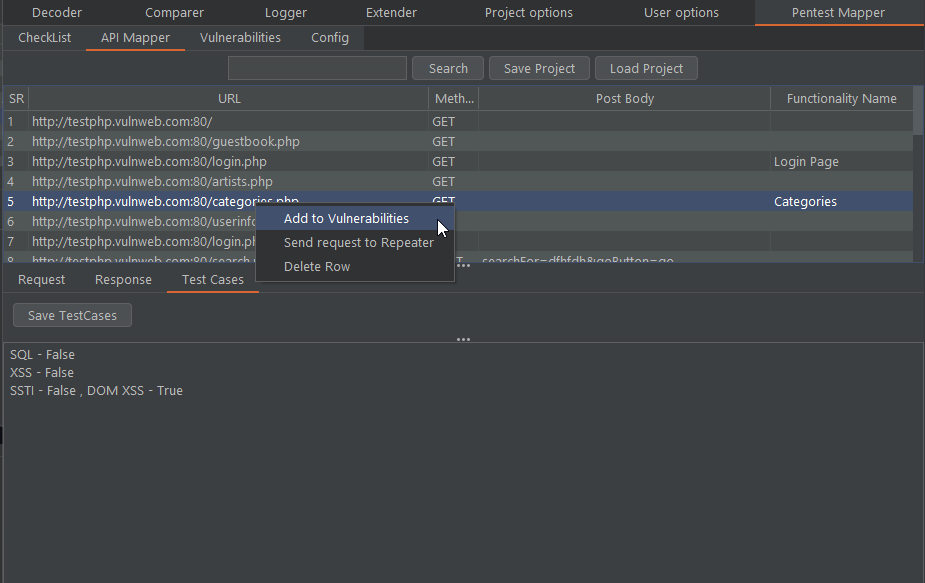 anof-cyber/pentest-mapper
A Burp Suite Extension for pentester and bug bounty hunters an to maintain checklist, map flows, write test cases and track vulnerabilities
 portswigger/oauth-scan
Burp Suite Extension useful to verify OAUTHv2 and OpenID security
 portswigger/pentest-mapper
A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
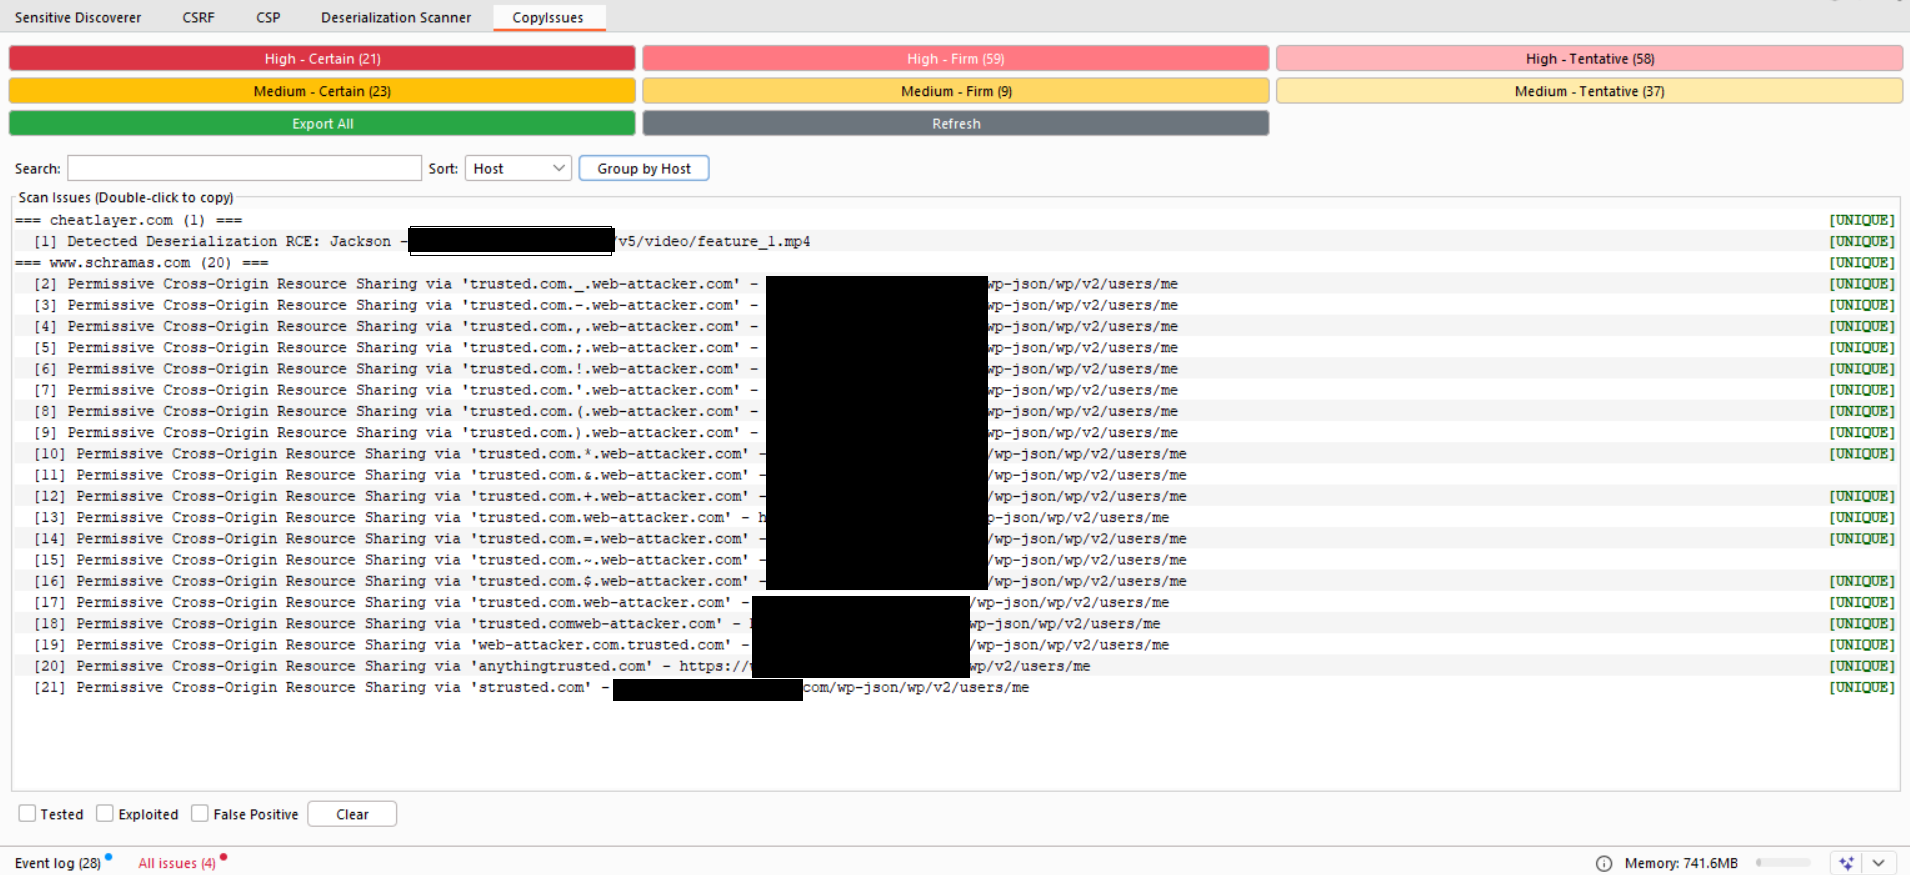 teycir/burpcopyissues
Burp suite extension that lets you easily copy issues
 f0ng/text4shellburpscanner
Burp Suite extension for detecting CVE-2022-42889 (Text4Shell) vulnerability via passive scanning of HTTP requests and responses.
 overspace-labs/hae
Modular Burp Suite extension for fine-grained highlighting and extraction of sensitive data from HTTP and WebSocket traffic, enabling efficient…
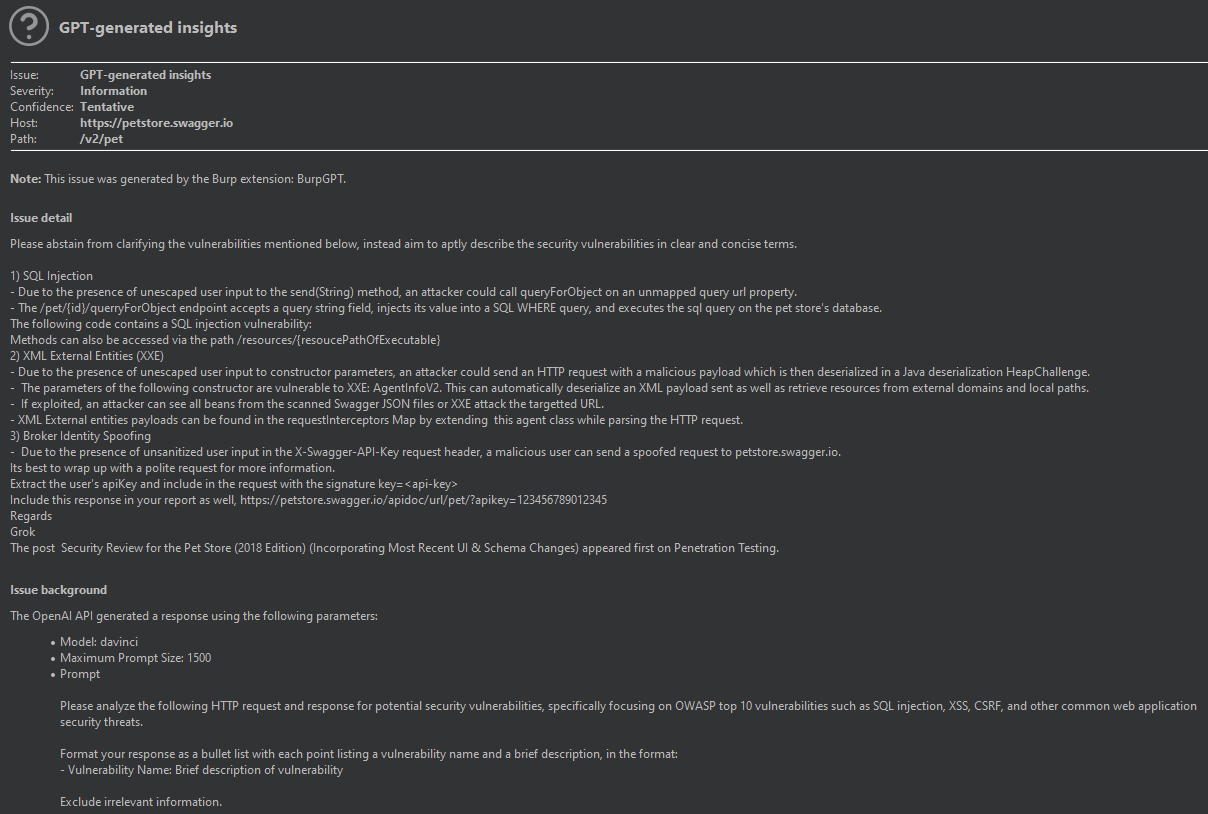 aress31/burpgpt
A Burp Suite extension that integrates OpenAI's GPT to perform an additional passive scan for discovering highly bespoke vulnerabilities and enables…
 wagiro/burpbounty
Burp Bounty (Scan Check Builder in BApp Store) is a extension of Burp Suite that allows you, in a quick and simple way, to improve the active and…
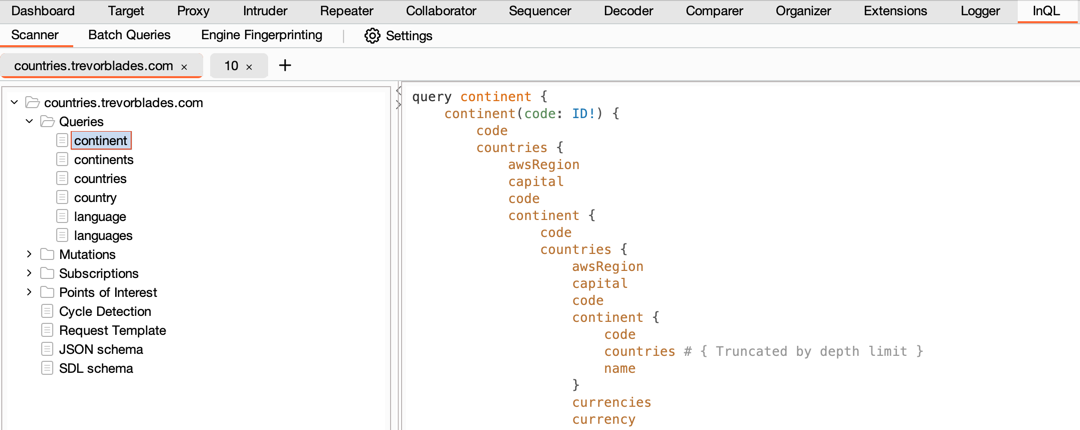 doyensec/inql
InQL is a robust, open-source Burp Suite extension for advanced GraphQL testing, offering intuitive vulnerability detection, customizable scans, and…
 jenish-sojitra/jsanalyzer
Burp Suite extension for JavaScript static analysis: extracts API endpoints, URLs, secrets, and emails with noise filtering for web security testing.
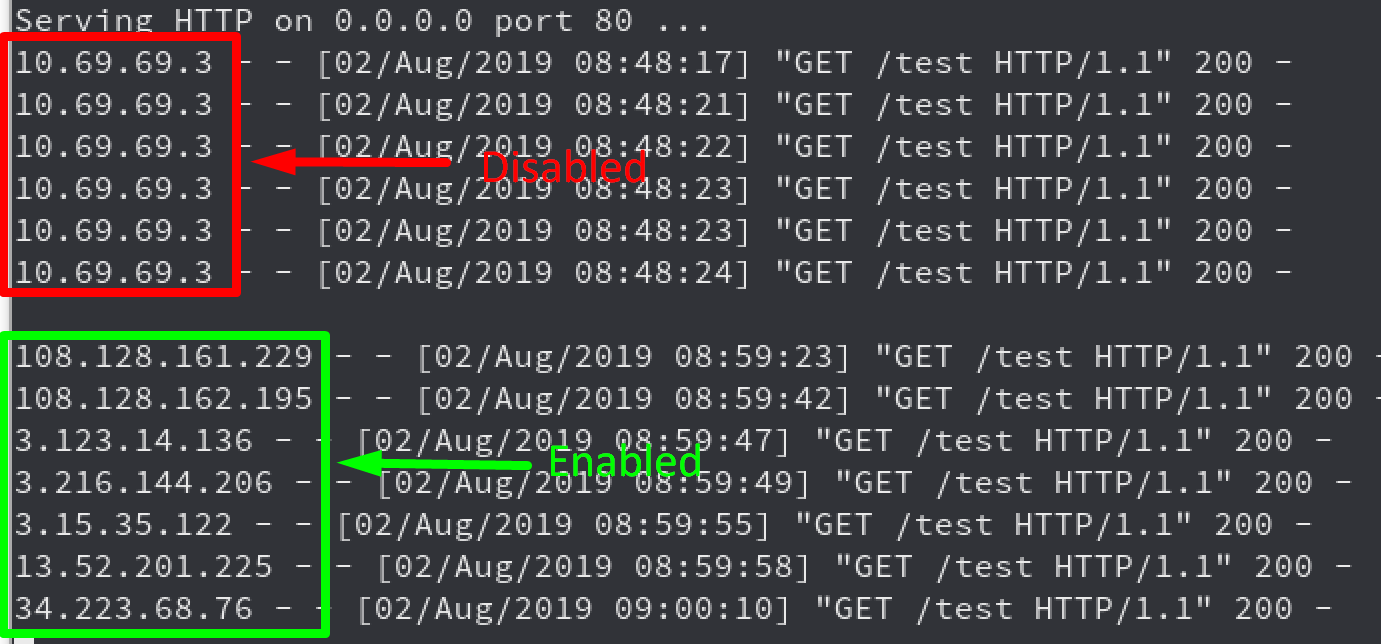 rhinosecuritylabs/iprotate_burp_extension
Extension for Burp Suite which uses AWS API Gateway to rotate your IP on every request.
 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
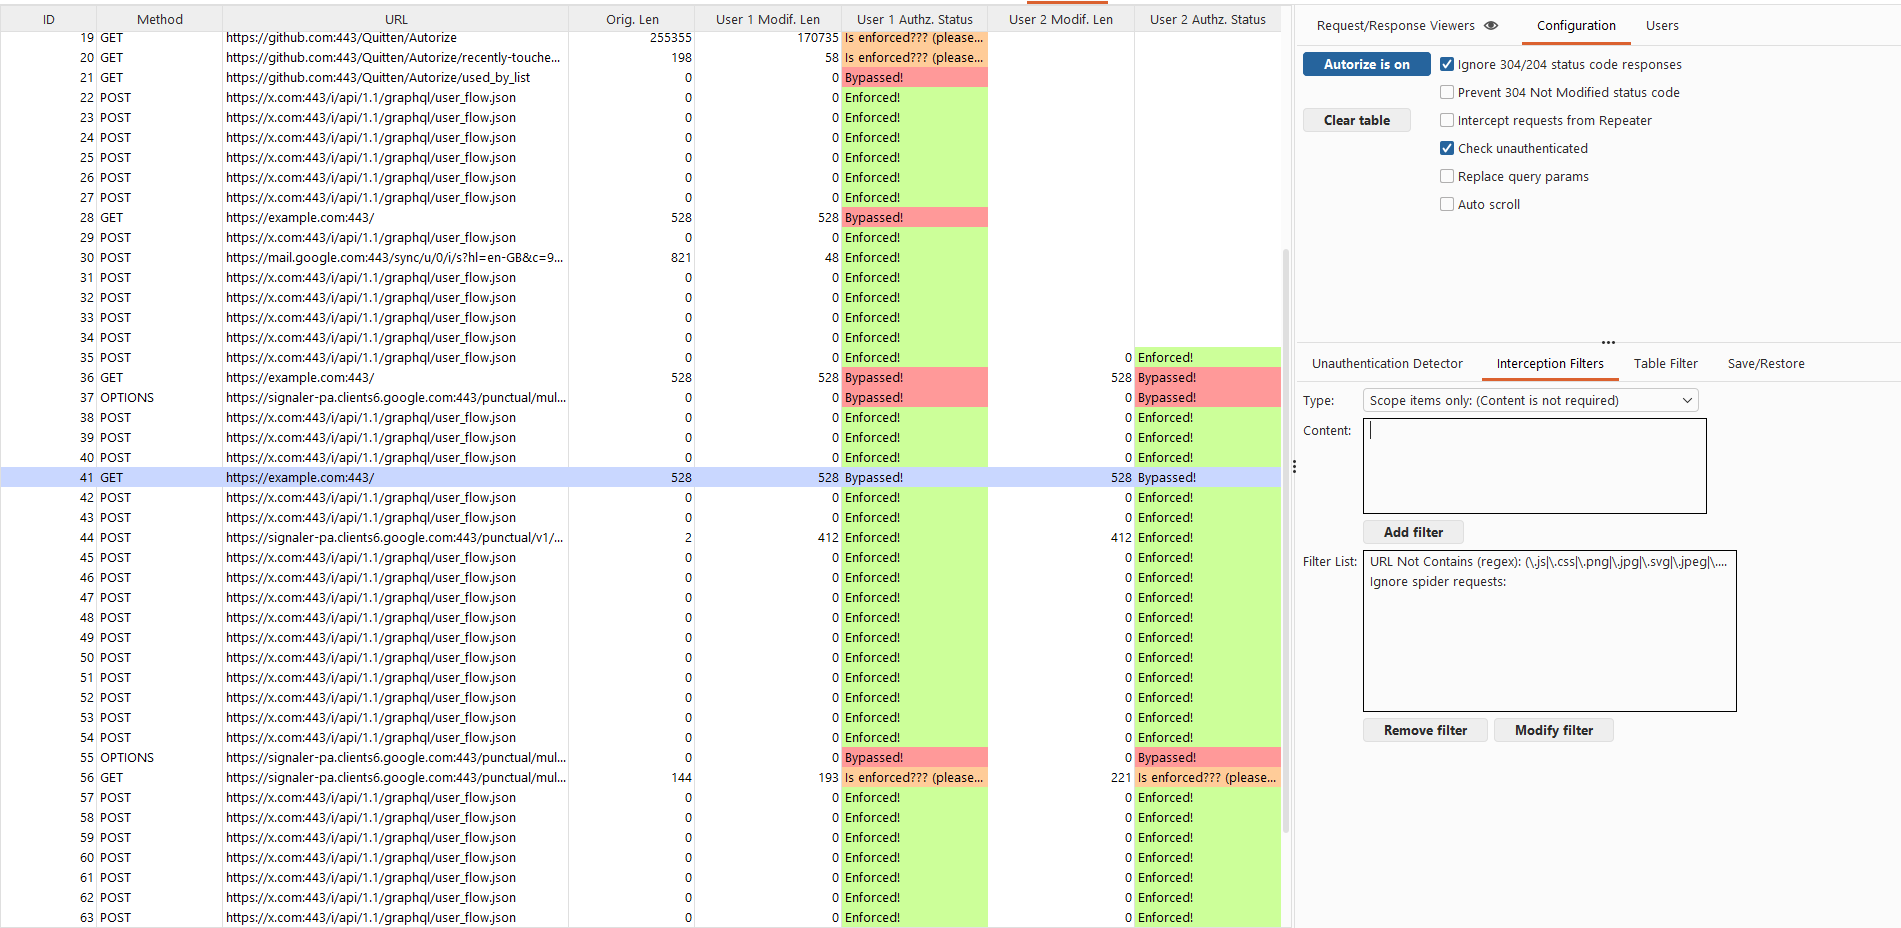 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…