

 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 presentdaypresenttime/shai_hulud
Worm written in python, abuses CVE-2020-7247
 cappricio-securities/socialengineering
SEt framework
 jacobtaylor3/cve-2021-21220
Browser-based CVE-2021-21220 exploit delivering a reverse shell via shellcode and a C2 implant for remote command execution on Windows targets.
 zhulin837/checkmk_cve-2024-0670
Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
 restdone/cve-2024-31771
Proof-of-concept exploit for CVE-2024-31771 demonstrating arbitrary file write in TotalAV via symbolic link attack, enabling DLL planting and SYSTEM…
 ianxtianxt/ssocks-0.0.14
SOCKS proxy for port forwarding and RDP tunneling, enabling lateral movement and remote access in penetration testing scenarios.
 fengzhouc/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, demonstrating remote code execution via malicious git repository cloning with symlink and filter abuse…
 trailer2/dll-planting-slack-4.33.73-cve-2023-38820
DLL Planting in the Slack 4.33.73 - CVE-2023-38820
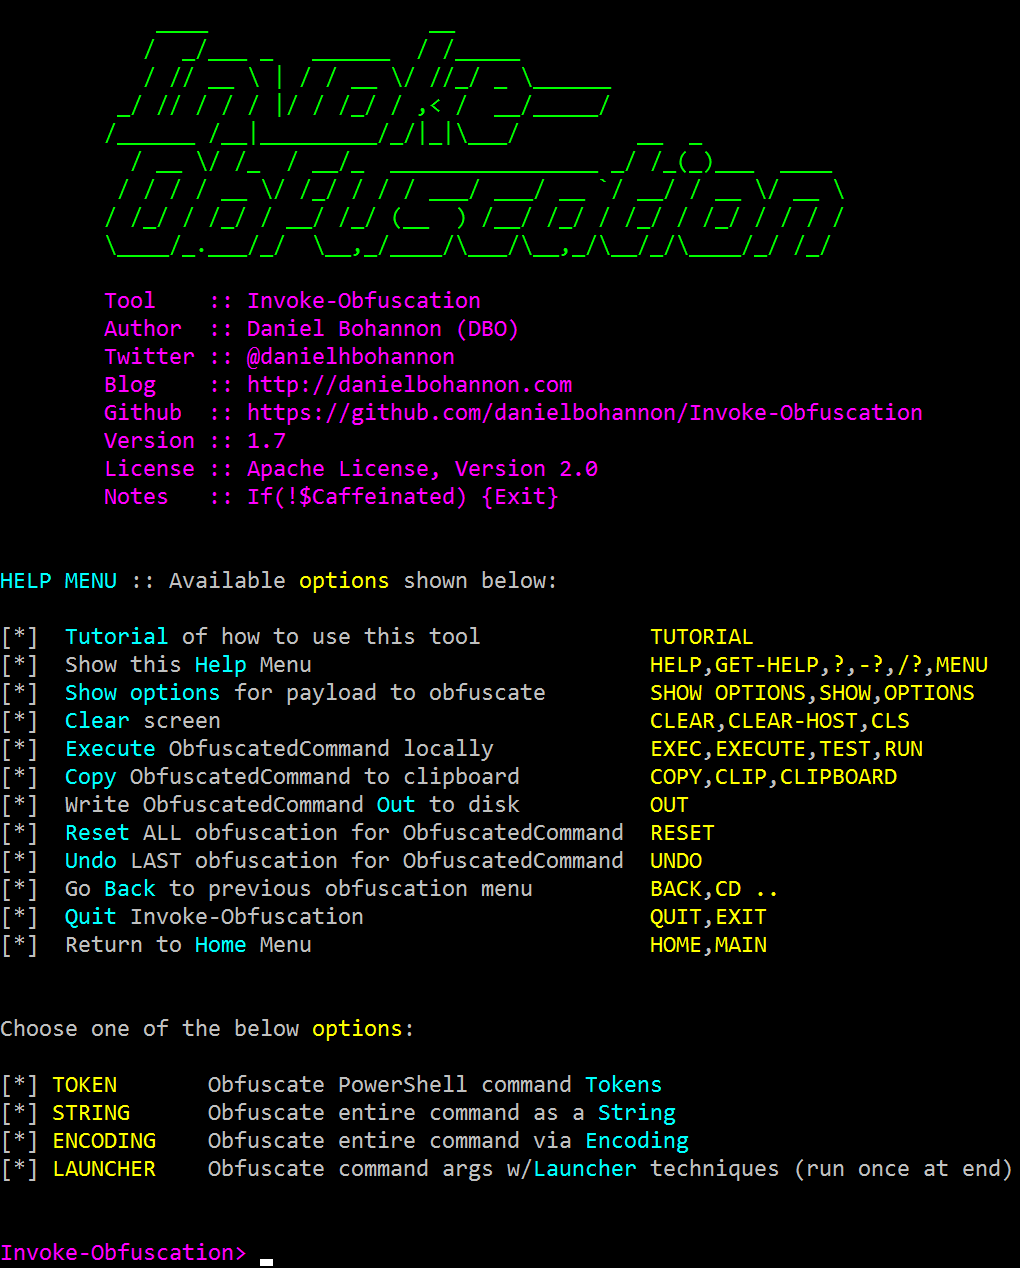 empireproject/empire
Empire is a PowerShell and Python post-exploitation agent.
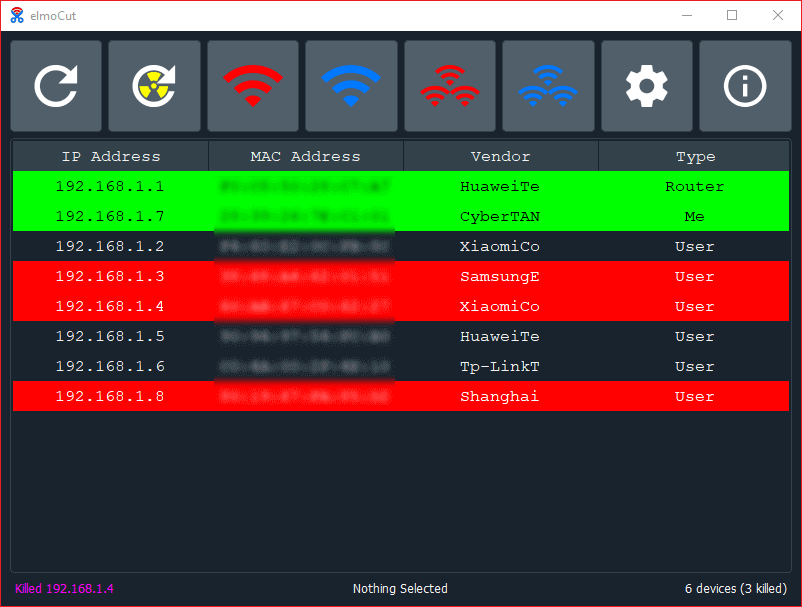 elmoiv/elmocut
Eye candy ARP spoofer for Windows
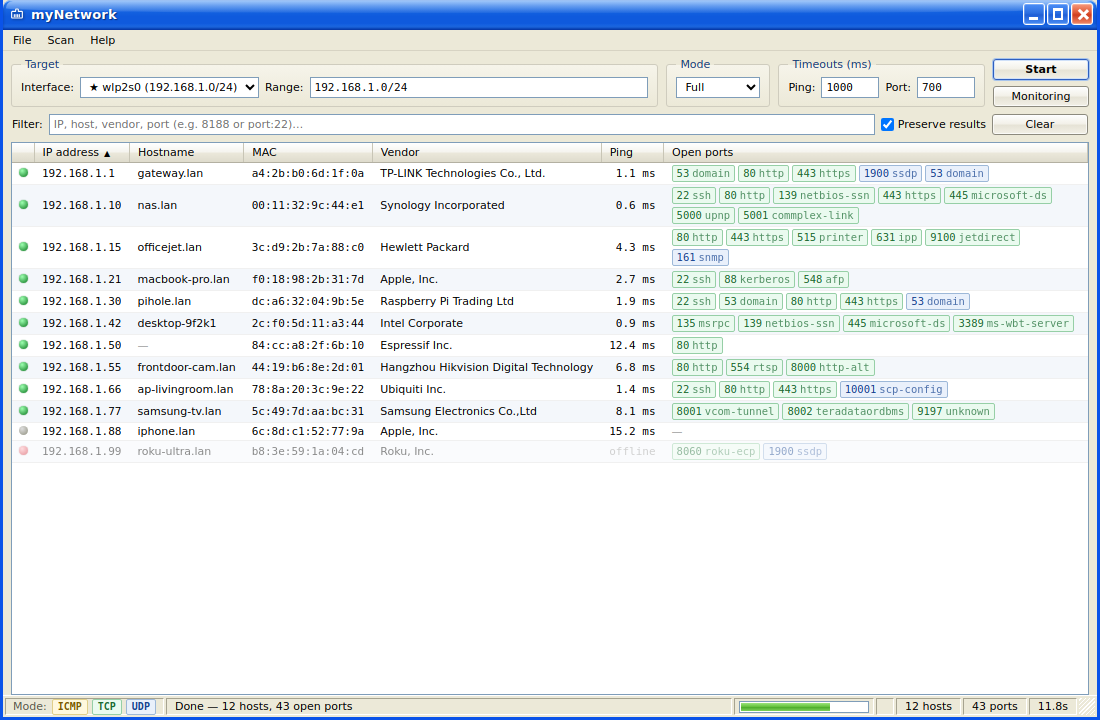 ancaferro/mynetwork
Cross-platform network & port scanner with a desktop GUI.
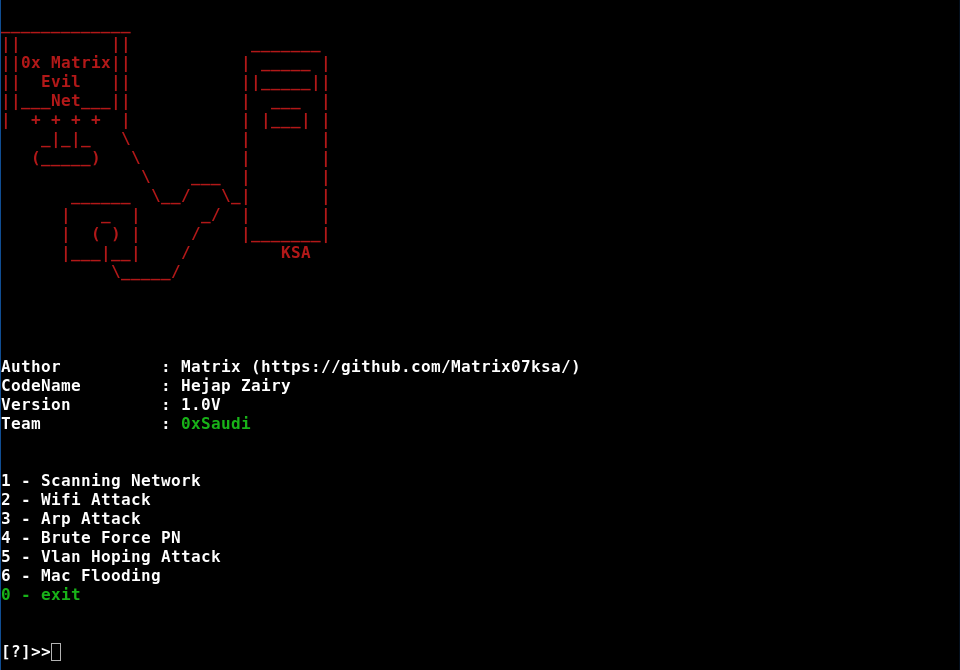 matrix07ksa/evilnet
Network Attack wifi attack vlan attack arp attack Mac Attack Attack revealed etc../
 mustafadalga/arp-poisoning-packet-sniffer
Aynı ağda bulunan hedef bilgisayarlar üzerinde ARP zehirlemesi(poisoning) yapmak ve ağ trafiğini izlemenizi sağlamak için yazılmış iki scripttir.
 fa1dz/internet-scanner
A Tkinter GUI that scans a local IPv4 network (ARP + nmap probing), shows devices, lets you run full port scans, and export results.