
Archived
CrowdFMS
 crowdstrike/crowdfms
CrowdStrike Feed Management System. CrowdFMS is a framework for automating collection and processing of samples from VirusTotal, by leveraging the…
api-securitydynamic-analysis-sandboxingmalware-analysis+1
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 mitre/caldera-crater
C# remote access trojan (RAT) implant for the Caldera adversary emulation framework, enabling post-exploitation command and control on Windows…
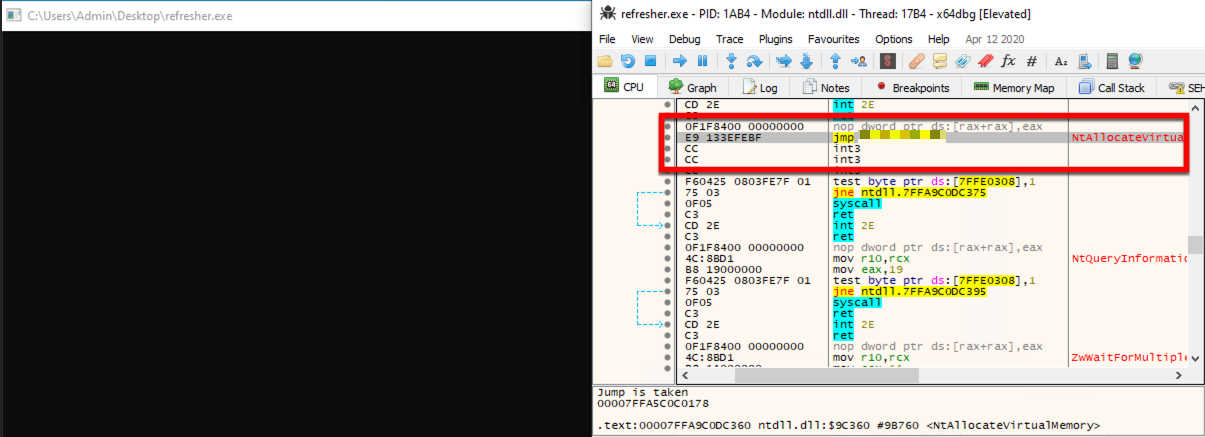 optiv/scarecrow
ScareCrow - Payload creation framework designed around EDR bypass.
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 optiv/ivy
Ivy is a payload creation framework for the execution of arbitrary VBA (macro) source code directly in memory. Ivy’s loader does this by utilizing…
 didi/kemon
An Open-Source Pre and Post Callback-Based Framework for macOS Kernel Monitoring.
 dobin/antnium
A C2 framework for initial access in Go
 carpedm20/awesome-hacking
A curated list of awesome Hacking tutorials, tools and resources
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
 hamed233/cybersecurity-mastery-roadmap
A comprehensive, step-by-step guide to mastering cybersecurity from beginner to expert level with curated resources, tools, and career guidance
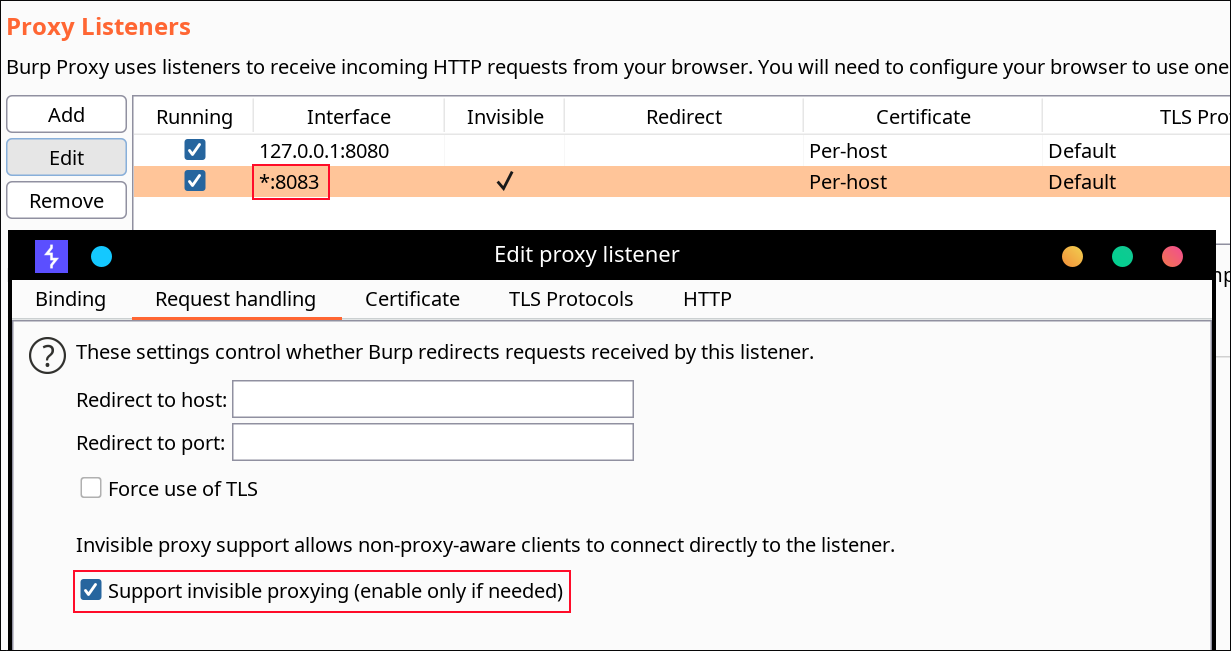 impact-i/reflutter
Patches Flutter engine libraries to enable runtime reverse engineering, traffic interception, and SSL pinning bypass for Android and iOS apps without…
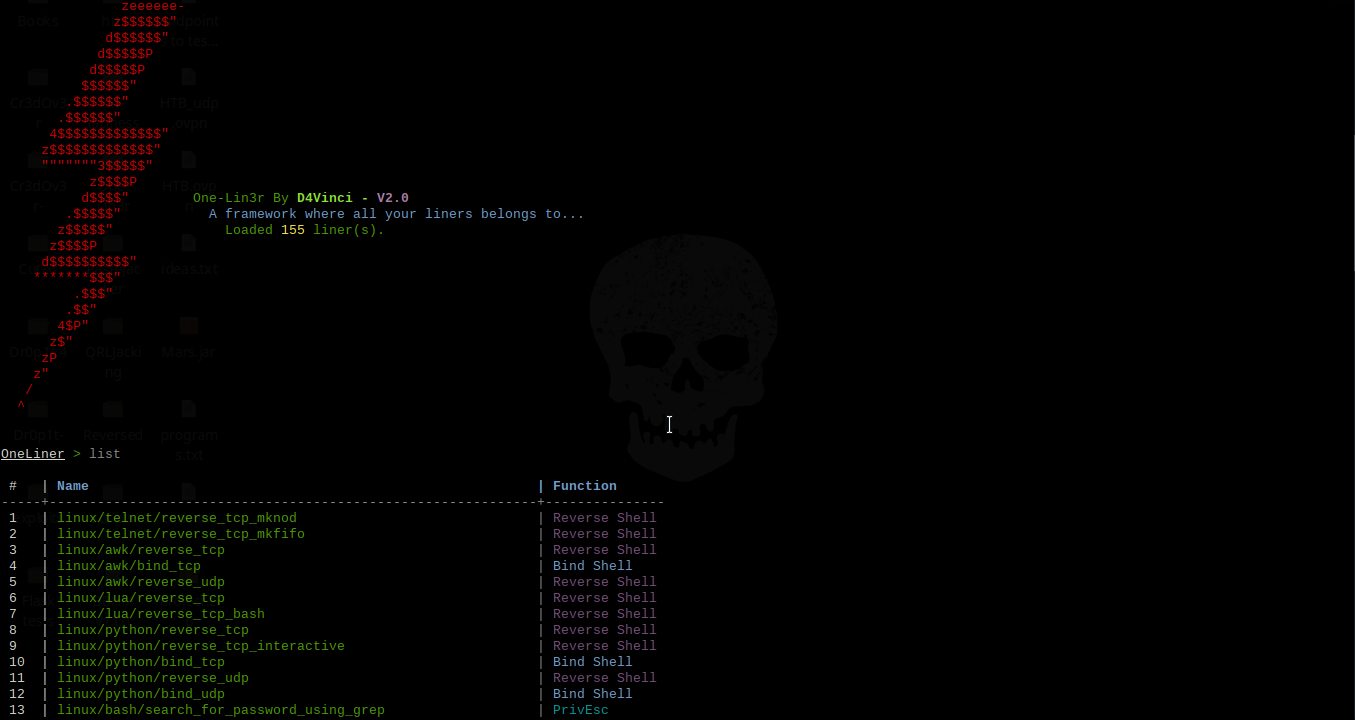 d4vinci/one-lin3r
Gives you one-liners that aids in penetration testing operations, privilege escalation and more
 darkr4y/geacon
Practice Go programming and implement CobaltStrike's Beacon in Go
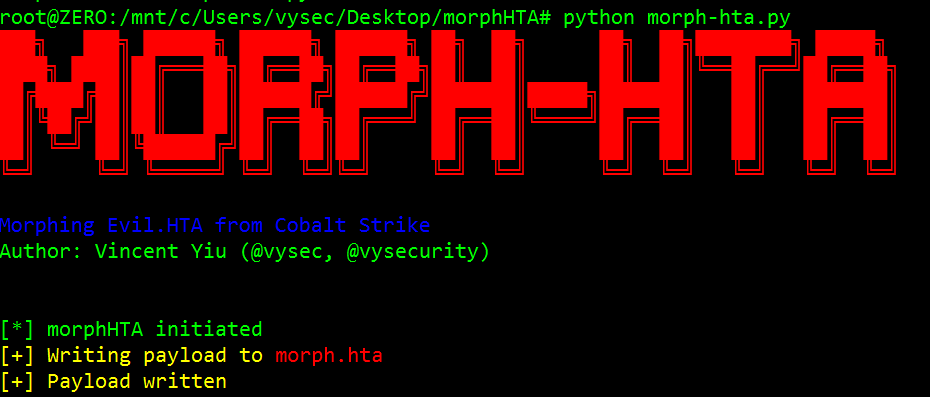 vysecurity/morphhta
morphHTA - Morphing Cobalt Strike's evil.HTA
 treehacks/botnet-hackpack
Build a basic Command & Control botnet in C
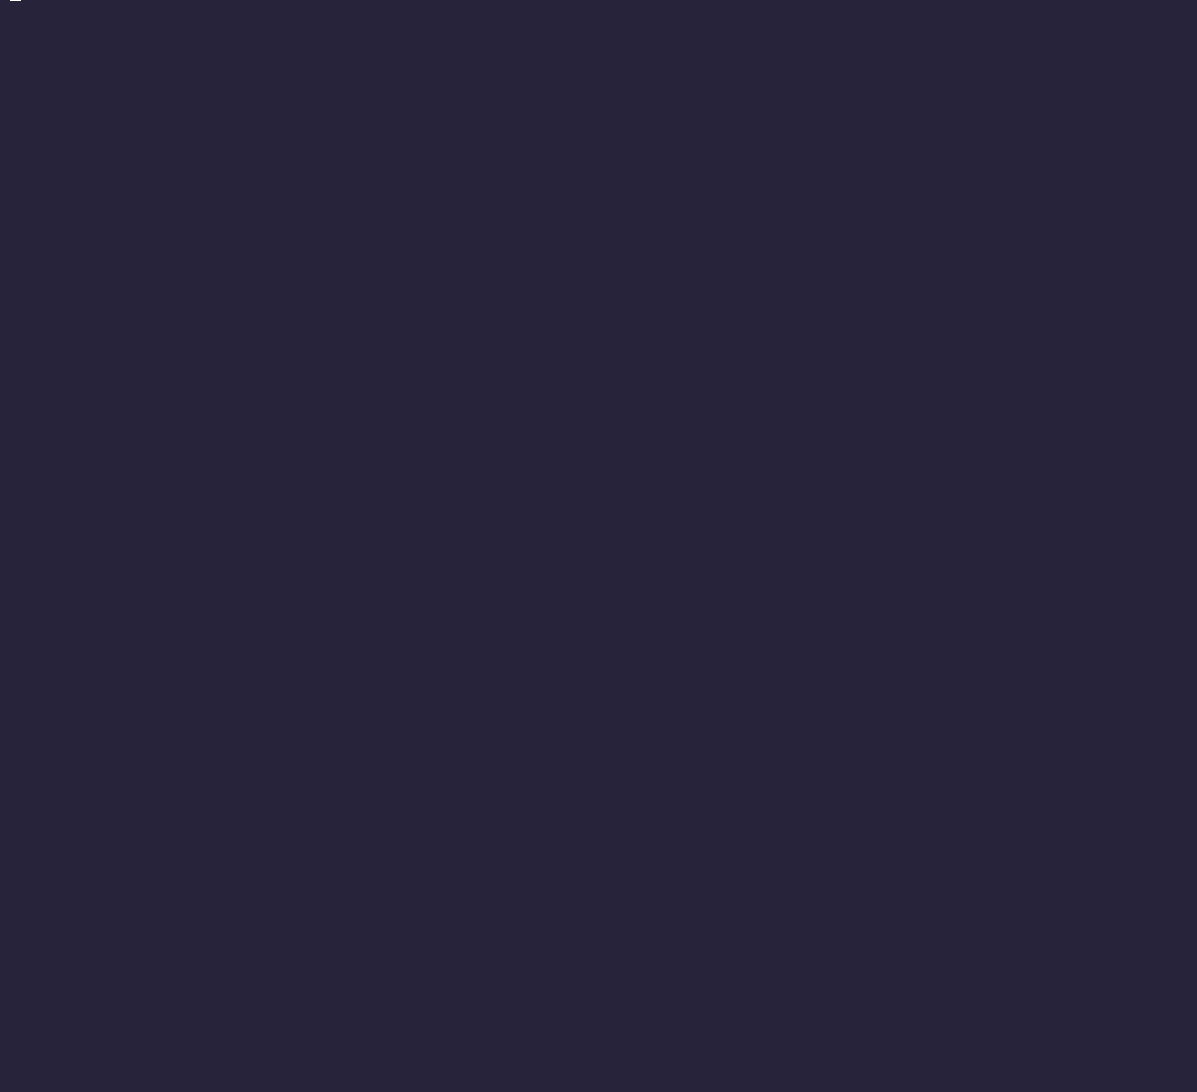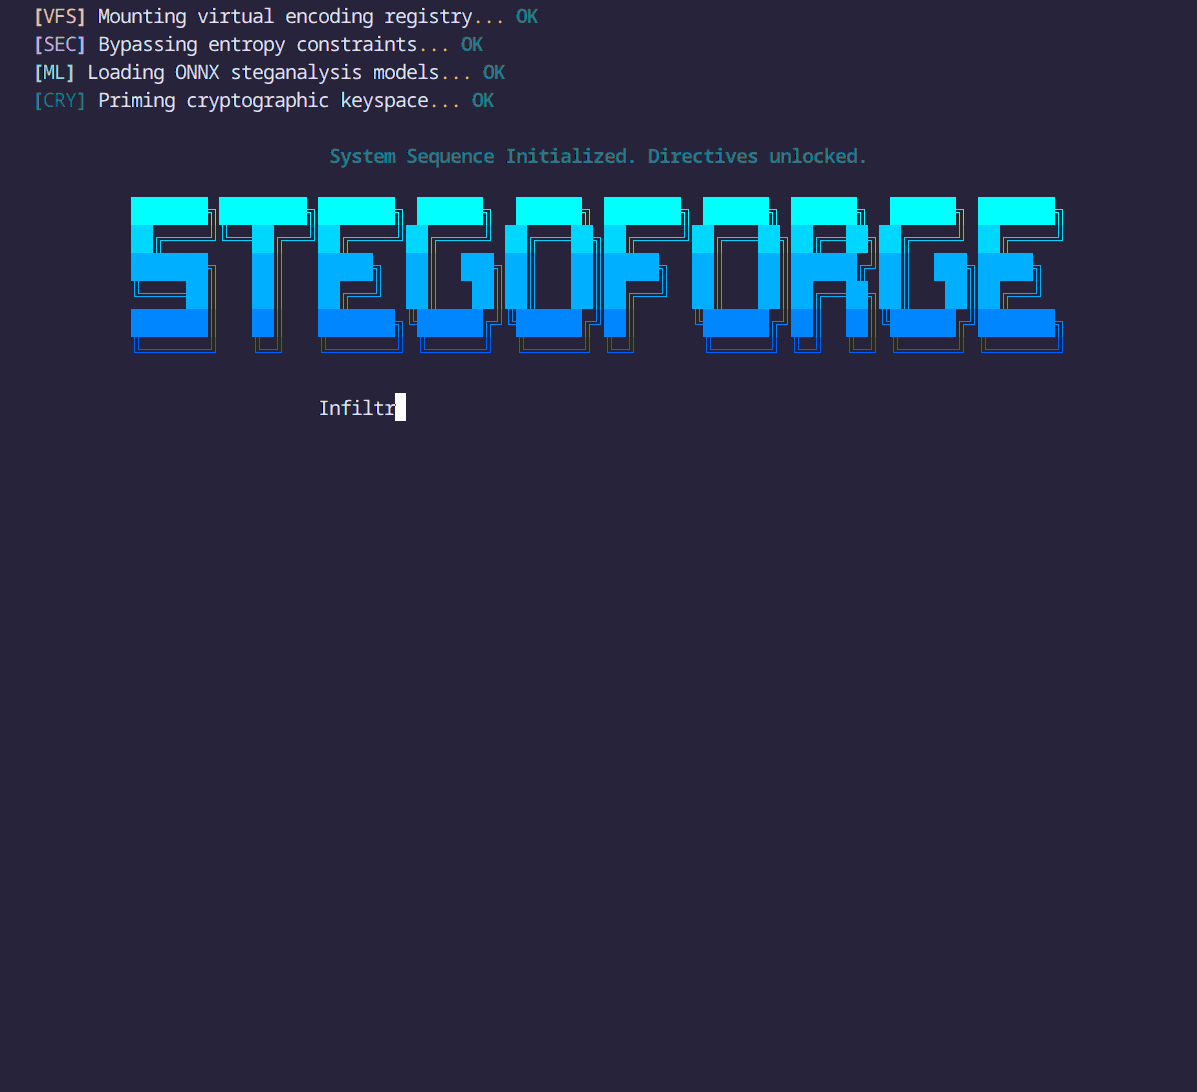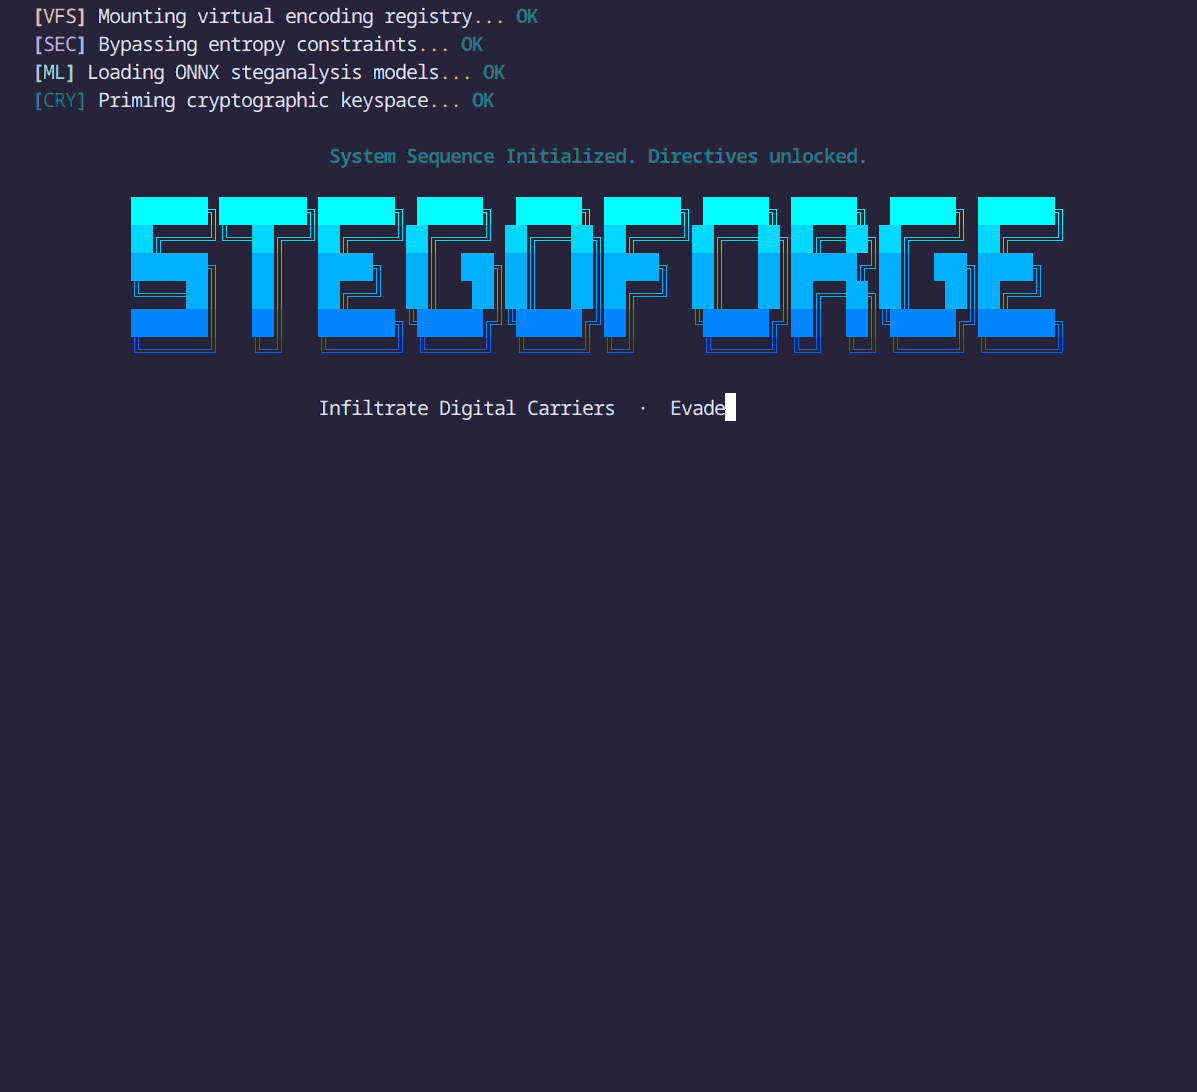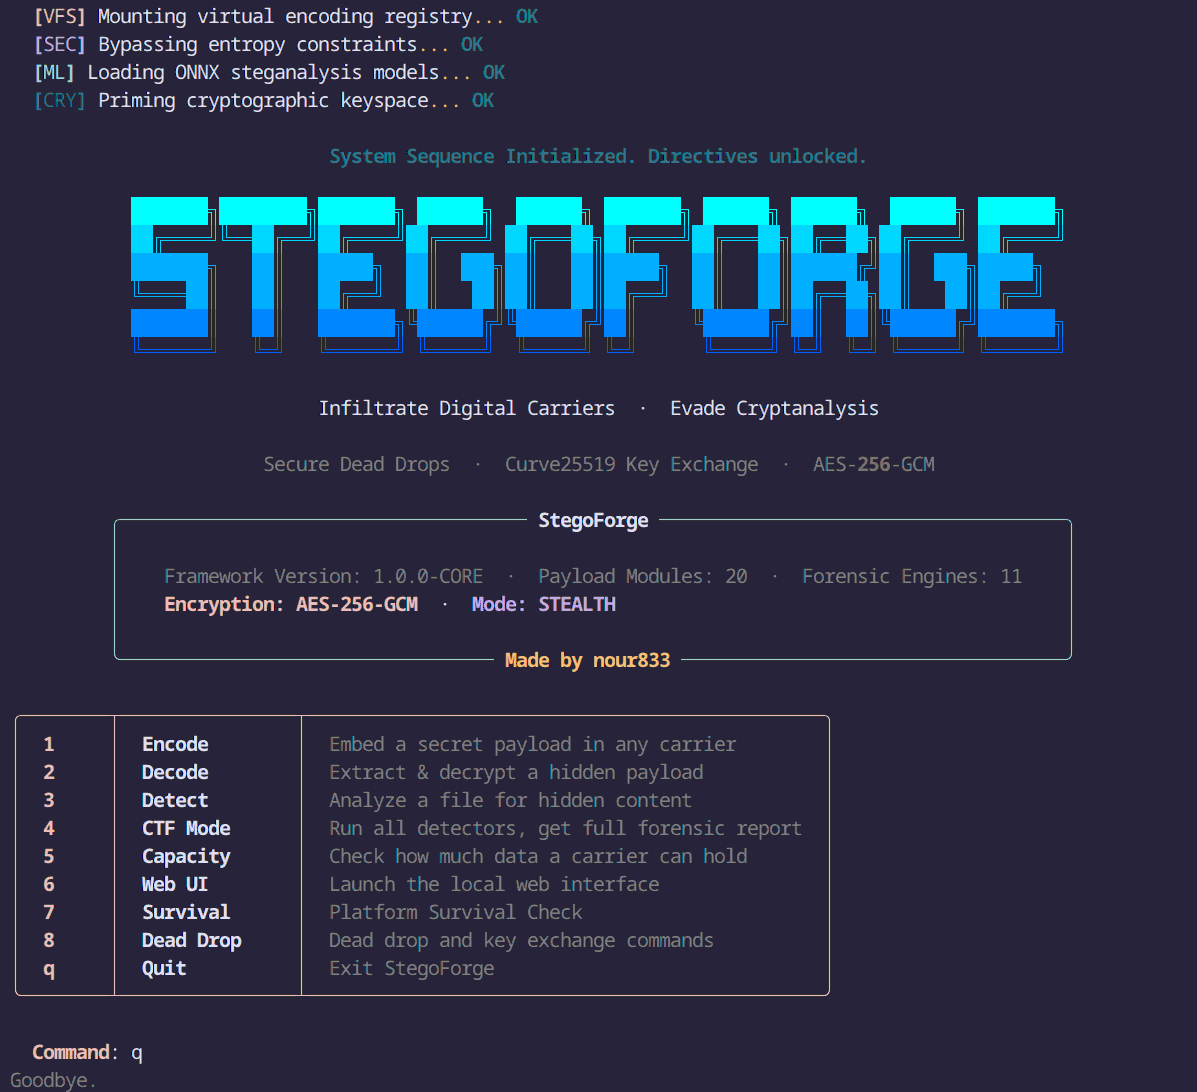 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…