disclosure-thinkware-u3000

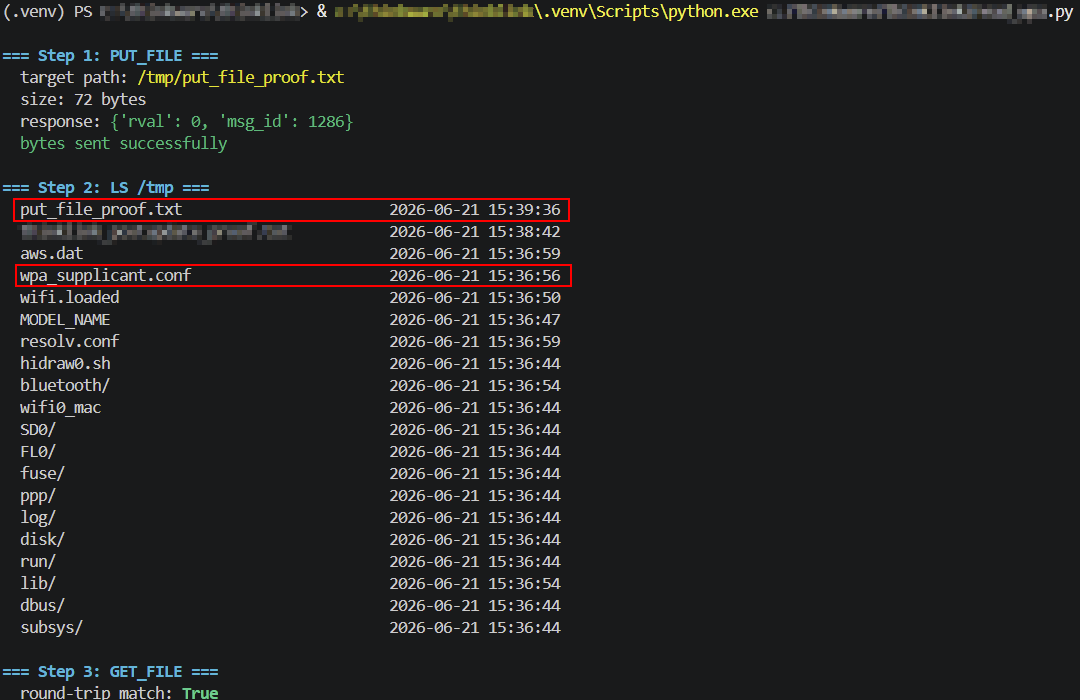
Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…

Three unauthenticated vulnerabilities in the Thinkware U3000 dashcam's local WiFi control protocol: arbitrary file write, arbitrary file read, and…

Nethugging client for Android, from wigle.net

Automatically exported from code.google.com/p/fern-wifi-cracker

Remote buffer overflow over wifi_stack in wpa_supplicant binary in android 11, platform:samsung a20e, stock options so like works out of the box

POC for CVE-2021-35448 based on https://www.exploit-db.com/exploits/49601

This repo has a blog post about my analysis for CVE-2018-19987 an authenticated OS command injection affecting multiple D-Link routers

Github mirror of official Kismet repository

A dope AF repo of all customized plugins & configurations I use as seen on my socials / YouTube. Helpful guides and troubleshooting too.

Repositorio del equipo T1GR3$ en el hackathon de Cybercamp 2018

macOS menu bar app that detects and prevents wireless bridging attacks by automatically disabling the AirPort module when Ethernet connectivity is…

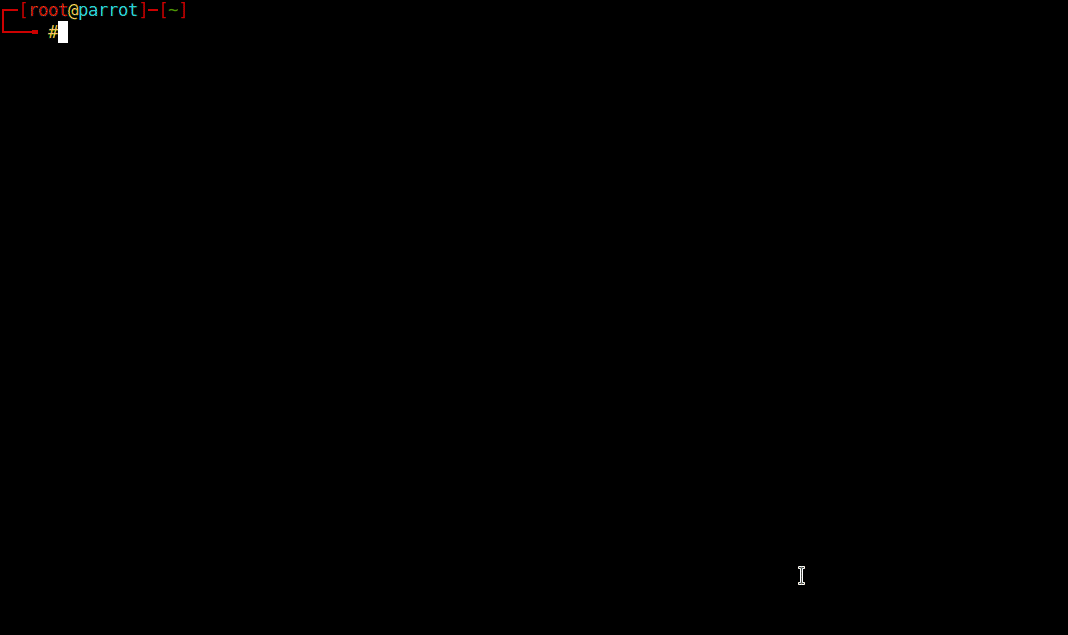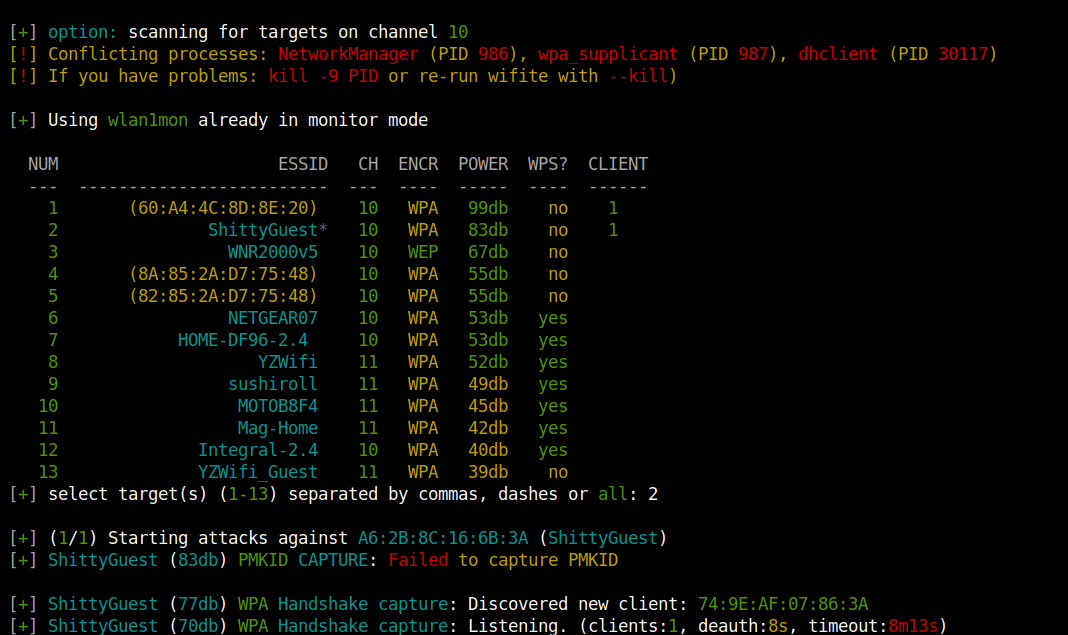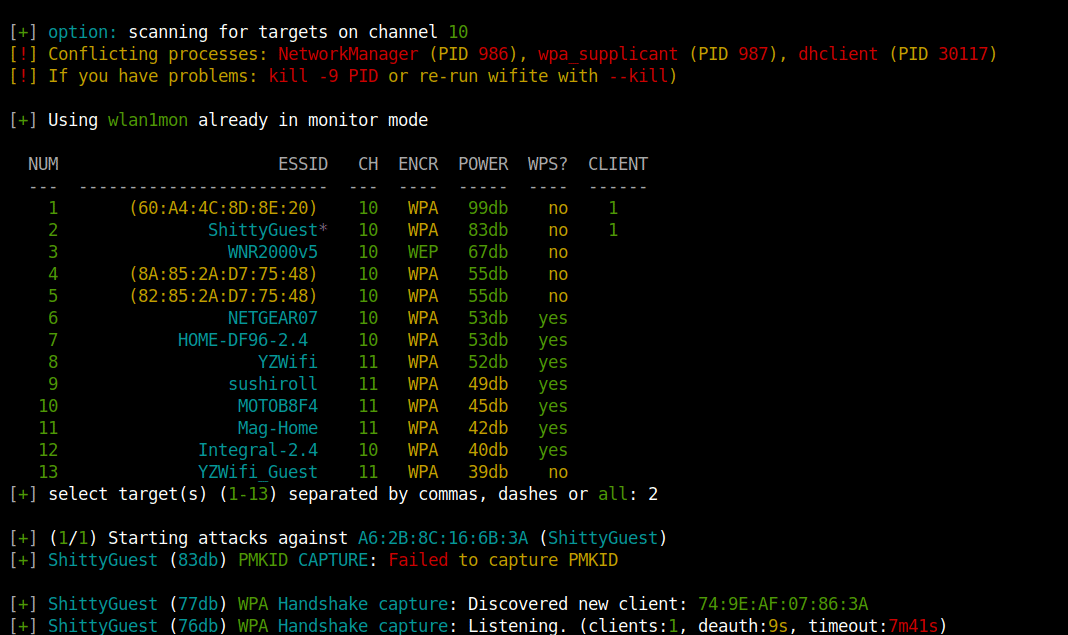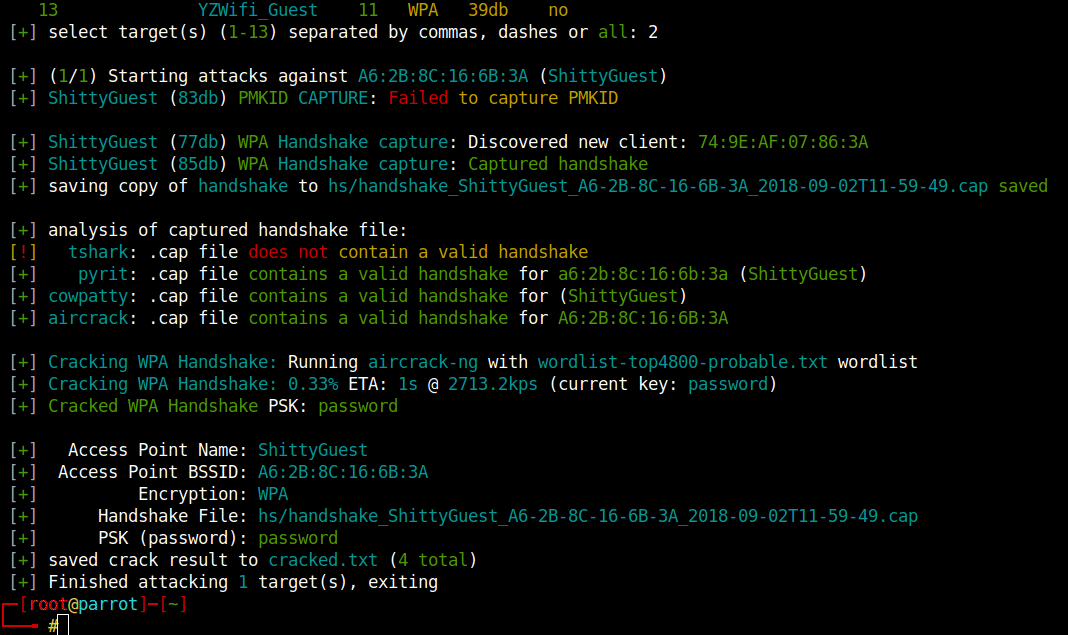
Rewrite of the popular wireless network auditor, "wifite"

Shell Script For Attacking Wireless Connections Using Built-In Kali Tools. Supports All Securities (WEP, WPS, WPA, WPA2)

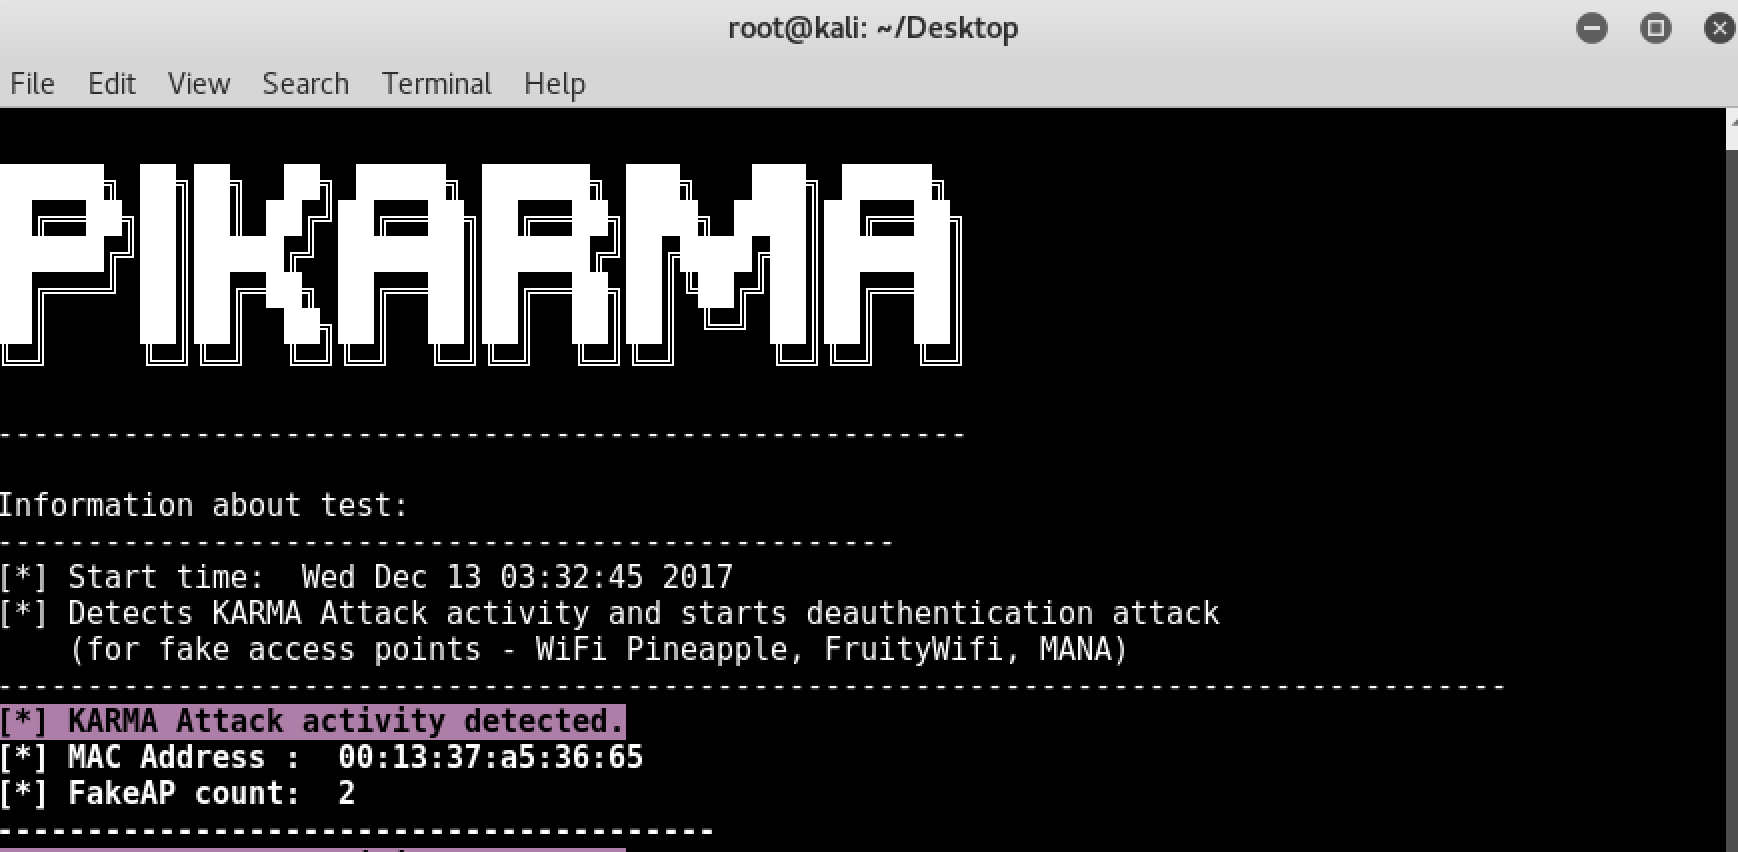
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)

Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.

A suite of WiFi/Bluetooth offensive and defensive tools for the ESP32

ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32