

coraza
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
api-securityapi-security-testingdefensive-tools+7
3.8k
corazawaf/corazaGo-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 enablesecurity/wafw00f
Automated Web Application Firewall fingerprinting tool that identifies and detects over 200 WAF products by analyzing HTTP responses to normal and…
 hakluke/hakrawler
Simple, fast web crawler designed for easy, quick discovery of endpoints and assets within a web application
 jaeles-project/jaeles
The Swiss Army knife for automated Web Application Testing
 codingo/nosqlmap
Automated NoSQL database enumeration and web application exploitation tool.
 xalgord/massive-web-application-penetration-testing-bug-bounty-notes
A comprehensive guide for web application penetration testing and bug bounty hunting, covering methodologies, tools, and resources for identifying…
 nccgroup/abptts
TCP tunneling over HTTP/HTTPS for web application servers
 christophetd/log4shell-vulnerable-app
Spring Boot web application vulnerable to Log4Shell (CVE-2021-44228).
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
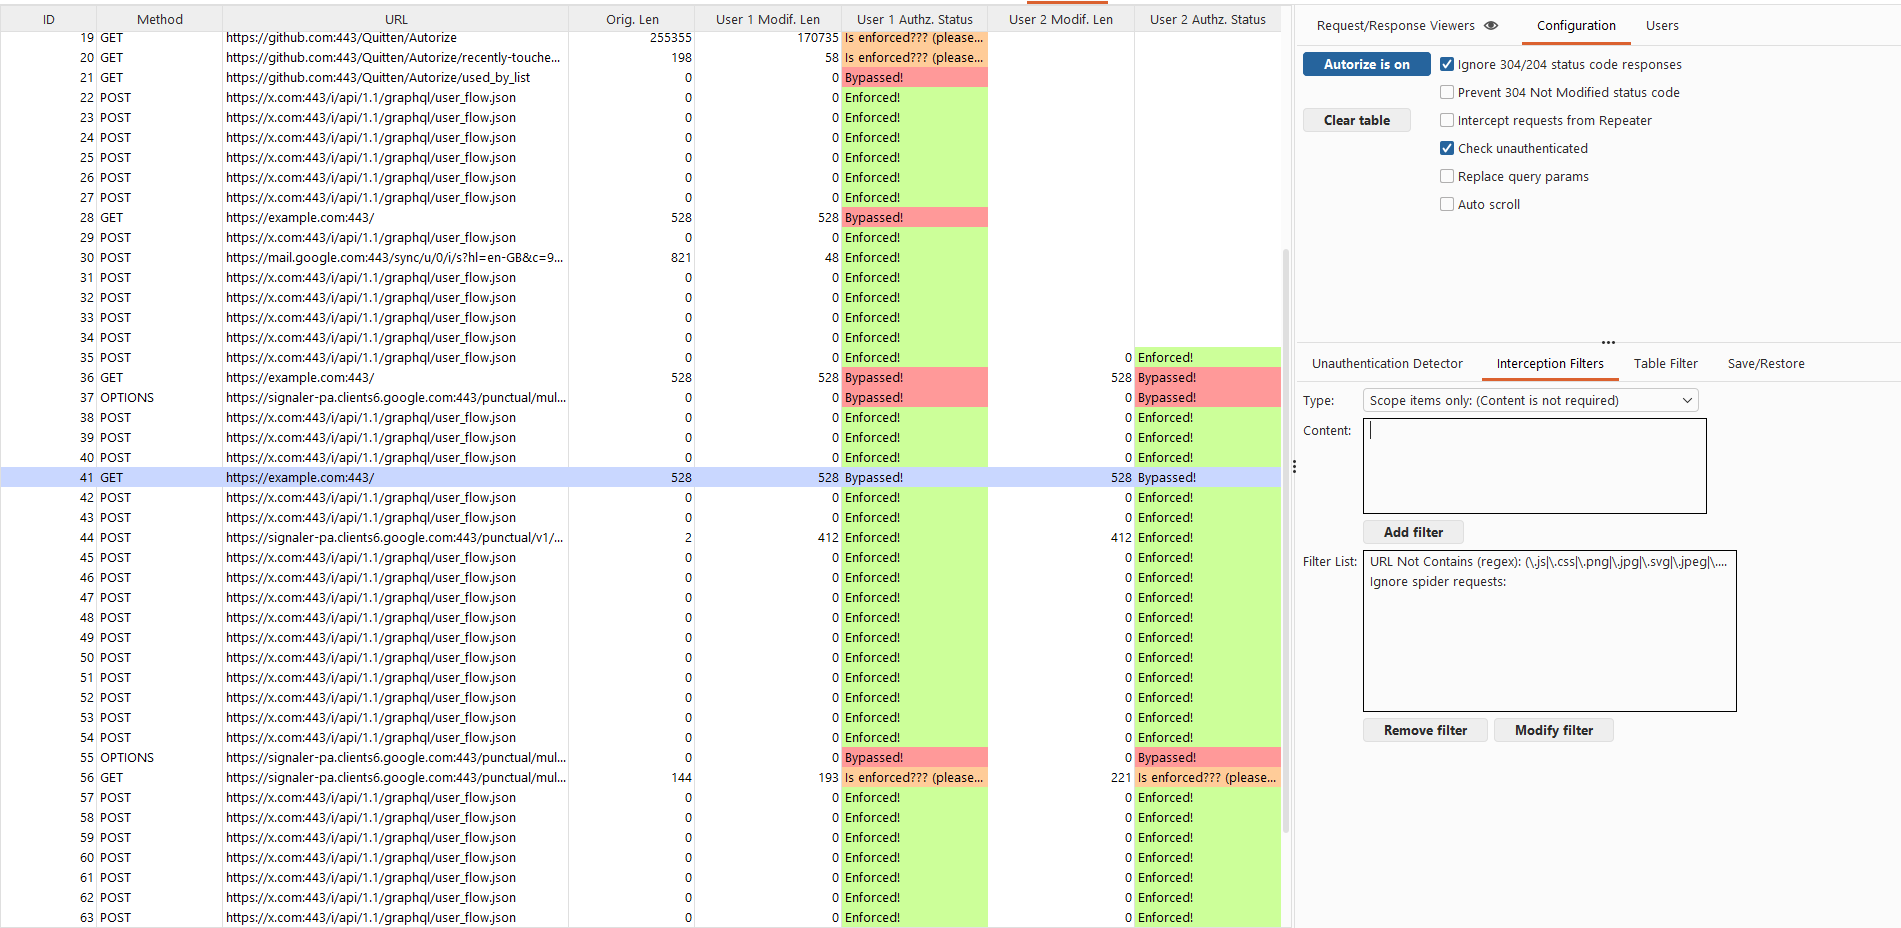 quitten/autorize
Automatic authorization enforcement detection extension for burp suite written in Jython developed by Barak Tawily in order to ease application…
 chrislockard/api_wordlist
A wordlist of API names for web application assessments
 hxsecurity/dongtai
Open-source Interactive Application Security Testing (IAST) tool that passively instruments Java applications to detect vulnerabilities and…
 cisagov/decider
A web application that assists network defenders, analysts, and researchers in the process of mapping adversary behaviors to the MITRE ATT&CK®…
 waf-bypass-maker/waf-community-bypasses
Curated CSV collection of community-sourced Web Application Firewall bypass payloads for testing and validating WAF protections.
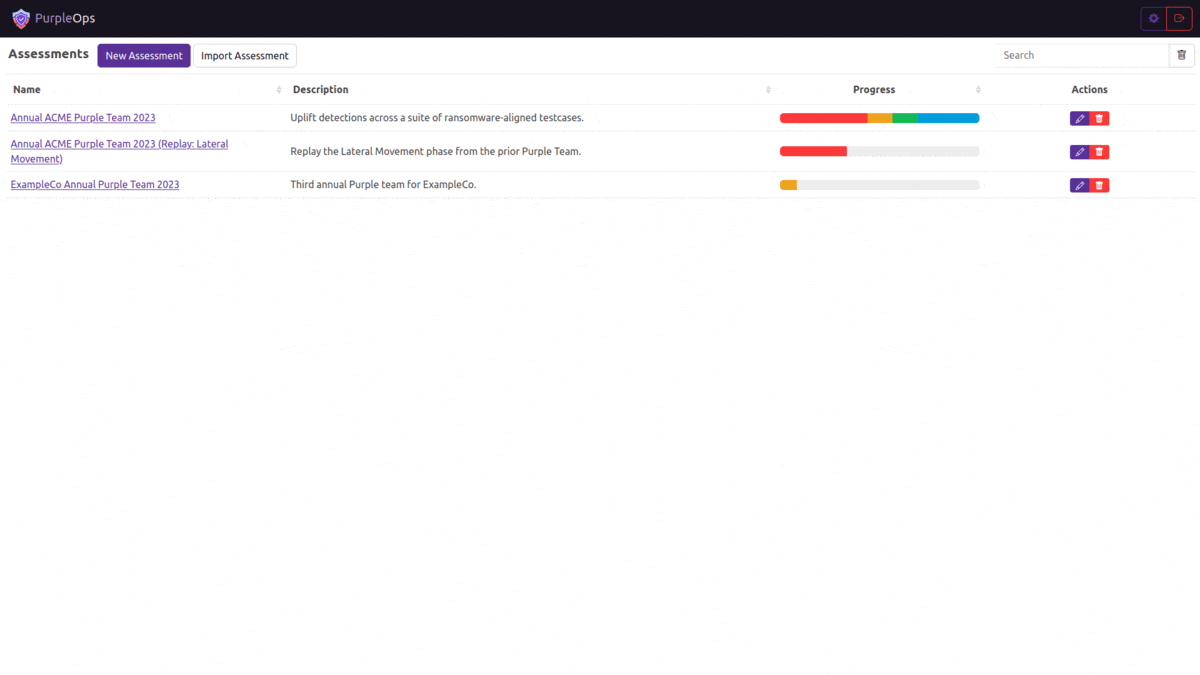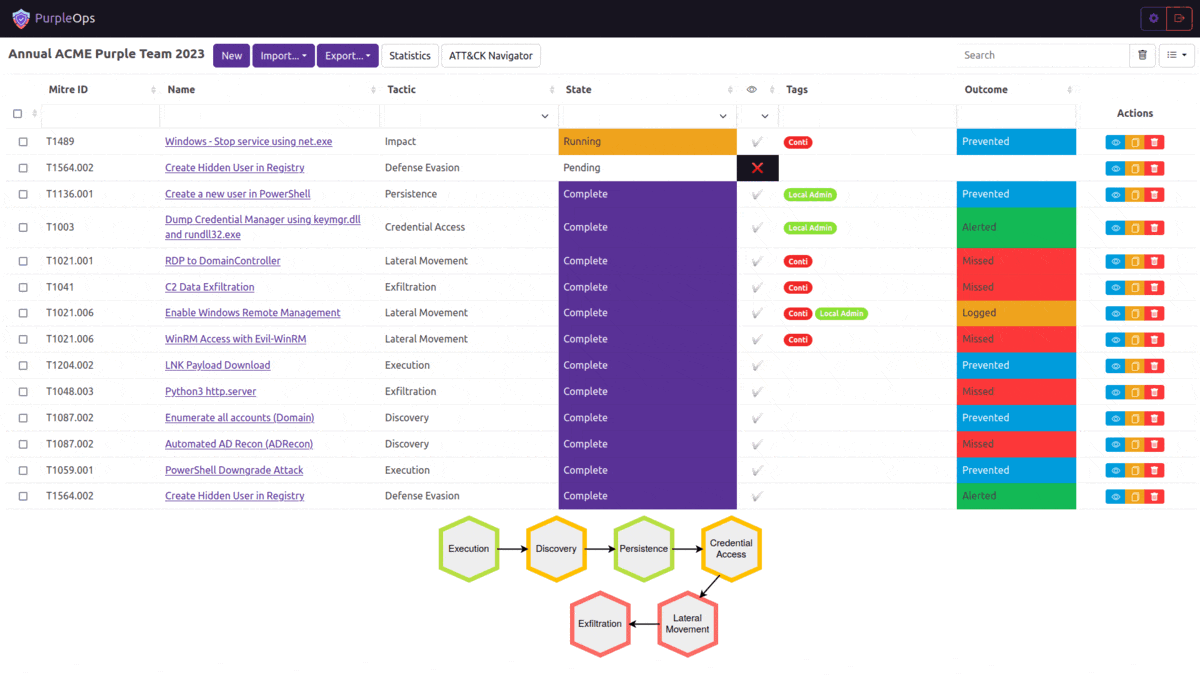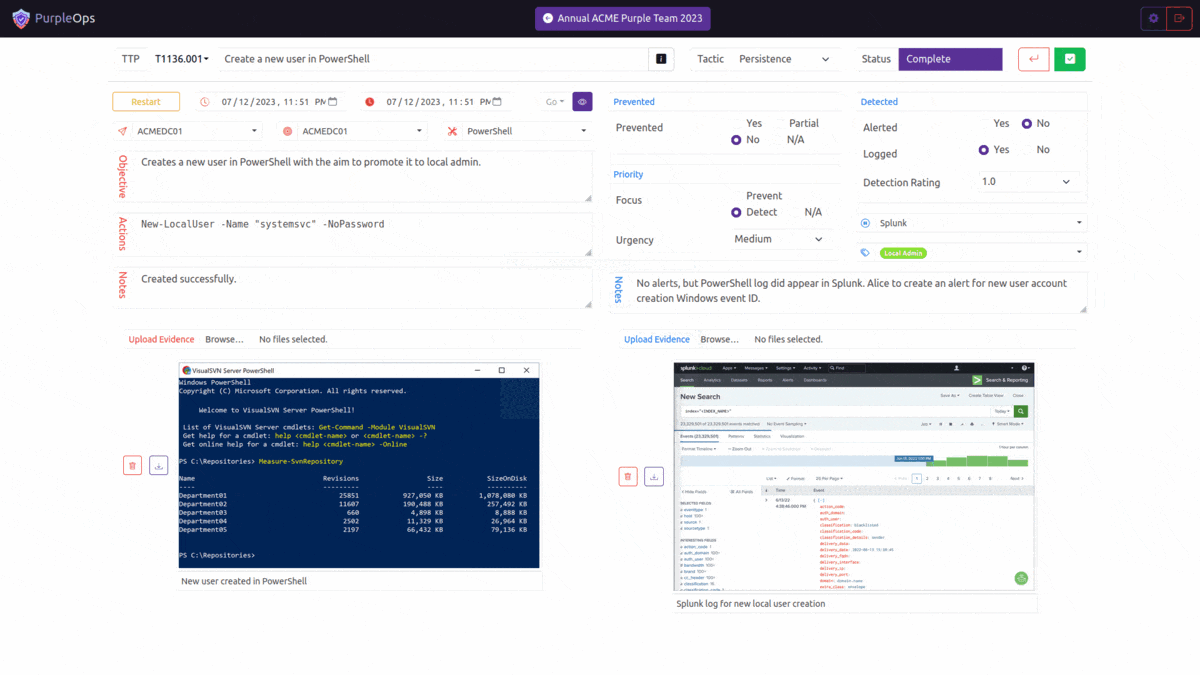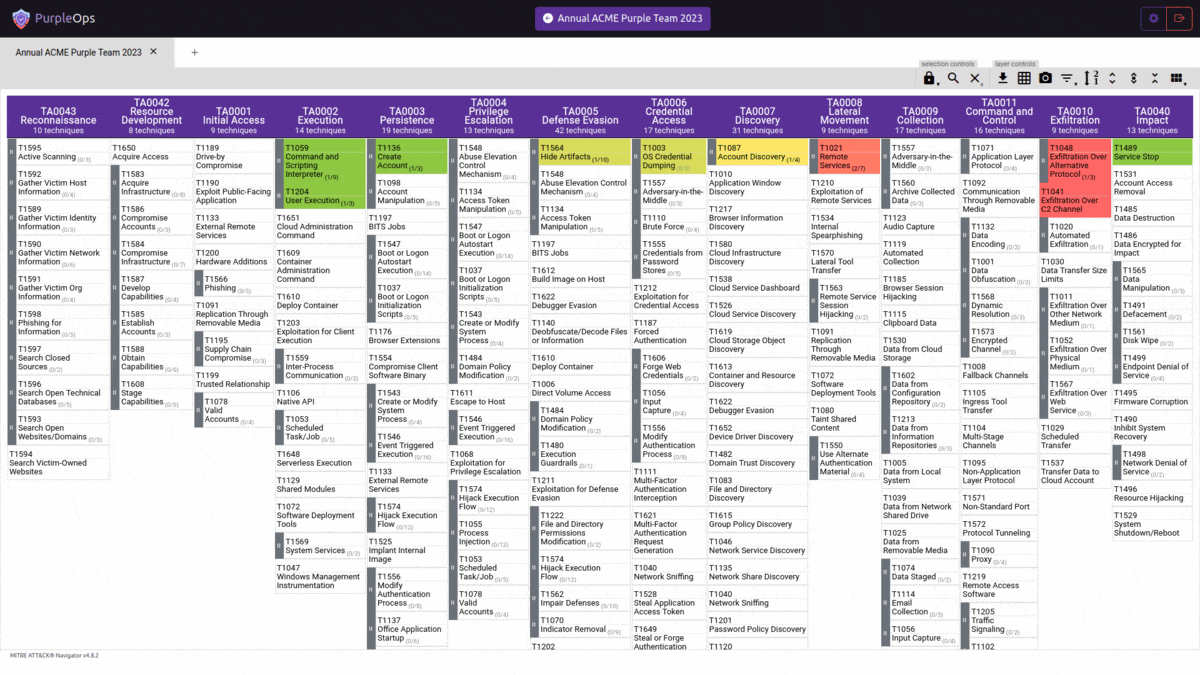 cybercx-sta/purpleops
An open-source self-hosted purple team management web application.
 ritvikb99/dark-fantasy-hack-tool
DDOS Tool: To take down small websites with HTTP FLOOD. Port scanner: To know the open ports of a site. FTP Password Cracker: To hack file system of…
 numencyber/vulnerability_poc
Collection of proof-of-concept exploits and technical analyses for high-impact CVEs, covering browser memory corruption, TCP/IP RCE, and web…
 owasp/honeypot-project
Deploy web honeypots to capture emerging attack data, analyze ModSecurity audit logs via ELK, and share threat intelligence with MISP for…