

CVE-2024-54772
 deauther890/cve-2024-54772
Python-based exploit for CVE-2024-54772 enabling username enumeration on MikroTik RouterOS versions v6.43 through v7.17.2 using wordlist or…
exploitationinformation-gatheringnetwork-security+3
33
deauther890/cve-2024-54772Python-based exploit for CVE-2024-54772 enabling username enumeration on MikroTik RouterOS versions v6.43 through v7.17.2 using wordlist or…
 pixelbubble/pastemonitor
Scrape Pastebin API to collect daily pastes, setup a wordlist and be alerted by email when you have a match.
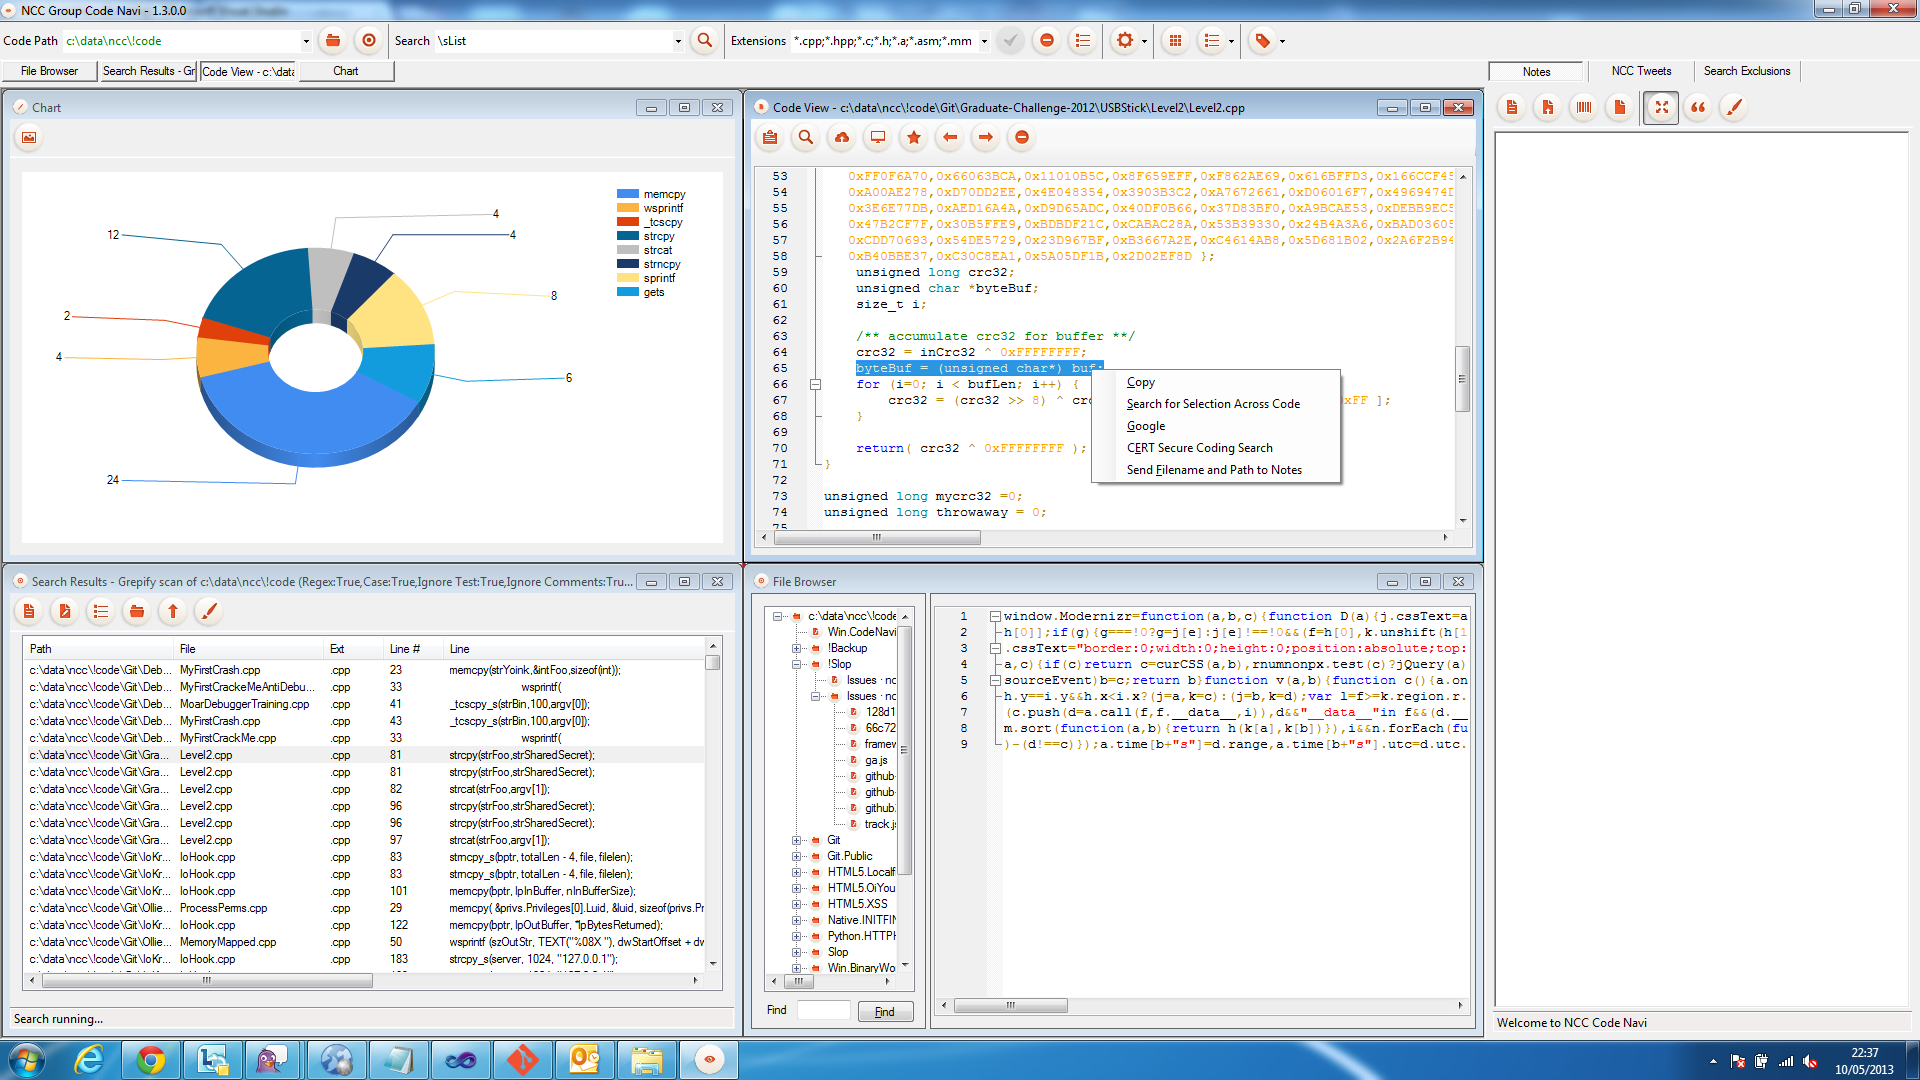 nccgroup/ncccodenavi
NCC Code Navigator
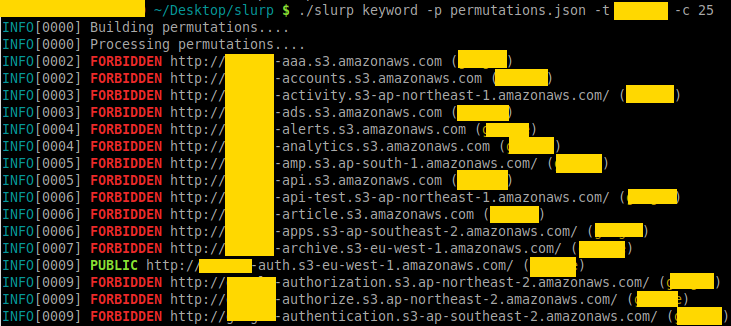
 chaudharyarjun/jwtxposer
An advanced JWT extraction & decoding tool for bug bounty hunters! 🏴☠️
 jsecu/bof-pack-1
A care package of useful bofs for red team engagments
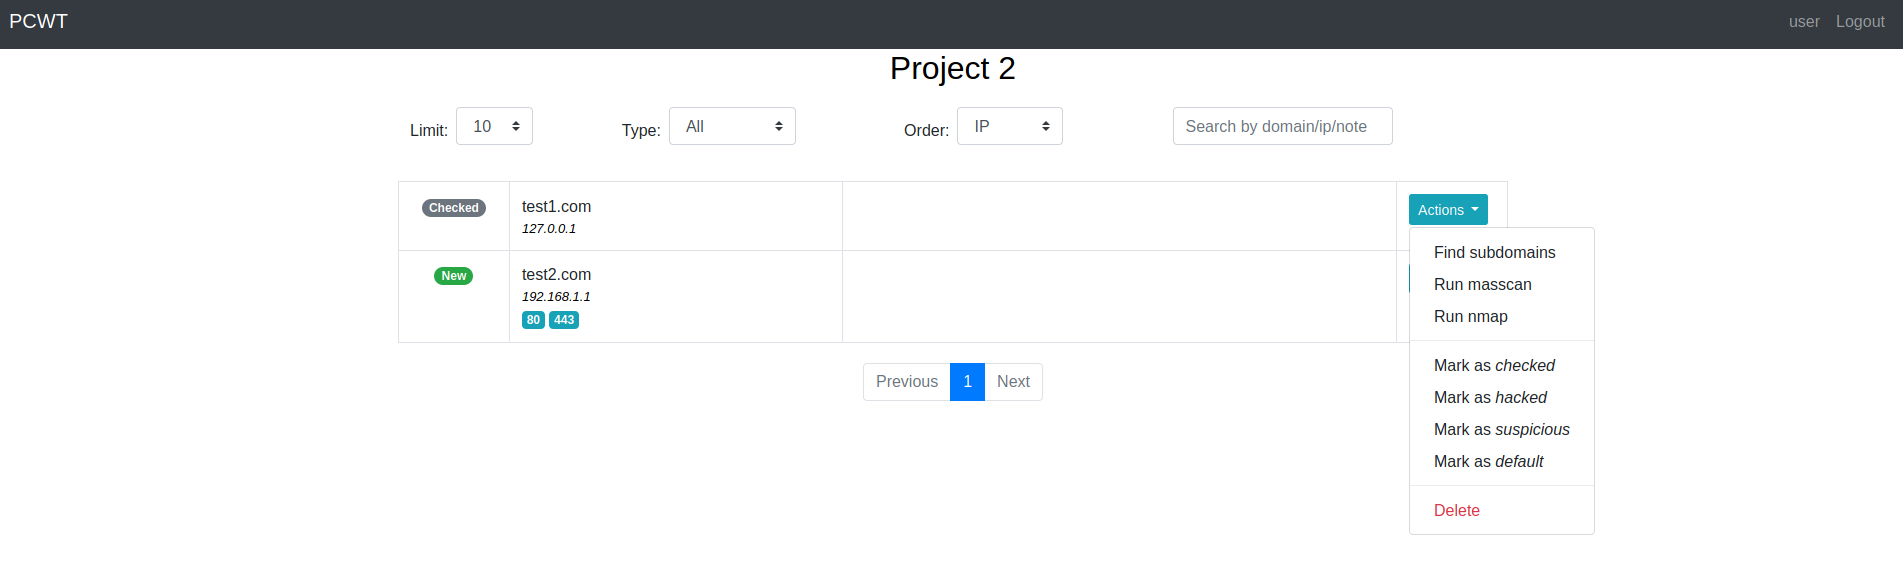 ascr0b/pcwt
Web-based project management interface for penetration testing and bug bounty workflows, automating port scanning with Nmap/Masscan and subdomain…
 chaitanyakrishna/iocscraper
IOCPARSER.COM is a Fast and Reliable service that enables you to extract IOCs and intelligence from different data sources.
 yasserjanah/cve-2020-5902
exploit code for F5-Big-IP (CVE-2020-5902)
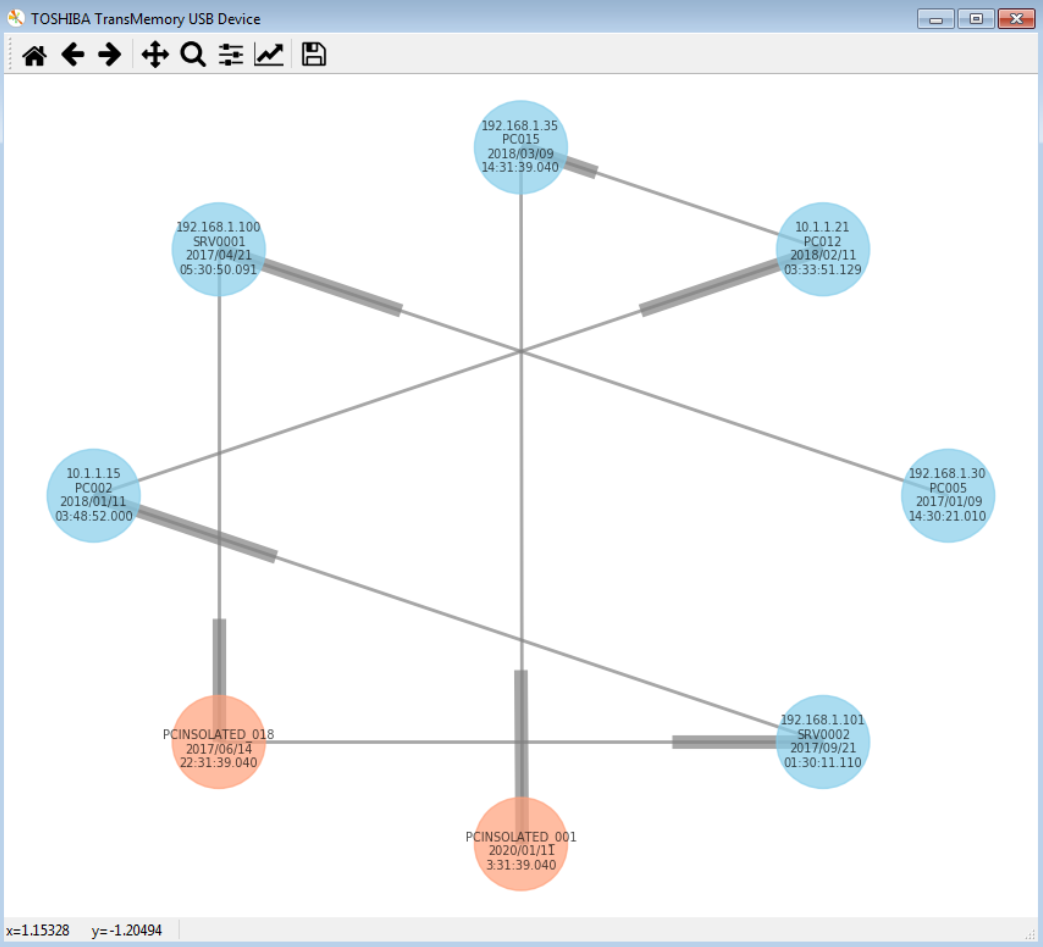 telefonica/hiddennetworks-python
USB device connection forensics tool that traces physical device-to-computer relationships across local and domain networks, generating visual graphs…
 syss-research/ldap-swak
LDAP Swiss Army Knife
 redhuntlabs/log4jhunt
An automated, reliable scanner for the Log4Shell (CVE-2021-44228) vulnerability.
 whiteoaksecurity/goawsconsolespray
Tool to spray AWS Console IAM Logins
 jas502n/cve-2018-14847
Proof-of-concept exploit for CVE-2018-14847 allowing arbitrary file read of plaintext passwords from MikroTik RouterOS WinBox service, with TCP/IP…
 lorddemon/cve-2021-41773-poc
PoC exploit script for Apache HTTP Server 2.4.49 path traversal and file disclosure vulnerability (CVE-2021-41773). Supports single IP, file list,…
 password123456/cve-collector
Automated CVE collector that crawls cvedetails.com, parses HTML for vulnerabilities with CVSS ≥ 6, and stores results in a delimiter-based file…
 gursev/flash-xdomain-xploit
ActionScript Proof of Concept to perform cross-domain reads
 eurecom-s3/linux_screenshot_xwindows
Volatility plugin to extract X screenshots from a memory dump