Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
213 results
MouseServer-1.7.8.5-RCE preview

MouseServer-1.7.8.5-RCE

GitHubmermehr/mouseserver-1.7.8.5-rce

PoC exploit for CVE-2022-3218 targeting WiFi Mouse Server 1.7.8.5, achieving RCE via keystroke injection and in-memory PowerShell payload delivery…

exploitationpayload-developmentpenetration-testing+2
4 days ago
LinksysLeaks preview

LinksysLeaks

GitHubjollyjumbuckk/linksysleaks

Python3 script to scan for Linksys smart wifi devices that are vulnerable to CVE-2014-8244

educationexploitationinformation-gathering+5
63 years ago
CVE-2022-43704 preview

CVE-2022-43704

GitHub9lyph/cve-2022-43704

Sinilink XY-WFTX Wifi Remote Thermostat Module Temperature Controller

authentication-authorizationembedded-systems-securityexploitation+7
51 year ago
Apple-Remote-Crash-Tool-CVE-2018-4407 preview

Apple-Remote-Crash-Tool-CVE-2018-4407

GitHubanonymouz4/apple-remote-crash-tool-cve-2018-4407

Crashes any macOS High Sierra or iOS 11 device that is on the same WiFi network

exploitationnetwork-securitypenetration-testing+3
47 years ago
ESPTouchCatcher preview

ESPTouchCatcher

GitHubsalgio/esptouchcatcher

eWeLinkESPT is a tool that automatically decodes and decrypts the WiFi network credentials transmitted to a supported ESP-based IoT device by the…

cryptographyexploitationhardware-iot-security+4
55 years ago
trackem preview

trackem

GitHubveteranop/trackem

Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…

bluetooth-securityinformation-gatheringiot-security+6
410 months ago
CVE-2026-58457 preview

CVE-2026-58457

GitHubj4ck3lsyn-gen2/cve-2026-58457

PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…

command-and-controleducationexploitation+7
22 months ago
mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce preview

mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce

GitHubhunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce

Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…

binary-exploitationeducationembedded-systems-security+5
33 months ago
CVE-2025-29338 preview

CVE-2025-29338

GitHubmasjadaan/cve-2025-29338

Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…

binary-exploitationembedded-systems-securityexploitation+2
34 months ago
CVE-2018-18441-exploit preview

CVE-2018-18441-exploit

GitHubbayazid-bit/cve-2018-18441-exploit

D-Link DCS series Wi-Fi camera expose sensitive information.

exploitationinformation-gatheringiot-security+3
34 months ago
CVE-2021-1965 preview

CVE-2021-1965

GitHubfoxtrot/cve-2021-1965

Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.

binary-exploitationexploitationexploit-frameworks+2
34 years ago
CVE-2025-52688 preview

CVE-2025-52688

GitHubjoelczk/cve-2025-52688

Proof-of-concept exploits for CVE-2025-52688: unauthenticated command injection and arbitrary file read vulnerabilities in Alcatel AP13161 enterprise…

command-and-controlexploitationhardware-iot-security+3
21 year ago
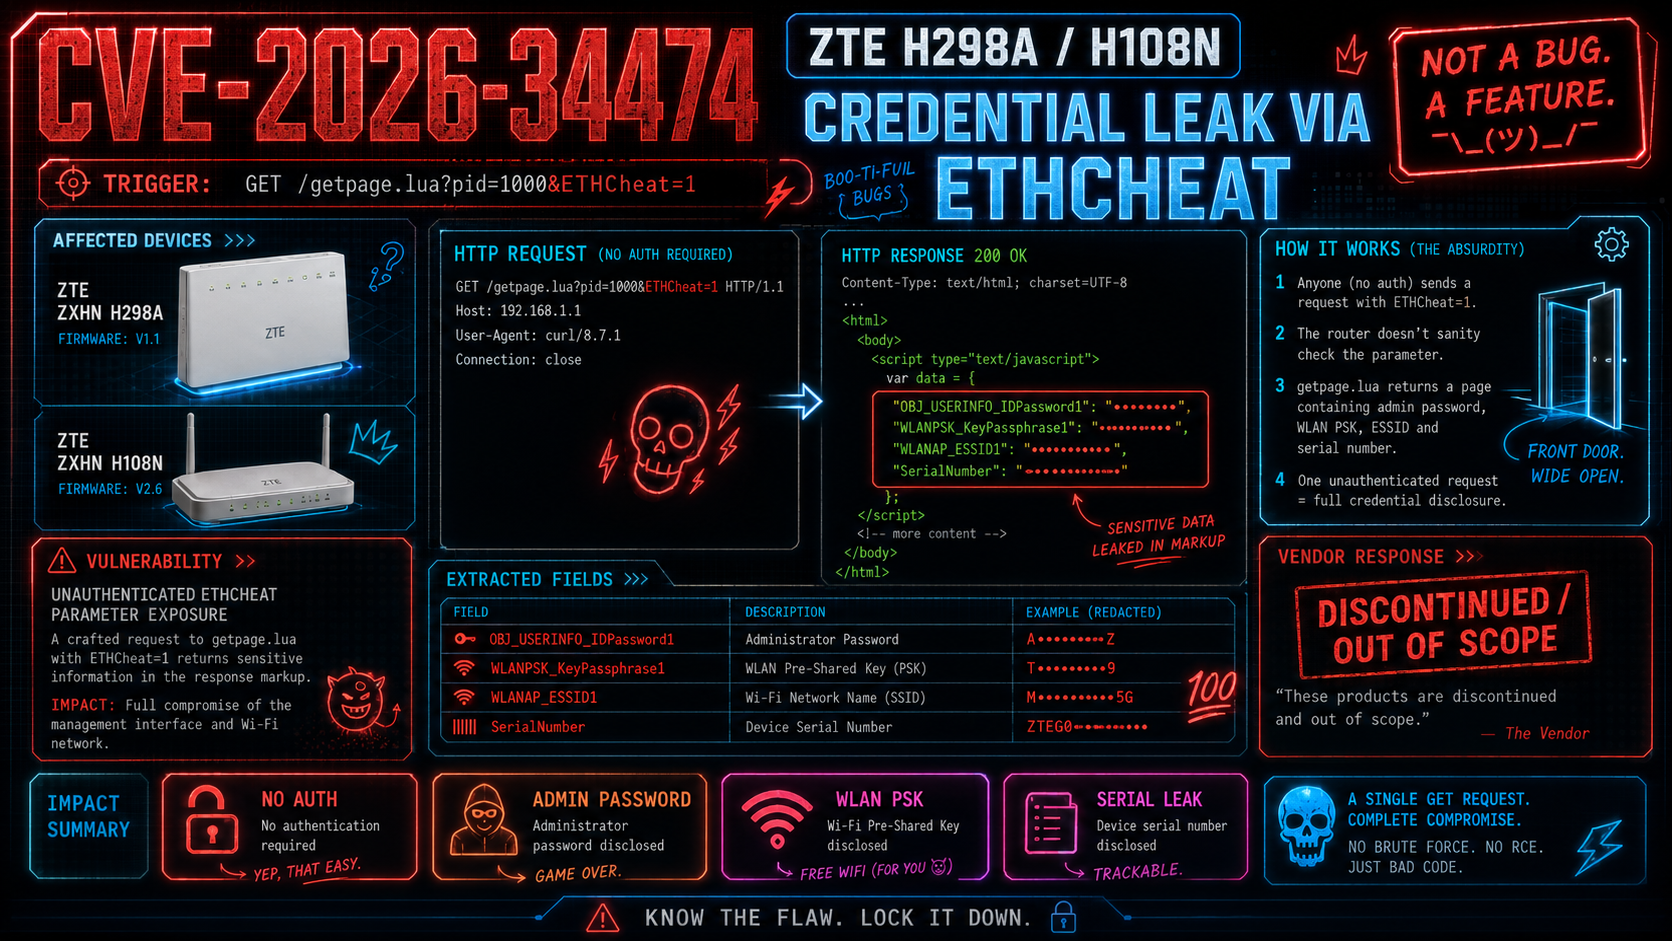
cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure preview

cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure

GitHubminanagehsalalma/cve-2026-34474-zte-h298a-h108n-sensitive-data-exposure

CVE-2026-34474: unauthenticated ETHCheat=1 requests leak the admin password and Wi-Fi PSK from ZTE H298A/H108N routers.

exploitationinformation-gatheringiot-security+3
14 months ago
bd-alaris-firmware-analysis preview

bd-alaris-firmware-analysis

GitHubnadafarafat/bd-alaris-firmware-analysis

Firmware security analysis of BD Alaris 8015 infusion pump (CVE-2016-9355). Identified 6 compound vulnerabilities including plaintext Wi-Fi…

cryptographyeducationembedded-systems-security+5
3 months ago
frameworks_opt_net_wifi_CVE-2021-0390 preview

frameworks_opt_net_wifi_CVE-2021-0390

GitHubuthrasri/frameworks_opt_net_wifi_cve-2021-0390

Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.

android-securityexploitationvulnerability-analysis+2
12 years ago
Komfy-Switch-Wifi-Password-Disclosure preview

Komfy-Switch-Wifi-Password-Disclosure

GitHubjasondoyle/komfy-switch-wifi-password-disclosure

Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…

bluetooth-securityexploitationiot-security+3
19 years ago
CVE-2024-42658 preview

CVE-2024-42658

GitHubbaroi-ai/cve-2024-42658

CVE-2024-42658 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the cookies…

exploitationinformation-gatheringiot-security+3
12 years ago
CVE-2024-42657 preview

CVE-2024-42657

GitHubbaroi-ai/cve-2024-42657

CVE-2024-42657 An issue in wishnet Nepstech Wifi Router NTPL-XPON1GFEVN v1.0 allows a remote attacker to obtain sensitive information via the lack of…

exploitationinformation-gatheringnetwork-security+3
12 years ago
Previous1…9101112Next